RATel
 frenchcisco/ratel
RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
command-and-controlencryption-decryption-toolspayload-generation+6
277
frenchcisco/ratelRAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
 sweetsoftware/ares
Python botnet and backdoor
 g1thub3r1st4/cve-2021-44909
orangescrum 1.8.0 - Remote Command Execution RCE (unauthenticated)
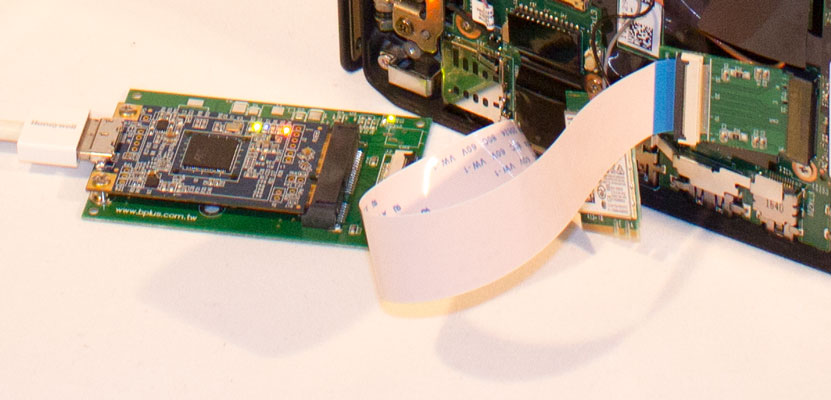 ufrisk/pcileech
Direct Memory Access (DMA) Attack Software
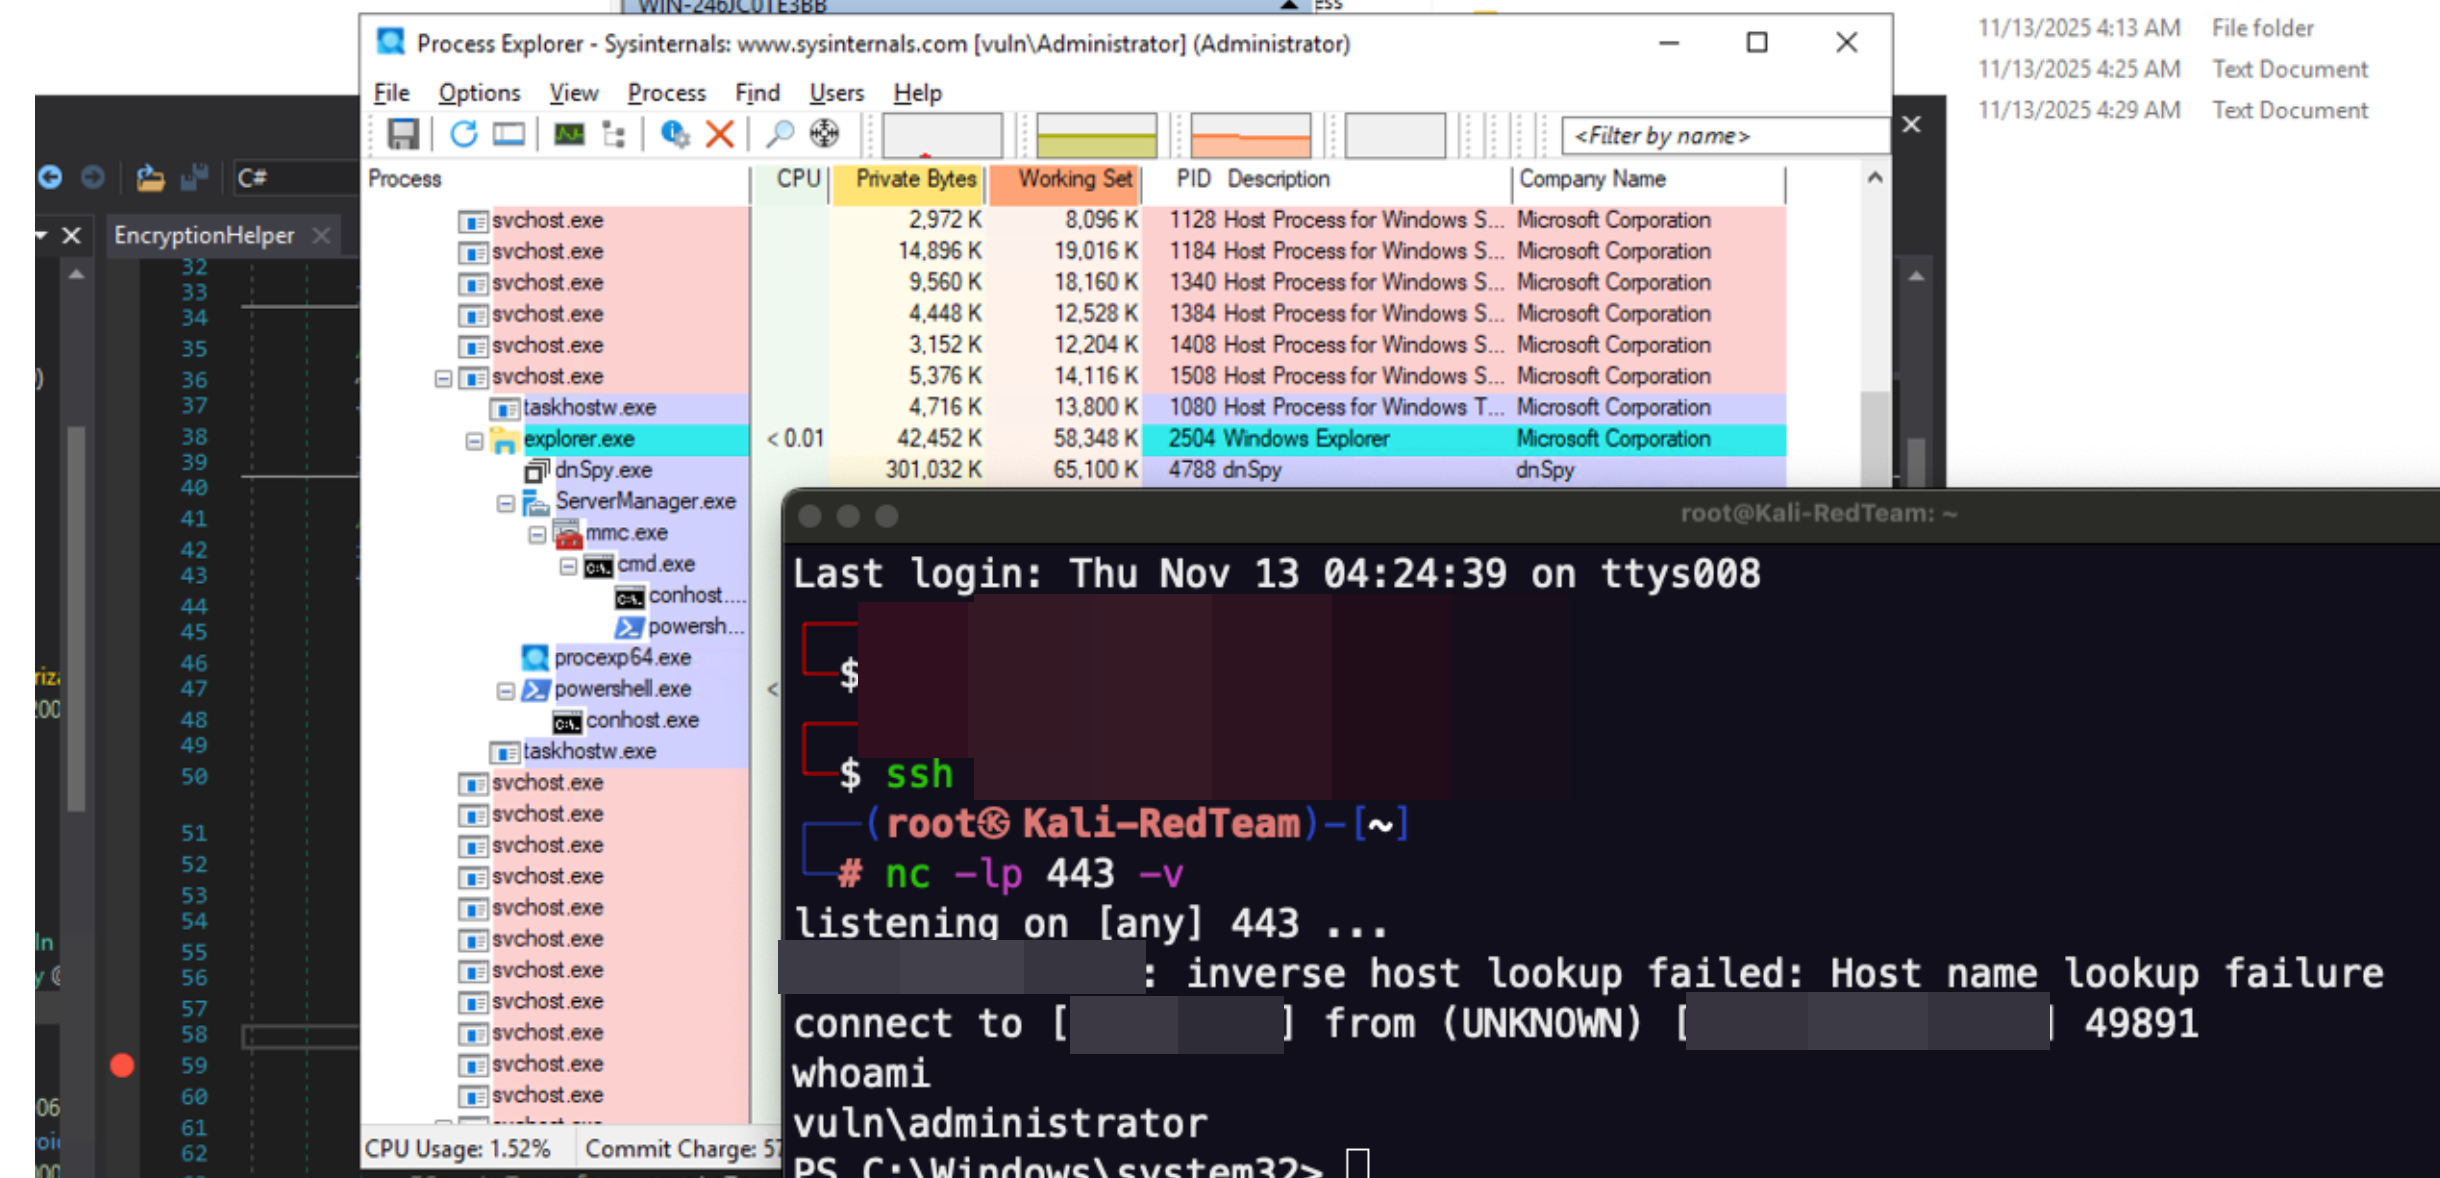 m507/cve-2025-59287-poc
Unauthenticated RCE PoC in Microsoft Windows Server Update Service (WSUS) - CVE-2025-59287 & CVE-2023-35317
 nathanlopez/stitch
Python Remote Administration Tool (RAT)
 gbrn1/pirate
Python Remote Access Tool
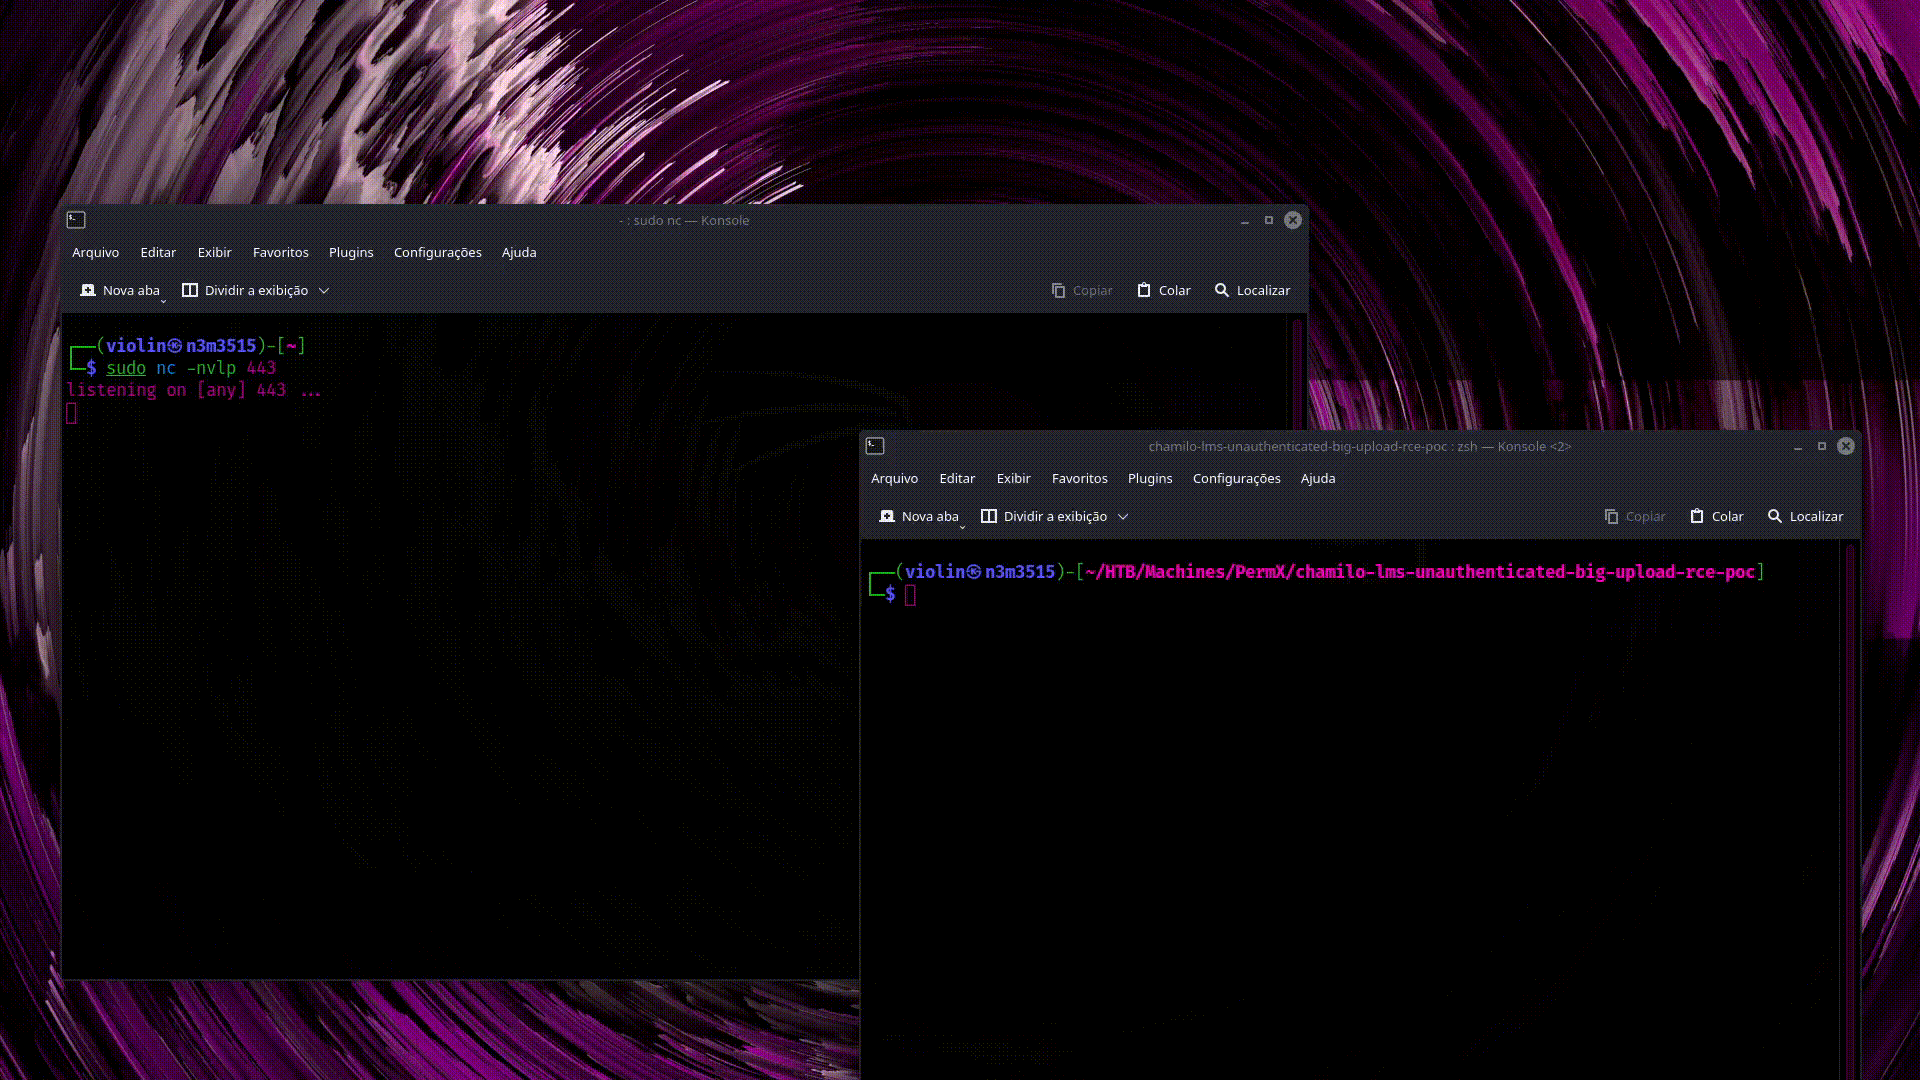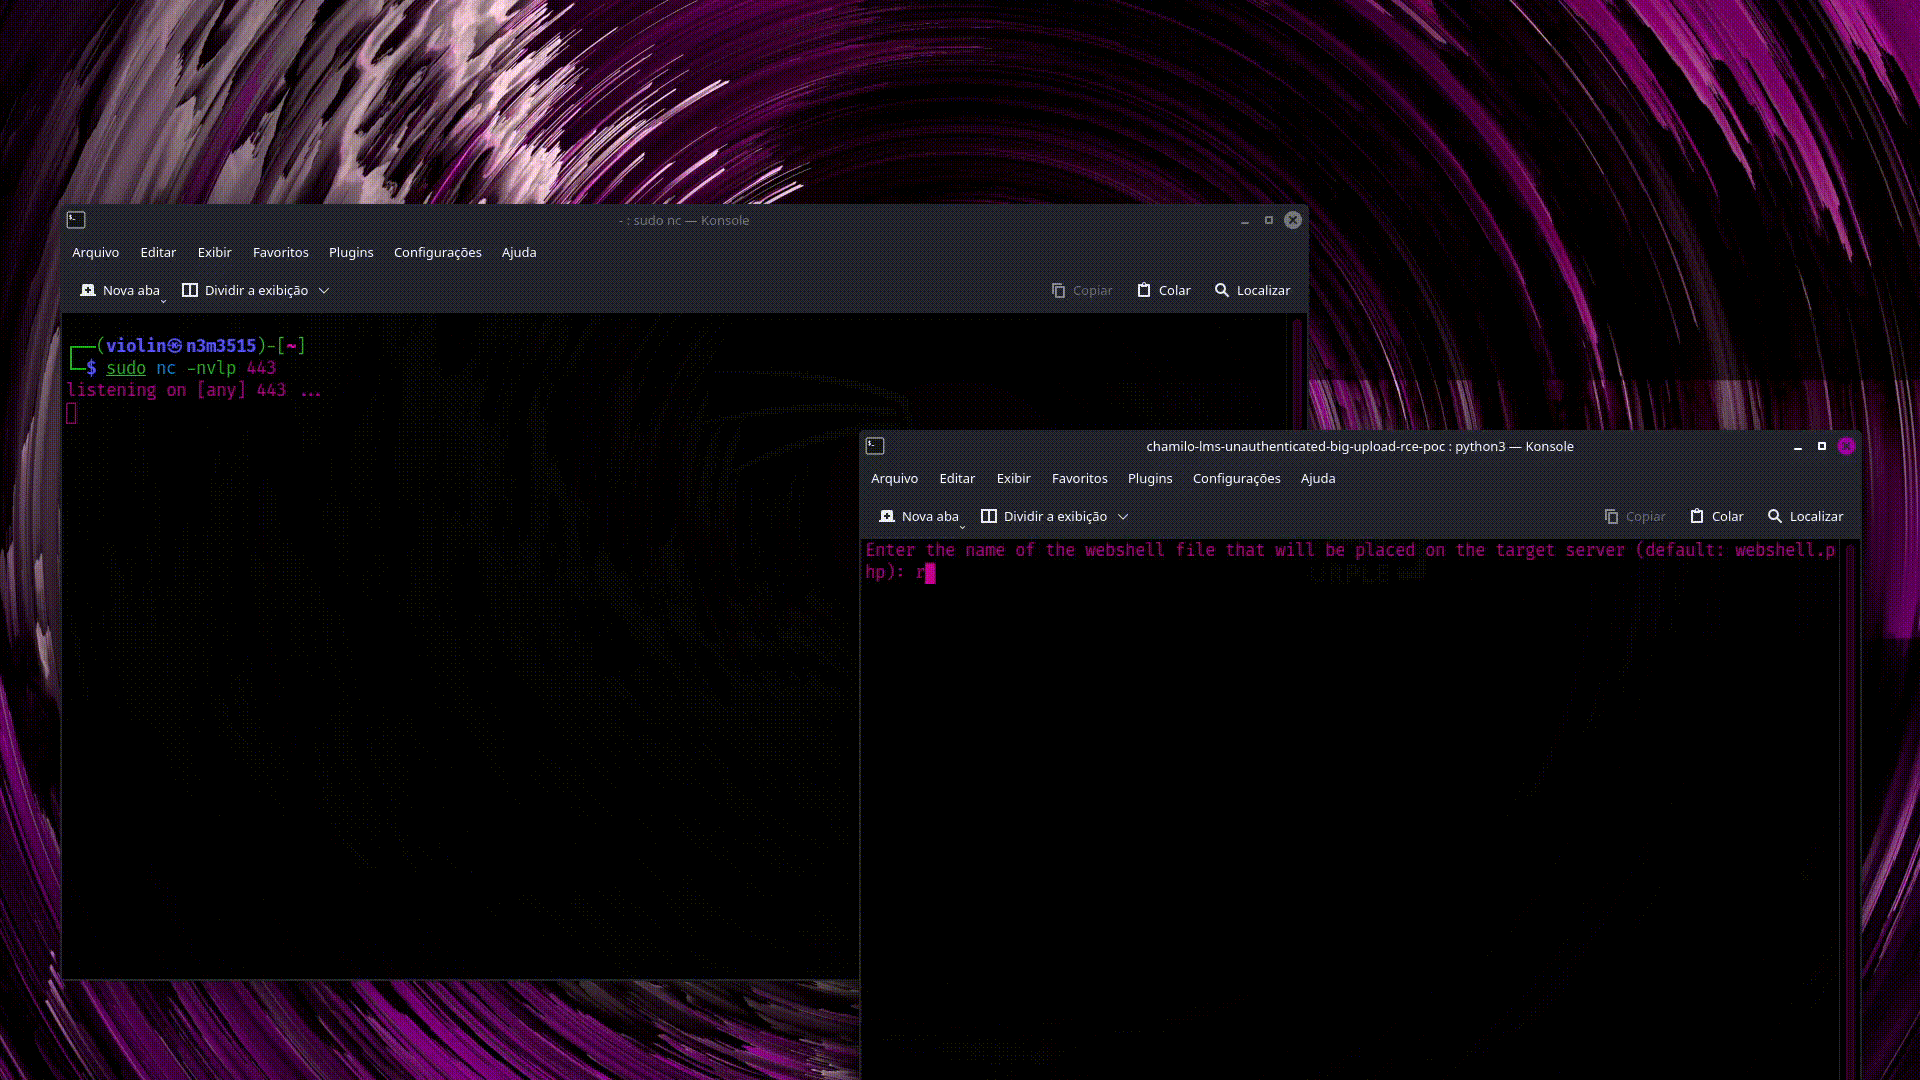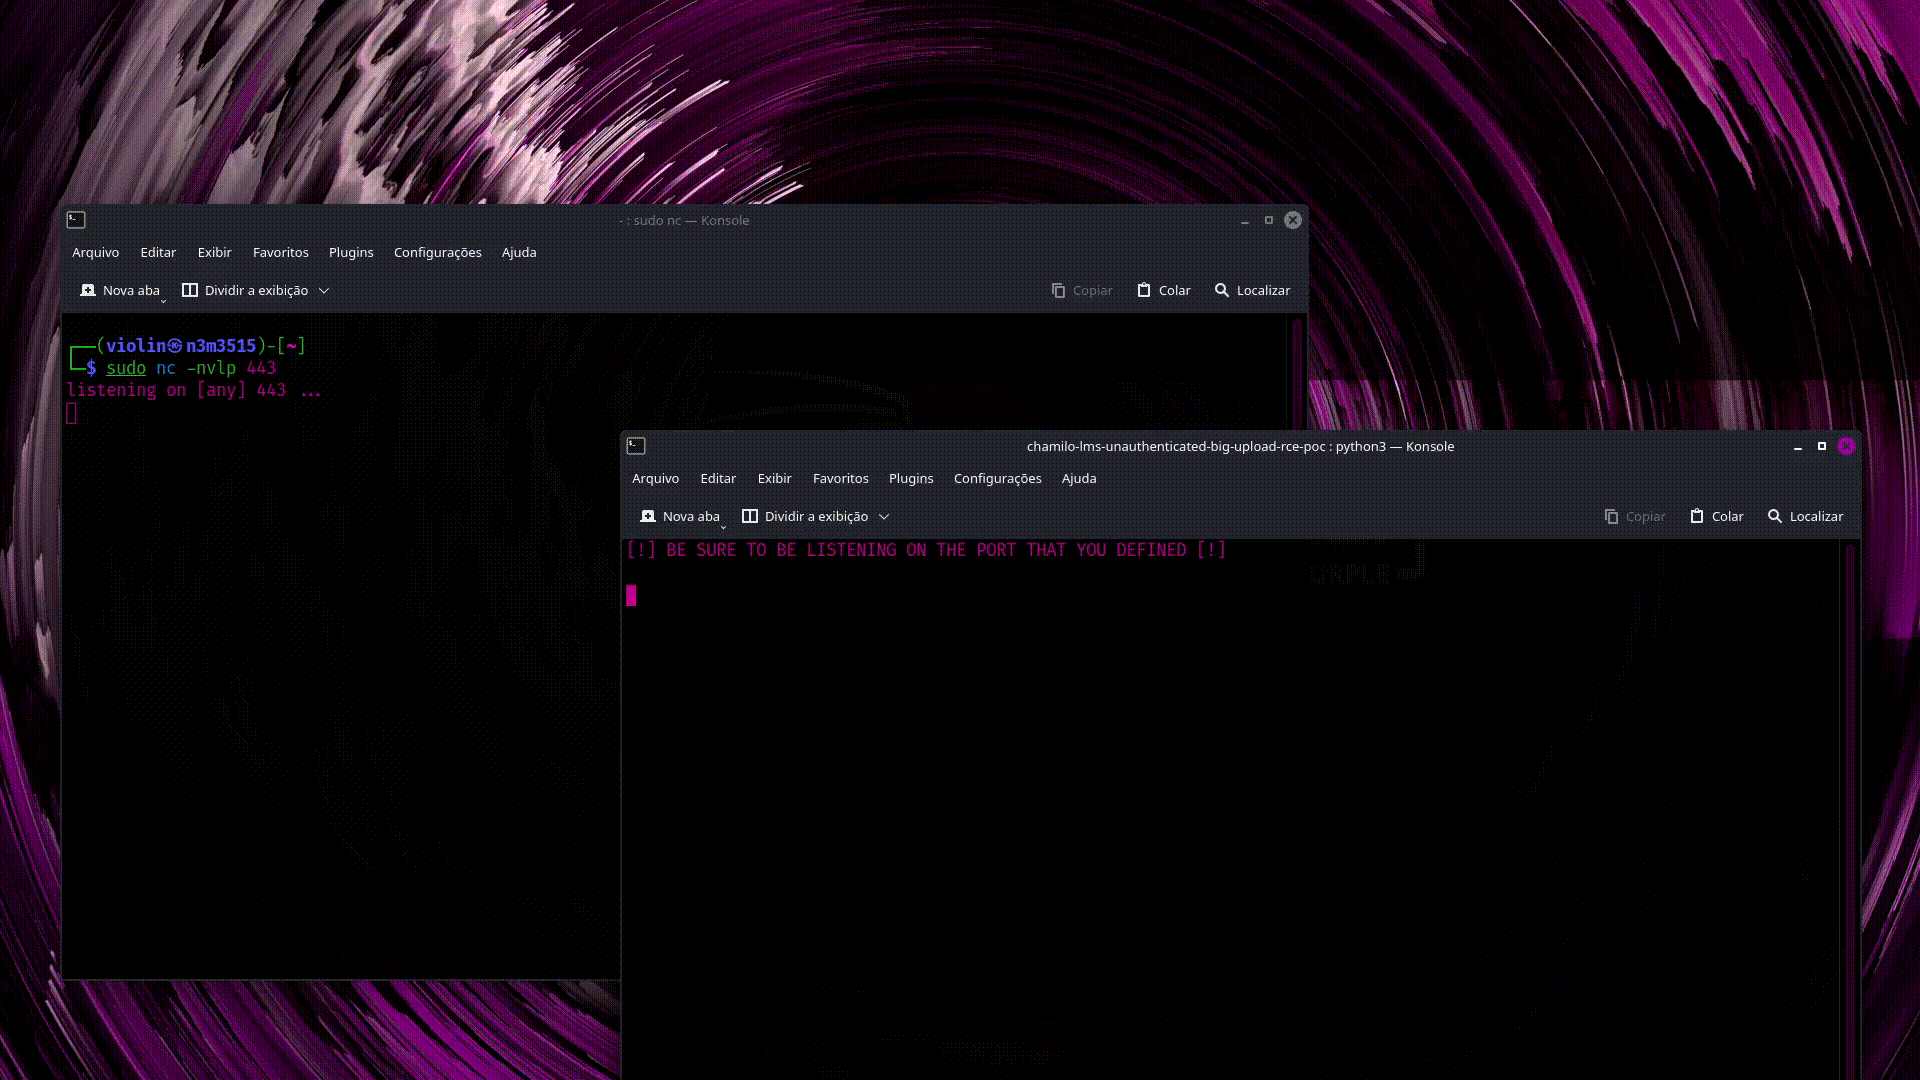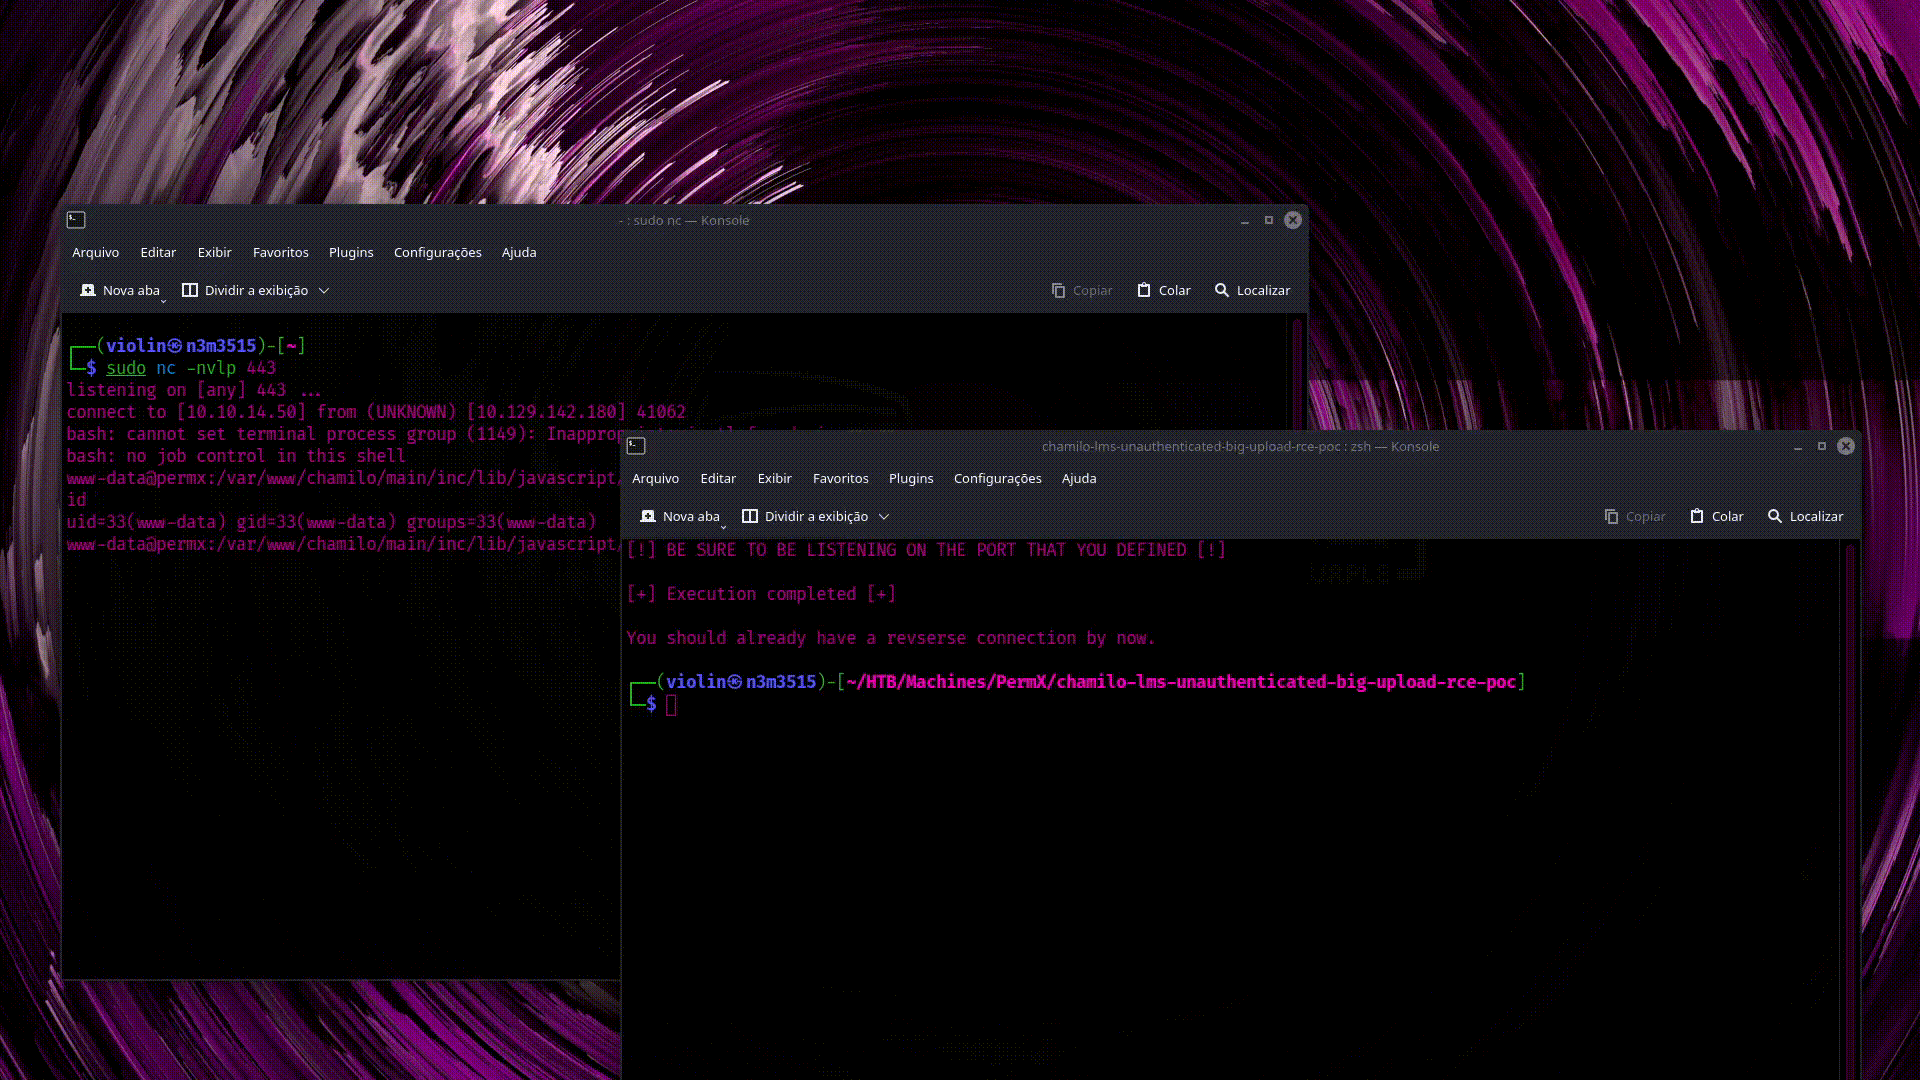 rai2en/cve-2023-4220-chamilo-lms
This is a script written in Python that allows the exploitation of the Chamilo's LMS software security flaw described in CVE-2023-4220
 gar-re/cve-2022-28944
Proof-of-concept exploit for unauthenticated remote code execution in EMCO Software products via DNS spoofing and malicious update injection.
 andreiverse/grc2
Lightweight C2 framework written in Nim for generating implants, managing listeners, and executing tasks via TCP/HTTP with a loot system for…
 00mjk/exploit-cve-2017-7494
SambaCry exploit (CVE-2017-7494)
 rdesktop/rdesktop
Open-source RDP client for connecting to Windows Terminal Services from Unix-like systems, supporting RDP versions 4 and 5 with smart-card…
 sp00kyskelet0n/py-rdp-patcher
Python script that patches the termsrv.dll file on Windows to enable multiple concurrent RDP sessions, supporting Windows 10 versions 1703 through…
 tomadimitrie/cve-2026-54424
Exploiting Parsec for Windows to gain SYSTEM privileges
 moisestapia/cve-2022-3218
Python exploit for CVE-2022-3218 that generates a reverse TCP payload via msfvenom and delivers it over HTTP to a target Windows host.
 yaldobaoth/cve-2015-1578-poc-metasploit
This is a proof-of-concept Metasploit module exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation…
 yaldobaoth/cve-2015-1578-poc
This is a proof-of-concept exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation leads to remote…