
Auto-PostXploit
 behzadmagzer/auto-postxploit
Windows Auto Post Exploitation - For ReD Team
information-gatheringpenetration-testingpost-exploitation+1
16
behzadmagzer/auto-postxploitWindows Auto Post Exploitation - For ReD Team
 bastillion-io/bastillion
Bastillion gives you a clean, browser-based way to manage SSH access across all your systems—like a bastion host with a friendly dashboard.
 loociprian/gc2-sheet
GC2 is a Command and Control application that allows an attacker to execute commands on the target machine using Google Sheet or Microsoft SharePoint…
 panagiks/rspet
RSPET (Reverse Shell and Post Exploitation Tool) is a Python based reverse shell equipped with functionalities that assist in a post exploitation…
 umutcamliyurt/pingrat
ICMP-based command-and-control tool that tunnels C2 traffic through firewalls using ping payloads, undetectable by most AV/EDR solutions.
 andreiverse/grc2
Lightweight C2 framework written in Nim for generating implants, managing listeners, and executing tasks via TCP/HTTP with a loot system for…
 ztgrace/sticky_keys_hunter
A script to test an RDP host for sticky keys and utilman backdoor.
 0x09al/browser-c2
Post Exploitation agent which uses a browser to do C2 operations.
 dviros/rat-via-telegram
Windows Remote Post Breach Tool via Telegram
 cedowens/macshellswift
Proof of concept MacOS post exploitation tool written in Swift. Designed as a POC for blue teams to build macOS detections. Author: Cedric Owens
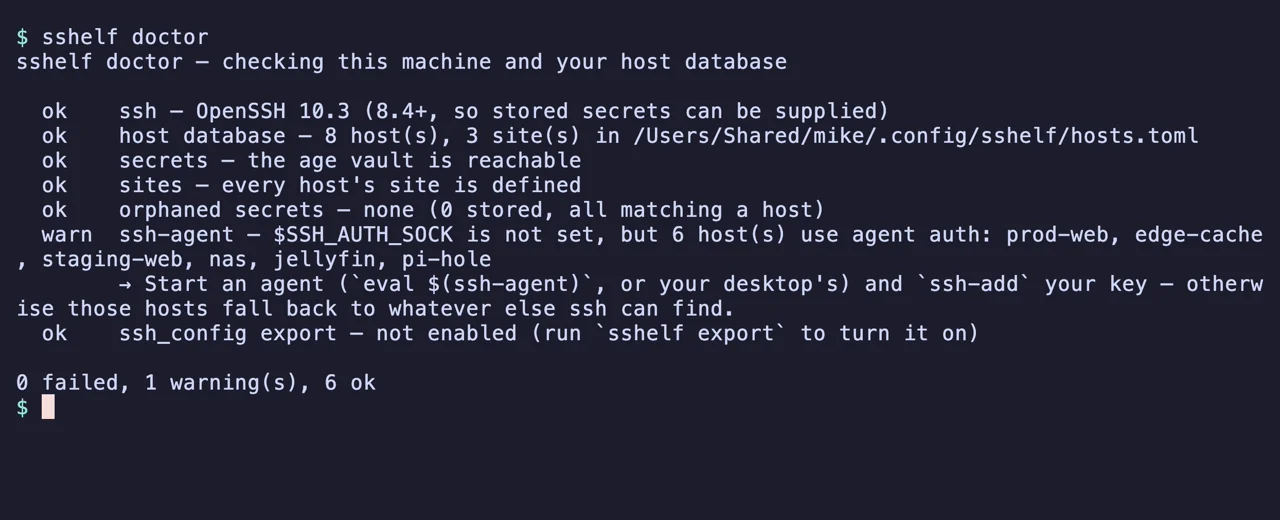 max-rh/sshelf
Fast terminal UI for your SSH hosts: fuzzy-search and connect in two keystrokes, dual-pane SFTP file transfer, and background port forwarding. Keeps…
 codextf2/pyhmmm
Simple PoC Python agent to showcase Havoc C2's custom agent interface. Not operationally safe or stable. Released with accompanying blog post as a…
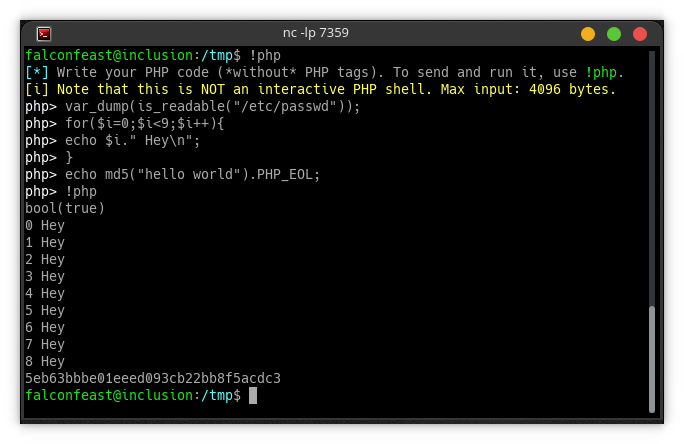 nickguitar/yaps
Yet Another PHP Shell - The most complete PHP reverse shell
 adhikara13/cve-2023-24489-sharefile
This project is a Python script that exploits the CVE-2023-24489 vulnerability in ShareFile. It allows remote command execution on the target server.…
 misterxid/watchguard_cve-2022-26318
Proof-of-concept exploit for CVE-2022-26318, a remote code execution vulnerability in WatchGuard XTM and FireWare OS, delivering a reverse shell via…
 anubissec/cve-2019-16278
A quick python exploit for the Nostromo 1.9.6 remote code execution vulnerability. Simply takes a host and port that the web server is running on.
 prodigiousmind/revshell
Pentestmonkeys' PHP reverse shell with dynamic host and port passing through GET request parameters
 shinthink/cve-2026-57517
💉 Blind SQL Injection → RCE exploit for Control Web Panel (CWP) ≤ 0.9.8.1224 — userRes POST → INTO DUMPFILE → cwpsvc shell