
php-reverse-shell
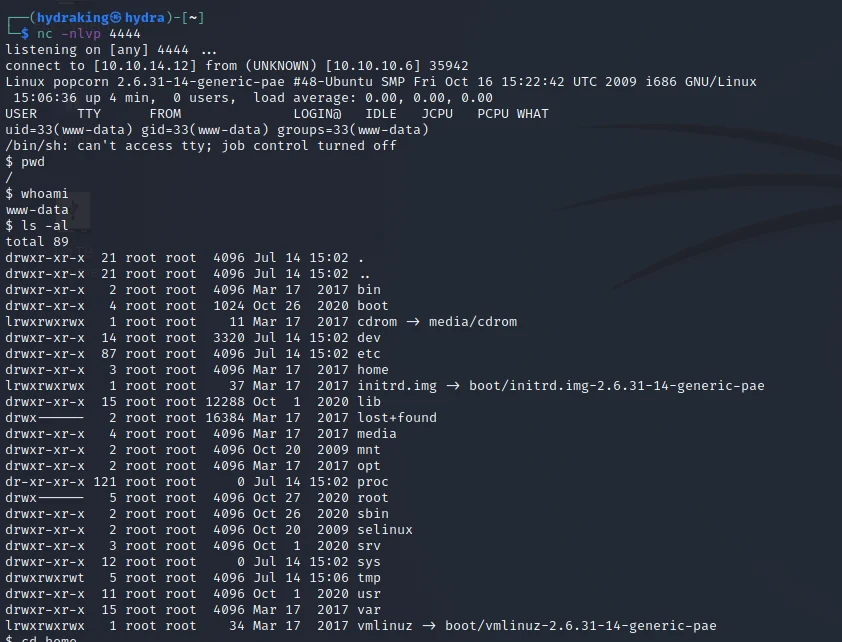
PHP script that establishes a reverse shell from a target server to the attacker's machine, enabling remote command execution and post-exploitation…

PHP script that establishes a reverse shell from a target server to the attacker's machine, enabling remote command execution and post-exploitation…

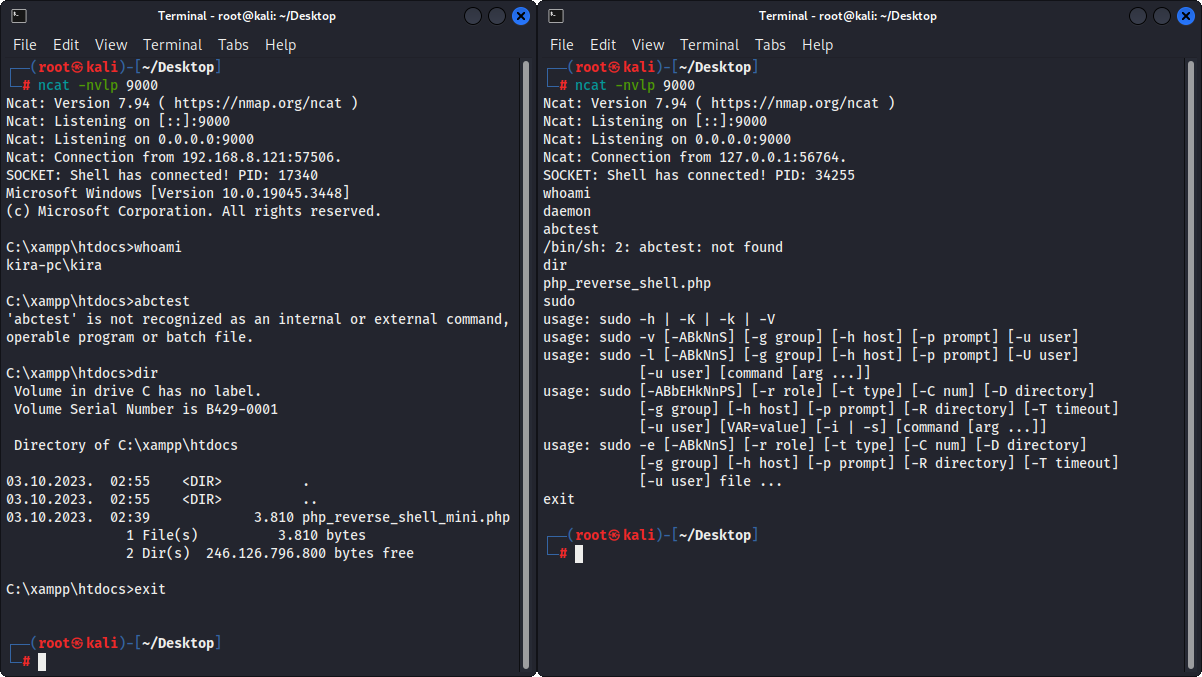
PHP shells that work on Linux OS, macOS, and Windows OS.

Exploit script for CVE-2020-24186 in WordPress that uploads a camouflaged PHP webshell and provides interactive or reverse shell access with optional…

Python scanner and proof-of-concept for CVE-2026-49049, an arbitrary file write in Joomla Helix3 that enables PHP web shell upload and remote code…

PHP reverse shell script for establishing a remote TCP connection, enabling command execution on a target web server.

PHP 8.1.0-dev Backdoor System Shell Script

Simple PHP reverse shell script for establishing remote command execution on target systems. Ideal for penetration testing and security assessments.


CVE-2022-22963 is a vulnerability in the Spring Cloud Function Framework for Java that allows remote code execution. This python script will verify…

Bash exploit automating authenticated remote code execution in Pluck CMS 4.7.18 via malicious ZIP upload, triggering a PHP reverse shell for…

Python exploit for Craft CMS CVE-2023-41892 Remote Code Execution vulnerability, delivering a PHP reverse shell for authorized penetration testing.

Authenticated RCE exploit for WBCE CMS <= 1.6.3 that creates a malicious module zip with a PHP reverse shell and netcat listener.

This script exploits the file upload feature in Pluck CMS v4.7.18 to upload a malicious PHP file, enabling remote access via a reverse shell. Once…

Python script that exploits CVE-2024-2389 in Progress Kemp Flowmon to execute arbitrary commands and establish a reverse shell via the…

Automated Python exploit for Camaleon CMS arbitrary file upload vulnerability (CVE-2024-46986). Supports reverse shell and command execution payloads…

Shell script exploit for CVE-2021-22204 targeting Exiftool, generating a malicious .djvu file to achieve remote code execution on vulnerable systems.

Exploit for ProFTPD 1.3.5 CVE-2015-3306 that writes a PHP backdoor to the target webroot and spawns a reverse shell for remote code execution.

The `swp_debug` parameter in `admin-post.php` allows remote attackers to include external files containing malicious PHP code, which are evaluated on…