
CVE-2022-30136
 fortra/cve-2022-30136
Windows Network File System Remote exploit for CVE-2022-30136
binary-exploitationexploitationpenetration-testing+2
143 years ago
fortra/cve-2022-30136Windows Network File System Remote exploit for CVE-2022-30136
 mrterrestrial/cve-2023-50564
This script exploits the file upload feature in Pluck CMS v4.7.18 to upload a malicious PHP file, enabling remote access via a reverse shell. Once…
 mchoudhary15/cve-2022-22029-nfs-server-
Proof-of-concept exploit for CVE-2022-22029, a Windows NFS remote code execution vulnerability. Includes PowerShell commands to disable NFSV3 as a…
 al1ex/cve-2022-1388
CVE-2022-1388 F5 BIG-IP iControl REST RCE
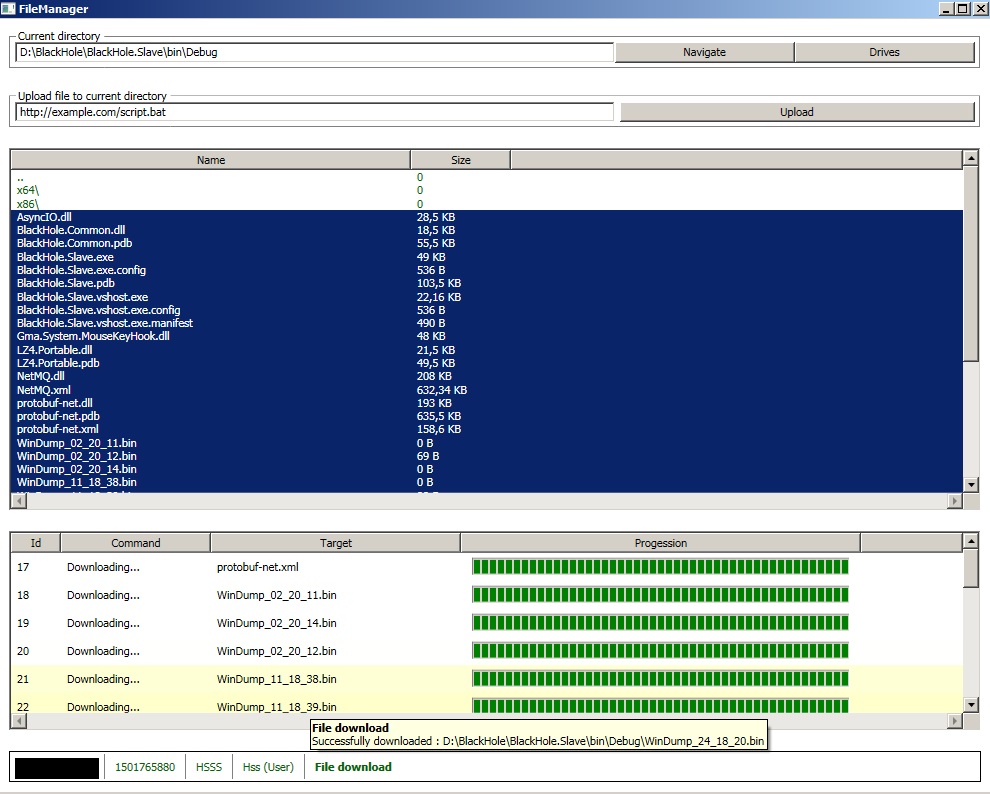 hussein-aitlahcen/blackhole
C# RAT (Remote Administration Tool)
 garvitv14/cve-2025-59287
Automated exploit for CVE-2025-59287, an unauthenticated RCE in WSUS, featuring payload generation, reverse shell listener, and AES encryption with…
 al1ex/cve-2021-22986
CVE-2021-22986 & F5 BIG-IP RCE
 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
 nccgroup/phantap
Phantom Tap (PhanTap) - an ‘invisible’ network tap aimed at red teams
 lnxg33k/webhandler
Bash simulator to control a server using PHP system functions.
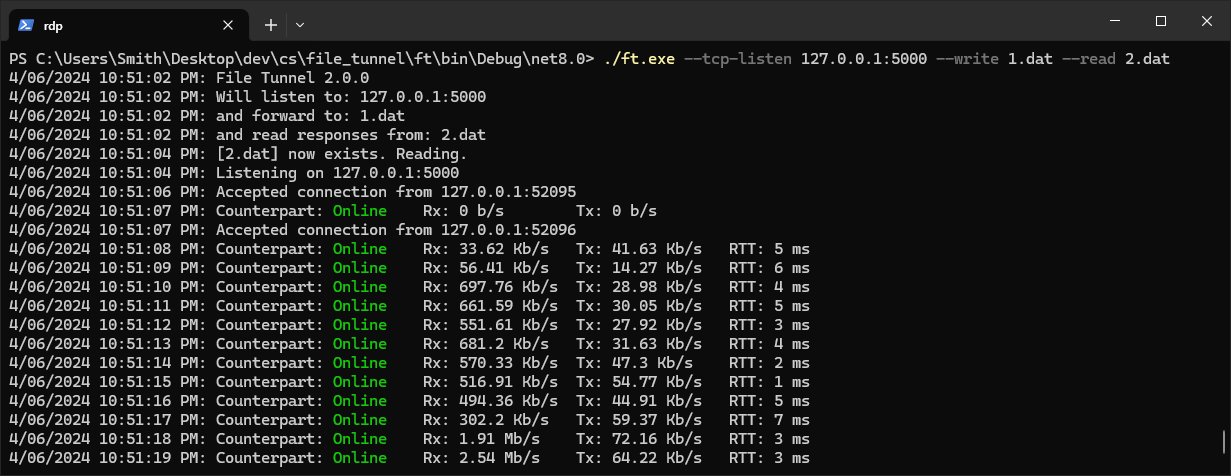 fiddyschmitt/file-tunnel
Tunnel TCP connections through a file
 nccgroup/socksoverrdp
Socks5/4/4a Proxy support for Remote Desktop Protocol / Terminal Services / Citrix / XenApp / XenDesktop
 r00t-3xp10it/meterpeter
C2 Powershell Command & Control Framework with BuiltIn Commands
 3v4si0n/http-revshell
Powershell reverse shell using HTTP/S protocol with AMSI bypass and Proxy Aware
 telefonica/ibombshell
Tool to deploy a post-exploitation prompt at any time
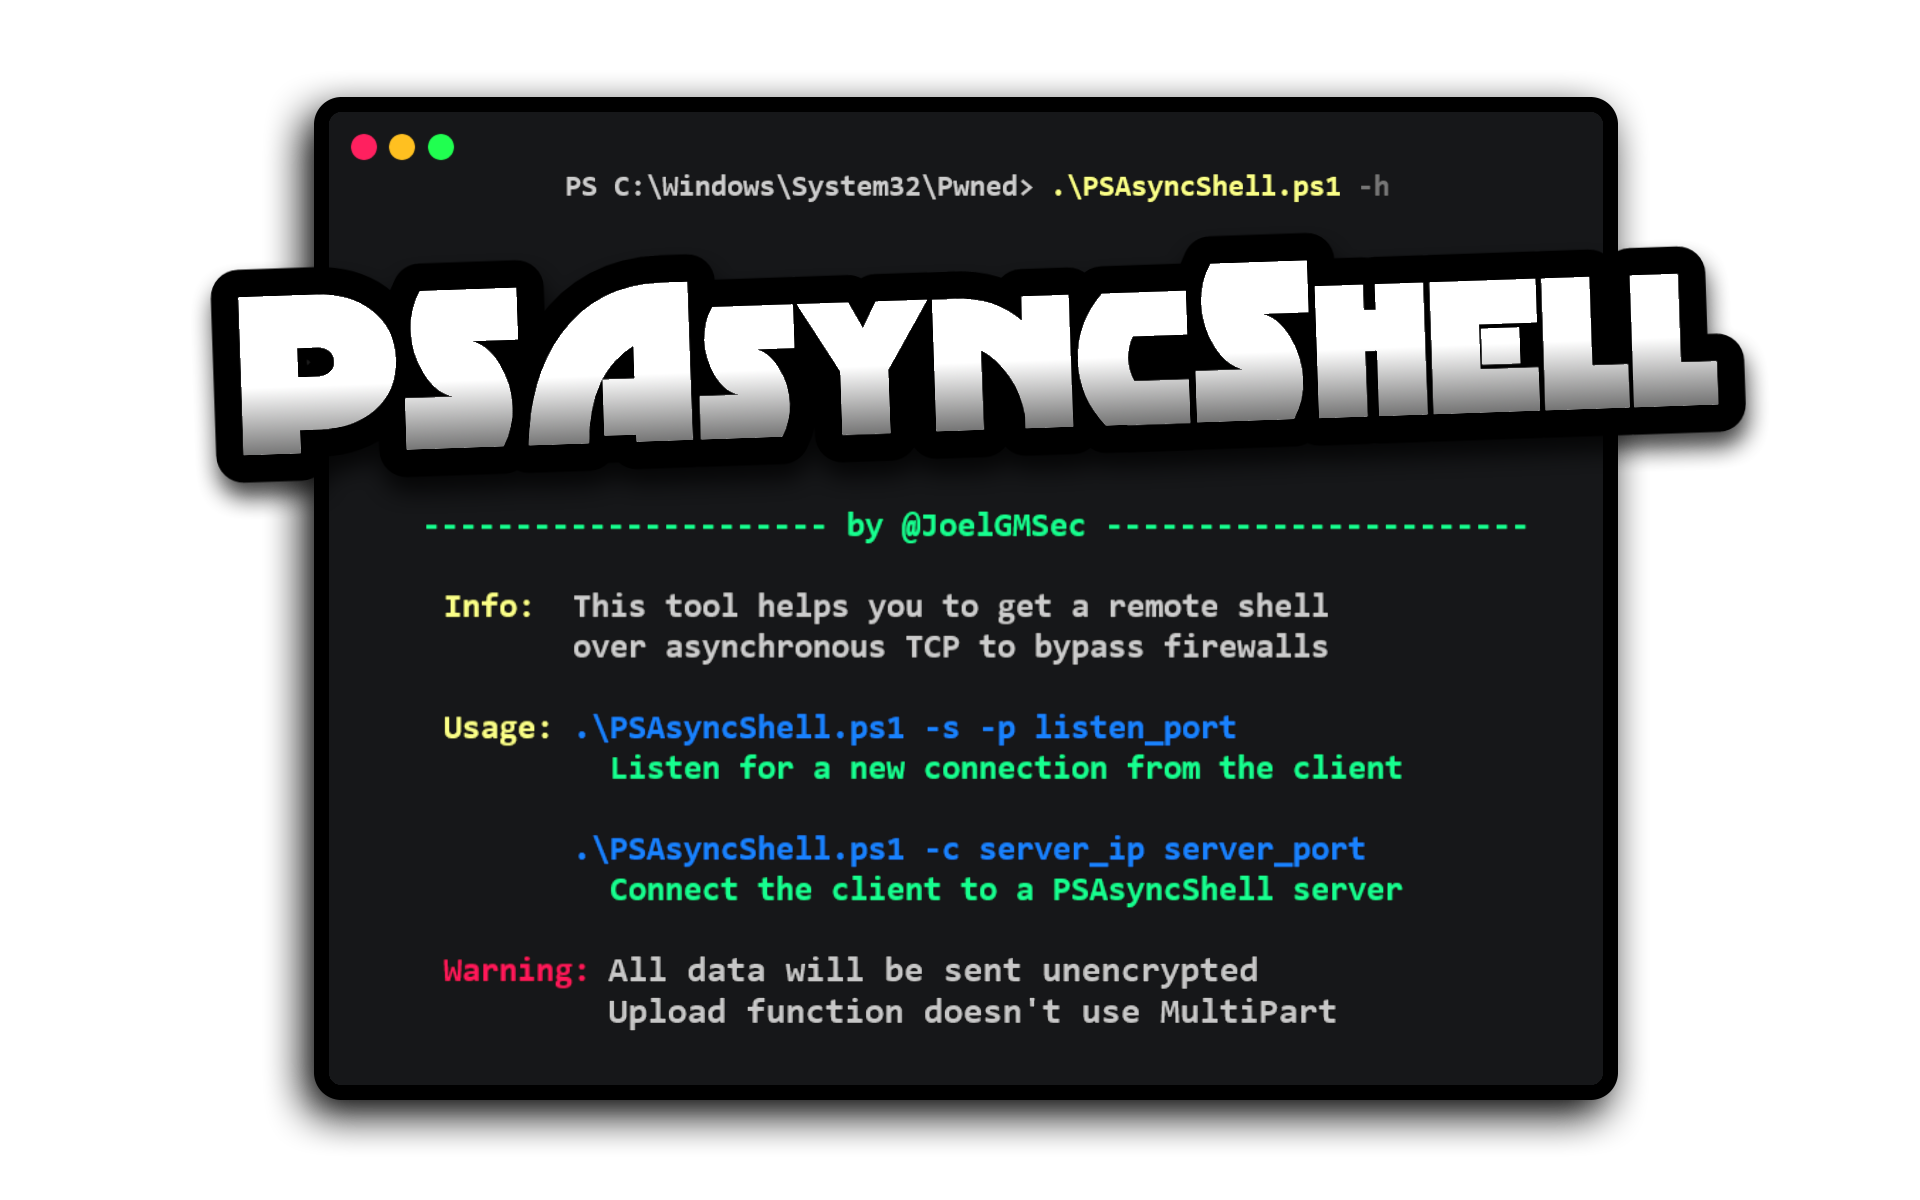 joelgmsec/psasyncshell
Asynchronous TCP reverse shell in pure PowerShell that bypasses firewalls via non-blocking I/O, with command history, file upload/download, and…
 hackerhouse-opensource/offensivelua
Offensive Lua.