Remote-Desktop-Services-Remote-Code-Execution-Vulnerability-CVE-2019-0708-

Remote code execution exploit for CVE-2019-0708 (BlueKeep) in Windows Remote Desktop Services, designed to integrate with the pocsuite3 framework for…

Remote code execution exploit for CVE-2019-0708 (BlueKeep) in Windows Remote Desktop Services, designed to integrate with the pocsuite3 framework for…

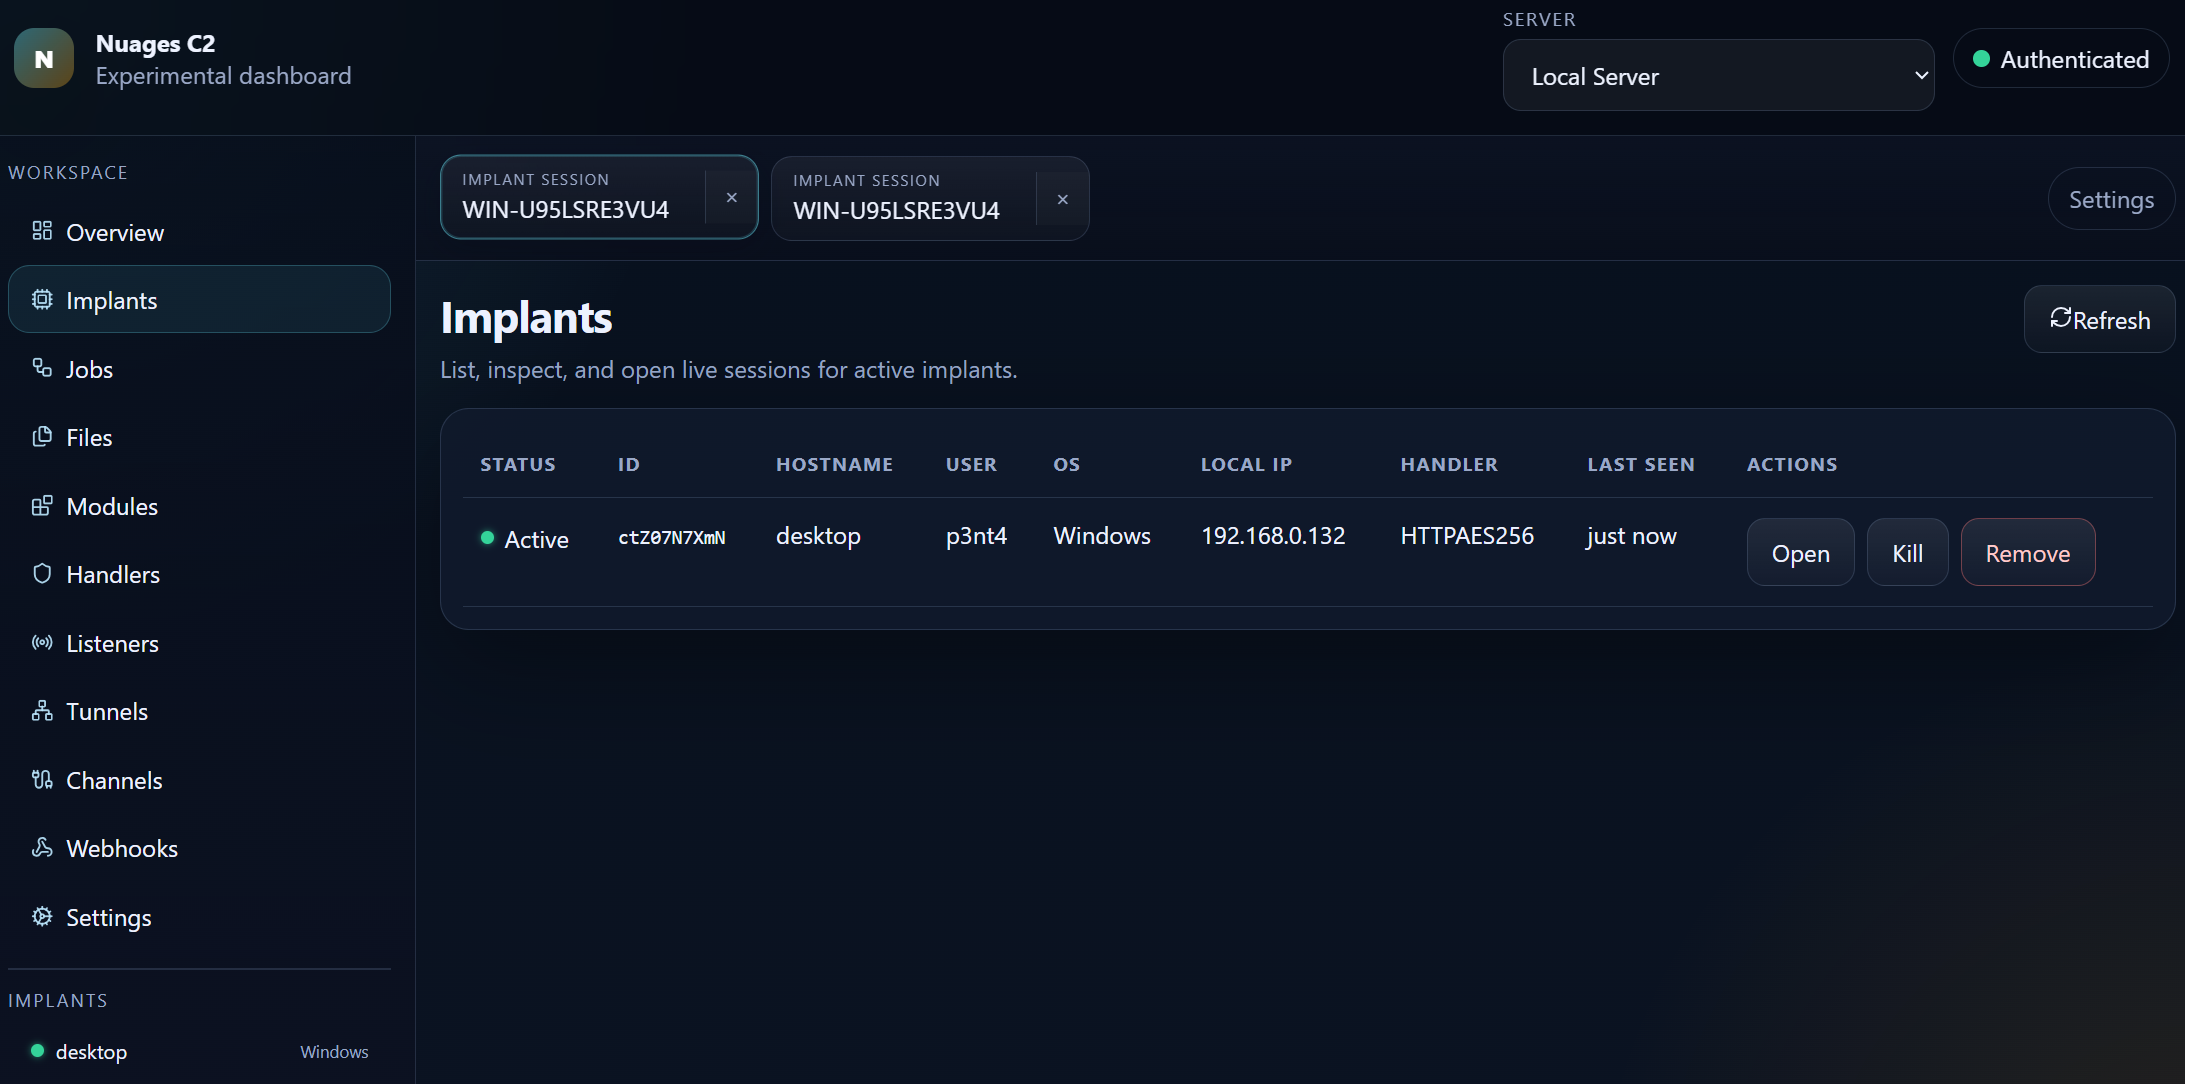
A third-party Gopher Assassin for the Havoc Framework.

Apfell C2 Server for the Google Chrome Extension Payload

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

MCP Server for Metasploit

The manage engine mass loader for CVE-2022-47966

CVE-2025-55182 Exploit | by infrar3d

A desktop operator console for Sliver C2, built with Wails. Provides a native, lightweight GUI interface for Sliver by directly interfacing with its…

A loader for bitbucket 2022 rce (cve-2022-36804)

Ghost Framework is an Android post-exploitation framework that exploits the Android Debug Bridge to remotely access an Android device.

A Framework meant for the exploitation of iOS devices.

A proof-of-concept Command & Control framework that utilizes the powerful AsyncSSH Python library which provides an asynchronous client and server…

A complete framework for exploiting the vulnerability CVE-2025-55182

The Shadow Attack Framework

Cross-platform Electron GUI for the Sliver C2 framework, providing session and beacon dashboards, payload generation, listeners, loot, and cloud…


Python exploit script targeting unauthenticated remote code execution in Strapi CMS 3.0.0-beta.17.4 via CVE-2019-18818 and CVE-2019-19609, delivering…

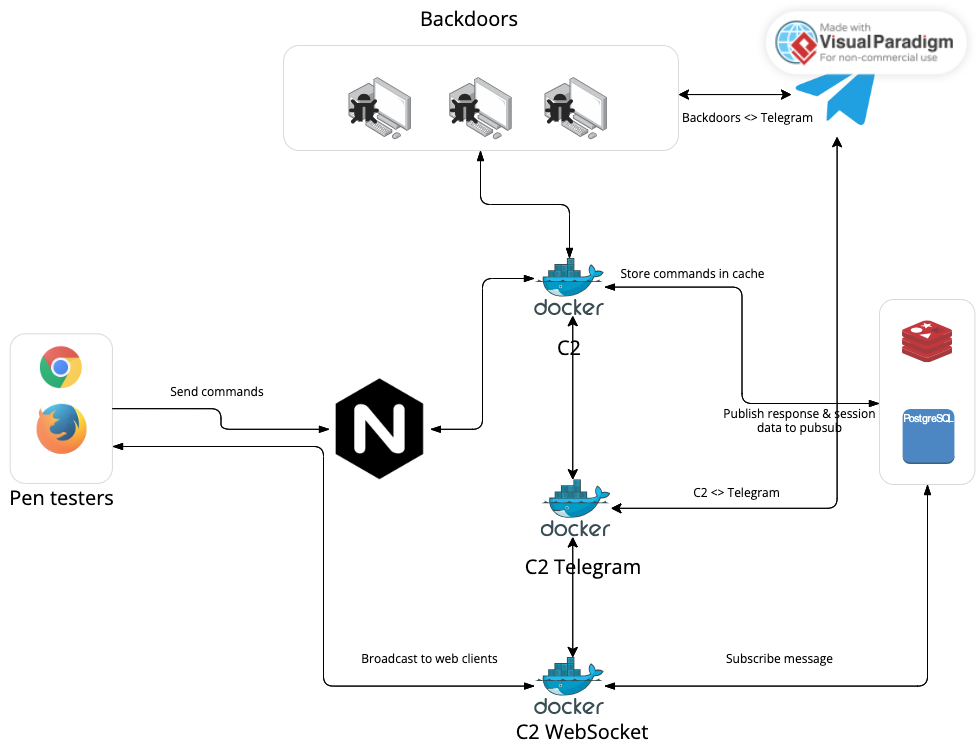
The C2 Cloud is a robust web-based C2 framework, designed to simplify the life of penetration testers. It allows easy access to compromised…