
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
14 results
cve-2024-6387-poc preview

cve-2024-6387-poc

GitHubacrono/cve-2024-6387-poc

32-bit PoC for CVE-2024-6387 — mirror of the original 7etsuo/cve-2024-6387-poc
binary-exploitationexploitationpenetration-testing+2
375
2 years ago
cve-2024-6387-poc preview

cve-2024-6387-poc

GitHublflare/cve-2024-6387-poc

MIRROR of the original 32-bit PoC for CVE-2024-6387 "regreSSHion" by 7etsuo/cve-2024-6387-poc
binary-exploitationexploitationpenetration-testing+2
1292 years ago
apache__mina-sshd_CVE-2023-35887_2-9-2 preview

apache__mina-sshd_CVE-2023-35887_2-9-2

GitHubshoucheng3/apache__mina-sshd_cve-2023-35887_2-9-2

Pure Java SSH client/server library implementing SSH-2 protocol with support for multiple ciphers, key exchanges, authentication methods, SFTP, SCP,…
authenticationcryptographyencryption-decryption-tools+5
1 year ago
CVE-2024-6387-poc-1 preview

CVE-2024-6387-poc-1

GitHubanhvutuan/cve-2024-6387-poc-1

CVE-2024-6387, also known as RegreSSHion, is a high-severity vulnerability found in OpenSSH servers (sshd) running on glibc-based Linux systems. It…
exploitationnetwork-securitypenetration-testing+3
22 years ago
CVE-2024-6387 preview

CVE-2024-6387

GitHubsxlmnwb/cve-2024-6387

Targeting a signal handler race condition in OpenSSH's server (sshd) on glibc-based Linux systems.
binary-exploitationexploitationpenetration-testing+2
212 years ago
cve-2024-6387-poc preview

cve-2024-6387-poc

GitHub7etsuo/cve-2024-6387-poc

a signal handler race condition in OpenSSH's server (sshd)
binary-exploitationexploitationpenetration-testing+2
12 years ago
cve-2024-6387-poc preview

cve-2024-6387-poc

GitHubt3rry327/cve-2024-6387-poc

Exploit for CVE-2024-6387 targeting a signal handler race condition in OpenSSH sshd on glibc-based Linux systems, enabling remote code execution as…
binary-exploitationexploitationpenetration-testing+2
2 years ago
CVE-2024-6387_poc preview

CVE-2024-6387_poc

GitHubjocker2410/cve-2024-6387_poc

Proof-of-concept exploit for CVE-2024-6387, a signal handler race condition in OpenSSH server (sshd) on glibc-based Linux systems, enabling remote…
exploitationpenetration-testingprivilege-escalation+3
2 years ago
sshimpanzee preview

sshimpanzee

GitHublexfo/sshimpanzee

SSHD Based implant supporting tunneling mecanisms to reach the C2 (DNS, ICMP, HTTP Encapsulation, HTTP/Socks Proxies, UDP...)
command-and-controldns-analysisnetwork-security+4
2951 year ago
regreSSHion preview

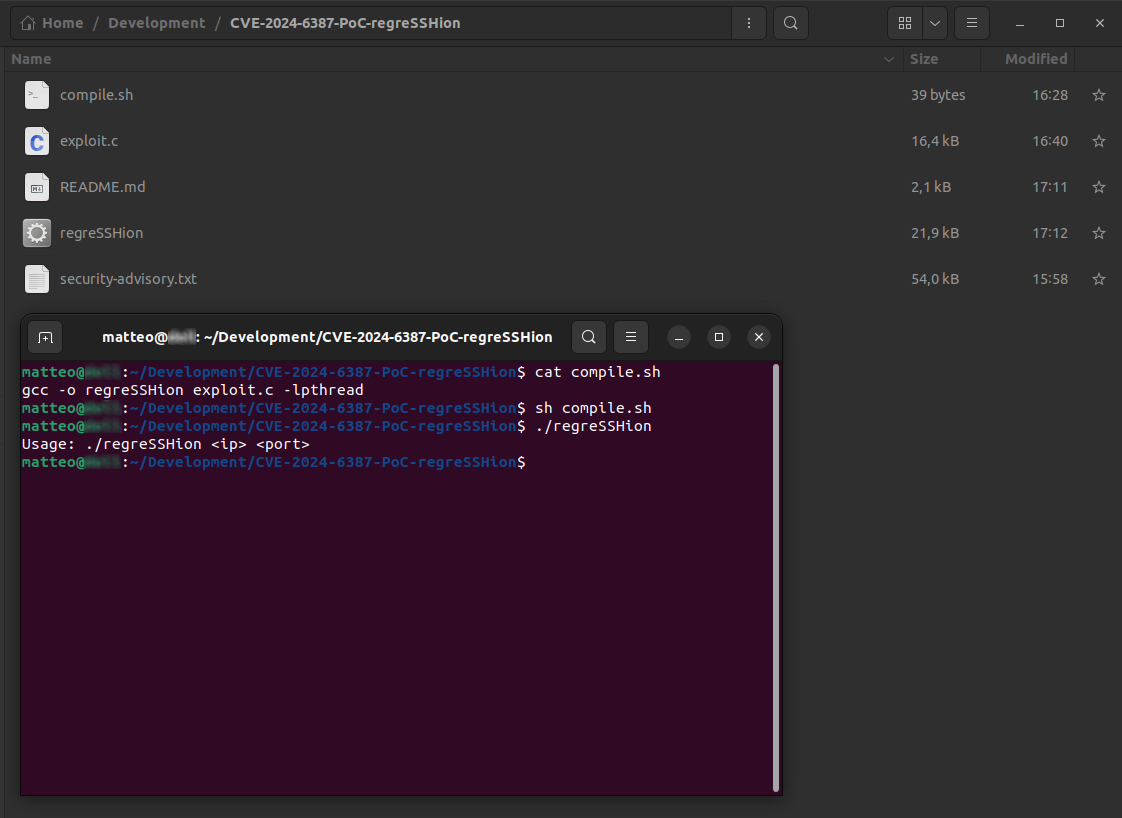
regreSSHion

GitHubxonoxitron/regresshion

CVE-2024-6387 (regreSSHion) Exploit (PoC), a vulnerability in OpenSSH's server (sshd) on glibc-based Linux systems.
exploitationpayload-developmentpenetration-testing+3
712 years ago
regreSSHive preview

regreSSHive

GitHub4lxprime/regresshive

rewrited SSH Exploit for CVE-2024-6387 (regreSSHion)
exploitationnetwork-securitypayload-development+3
2 years ago
cve-2024-6387-poc preview

cve-2024-6387-poc

GitHubdimamend/cve-2024-6387-poc

Exploit for CVE-2024-6387, a signal handler race condition in OpenSSH sshd, enabling remote code execution as root on glibc-based Linux systems.
binary-exploitationexploitationpenetration-testing+3
2 years ago
CVE-2023-25136 preview

CVE-2023-25136

GitHubnhakobyan685/cve-2023-25136

OpenSSH 9.1 vulnerability mass scan and exploit
exploitationnetwork-securitypenetration-testing+3
83 years ago
ssh_poc2024 preview

ssh_poc2024

GitHubalex14324/ssh_poc2024

An exploit for CVE-2024-6387, targeting a signal handler race condition in OpenSSH's server

binary-exploitationexploitationpenetration-testing+3
12 years ago