

Empire
 bc-security/empire
Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
adversarial-attackcommand-and-controldata-exfiltration+16
5.3k
bc-security/empireEmpire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
 its-a-feature/mythic
A collaborative, multi-platform, red teaming framework
 i-am-shodan/usbarmyknife
USB Army Knife – the ultimate close access tool for penetration testers and red teamers.
 nccgroup/phantap
Phantom Tap (PhanTap) - an ‘invisible’ network tap aimed at red teams
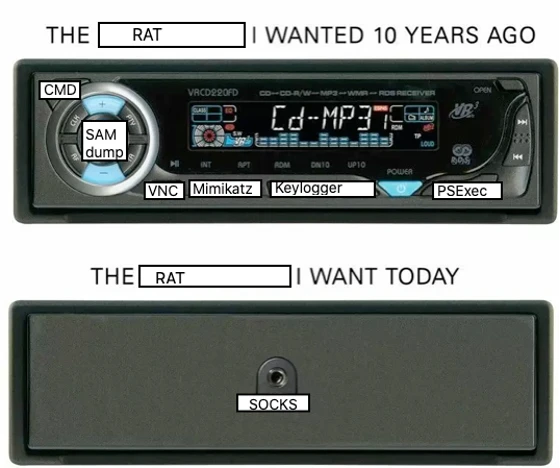 yeeb1/socktail
Lightweight Go binary that joins a device to a Tailscale network and exposes a local SOCKS5 proxy for ephemeral red team access. Supports…
 cyb0r9/androspy
Automated Android backdoor generator with crypter, IP poisoning, and Metasploit payload integration for penetration testing and red team operations.
 4g3nt47/striker
Multi-operator C2 framework with native C and Python agents, HTTP(S) channels, asynchronous tasking, and a reactive web UI for red team operations.
 kimd155/quickresponsec2
Covert C2 framework using QR codes for indirect command execution and result retrieval via HTTP/S, designed for stealthy penetration testing and red…
 yehia-mamdouh/shell3er
PowerShell-based reverse shell with background task execution, file transfer, and dual persistence mechanisms via registry and startup folder for red…
 dereeqw/blackberryc2
Encrypted command‑and‑control (C2) research framework for cybersecurity education, red team labs, and secure client‑server communication experiments.
 behzadmagzer/auto-postxploit
Windows Auto Post Exploitation - For ReD Team
 h3x0v3rl0rd/freepbx-reverse-shell-module
Exploit module for FreePBX delivering a reverse shell payload to achieve remote command execution and persistent shell access, designed for…
 bishopfox/sliver
Adversary Emulation Framework
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
 nettitude/poshc2_old
Powershell C2 Server and Implants
 hackerhouse-opensource/offensivelua
Offensive Lua.
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 apenwarr/sshuttle
Wrong project! You should head over to http://github.com/sshuttle/sshuttle