metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…

Automated exploitation framework for CVE-2025-55182 (Next.js RCE) with subdomain enumeration, vulnerability scanning, payload generation, and…

Modular Python exploitation framework with a Metasploit-style console, auto-registering Exploit and Auxiliary modules, tri-state checks, and multiple…

n8n God Mode Ultimate - CVE-2025-68613 Scanner v1.0.0 ║ ║ Workflow Automation Remote Code Execution


Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…

Weaponized web shell

Vulnerability-specific PoC scripts for discovering and exploiting RCE, SQLi, XXE, SSRF, and unauthorized-access flaws in enterprise web apps and…

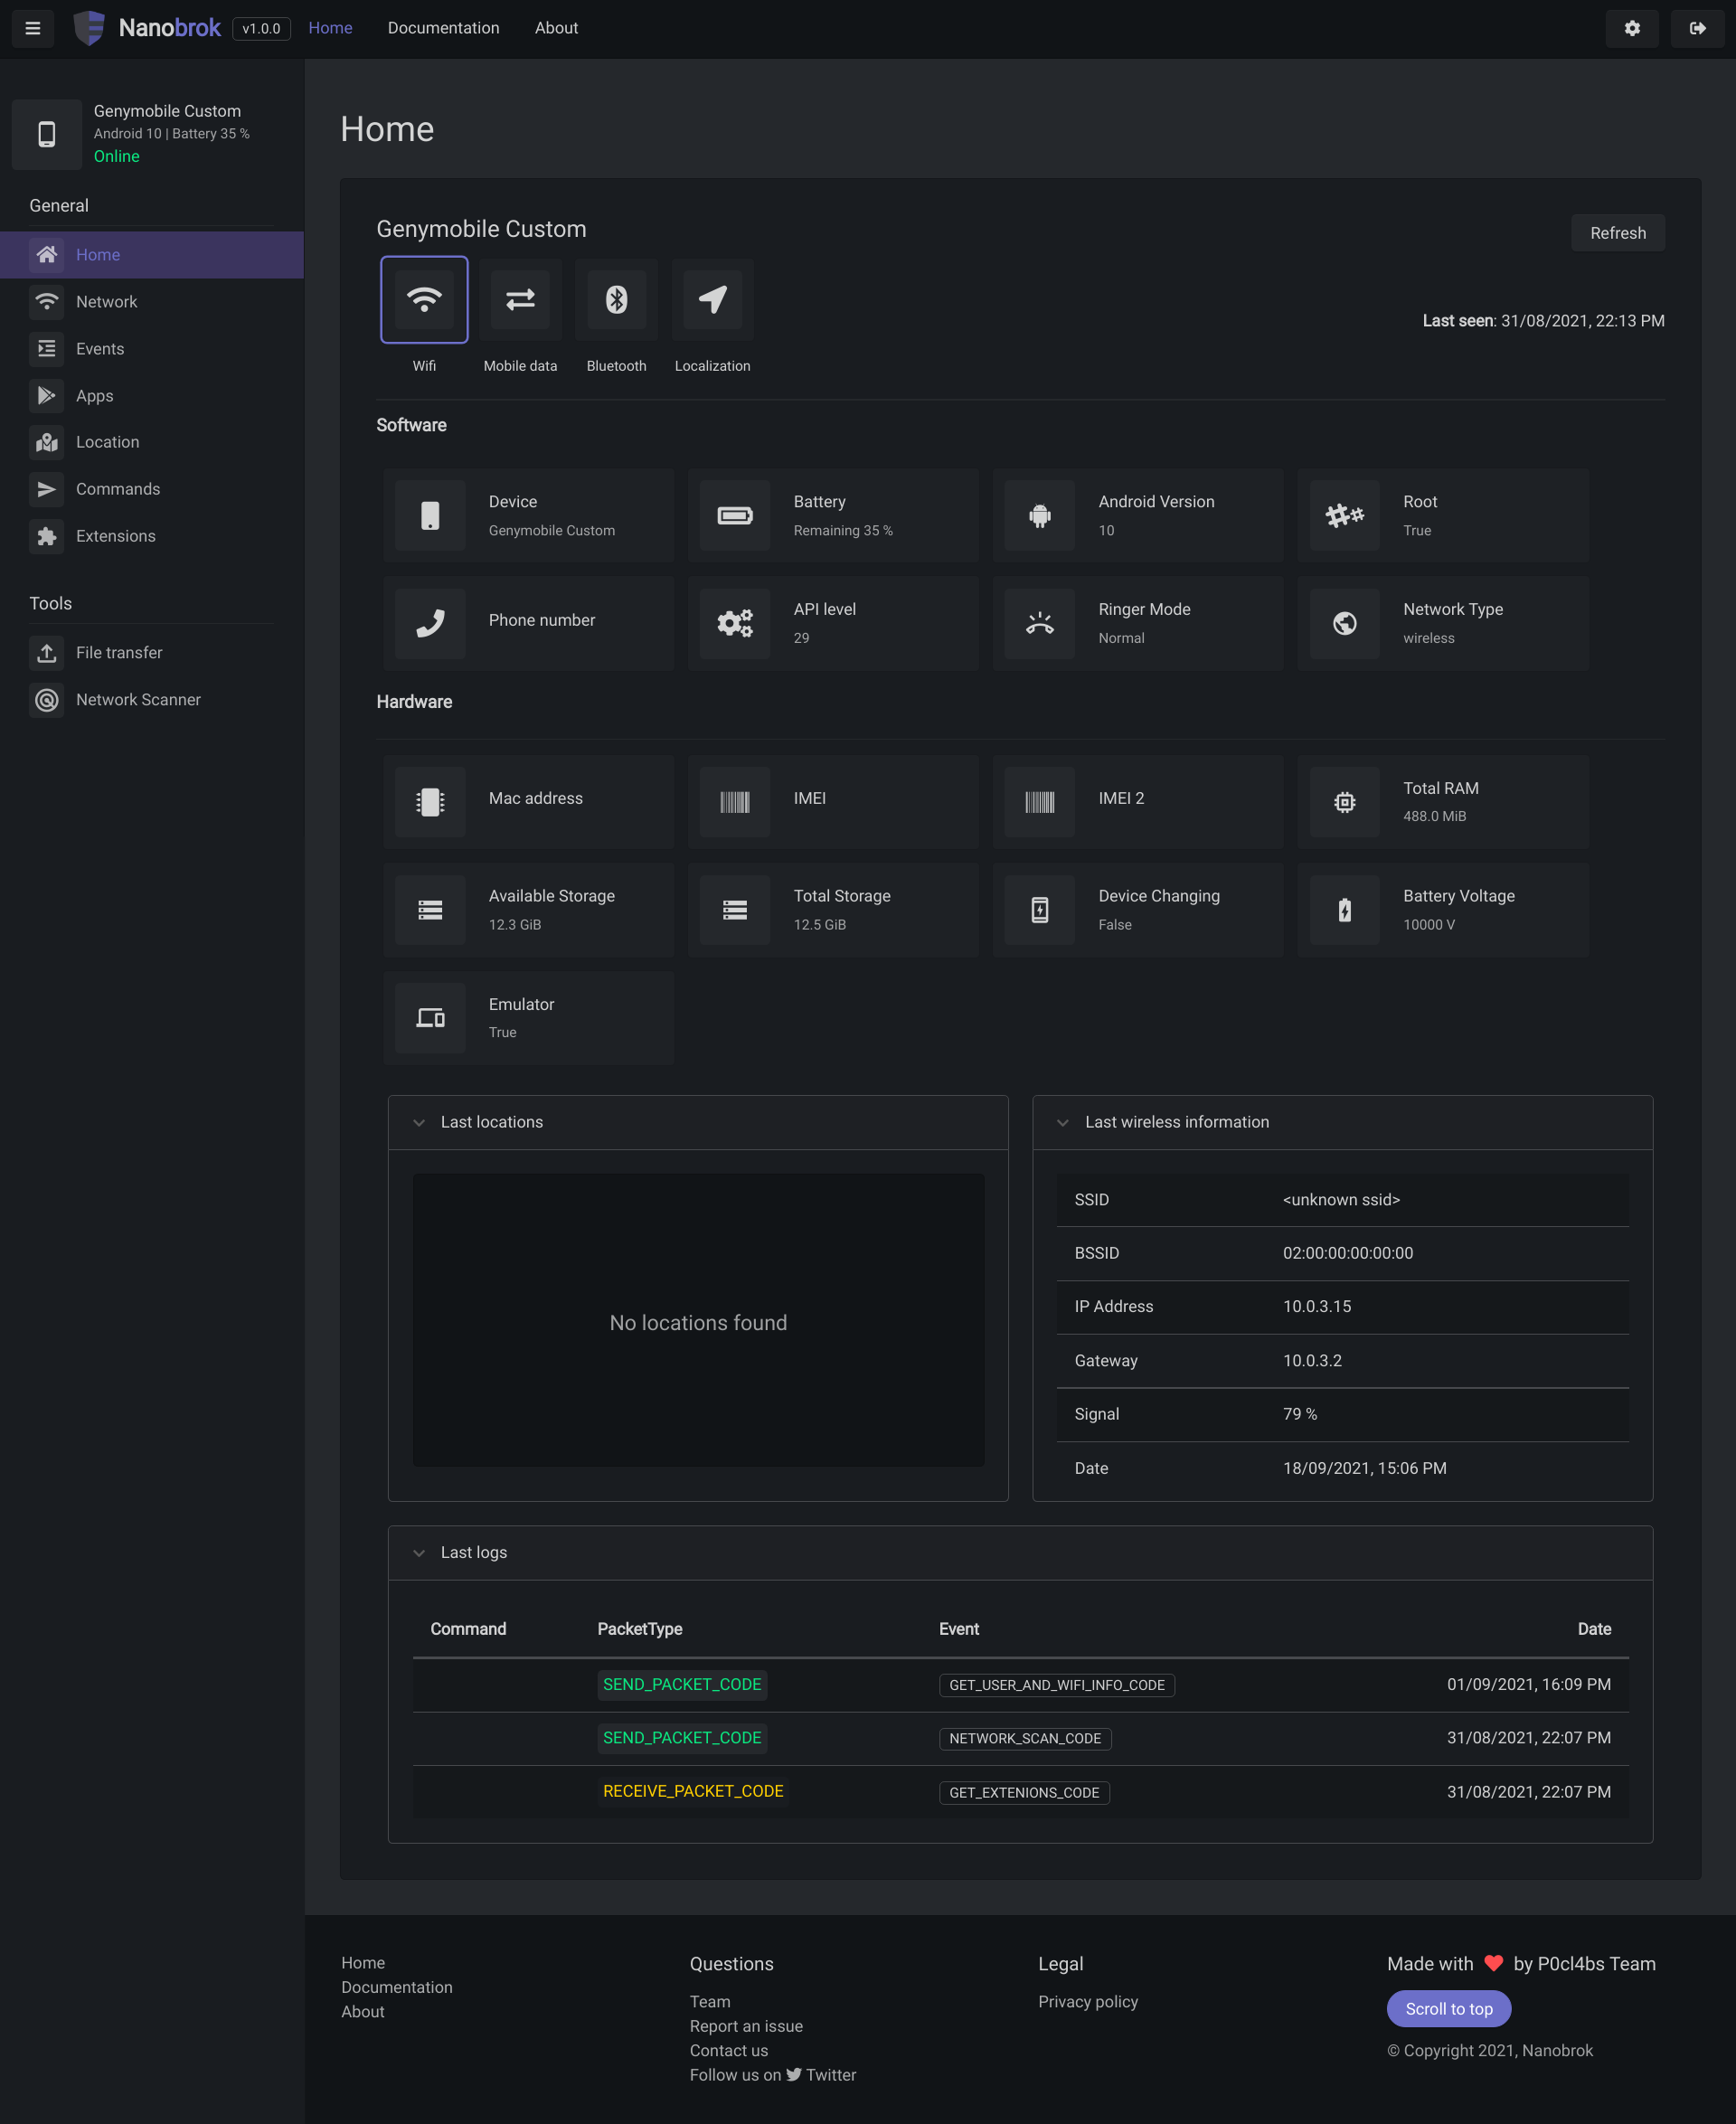
Web Service write in Python for control and protect your android device remotely.

Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…

Python-based proof-of-concept exploit for CVE-2022-32548, an unauthenticated remote code execution vulnerability in DrayTek routers via buffer…

This exploit was created to exploit an XXE (XML External Entity). Through it, I read the backend code of the web service and found an endpoint where…

Proof-of-concept exploit for Apache mod_http2 double-free vulnerability (CVE-2026-23918) with recon, exploit, and RCE risk assessment phases.

CVE-2015-3224 Exploit - Rails Web Console RCE

Unauthenticated arbitrary file upload on Honeywell PD45 web admin (firmware F10.19.010040–before F10.22.030745) leading to RCE. Python check/exploit…

complex webshell manager, quasi-http botnet.

CVE-2019-0708 C#验证漏洞