
CVE-2019-19609
 glowbase/cve-2019-19609
Python exploit script targeting unauthenticated remote code execution in Strapi CMS 3.0.0-beta.17.4 via CVE-2019-18818 and CVE-2019-19609, delivering…
exploitationpenetration-testingremote-access-tool+2
2
glowbase/cve-2019-19609Python exploit script targeting unauthenticated remote code execution in Strapi CMS 3.0.0-beta.17.4 via CVE-2019-18818 and CVE-2019-19609, delivering…
 diegaccio/craft-cms-exploit
Python exploit for Craft CMS CVE-2023-41892 Remote Code Execution vulnerability, delivering a PHP reverse shell for authorized penetration testing.
 h3x0v3rl0rd/cve-2018-16763
Python-based remote code execution exploit targeting fuel CMS 1.4.1, enabling authenticated attackers to execute arbitrary commands on vulnerable web…
 ajdumanhug/cve-2022-42092
CVE-2023-46818 Python3 Exploit for Backdrop CMS <= 1.22.0 Authenticated Remote Command Execution (RCE)
 m4rm0k/cve-2019-16113
Bludit 3.9.2 - Remote command execution - CVE-2019-16113
 khush-613/cve-2026-44011-poc
Python proof-of-concept exploit for CVE-2026-44011, an authenticated RCE in Craft CMS via Yii behavior injection, with two-stage command output…
 vitobonetti/cve-2018-16763
Fuel CMS 1.4.1 - Remote Code Execution - Python 3.x
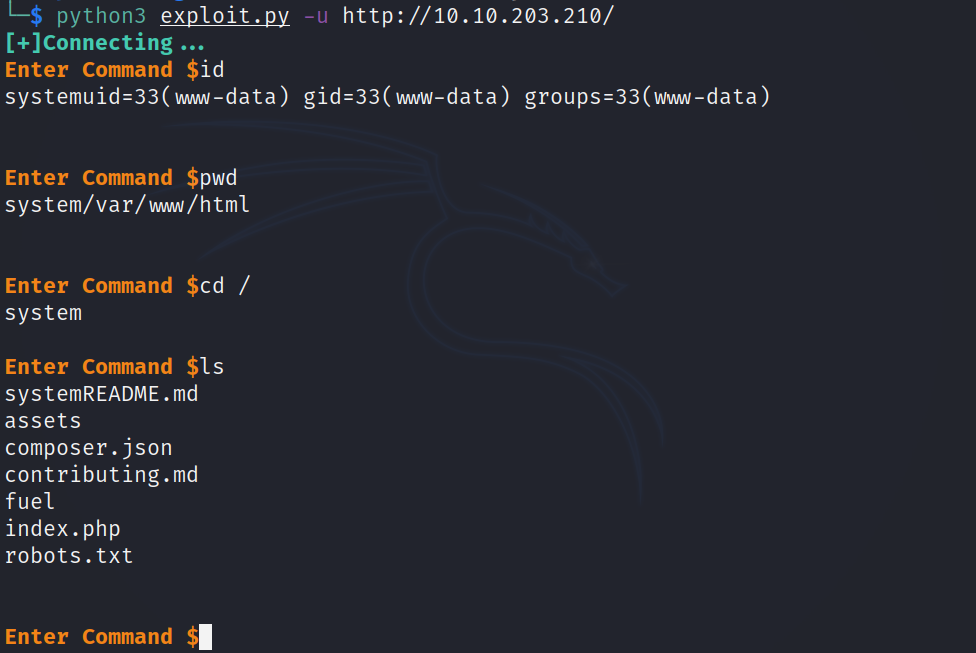 padsalatushal/cve-2018-16763
Fuel CMS 1.4.1 - Remote Code Execution
 b1d0ws/exploit-cve-2018-7448
Python script for CMS Made Simple 2.1.6 - Remote Code Execution.
 0asylum/cve-2026-31857
CraftCMS has an RCE vulnerability via relational conditionals in the control panel
 mbadanoiu/cve-2022-40635
CVE-2022-40635: Groovy Sandbox Bypass in CrafterCMS
 vidura2/cve-2024-46986
Automated Python exploit for Camaleon CMS arbitrary file upload vulnerability (CVE-2024-46986). Supports reverse shell and command execution payloads…
 raffli-dev/cve-2023-41425
Exploit for Wonder CMS XSS to RCE (CVE-2023-41425) with theme upload and reverse shell payloads.
 swammers8/wbce-v1.6.3-authenticated-rce
Authenticated RCE exploit for WBCE CMS <= 1.6.3 that creates a malicious module zip with a PHP reverse shell and netcat listener.
 can0i0ever0enter/cve-2023-45878
Python exploit for CVE-2023-45878, an unauthenticated arbitrary file upload in Gibbon CMS, enabling RCE via webshell upload and interactive shell…
 predyy/cve-2026-28695
Python PoC exploit for CVE-2026-28695, an authenticated blind RCE in Craft CMS that bypasses the create() BaseObject patch and spawns a reverse shell.
 p34nut2/cve-2025-32432-exploit-by-p34nut
Reliable CVE-2025-32432 pre-auth RCE exploit for Craft CMS 3.x/4.x/5.x, works where other public PoCs fail
 kaxm23/exploit_cms_fuel
Python3 exploit for Fuel CMS 1.4.1 Remote Code Execution (CVE-2018-16763) with Reverse Shell.