
LocalNet_Attacker
This is a project about attacking and gathering information of the windows machines which is connected in the same network by using java programs

This is a project about attacking and gathering information of the windows machines which is connected in the same network by using java programs

A PoC Java Stager which can download, compile, and execute a Java file in memory.

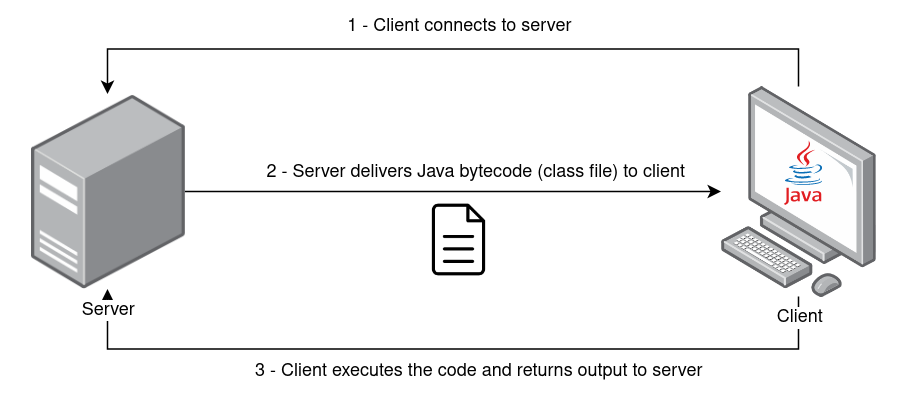
Client-server tool for remotely loading and executing Java bytecode via ClassLoader and Reflect API, with ChaCha20 encryption and keepalive…

This is a Java program that exploits Spring Break vulnerability (CVE-2017-8046).

CVE-2022-22963 is a vulnerability in the Spring Cloud Function Framework for Java that allows remote code execution. This python script will verify…

F5 BIG-IP iControl REST vulnerability RCE exploit with Java including a testing LAB

Python PoC exploiting CVE-2026-33439, a pre-auth RCE in OpenAM via Java deserialization of the jato.clientSession parameter, with interactive and…

Proof of concept for CVE-2026-33439, an unauthenticated RCE in OpenAM via Java deserialization

Proof-of-concept exploit for CVE-2025-30065 demonstrating remote class instantiation and SSRF via malicious Parquet files in Java applications.

Unauthenticated remote command execution in Papercut service allows an attacker to execute commands due to improper access controls in the…

Java deserialization exploit targeting Elasticsearch 1.5.2 transport protocol (port 9300) using Groovy MethodClosure chain for remote code execution…

CVE-2022-41678 是 Apache ActiveMQ 中的一个远程代码执行漏洞。该漏洞允许攻击者通过 JMX (Java Management Extensions) 接口修改 Log4j 配置或 JFR (Java Flight Recorder) 配置,从而写入恶意的 JSP…

Java GUI tool for exploiting CVE-2026-21962, an unauthenticated RCE in Oracle WebLogic Proxy Plug-In, enabling multi-target command execution via…

Automated PoC exploit for CVE-2026-6009, a Java deserialization RCE in Jaspersoft Reports <=7.0.3. Generates malicious .jasper payloads via ysoserial…

Java PoC for WebLogic CVE-2020-14645 Coherence deserialization RCE. Hosts a malicious class via LDAP and triggers remote code execution on vulnerable…

JSP-less Java Servlets Backdoor inspired by https://www.redteam-pentesting.de/files/redteam-jboss.tar.gz

Proof-of-concept exploit for BlueKeep (CVE-2019-0708) enabling remote code execution on Windows via RDP, with implementations in Python, Java, C++,…

IBM i DDM Unauthenticated RCE - Java Reverse Shell