

cve-2020-00796
 bsec404/cve-2020-00796
Python scanner to identify systems vulnerable to CVE-2020-0796 (SMBv3 RCE) by sending crafted negotiate requests and checking for the flaw.
exploitationnetwork-securitypenetration-testing+2
1
bsec404/cve-2020-00796Python scanner to identify systems vulnerable to CVE-2020-0796 (SMBv3 RCE) by sending crafted negotiate requests and checking for the flaw.
 nccgroup/gitpwnd
GitPwnd is a network penetration tool that lets you use a git repo for command and control of compromised machines
 sp00kyskelet0n/py-rdp-patcher
Python script that patches the termsrv.dll file on Windows to enable multiple concurrent RDP sessions, supporting Windows 10 versions 1703 through…
 an00byss/doublehop
A Tool to use PowerShell Remoting / WinRM to execute PowerShell commands on remote hosts through WinRM double hop technique.
 nullarray/autosploit
Automated Mass Exploiter
 synacktiv/ica2tcp
A SOCKS proxy for Citrix.
 jacobmisirian/dbltekgoippwn
Tool to check if an IP of a DblTek GoIP is vulnerable to a challenge-response login system, send SMS messages from the system, execute remote…
 livehybrid/poc-cribl-rce
CVE-2019-11076 - Cribl UI 1.5.0 allows remote attackers to run arbitrary commands via an unauthenticated web request
 mantvmass/react2shell
A CLI tool that exploits vulnerabilities in React Server Components and Server Actions (CVE-2025-55182, CVE-2025-66478) to achieve remote code…
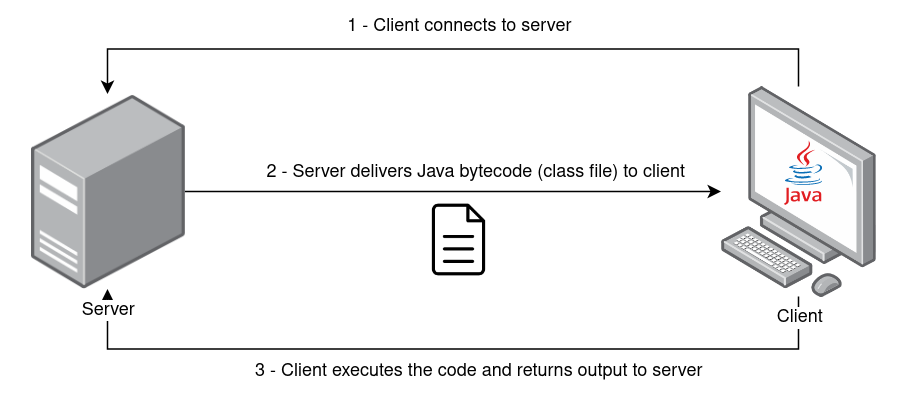 joaovarelas/java-remote-class-loader
Client-server tool for remotely loading and executing Java bytecode via ClassLoader and Reflect API, with ChaCha20 encryption and keepalive…
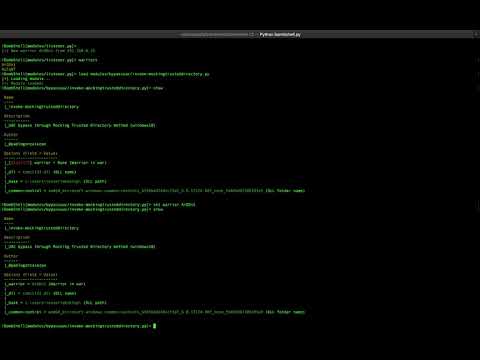 telefonica/ibombshell
Tool to deploy a post-exploitation prompt at any time
 abrewer251/cve-2025-32433_erlang-otp_poc
This script is a custom security tool designed to test for a critical pre-authentication vulnerability in systems running Erlang-based SSH servers
 odst-forge/cve-2025-32433_poc
This script is a custom security tool designed to test for a critical pre-authentication vulnerability in systems running Erlang-based SSH servers
 pentestical/cve-2021-22204
Shell script exploit for CVE-2021-22204 targeting Exiftool, generating a malicious .djvu file to achieve remote code execution on vulnerable systems.
 johenlastgen-jlg/cve-2026-18351
Mass exploit tool for CVE-2026-18351, an unauthenticated arbitrary file upload to RCE in Elementor Forms <= 1.6.0, with passive probing, shell…
 jptr218/tc_hack
Exploit tool for CVE-2017-12617 in Apache Tomcat, leveraging the PUT method to gain remote access to vulnerable servers via command-line interface.
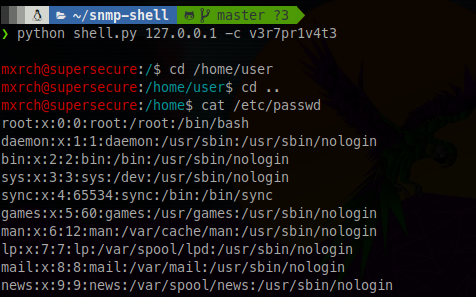 mxrch/snmp-shell
Shell Simulation over Net-SNMP with extend functionality
 cedowens/macshellswift
Proof of concept MacOS post exploitation tool written in Swift. Designed as a POC for blue teams to build macOS detections. Author: Cedric Owens