
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
37 results
Telegra_Csharp_C2 preview

Telegra_Csharp_C2

GitHubsf197/telegra_csharp_c2

Command and Control for C# Writing

command-and-controlpayload-generationpost-exploitation+2
674 years ago
SharpC2 preview

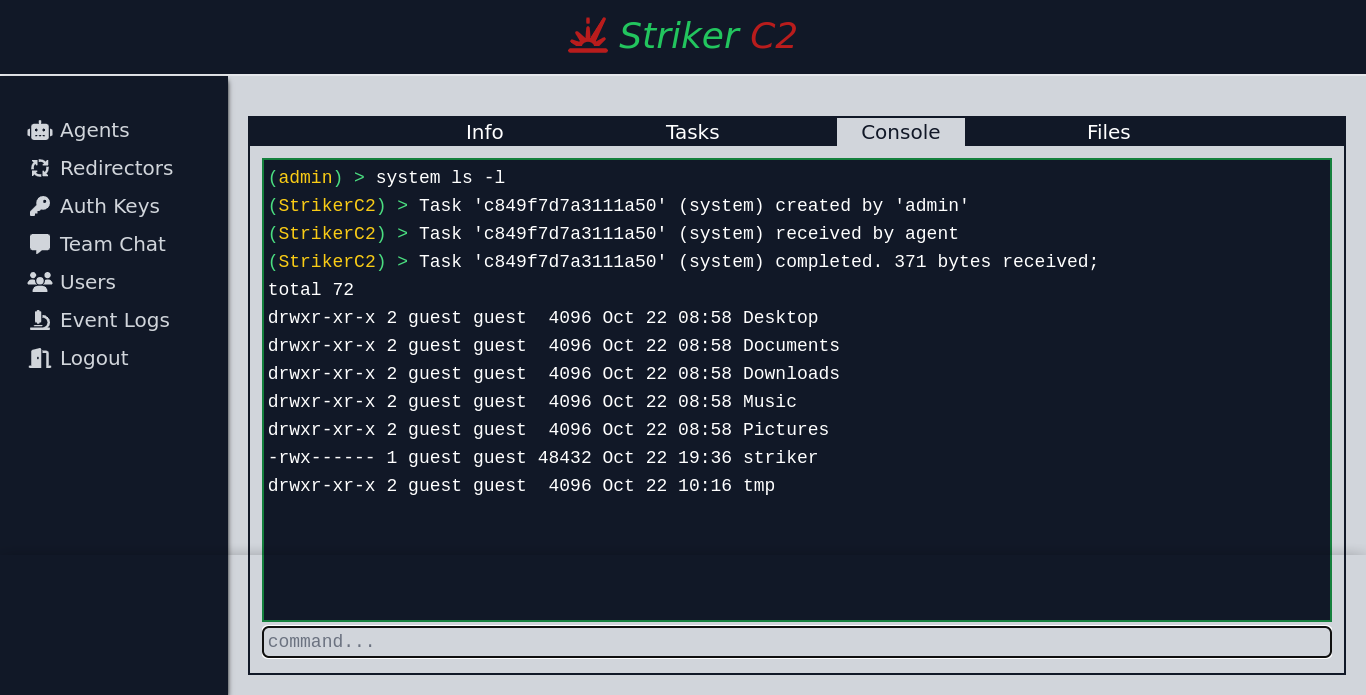
SharpC2

GitHubrasta-mouse/sharpc2

Command and Control Framework written in C#
command-and-controlpenetration-testingpost-exploitation+2
4313 years ago
Striker preview

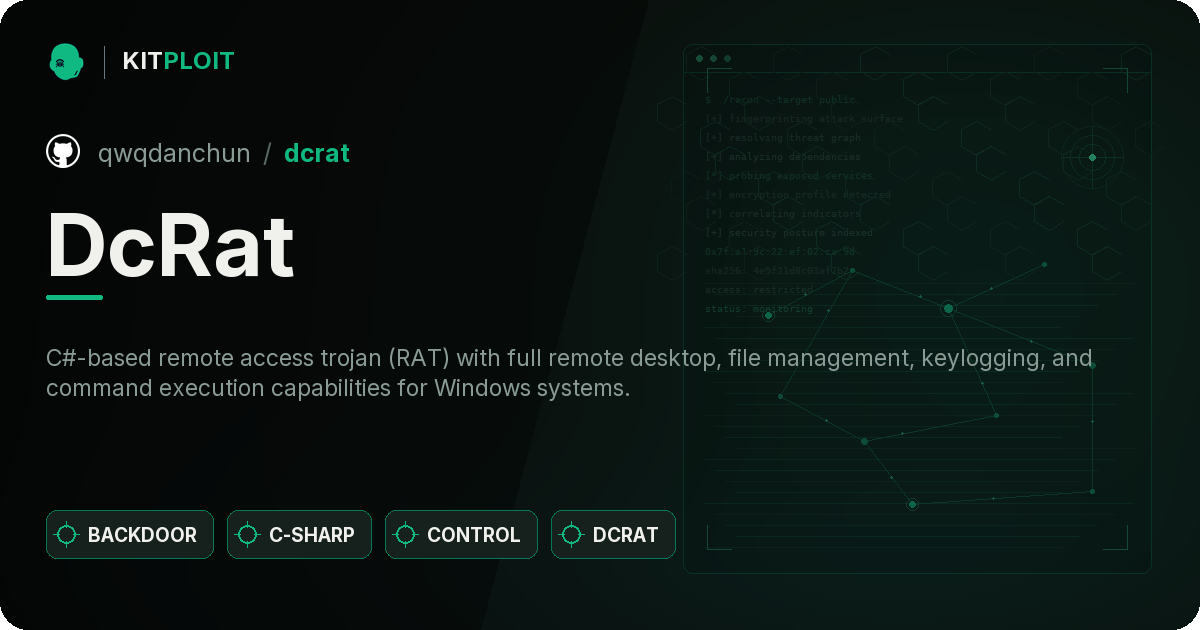
Striker

GitHub4g3nt47/striker

Multi-operator C2 framework with native C and Python agents, HTTP(S) channels, asynchronous tasking, and a reactive web UI for red team operations.
command-and-controlpayload-generationred-teaming+1
3003 years ago
DcRat preview
Archived

DcRat

GitHubqwqdanchun/dcrat

A simple remote tool in C#.

command-and-controldata-exfiltrationids-ips-evasion+9
1.0k4 years ago
AsyncRAT-C-Sharp preview

AsyncRAT-C-Sharp

GitHubnyan-x-cat/asyncrat-c-sharp

Open-Source Remote Administration Tool For Windows C# (RAT)
command-and-controldata-exfiltrationpassword-cracking+5
3.0k3 years ago
SharpWMI preview

SharpWMI

GitHubghostpack/sharpwmi

SharpWMI is a C# implementation of various WMI functionality.
command-and-controlinformation-gatheringlateral-movement+5
7675 years ago
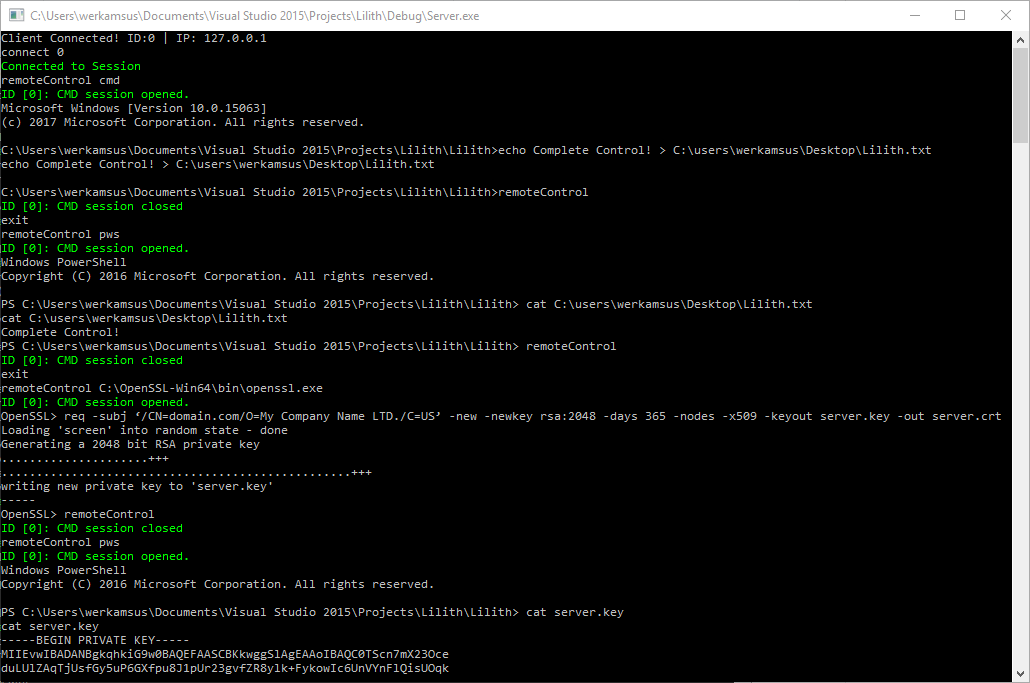
Lilith preview

Lilith

GitHubwerkamsus/lilith

Lilith - Foundational reverse engineering resource for cybersecurity entrepreneurs in C++
command-and-controlpayload-generationpenetration-testing+4
7487 years ago
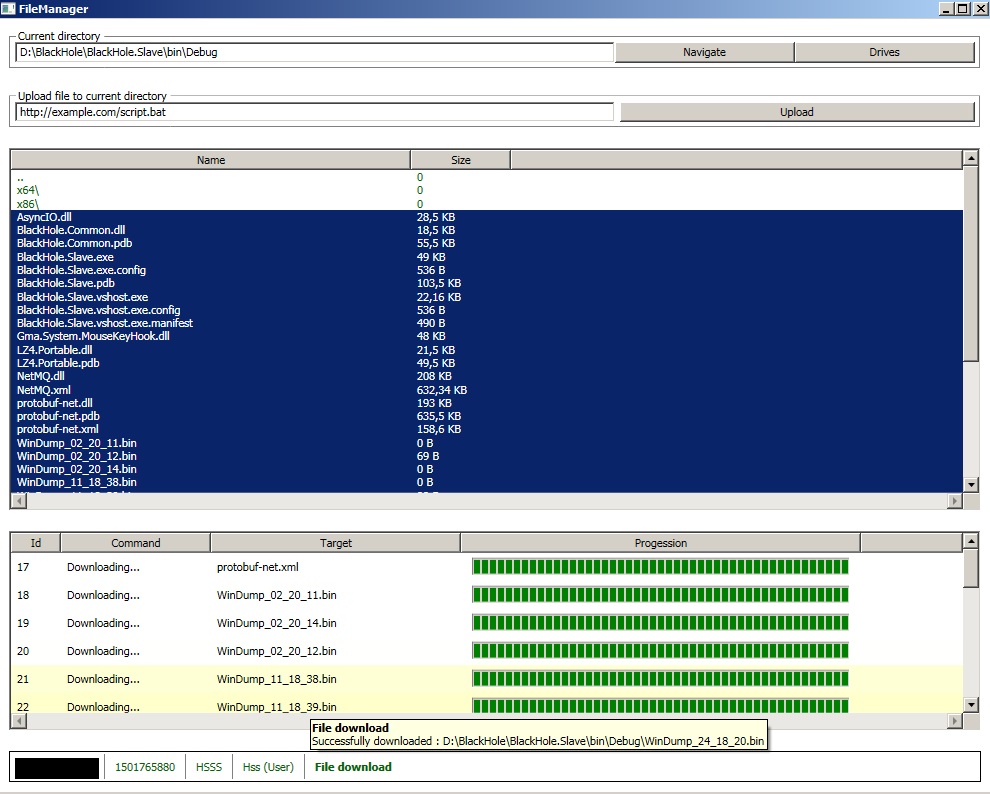
BlackHole preview

BlackHole

GitHubhussein-aitlahcen/blackhole

C# RAT (Remote Administration Tool)
command-and-controleducationpayload-development+5
3029 years ago
Vayne-RaT preview

Vayne-RaT

GitHubthem4hd1/vayne-rat

An Advanced C# .NET Rat, It’s Stable and Contains Many Features.
command-and-controlpassword-crackingpayload-generation+4
2738 years ago
CIMplant preview

CIMplant

GitHubredsiege/cimplant

C# port of WMImplant which uses either CIM or WMI to query remote systems
command-and-controlinformation-gatheringlateral-movement+4
2045 years ago
n00bRAT preview

n00bRAT

GitHubabhishekkr/n00brat

Remote Administration Toolkit (or Trojan) for POSiX (Linux/Unix) system working as a Web Service
command-and-controleducationfingerprint-spoofing+5
1767 years ago
sak1to-shell preview

sak1to-shell

GitHubd4rk007/sak1to-shell

Multi-threaded, multi-os/platform (Linux/Windows) c2 server and Windows reverse TCP shell client both written in C.

command-and-controlpayload-generationpost-exploitation+2
1204 years ago
R2Socks preview

R2Socks

GitHubivancabrera02/r2socks

SOCKS5 proxy tunneled through Cloudflare R2 object storage, with Python and dependency-free C++ agents relaying TCP traffic via encrypted R2 objects…
command-and-controldata-exfiltrationencryption-decryption-tools+5
391 month ago
teletunnel preview

teletunnel

GitHubmhdgning131/teletunnel

Bypassing EDR's with stealthy c++ telegram Bot and Telegram itself as C2 interface !
command-and-controldata-exfiltrationids-ips-evasion+7
457 months ago
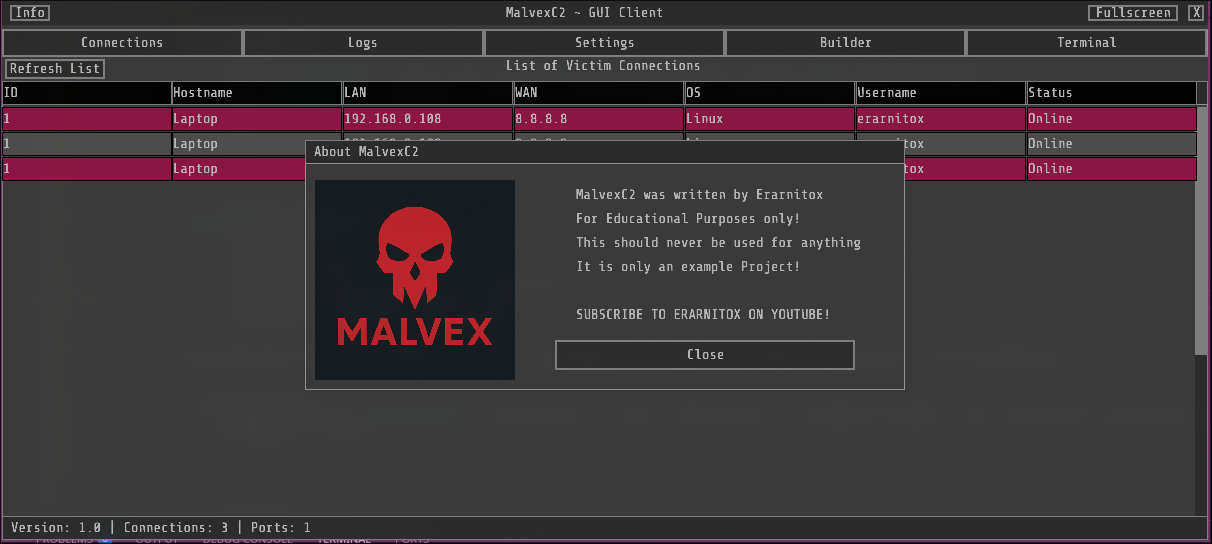
MalvexC2 preview

MalvexC2

GitHuberarnitox/malvexc2

A simple C2 Framework written in modern C++

command-and-controleducationexploit-frameworks+6
343 months ago
XeytanWin32-RAT preview

XeytanWin32-RAT

GitHubmelardev/xeytanwin32-rat

WORK IN PROGRESS. RAT written in C++ using Win32 API
command-and-controldata-exfiltrationexploitation+8
207 years ago
CVE-2019-3980 preview

CVE-2019-3980

GitHubwarferik/cve-2019-3980

Proof-of-concept exploit for CVE-2019-3980 enabling remote command execution via custom C# payload with HTTP callback for output retrieval.
command-and-controlexploitationpayload-generation+3
185 years ago
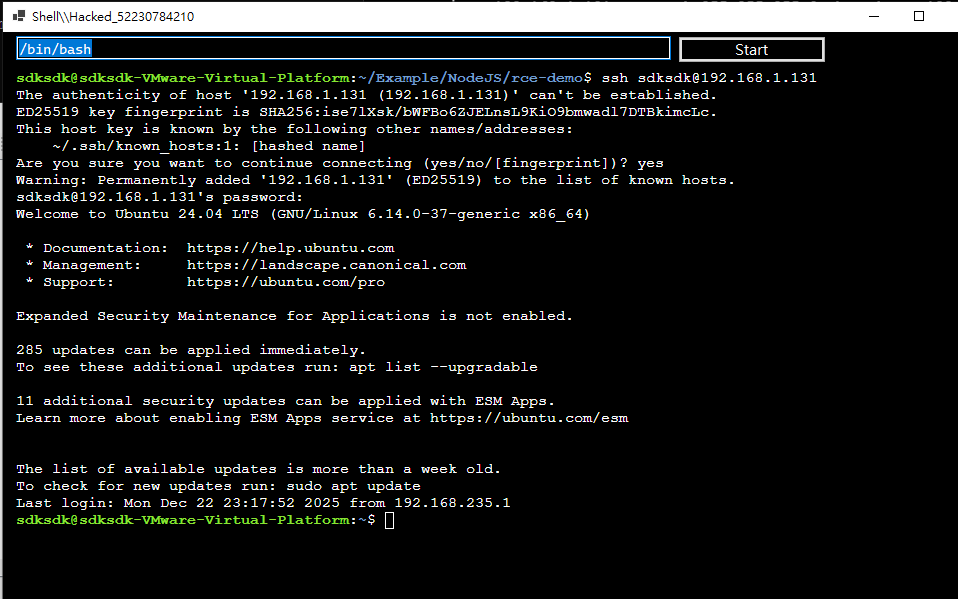
Eden-RAT preview

Eden-RAT

GitHubiss4cf0ng/eden-rat

An open-source Linux GUI-based Remote Access Tool developed in C# with a Python payload, intended for legitimate penetration testing and…

command-and-controlencryption-decryption-toolsexploitation+5
337 months ago
Previous123Next