
CANalyse
 kartheeklade/canalyse
A vehicle network analysis and attack tool.
exploitationhardware-hackingremote-access-tool
kartheeklade/canalyseA vehicle network analysis and attack tool.
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
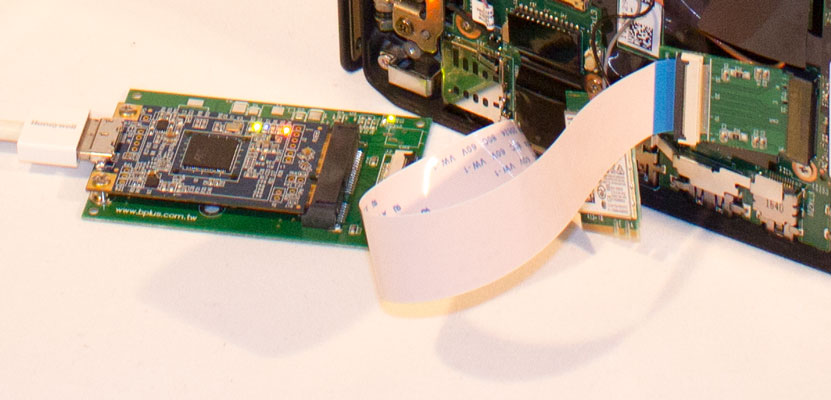 ufrisk/pcileech
Direct Memory Access (DMA) Attack Software
 fmd-foss/fmd-android
Find your device and control it remotely. Works over SMS, instant messengers, or FMD Server's web interface. A secure open source alternative to…
 casp3r0x0/cve-2026-34159
0 Click RCE exploit for CVE-2026-34159 Lama.cpp RPC server
 xorrior/apfell-chrome-extension-c2server
Apfell C2 Server for the Google Chrome Extension Payload
 fixyourface/springbreakpoc
PoC for SpringBreak (CVE-2017-8046)
 0xryuk/cve-2022-24637
Open Web Analytics 1.7.3 - Remote Code Execution Exploit v2

 monjheta/cve-2020-0796
Proof-of-concept remote code execution exploit for CVE-2020-0796 (SMBGhost) targeting unpatched Windows 10 1903/1909. Delivers a reverse shell via…
 jamf/cve-2020-0796-rce-poc
CVE-2020-0796 Remote Code Execution POC
 dinosn/cve-2026-25243
CVE-2026-25243 — Redis RESTORE zipmap double-free → remote code execution (ASLR on).
 dorkerdevil/cve-2020-28018
Exploit for Exim Use-After-Free (CVE-2020-28018) achieving remote code execution via memory corruption primitives, including arbitrary read/write and…
 s4dbrd/cve-2020-9496
Exploit script for Apache OFBiz CVE-2020-9496 unsafe deserialization vulnerability, enabling remote code execution via crafted XML-RPC requests with…
 hook-s3c/cve-2019-0708-poc
proof of concept exploit for Microsoft Windows 7 and Server 2008 RDP vulnerability
 umutcamliyurt/pingrat
ICMP-based command-and-control tool that tunnels C2 traffic through firewalls using ping payloads, undetectable by most AV/EDR solutions.
 4m3rr0r/cve-2025-47812-poc
Wing FTP Server Remote Code Execution (RCE) Exploit (CVE-2025-47812)