
shepard
 d3adzo/shepard
In progress persistent download/upload/execution tool using Windows BITS.
command-and-controldata-exfiltrationpersistence-mechanisms+3
41
d3adzo/shepardIn progress persistent download/upload/execution tool using Windows BITS.
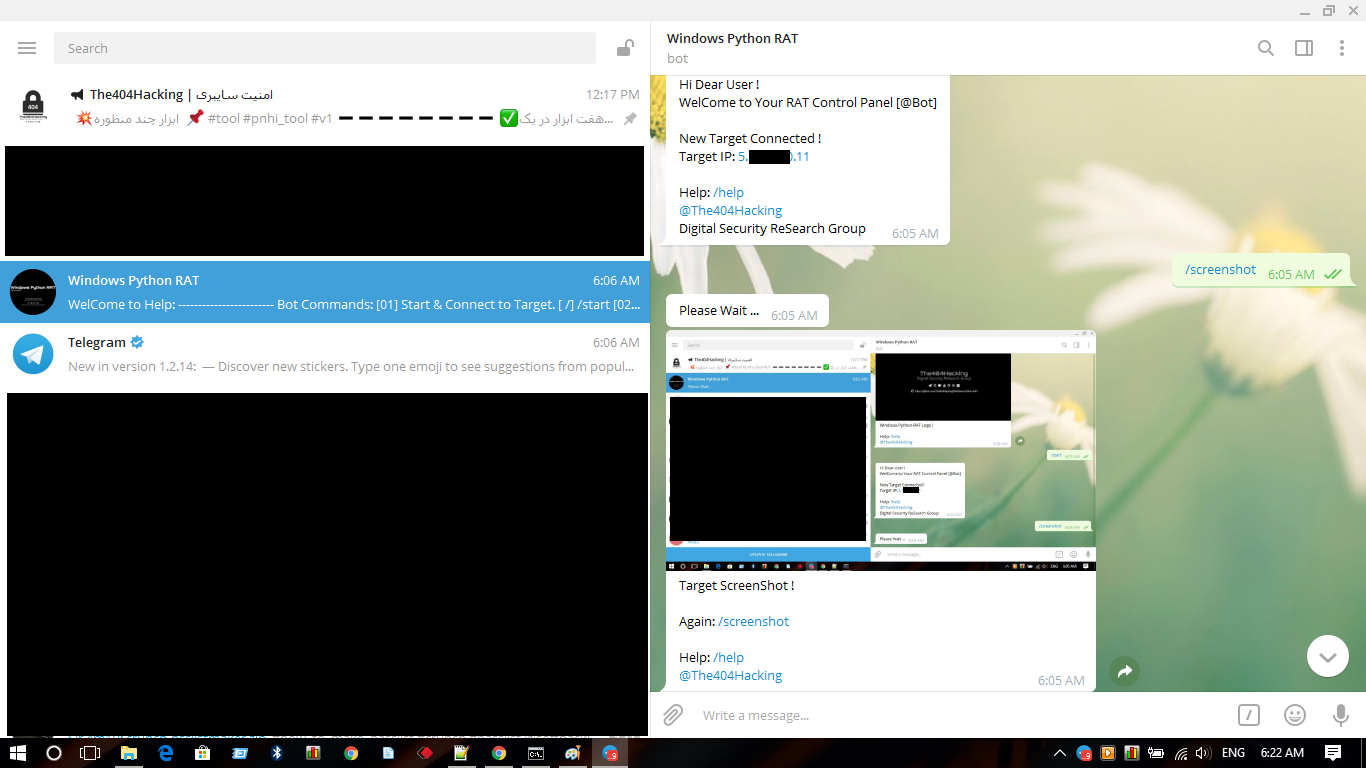 the404hacking/windows-python-rat
A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.
 x-projetion/cve-2023-4596-vulnerable-exploit-and-checker-version
CVE-2023-4596 Vulnerable Exploit and Checker Version
 johenlastgen-jlg/cve-2026-18351
Mass exploit tool for CVE-2026-18351, an unauthenticated arbitrary file upload to RCE in Elementor Forms <= 1.6.0, with passive probing, shell…
 0xgh057r3c0n/cve-2026-22812
Python exploit tool for OpenCode RCE (CVE-2026-22812) providing command execution, file read/write/upload/download, and interactive shell for…
 filipstudeny/-cve-2014-6271-shellshock-remote-command-injection-
[CVE-2014-6271] Apache Shellshock Remote Command Injection tool for quick reverse shell and file browsing
 yasserbdj96/hiphp
PHP-based backdoor tool for remote website control via HTTP/HTTPS. Enables file management, command execution, and Tor connectivity with…
 joelgmsec/pyshell
Multi-platform Python webshell providing remote shell access on web servers with command history, file upload/download, and directory traversal…
 joelgmsec/http-shell
Multiplatform HTTP reverse shell providing a shell-like interface over HTTP, with file upload/download, command history, auto-reconnection, and sudo…
 francescobrina/hfs-cve-2014-6287-exploit
Python-based exploit for CVE-2014-6287 in HTTP File Server 2.3.x, delivering a reverse shell via Base64-encoded PowerShell payload for authorized…
 zorejt/rust_cve-2025-55182
Rust-based exploit tool for CVE-2025-55182, enabling remote code execution on react-server-dom-webpack servers via crafted multipart requests with…
 jakabakos/cve-2023-26360-adobe-coldfusion-rce-exploit
Python exploit script for remote file read and command execution targeting Adobe ColdFusion vulnerabilities CVE-2023-26359, CVE-2023-26360, and…
 ajdumanhug/cve-2022-42092
CVE-2023-46818 Python3 Exploit for Backdrop CMS <= 1.22.0 Authenticated Remote Command Execution (RCE)
 amitlttwo/cve-2022-1388
Python-based exploit for CVE-2022-1388, an F5 BIG-IP iControl REST authentication bypass leading to remote code execution. Supports single URL,…
 rohmatariow/cve-2026-22812-exploit
Exploitation toolkit for CVE-2026-22812 (OpenCode unauthenticated RCE) providing interactive shell, arbitrary command execution, file…
 ltvthang/cve-2020-5903
Exploit for CVE-2020-5902 targeting F5 BIG-IP RCE via path traversal and JDBC deserialization, enabling command execution, file read/write, and…
 sashka3076/f5-big-ip-exploit
CVE-2022-1388
 davidtavarez/cve-2015-3306
Exploit for CVE-2015-3306 targeting ProFTPd 1.3.5 with mod_copy, enabling remote file copy and command execution on vulnerable Debian systems.