
CVE-2023-41425-WonderCMS-Authenticated-RCE
 diegomjx/cve-2023-41425-wondercms-authenticated-rce
Xss injection, WonderCMS 3.2.0 -3.4.2
educationexploitationpayload-generation+4
diegomjx/cve-2023-41425-wondercms-authenticated-rceXss injection, WonderCMS 3.2.0 -3.4.2
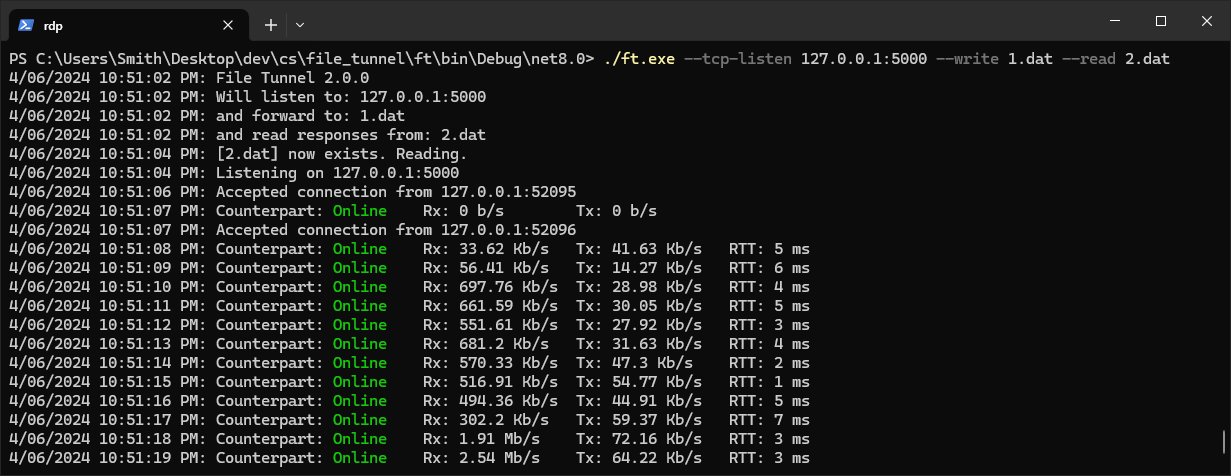 fiddyschmitt/file-tunnel
Tunnel TCP connections through a file
 adhikara13/cve-2023-24489-sharefile
This project is a Python script that exploits the CVE-2023-24489 vulnerability in ShareFile. It allows remote command execution on the target server.…
 soliux/cve-2021-41773
On the 11/11/21 the apache 2.4.49-2.4.50 remote command execution POC has been published online and this is a loader so that you can mass exploit…
 websecnl/cve-2022-26809
Remote Code Execution Exploit in the RPC Library
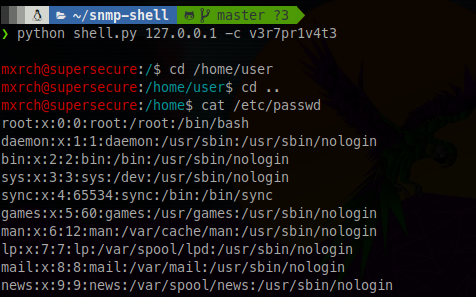 mxrch/snmp-shell
Shell Simulation over Net-SNMP with extend functionality
 lautarovculic/ioscpy
Now you can mirror and control your jailbroken iPhone over USB
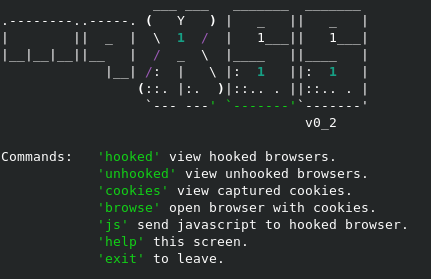 grampae/mqxss
Hooked browser communication over MQTT
 junnythemarksman/cve-2024-24590
Deserialization of untrusted data can occur in versions 0.17.0 to 1.14.2 of the client SDK of Allegro AI’s ClearML platform, enabling a maliciously…
 epinna/weevely3
Weaponized web shell
 orangmuda/cve-2021-27651
bypass all stages of the password reset flow
 bishopfox/sliver
Adversary Emulation Framework
 boroeurnprach/cve-2026-23744-poc
CVE-2026-23744 - Versions 1.4.2 and earlier of MCPJam inspector are vulnerable to remote code execution (RCE). Because the tool listens on 0.0.0.0 by…
 bytereaper77/webmin_exploit_reverse_shell
A simple C-based vulnerability in Webmin versions 1.890 to 1.920
 ziad-sakr/chamilo-cve-2023-4220-exploit
This is an Exploit for Unrestricted file upload in big file upload functionality in Chamilo-LMS for this location…
 gotr00t0day/cve-2022-1388
A remote code execution vulnerability exists in the iControl REST API feature of F5's BIG-IP product. An unauthenticated, remote attacker can exploit…
 quinnbast/malicious-mcp
A Proof-of-concept repository showing how an untrusted MCP server can steal literally everything...
 cotherm/cve-2025-25705
Proof-of-concept exploit for authenticated remote code execution via command injection in ProApps Enterprise Appliance ping functionality, with…