
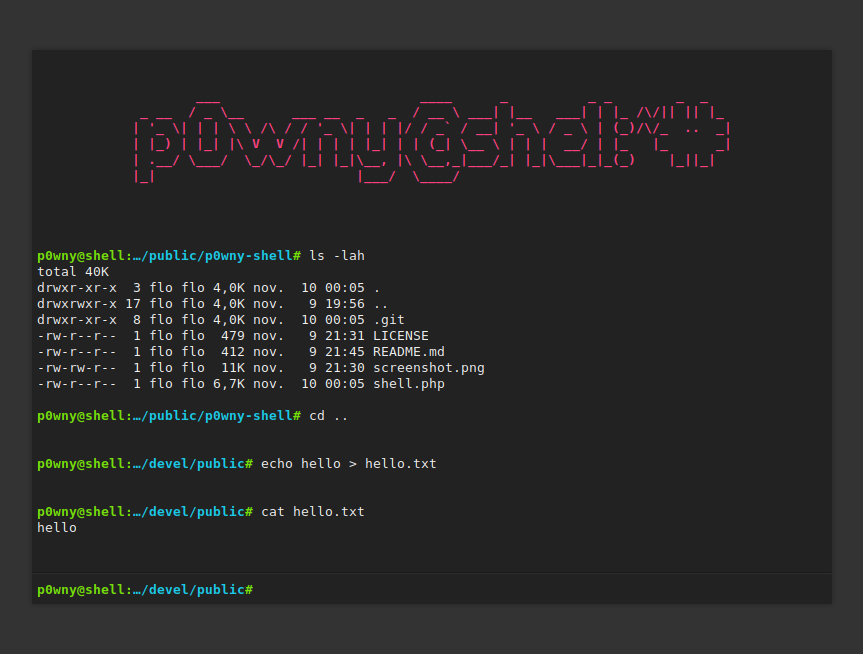
p0wny-shell
 flozz/p0wny-shell
Single-file PHP shell
penetration-testingremote-access-toolweb-application-exploitation
flozz/p0wny-shellSingle-file PHP shell
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
 note0577/cve-2019-12840-nodejs-exploit
Authenticated Remote Command Execution - Webmin <= 1.910
 touchmycrazyredhat/cve-2022-27925-revshell
Python exploit for CVE-2022-27925 targeting Zimbra Collaboration Suite, enabling unauthenticated remote code execution and reverse shell delivery.
 mindflarex/cve-2025-61882-poc
Exploit for CVE-2025-61882, a critical pre-auth RCE in Oracle E-Business Suite. Combines SSRF, CRLF injection, HTTP smuggling, and XSLT injection for…
 huahuatzt/cve-2022-27925
Unauthenticated remote code execution exploit for Zimbra Collaboration Suite (CVE-2022-27925). Delivers a reverse shell payload to compromise…
 runik/harmonic
Suite for reverse shell handling geared toward working within the native shell