

sliver
 bishopfox/sliver
Adversary Emulation Framework
adversarial-attackcommand-and-controldata-exfiltration+16
bishopfox/sliverAdversary Emulation Framework
 brows3r/ipwn
A Framework meant for the exploitation of iOS devices.
 zr0n/react2shell
A complete framework for exploiting the vulnerability CVE-2025-55182
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 ekomssavior/airborne-poc
poc for CVE-2025-24252 & CVE-2025-24132
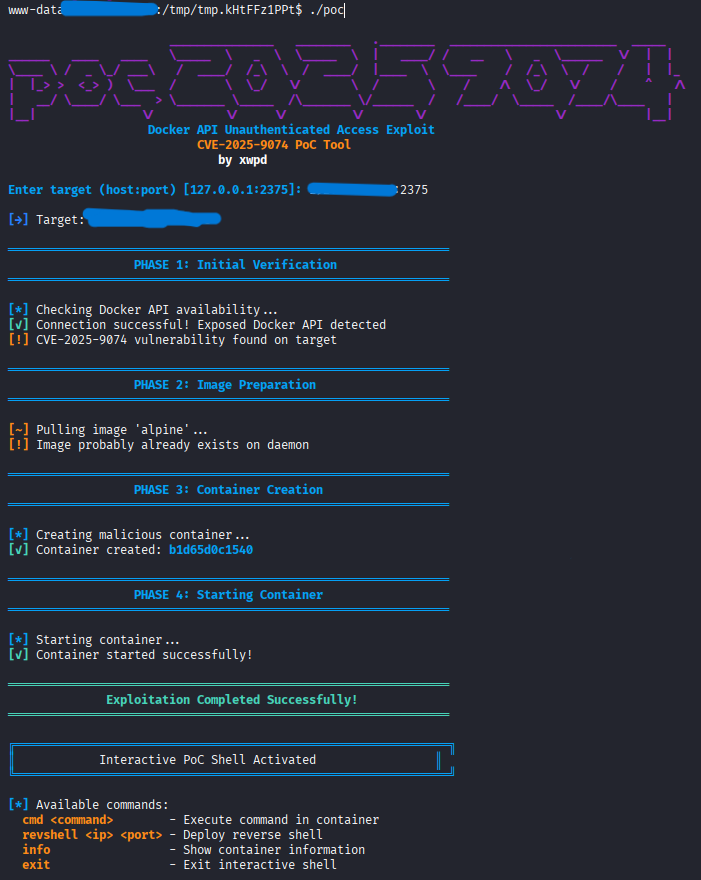 xwpdx0/poc-2025-9074
Docker API CVE-2025-9074 PoC (Proof-Of-Concept). A sophisticated exploitation framework for CVE-2025-9074, targeting unauthenticated Docker API…
 sh4den/cve-2022-36804
A loader for bitbucket 2022 rce (cve-2022-36804)
 calfcrusher/maccaronic2
A proof-of-concept Command & Control framework that utilizes the powerful AsyncSSH Python library which provides an asynchronous client and server…
 xm0kht4r/phoenix-framework
Post-exploitation framework that abuses trusted sites like Telegram and Discord for C2.
 xorrior/apfell-chrome-extension-c2server
Apfell C2 Server for the Google Chrome Extension Payload
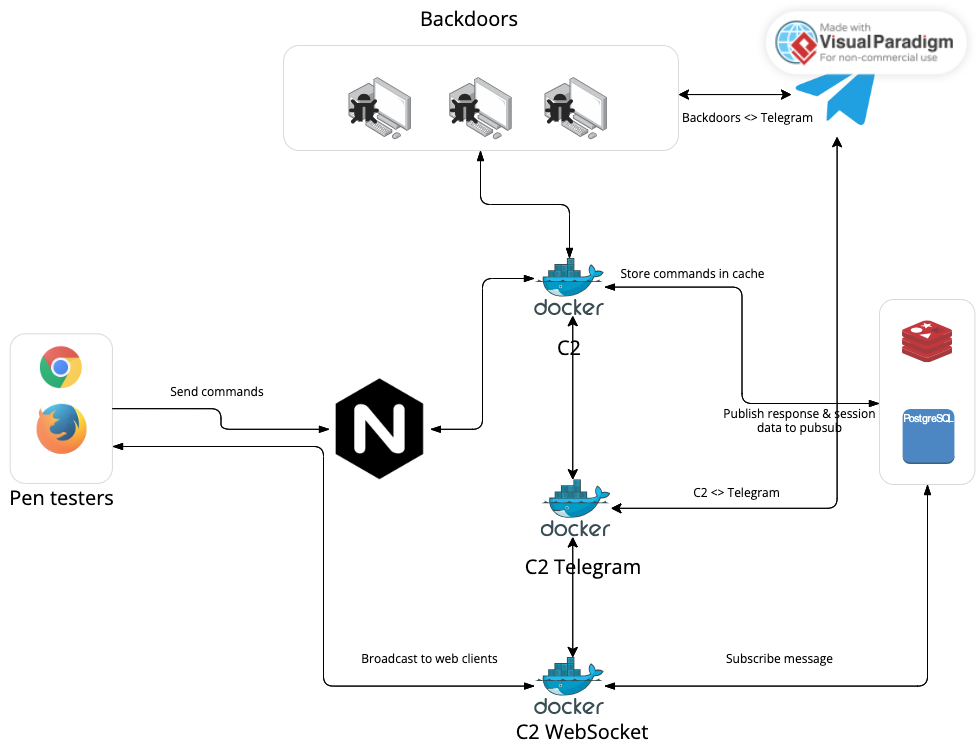 govindasamyarun/c2-cloud
The C2 Cloud is a robust web-based C2 framework, designed to simplify the life of penetration testers. It allows easy access to compromised…
 devianntsec/cve-2025-55182
Master's thesis research on CVE-2025-55182 (React2Shell). Modular exploitation framework with 6 attack scenarios (RCE, exfiltration, defacement),…
 mandiant/gopacket
A complete Go port of Impacket - 63 CLI tools and 24 libraries for Windows & Active Directory protocol attacks, compiled to a single dependency-free…
 wqsemc/cve-2019-0708
initial exploit for CVE-2019-0708, BlueKeep CVE-2019-0708 BlueKeep RDP Remote Windows Kernel Use After Free The RDP termdd.sys driver improperly…
 bolivarj/cve-2011-2523
Python exploit for vsftpd 2.3.4 - Backdoor Command Execution
 adyanamul/remote-code-execution-rce-exploit-bluekeep-cve-2019-0708-poc
Proof-of-concept exploit for BlueKeep (CVE-2019-0708) enabling remote code execution on Windows via RDP, with implementations in Python, Java, C++,…
 puppetma4ster/metasploit-wordpress-canto-exploit-rce
this is a metasploit exploit module for CVE-2024-25096 and CVE-2023-3452
 icmpoff/apache-2.4.49-2.4.50-traversal-remote-code-execution-exploit
This Metasploit module exploits an unauthenticated remote code execution vulnerability which exists in Apache version 2.4.49 (CVE-2021-41773). If…