Chamilo-LMS-Unauthenticated-File-Upload-CVE-2023-4220

Proof-of-concept exploit for CVE-2023-4220: unauthenticated file upload in Chamilo LMS enabling stored XSS and remote code execution via web shell…

Proof-of-concept exploit for CVE-2023-4220: unauthenticated file upload in Chamilo LMS enabling stored XSS and remote code execution via web shell…

Rejetto HTTP File Server (HFS) 2.x - Unauthenticated RCE exploit module (CVE-2024-23692)

Alex Reservations: Smart Restaurant Booking <= 2.2.3 - Authenticated (Admin+) Arbitrary File Upload

AI Feeds <= 1.0.11 - Unauthenticated Arbitrary File Upload

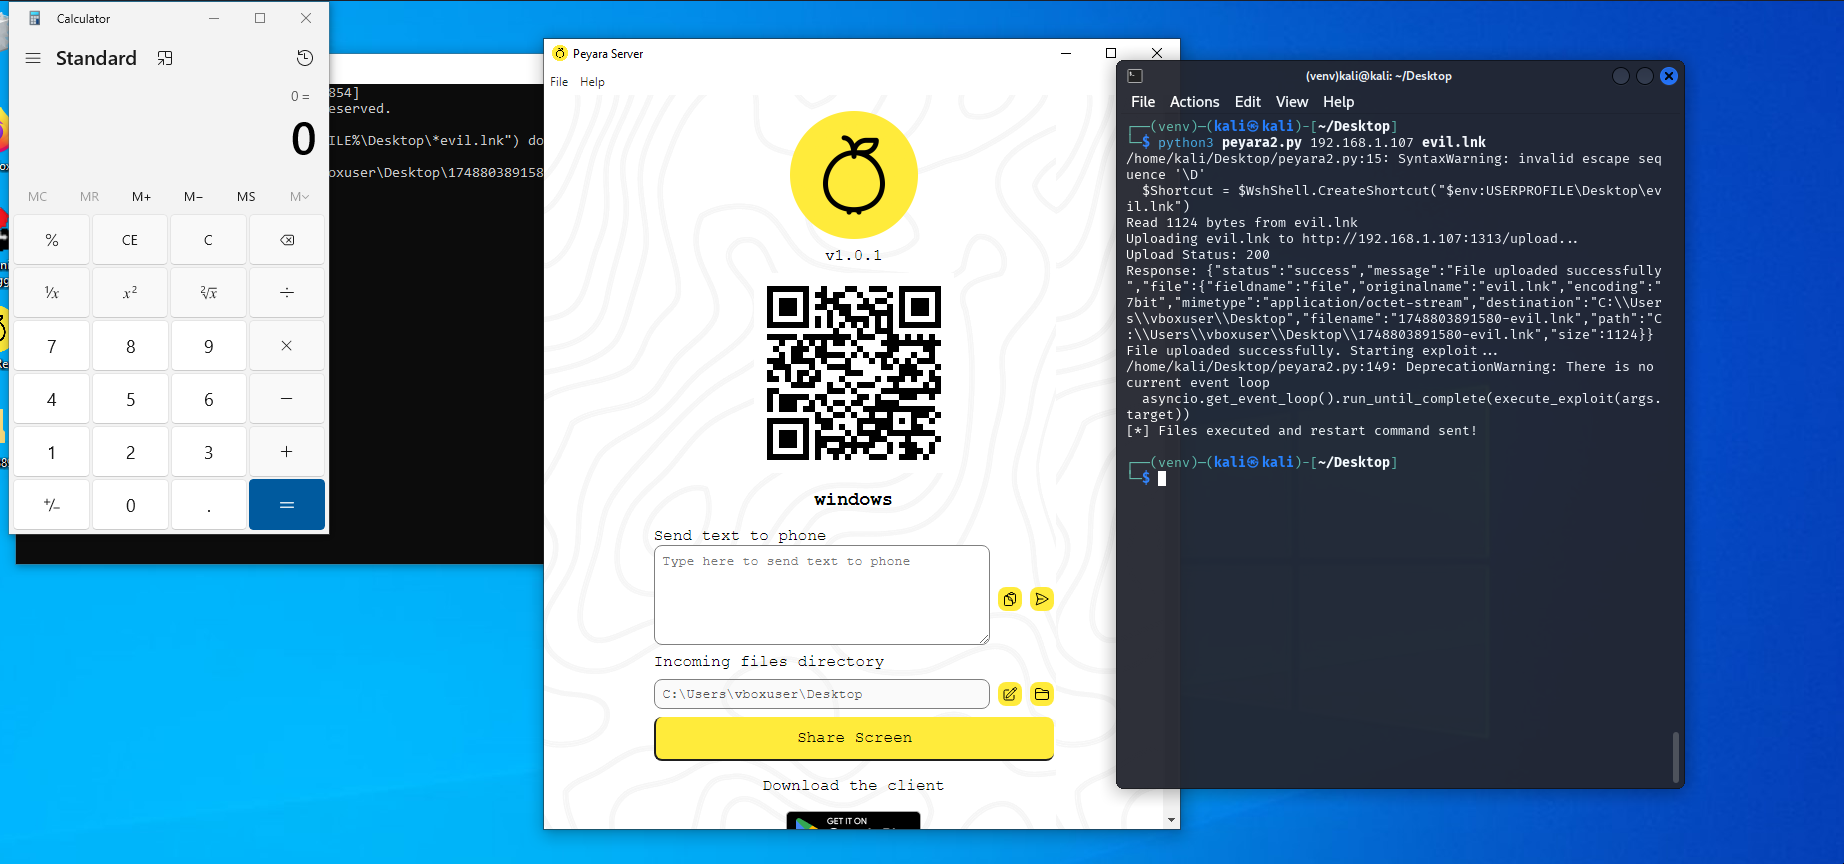
Peyara Remote Mouse Unauthenticated Arbitrary File Upload

Rejetto HFS (HTTP File Server) is a simple web file server that facilitates file sharing over a network or the internet.

Netcat with automated NAT traversal, secure P2P, and advanced features for shell access, file transfer, and network proxying.

Decrypted content of eqgrp-auction-file.tar.xz

Better Remote Access Trojan

React2Shell - CVE-2025-66478 RCE Exploit

POC exploit for CVE-2021-44967

RCE exploit for CVE-2018-14772

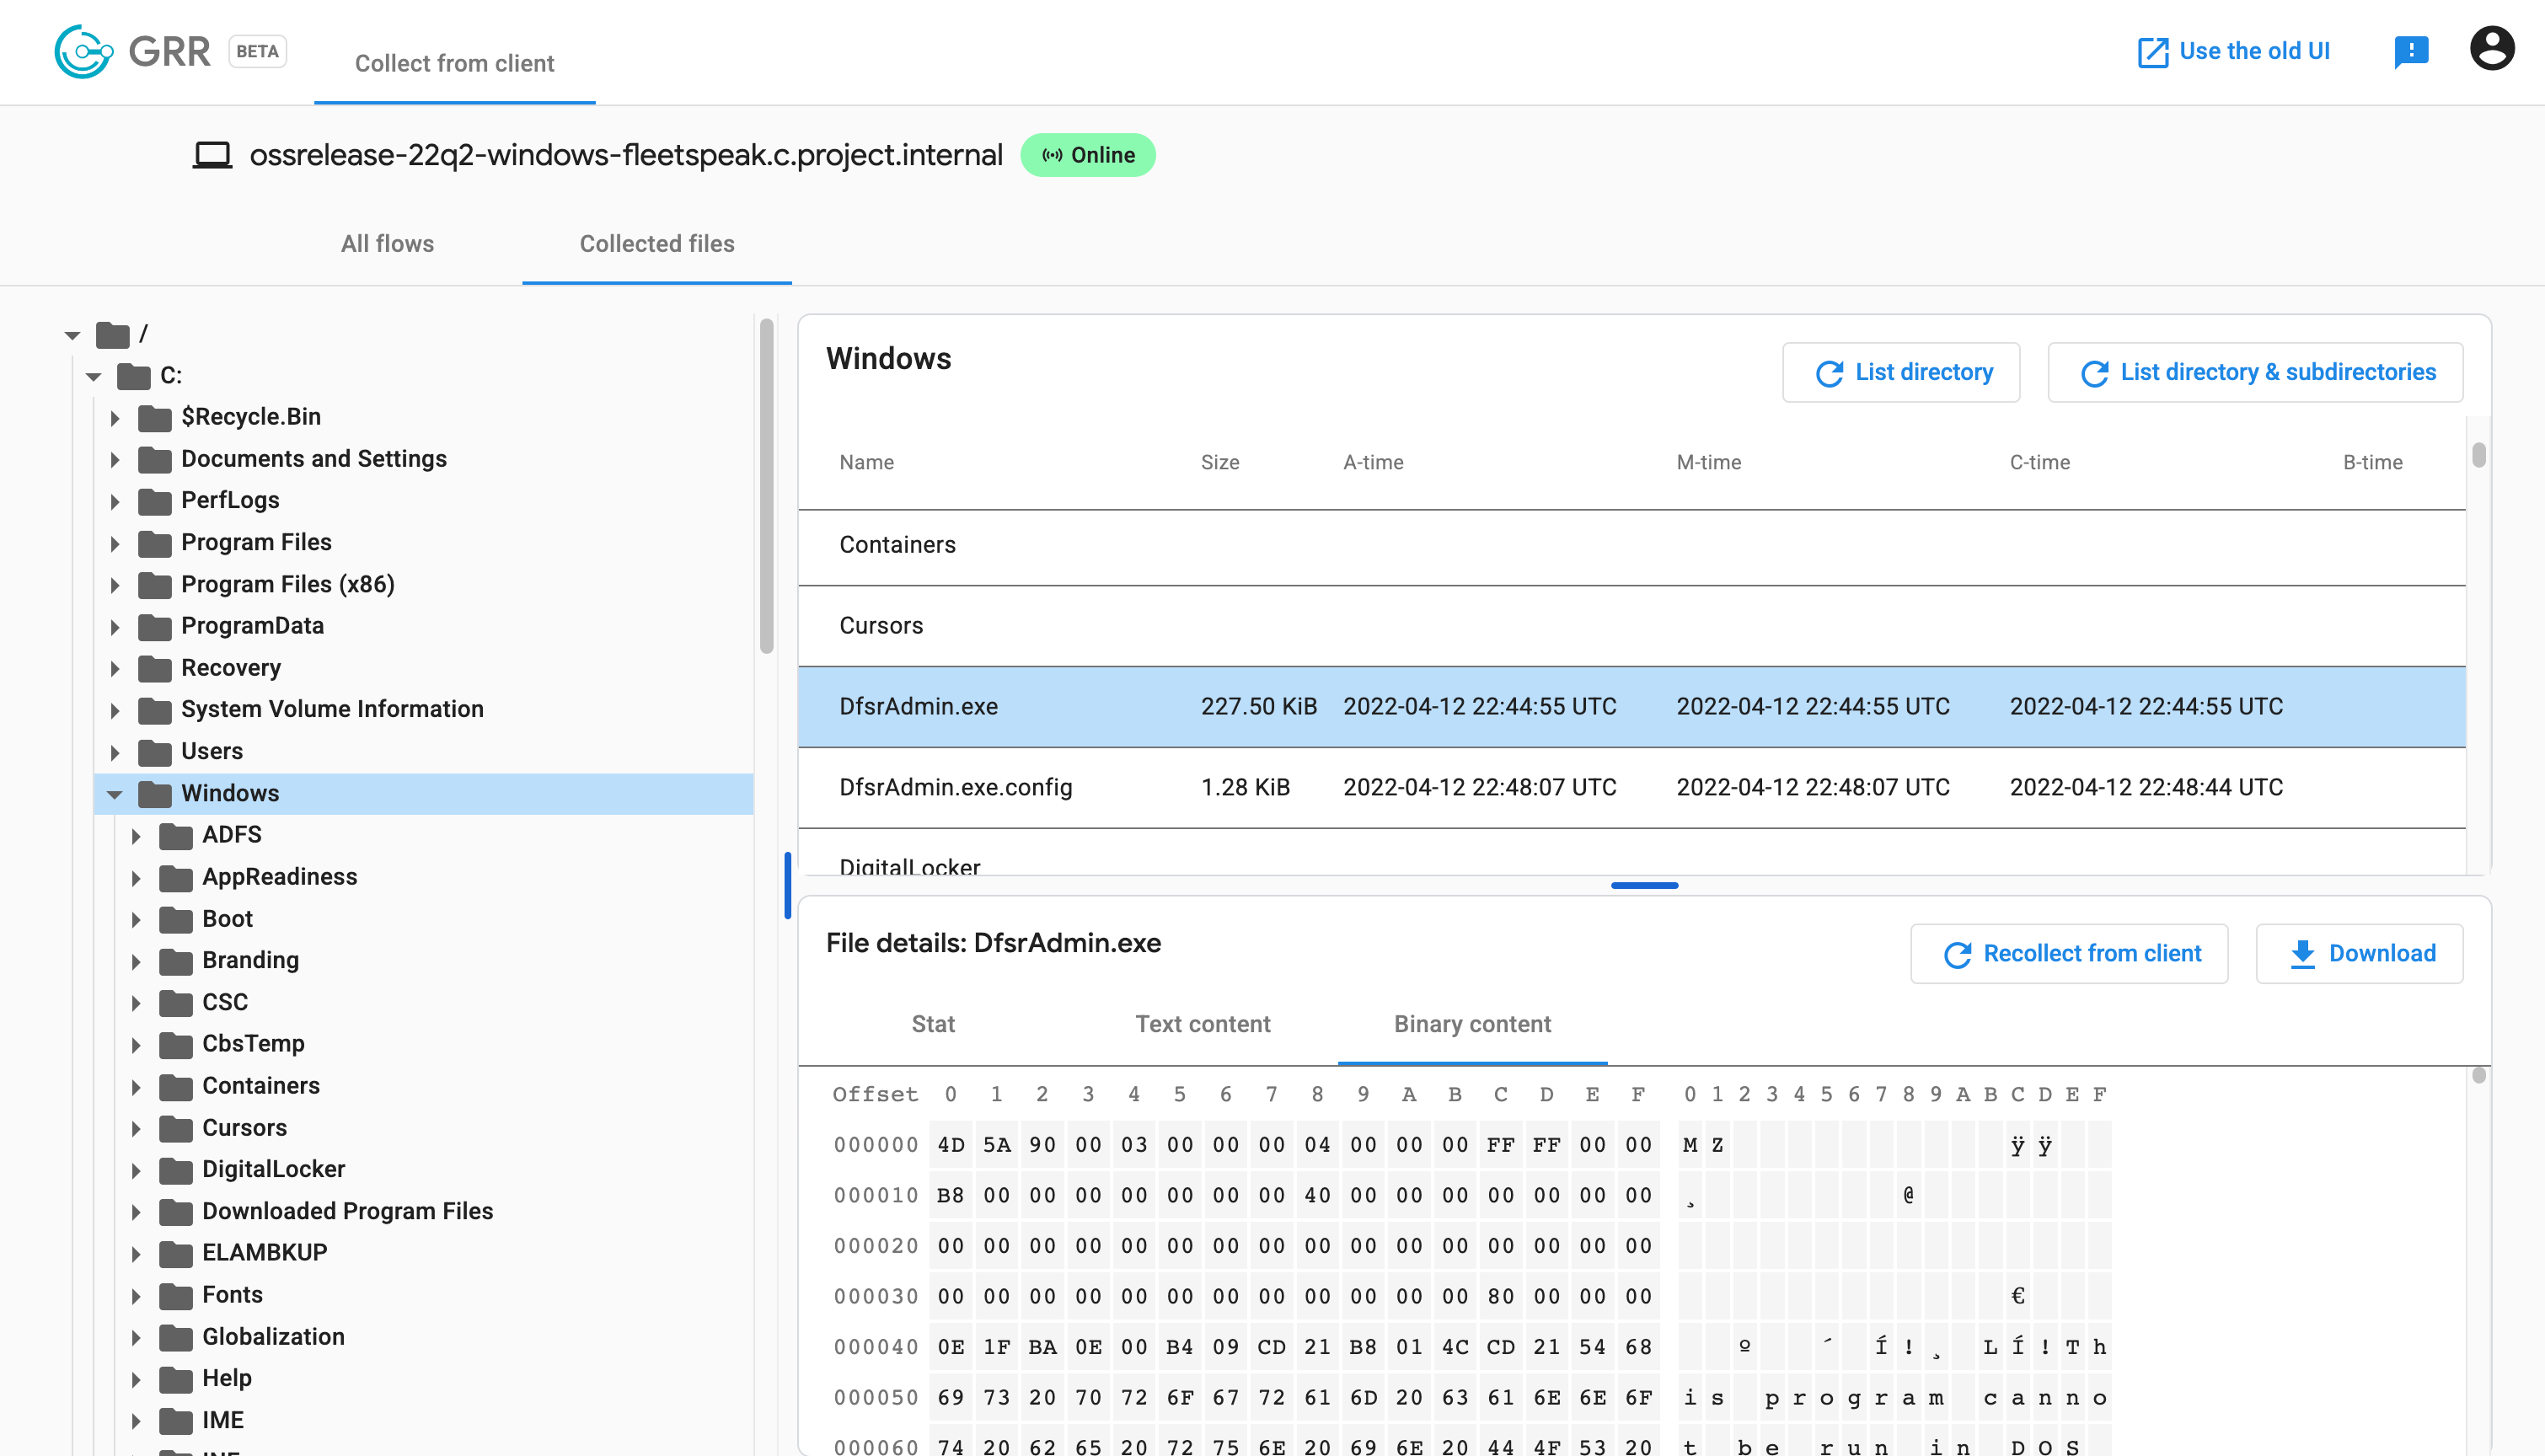
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…

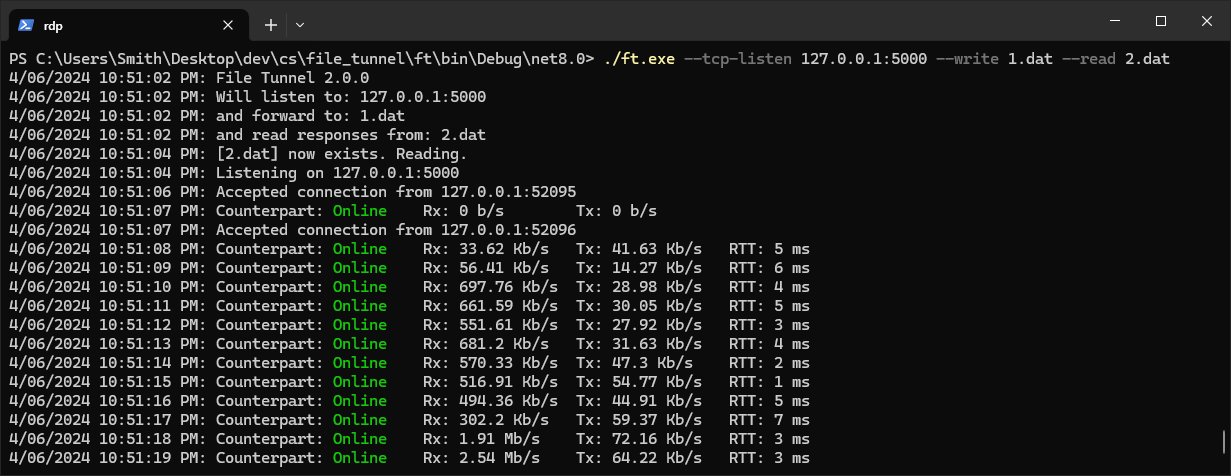
Tunnel TCP connections through a file

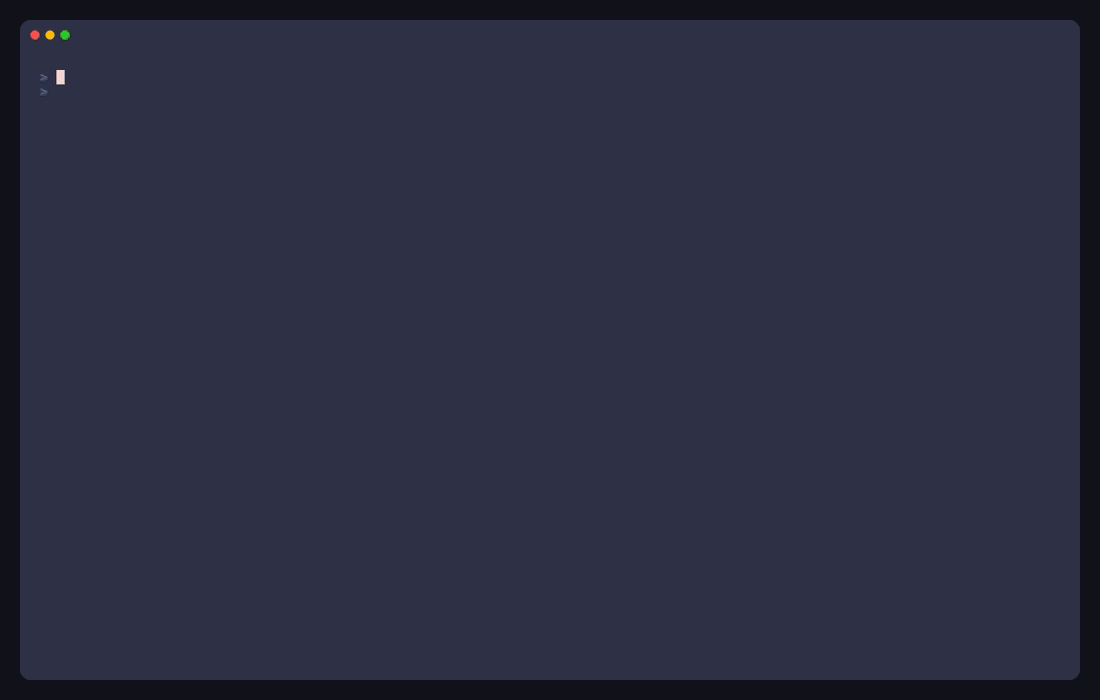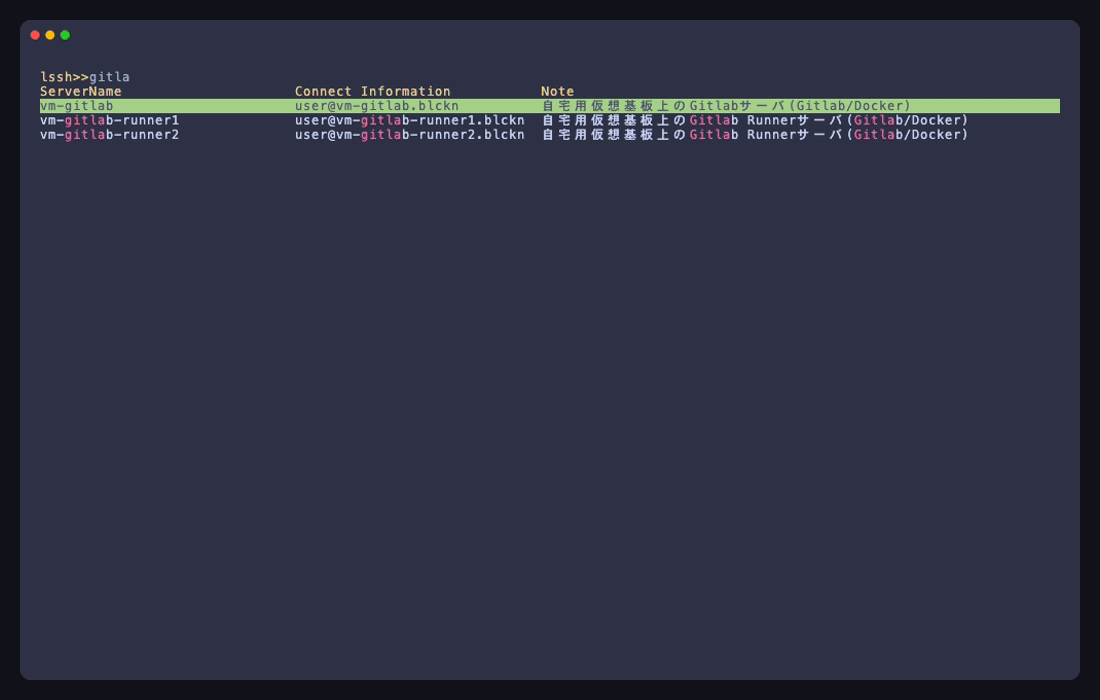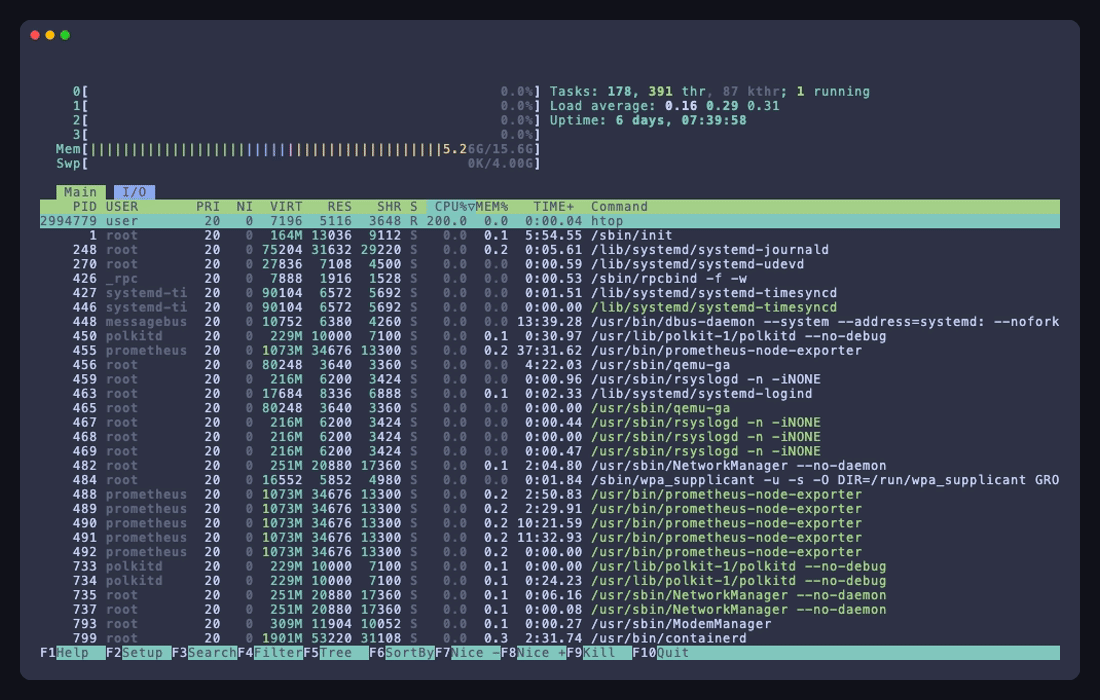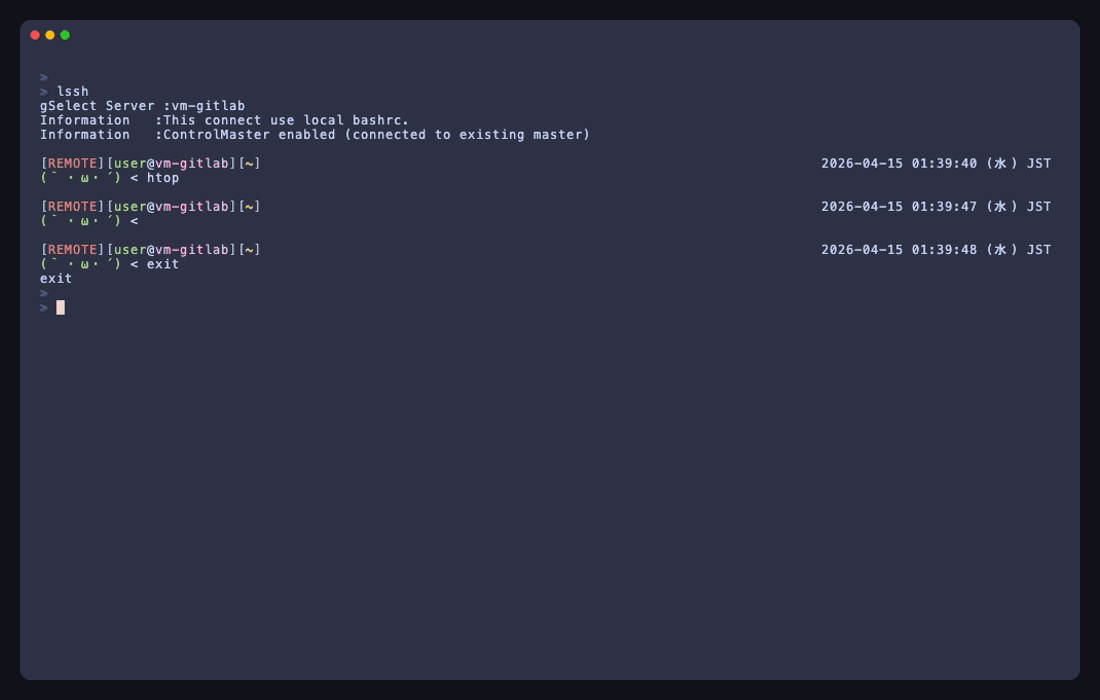
A terminal-native remote access suite for SSH, cloud inventories, provider-backed connectors, parallel commands, mux workspaces, file transfer, and…

Tiny payload for transfer via LOKI - Provides high speed Virtual Channel two way file transfer capabilities

Proof-of-concept exploit for CVE-2026-65400 enabling authenticated file read/write, reverse shells, and persistence on macOS via Apple ScreenSharing.

Proof of concept for CVE-2025-15276 - FontForge SFD File Parsing Deserialization of Untrusted Data Remote Code Execution Vulnerability