
PageBuilderCK-CVE-2026-56290-Exploit
 sagsooz/pagebuilderck-cve-2026-56290-exploit
Page Builder CK for Joomla - Unauthenticated SSRF / Remote File Write leading to PHP execution Exploiter
exploitationpayload-generationpenetration-testing+3
sagsooz/pagebuilderck-cve-2026-56290-exploitPage Builder CK for Joomla - Unauthenticated SSRF / Remote File Write leading to PHP execution Exploiter
 iduzzel/cve-2023-24249-exploit
Exploit script for CVE-2023-24249 - a vulnerability allowing remote code execution via file upload and command injection.
 c411e/cve-2024-53691
CVE-2024-53691
 code-developers/cve-2020-11932
Proof-of-concept exploit for CVE-2020-11932, a double-free vulnerability in WhatsApp GIF processing, enabling remote code execution via crafted .gif…
 pizza-power/golang-webmin-cve-2022-0824-revshell
Exploit POC for CVE-2022-0824
 mrterrestrial/cve-2023-50564
This script exploits the file upload feature in Pluck CMS v4.7.18 to upload a malicious PHP file, enabling remote access via a reverse shell. Once…
 joshuavanderpoll/cve-2026-54806
Proof-of-concept exploit for CVE-2026-54806: unauthenticated PHP object injection in WP Activity Log plugin enabling blind RCE via User-Agent header.…
 rasta-mouse/pwnlift
Easy peasy file uploads
 skelsec/evilrdp
RDP client with extended control for automated mouse, keyboard, and clipboard manipulation, file transfer, SOCKS proxy, and remote command execution…
 joaz94/rejjeto_hfs-rce-exploit-cve-2014-6287
Remote Command Execution exploit for Rejetto HTTP File Server 2.3.x (CVE-2014-6287) rewritten in Python 3 for modern offensive security testing.
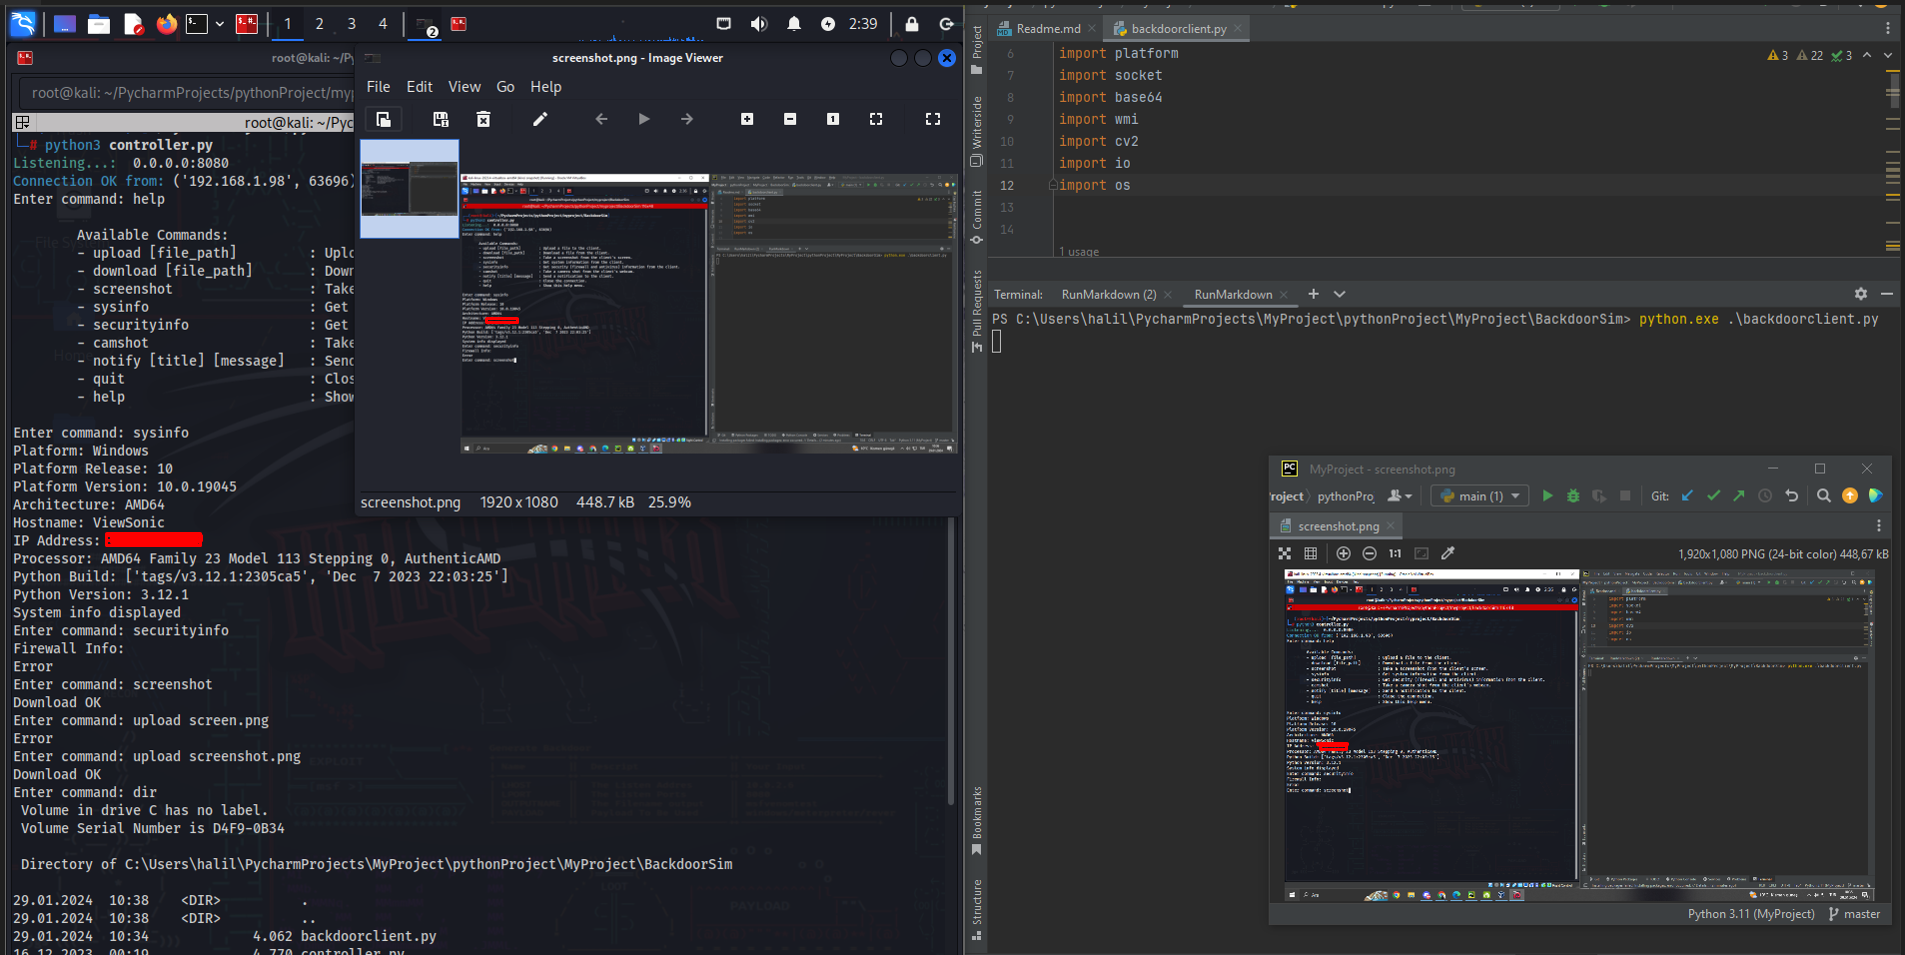 halildeniz/backdoorsim
Educational remote administration tool for learning RAT concepts, featuring file transfer, screenshot capture, system monitoring, and webcam access…
 gokul-ramesh/webminrce-exploit
CVE-2022-0824, CVE-2022-0829, File Manger privilege exploit
 akucybersec/cve-2022-1329-wordpress-elementor-3.6.0-3.6.1-3.6.2-remote-code-execution-exploit
Exploit for CVE-2022-1329, a WordPress Elementor plugin RCE vulnerability, allowing authenticated users to upload and execute arbitrary PHP files via…
 vidura2/cve-2024-46986
Automated Python exploit for Camaleon CMS arbitrary file upload vulnerability (CVE-2024-46986). Supports reverse shell and command execution payloads…
 exopteron/bibliorce
CVE-2023-29478 - BiblioCraft File Manipulation/Remote Code Execution exploit affecting BiblioCraft versions prior to v2.4.6
 v3cn4x00/poc-cve-2025-66034
Automated exploit for CVE-2025-66034, chaining path traversal and XML injection in fontTools varLib to achieve unauthenticated remote code execution…
 dairrow/cve-2025-31161
PoC Authentication Bypass to RCE to Exploit CVE-2025-31161
 0xkayala/cve-2023-33246
Exploits Apache RocketMQ brokers vulnerable to CVE-2023-33246 remote code execution and checks targets via IP, CIDR, or file input.