
cve-2015-1538-1
 oguzhantopgul/cve-2015-1538-1
An exploit for CVE-2015-1538-1 - Google Stagefright ‘stsc’ MP4 Atom Integer Overflow Remote Code Execution
android-securitybinary-exploitationexploitation+4
3
oguzhantopgul/cve-2015-1538-1An exploit for CVE-2015-1538-1 - Google Stagefright ‘stsc’ MP4 Atom Integer Overflow Remote Code Execution
 ireshchaminda1/android-privilege-escalation-remote-access-vulnerability-cve-2015-1805
AndroRAT is a capability that can be used to inject a root exploit as a silent installation to perform a malicious task on the device. This AndroRAT…
 c0d331ng/blackash-cve-2025-48593
CVE-2025-48593
 seqred-s-a/cve-2019-14514
Remote code execution in Microvirt MEmu
 fredevsec/cve-2026-0073
0-Click RCE Android Adb TLS Wireless Debugging
 renjithsasidharan/cve-2015-1538-1
An exploit for CVE-2015-1538-1 - Google Stagefright ‘stsc’ MP4 Atom Integer Overflow Remote Code Execution
 synchancybersecurity/crimson-cloak-ish-wrapper-ios-
Wrapper to maximize ISH iOS app capabilities without jailbreak
 n0c71v3x/cve-2026-78745
Discloses CVE-2026-78745, a remote code execution vulnerability in Android Debug Bridge (ADB) on HiDPT devices, allowing root-level arbitrary code…
 tharana/android-vulnerability-exploitation
Google Android - 'Stagefright' Remote Code Execution - CVE-2015-1538
 xsleaksiki/cve
An exploit for CVE-2015-1538-1 - Google Stagefright ‘stsc’ MP4 Atom Integer Overflow Remote Code Execution
 kalibb/cve-2020-0022
Zero-click Bluetooth RCE exploit for Android 8-9 (CVE-2020-0022) with heap spraying, address leaking, and JOP chain execution for remote code…
 bhathiya404/exploiting-stagefright-vulnerability-cve-2015-3864
Exploit implementation for Android Stagefright vulnerability CVE-2015-3864, enabling remote code execution and privilege escalation on Android 5.1.1…
 ahmyth/ahmyth-android-rat
Android Remote Administration Tool
 mesquidar/adbsploit
A python based tool for exploiting and managing Android devices via ADB
 umarrehmansiddiqui/cve-2026-0073
Proof-of-concept exploit for an Android adbd Wireless Debugging TLS auth bypass, using an EC/RSA key type mismatch to obtain an unauthenticated…
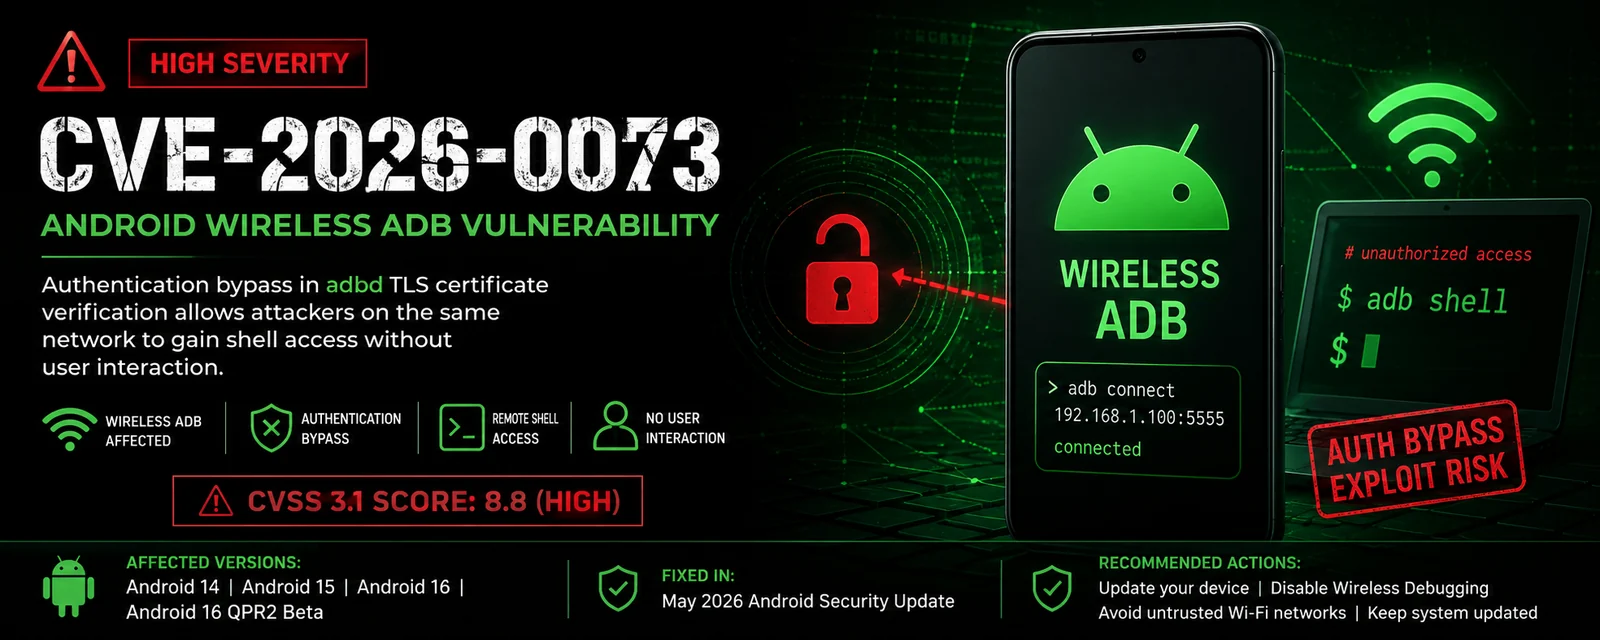 0xredash/cve-2026-0073
C++ proof-of-concept checker and exploit for CVE-2026-0073, an Android Wireless ADB authentication bypass allowing unauthenticated remote shell…