
CVE-2026-49049
 matakucing-ofc/cve-2026-49049
Python scanner and proof-of-concept for CVE-2026-49049, an arbitrary file write in Joomla Helix3 that enables PHP web shell upload and remote code…
exploitationpenetration-testingremote-access-tool+4
matakucing-ofc/cve-2026-49049Python scanner and proof-of-concept for CVE-2026-49049, an arbitrary file write in Joomla Helix3 that enables PHP web shell upload and remote code…
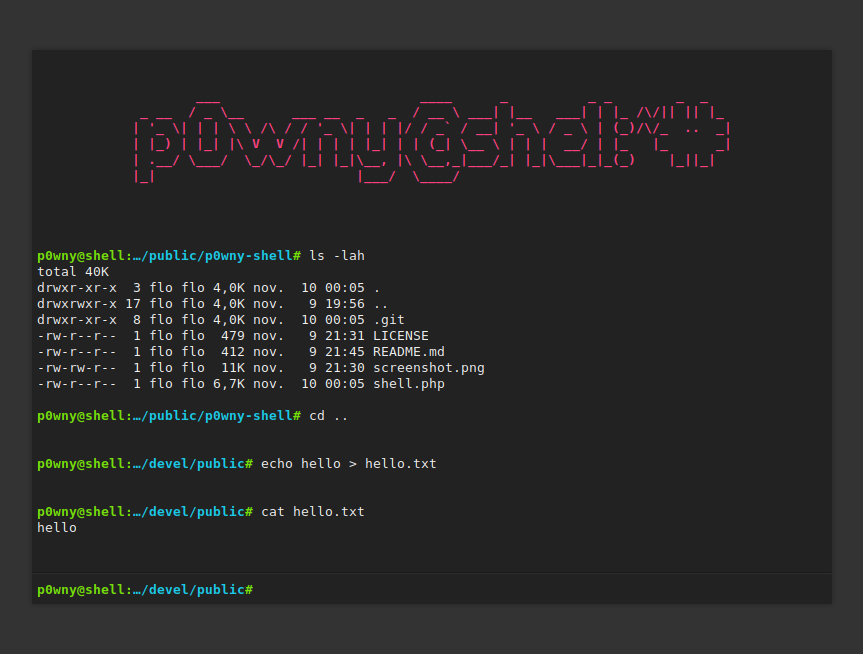 flozz/p0wny-shell
Single-file PHP shell
 0x0d3ad/cve-2020-14008
CVE-2020-14008 - ManageEngine Applications Manager RCE
 mbadanoiu/cve-2022-41678
CVE-2022-41678: Dangerous MBeans Accessible via Jolokia API in Apache ActiveMQ
 lil0xplorer/cve-2025-60787_poc
Authenticated RCE exploit for MotionEye <= 0.43.1b4 via client-side validation bypass on the image_file_name field. Includes reverse shell payload…
 nxploited/cve-2024-12252
SEO LAT Auto Post <= 2.2.1 - Missing Authorization to File Overwrite/Upload (Remote Code Execution)
 horizon3ai/cve-2025-64155
CVE-2025-64155: Fortinet FortiSIEM Argument Injection to Remote Code Execution
 bly-coder/python-exploit-cve-2020-25213
Python exploit for RCE in Wordpress
 husenjandev/cve-2023-422-chamilo-lms-rce
Remote Code Execution for Chamilo LMS
 joelgmsec/psasyncshell
Asynchronous TCP reverse shell in pure PowerShell that bypasses firewalls via non-blocking I/O, with command history, file upload/download, and…
 ajdumanhug/cve-2024-21546
This Python exploit script targets a vulnerable Laravel Filemanager created by UniSharp, which allows authenticated users to bypass file restrictions…
 gagaltotal/n8n-cve-2025-68613
Authenticated RCE exploit PoC and vulnerability scanner for CVE-2025-68613 in n8n. Supports command execution, file operations, and reverse shell…
 ktn1990/cve-2024-5084
WordPress Hash Form – Drag & Drop Form Builder <= 1.1.0 - Unauthenticated Arbitrary File Upload to Remote Code Execution
 nccgroup/loki
LOKI (Limited Obstructive Keyboard Impersonator) is a RDP File Transfer Tool Using Keypresses
 h4rk3nz0/cve-2024-3912
Asus Router Arbitrary File Write to Remote Code Execution PoC - Fk Mirai
 raeezrbr/cve-2024-5084
Exploit for CVE-2024-5084: unauthenticated arbitrary file upload in Hash Form WordPress plugin, enabling remote code execution via Python script with…
 hunthubspace/cve-2024-0757-exploit
A PoC Exploit for CVE-2024-0757 - Insert or Embed Articulate Content into WordPress Remote Code Execution (RCE)
 orangmuda/cve-2020-0796
Remote Code Execution POC for CVE-2020-0796