
CVE-2021-44228-Apache-Log4j
 lonecloud/cve-2021-44228-apache-log4j
CVE-2021-44228-Apache-Log4j
command-and-controlexploitationpayload-generation+3
lonecloud/cve-2021-44228-apache-log4jCVE-2021-44228-Apache-Log4j
 mbadanoiu/cve-2020-8254
CVE-2020-8254: Zip Slip in Pulse Secure VPN Windows Client
 lychi3/vsftpd-backdoor
Exploit hecho en python para vsftpd 2.3.4 | CVE-2011-2523
 pol-ruiz/poc-cve-2019-12840
Esto es una prueba de concepto propia i basica de la vulneravilidad CVE-2019-12840 la qual te da un RCE en root
 lolameroo/codiad-cve-2018-14009
Codiad through 2.8.4 allows Remote Code Execution, a different vulnerability than CVE-2017-11366 and CVE-2017-15689
 any3ite/cve-2023-38646-metabase-reverseshell
Go-based exploit for CVE-2023-38646 in Metabase, enabling remote code execution and reverse shell connection to an attacker-controlled host.
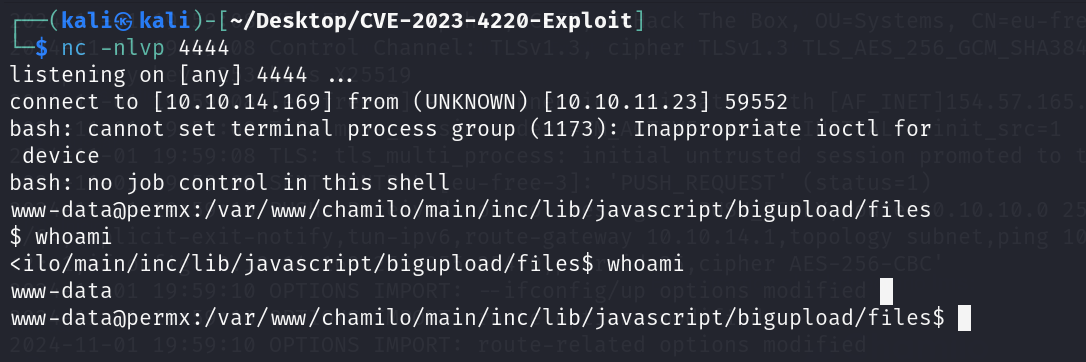 h4cking4all/cve-2023-4220
CVE-2023-4220 Chamilo Exploit
 arunhatter/cve-2022-31814
This script is a proof-of-concept exploit for pfBlockerNG <= 2.1.4_26 that allows for remote code execution. It takes a single target URL or a list…
 tenor-z/smileysploit
A basic script that exploits CVE-2011-2523
 arenaldyp/cve-2024-38063-medium
Kode Eksploitasi CVE-2024-38063
 dbgee/cve-2021-44228
Apache Log4j 2 a remote code execution vulnerability via the ldap JNDI parser.
 elphon/cve-2007-2447-exploit
Python exploit for Samba smbd 3.0.20 (CVE-2007-2447) enabling remote command execution and reverse shell via crafted SMB requests.
 h3x0v3rl0rd/freepbx-reverse-shell-module
Exploit module for FreePBX delivering a reverse shell payload to achieve remote command execution and persistent shell access, designed for…
 swammers8/wbce-v1.6.3-authenticated-rce
Authenticated RCE exploit for WBCE CMS <= 1.6.3 that creates a malicious module zip with a PHP reverse shell and netcat listener.
 herculesrd/vsftpd2.3.4pyexploit
An exploit to get root in vsftpd 2.3.4 (CVE-2011-2523) written in python
 sug4r-wr41th/cve-2011-2523
vsFTPd 2.3.4 CVE-2011-2523 PoC
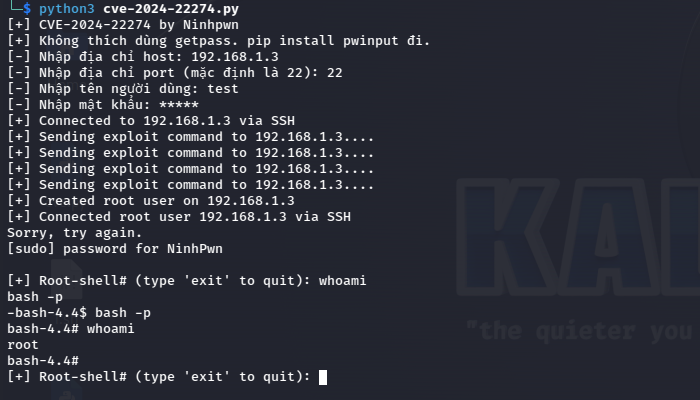 ninhpn1337/cve-2024-22274
Exploit for CVE-2024-22274 that creates a privileged user and spawns a root SSH shell on a target host using provided credentials.
 raeezrbr/cve-2024-5084
Exploit for CVE-2024-5084: unauthenticated arbitrary file upload in Hash Form WordPress plugin, enabling remote code execution via Python script with…