

CVE-2022-24637
 0xryuk/cve-2022-24637
Open Web Analytics 1.7.3 - Remote Code Execution Exploit v2
exploitationpayload-generationremote-access-tool+2
1
0xryuk/cve-2022-24637Open Web Analytics 1.7.3 - Remote Code Execution Exploit v2
 adibna/cve-2021-31630
This is a automation of cve-2021-31630 exploitation
 tamirido30/cve-2024-10914-exploit
CVE-2024-10914 Shell Exploit
 nickguitar/yaps
Yet Another PHP Shell - The most complete PHP reverse shell
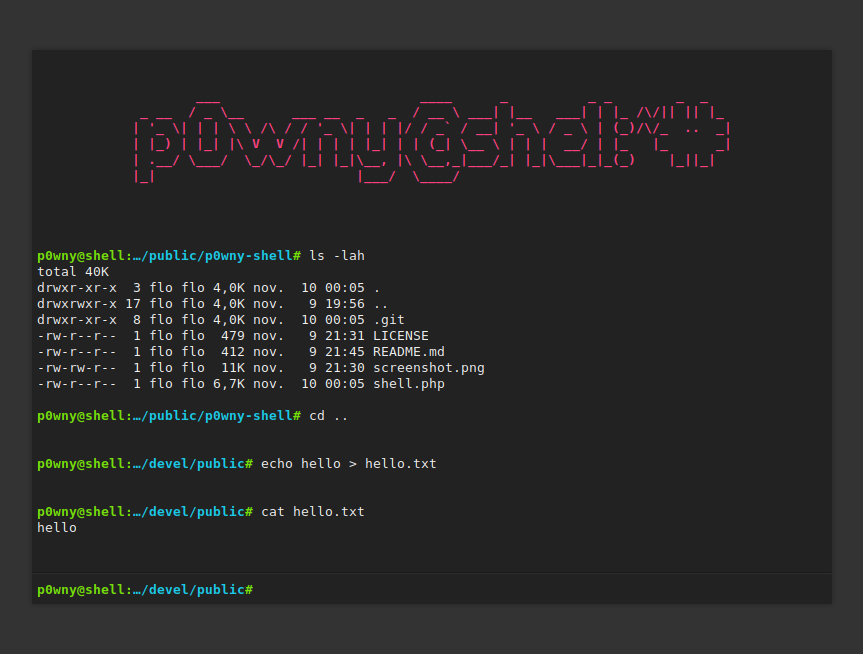 flozz/p0wny-shell
Single-file PHP shell
 emrekybs/nim-shell
Reverse shell that can bypass windows defender detection
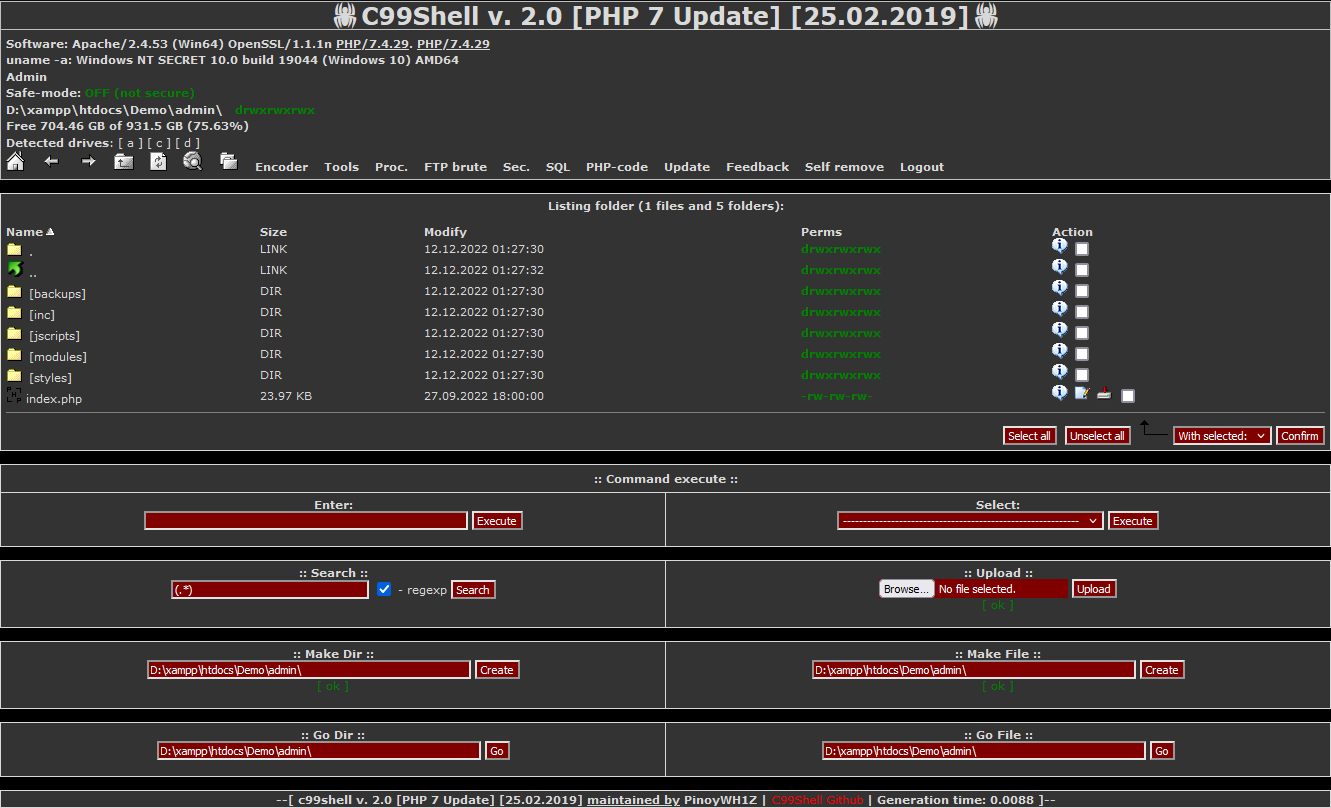 pinoywh1z/c99shell-php7
PHP 7 and safe-build Update of the popular C99 variant of PHP Shell.
 win3zz/cve-2017-5638
Apache Struts 2.3.5 < 2.3.31 / 2.5 < 2.5.10 - Remote Code Execution - Shell Script
 zyphorixofficialmain-lab/cve-2026-87902
Python exploit for CVE-2026-87902, a WordPress Core LFI-to-RCE chain. Fingerprints versions, writes a PHP shell via pearcmd, and provides command…
 zux0x3a/tinyshell
Small PHP shell, Controlled by Python Client , connecting over protocol method
 theendofabbys/cve-2026-48908
Python PoC for CVE-2026-48908: unauthenticated ZIP upload in Joomla SP Page Builder (com_sppagebuilder) leading to remote code execution via a PHP…
 murrez/cve-2026-94132
Python check/exploit PoC for CVE-2026-94132: detects AcyMailing for Joomla versions, probes the media/com_acym/upload directory, and verifies…
 jrbh4ck/cve-2022-22963
Proof-of-concept exploit for CVE-2022-22963, a Spring Cloud Function SpEL injection leading to remote code execution. Includes a shell script for…
 lukechilds/reverse-shell
On-demand reverse shell service that auto-detects target environment and executes appropriate payload for remote access during penetration tests.

 s_r_e_e_r_a_j/php-reverse-shell
This is a powerful and stealthy PHP reverse shell designed for ethical hacking and penetration testing. It establishes a reliable and quiet…
 prodigiousmind/revshell
Pentestmonkeys' PHP reverse shell with dynamic host and port passing through GET request parameters
 nickswink/cve-2023-38646
CVE-2023-38646 Unauthenticated RCE vulnerability in Metabase
 arianeblow/nagiosxi-rce-all-version-cve-2021-40345
RFI to RCE Nagios/NagiosXI exploitation