
CVE-2026-4631-cockpit-RCE
 exdev994/cve-2026-4631-cockpit-rce
Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection Cockpit versions 327 – 359 | CVSS 9.8 Critical | CWE-78
command-and-controlexploitationinformation-gathering+6
exdev994/cve-2026-4631-cockpit-rceUnauthenticated Remote Code Execution via SSH Command-Line Argument Injection Cockpit versions 327 – 359 | CVSS 9.8 Critical | CWE-78
 l-urk/cve-2024-6387
Proof of concept python script for regreSSHion exploit.
 teamos-hub/regresshion
This is a POC I wrote for CVE-2024-6387
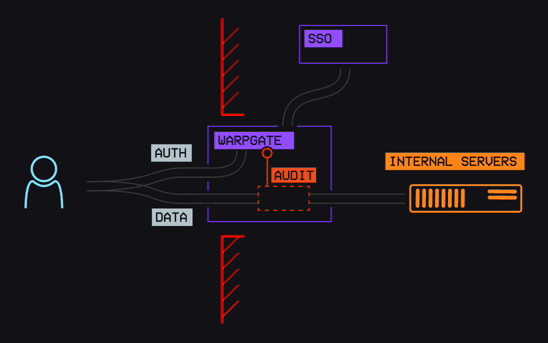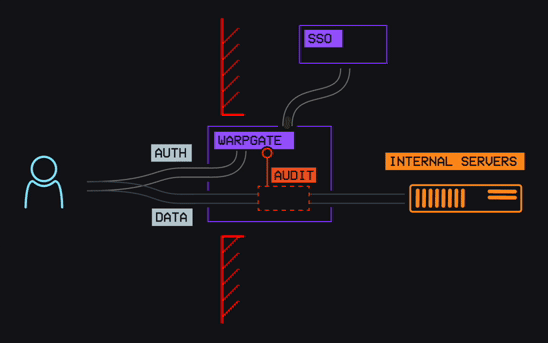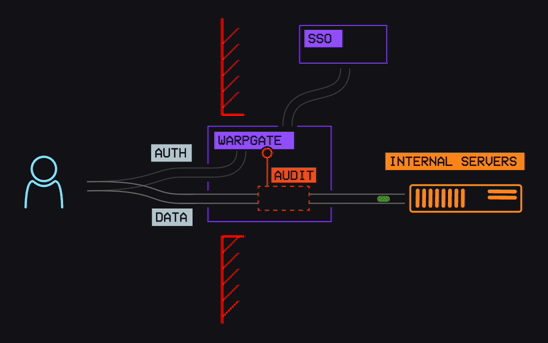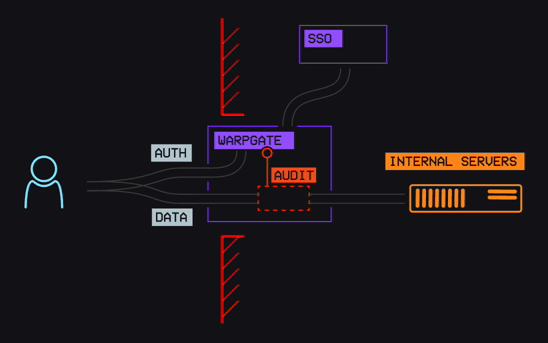 warp-tech/warpgate
Fully transparent SSH, HTTPS, Kubernetes, database and RDP/VNC bastion/PAM that doesn't need additional client-side software
 bastillion-io/bastillion
Bastillion gives you a clean, browser-based way to manage SSH access across all your systems—like a bastion host with a friendly dashboard.
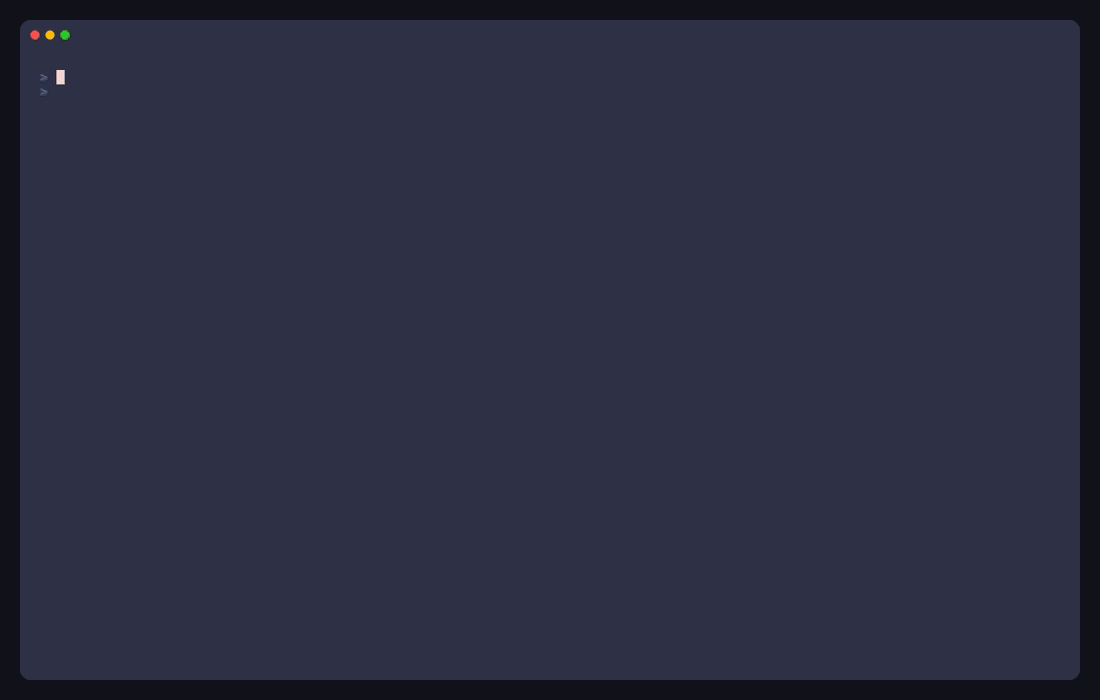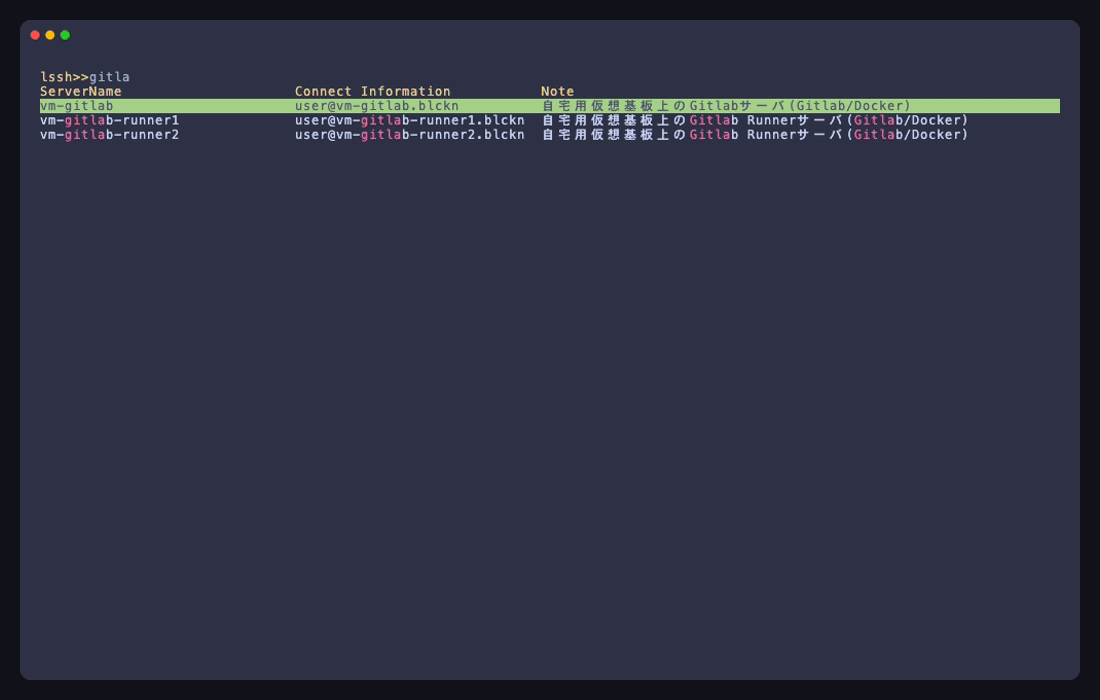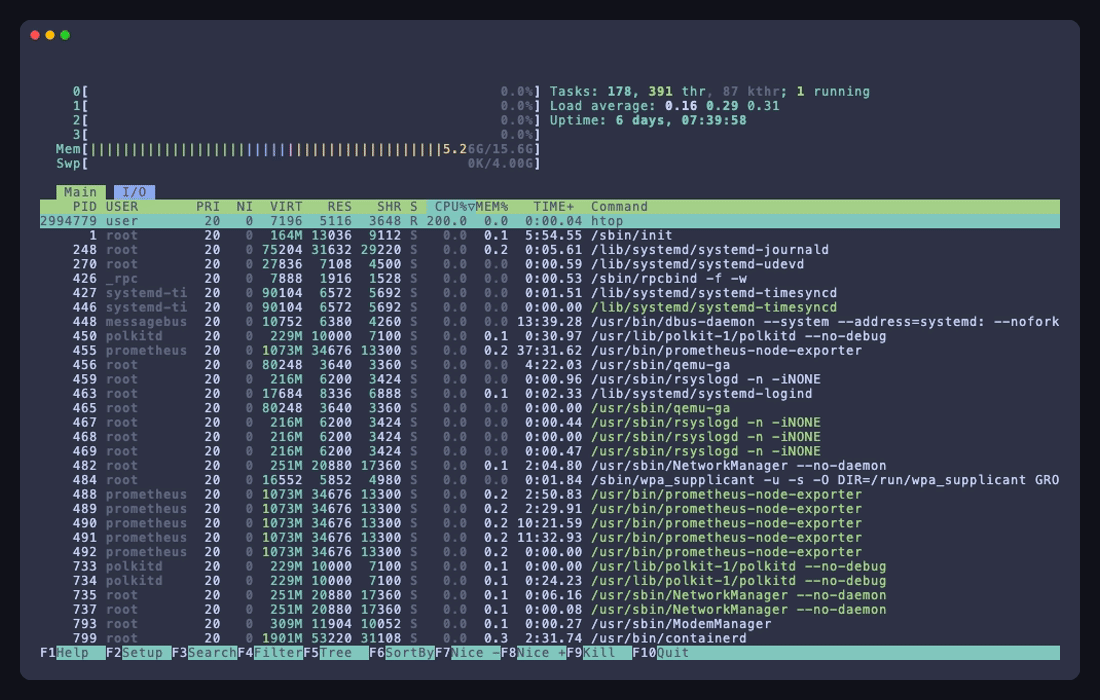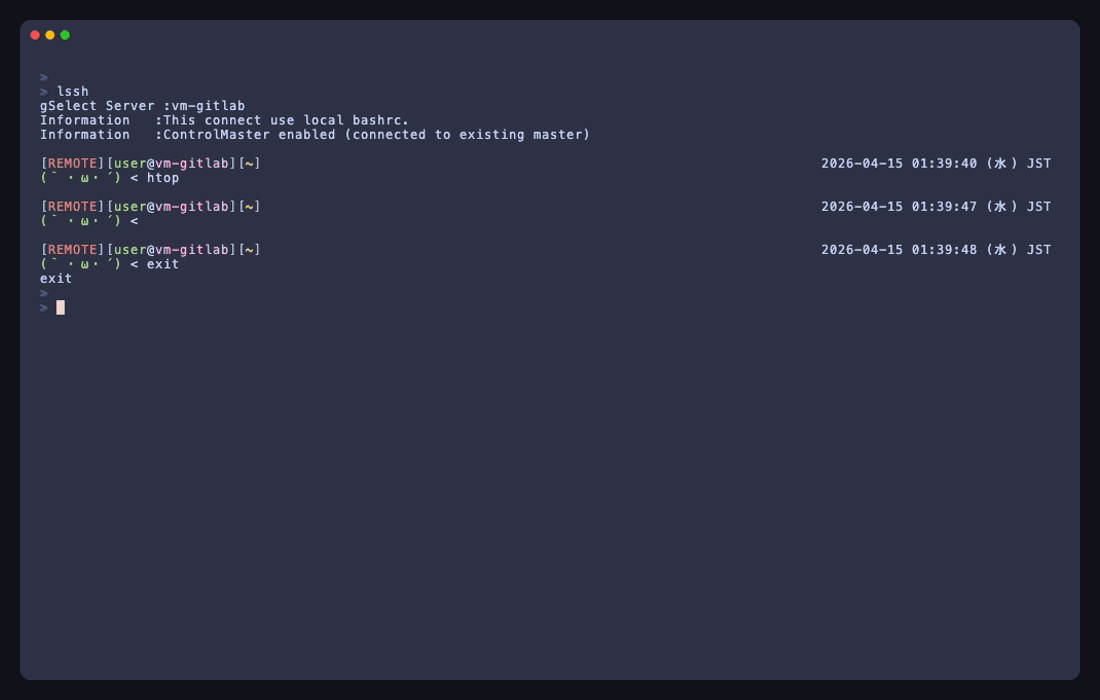 blacknon/lssh
A terminal-native remote access suite for SSH, cloud inventories, provider-backed connectors, parallel commands, mux workspaces, file transfer, and…
 daradib/sidedoor
SSH connection daemon for Debian/Raspbian/Ubuntu/etc
 jumpserver/jumpserver
JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH,…
 apple/swift-nio-ssh
SwiftNIO SSH is a programmatic implementation of SSH using SwiftNIO
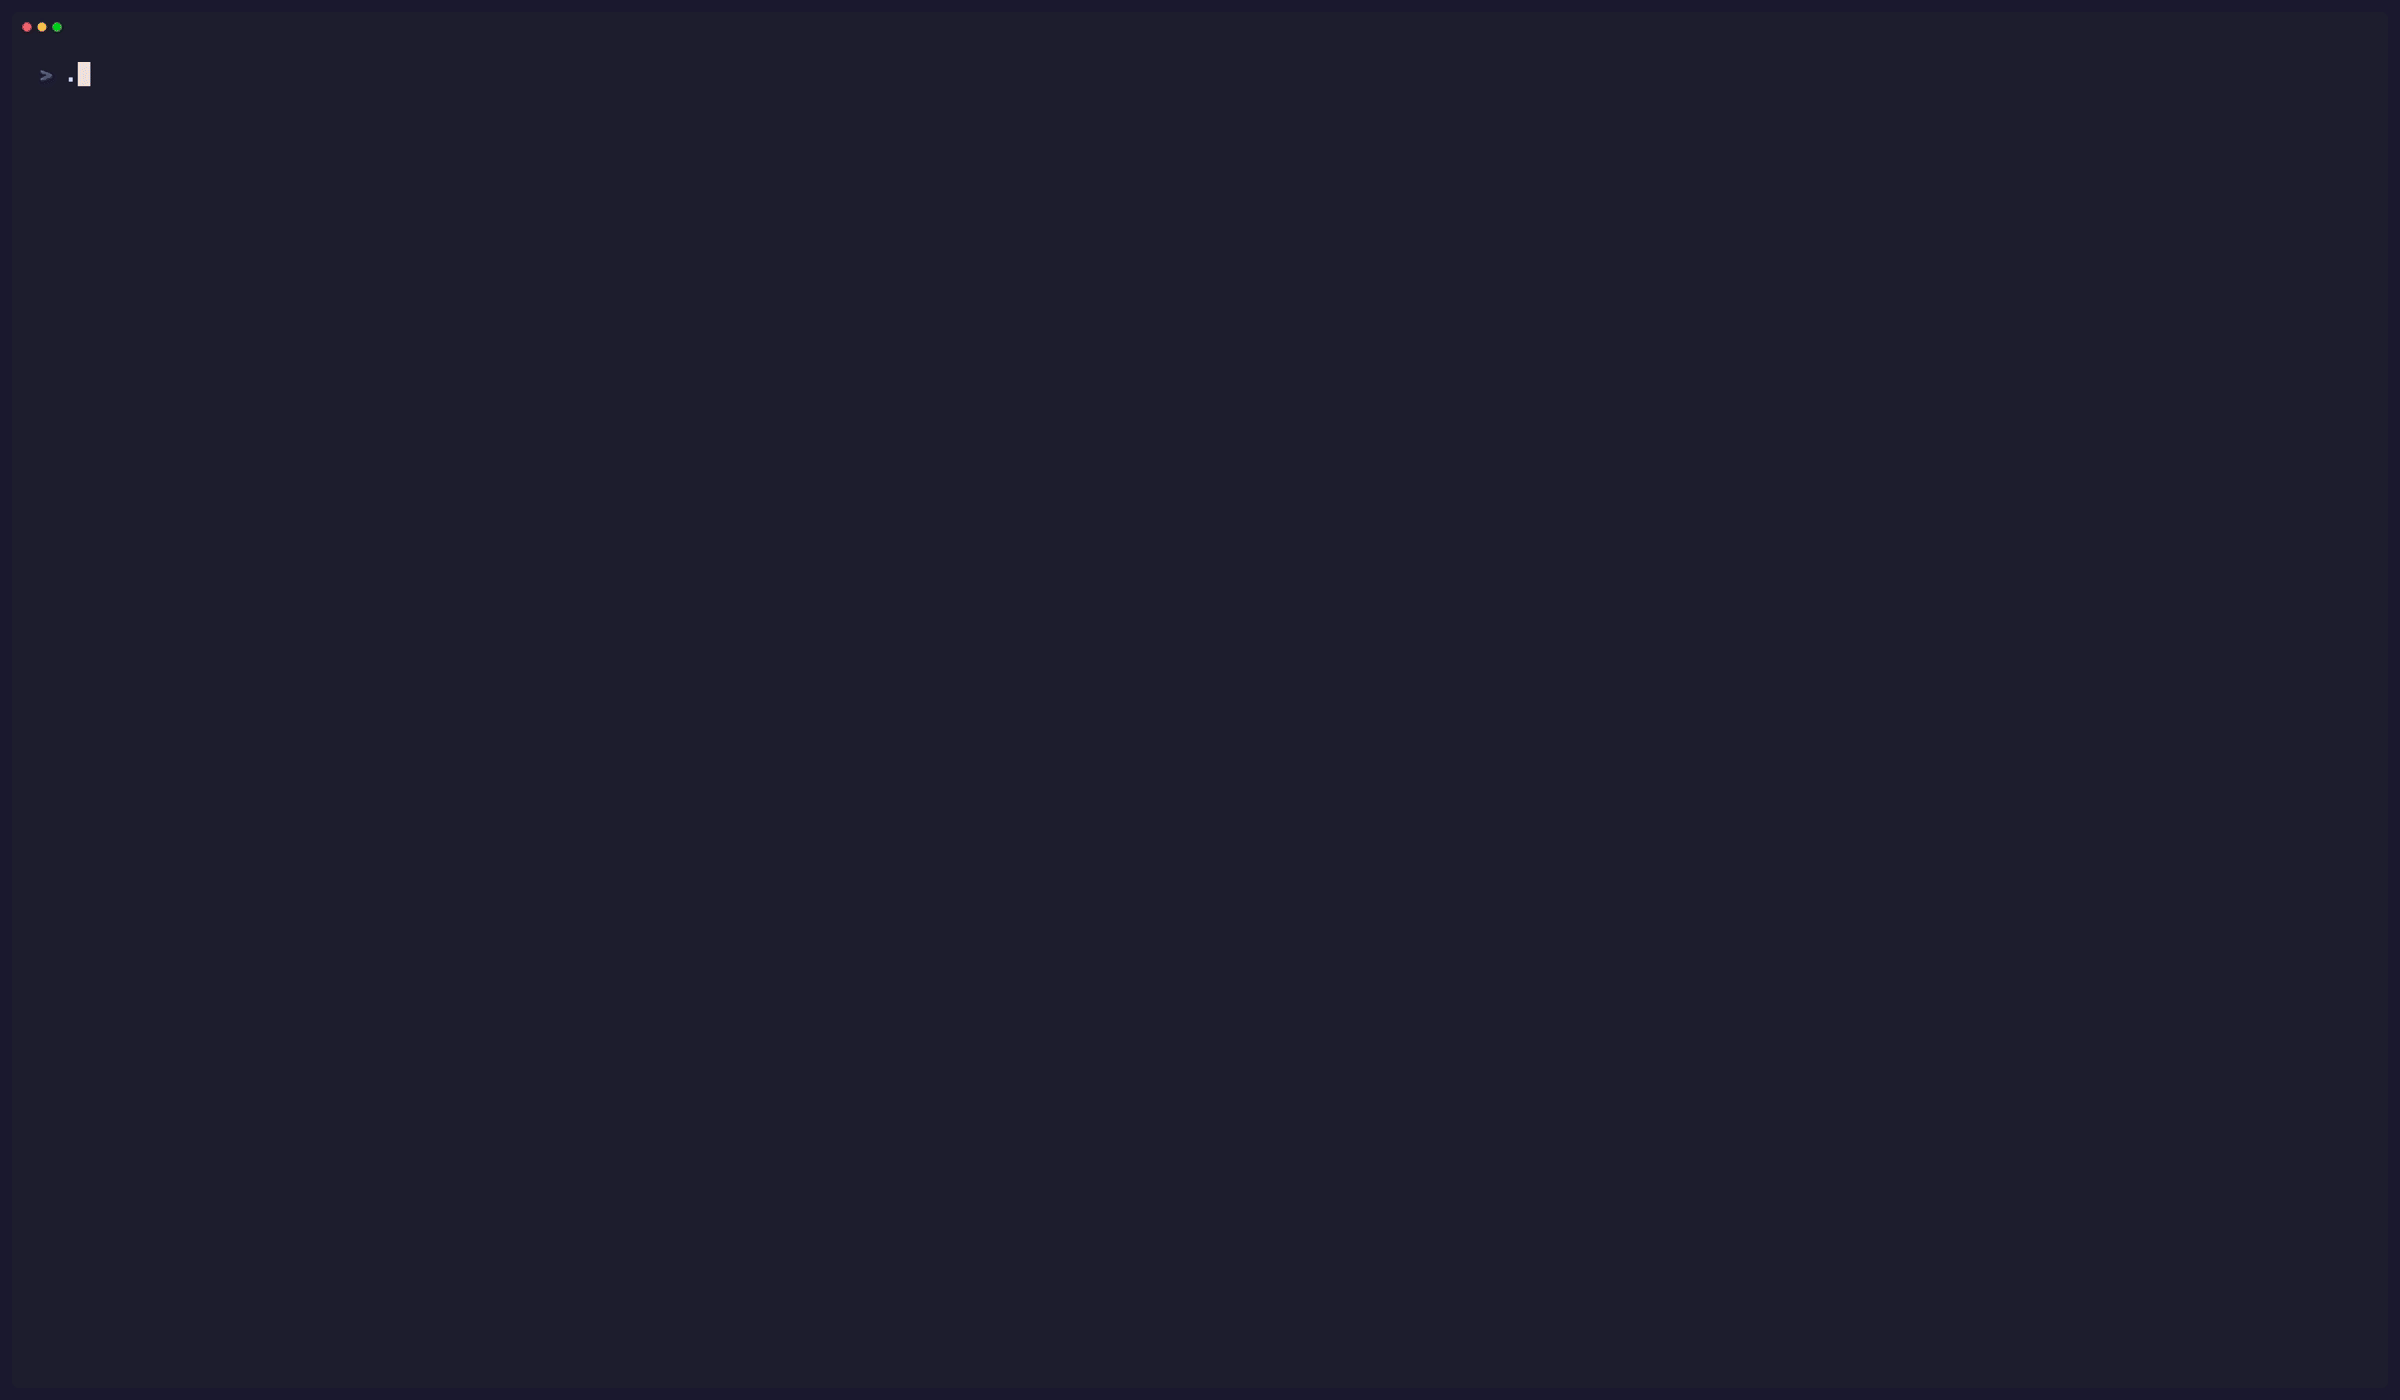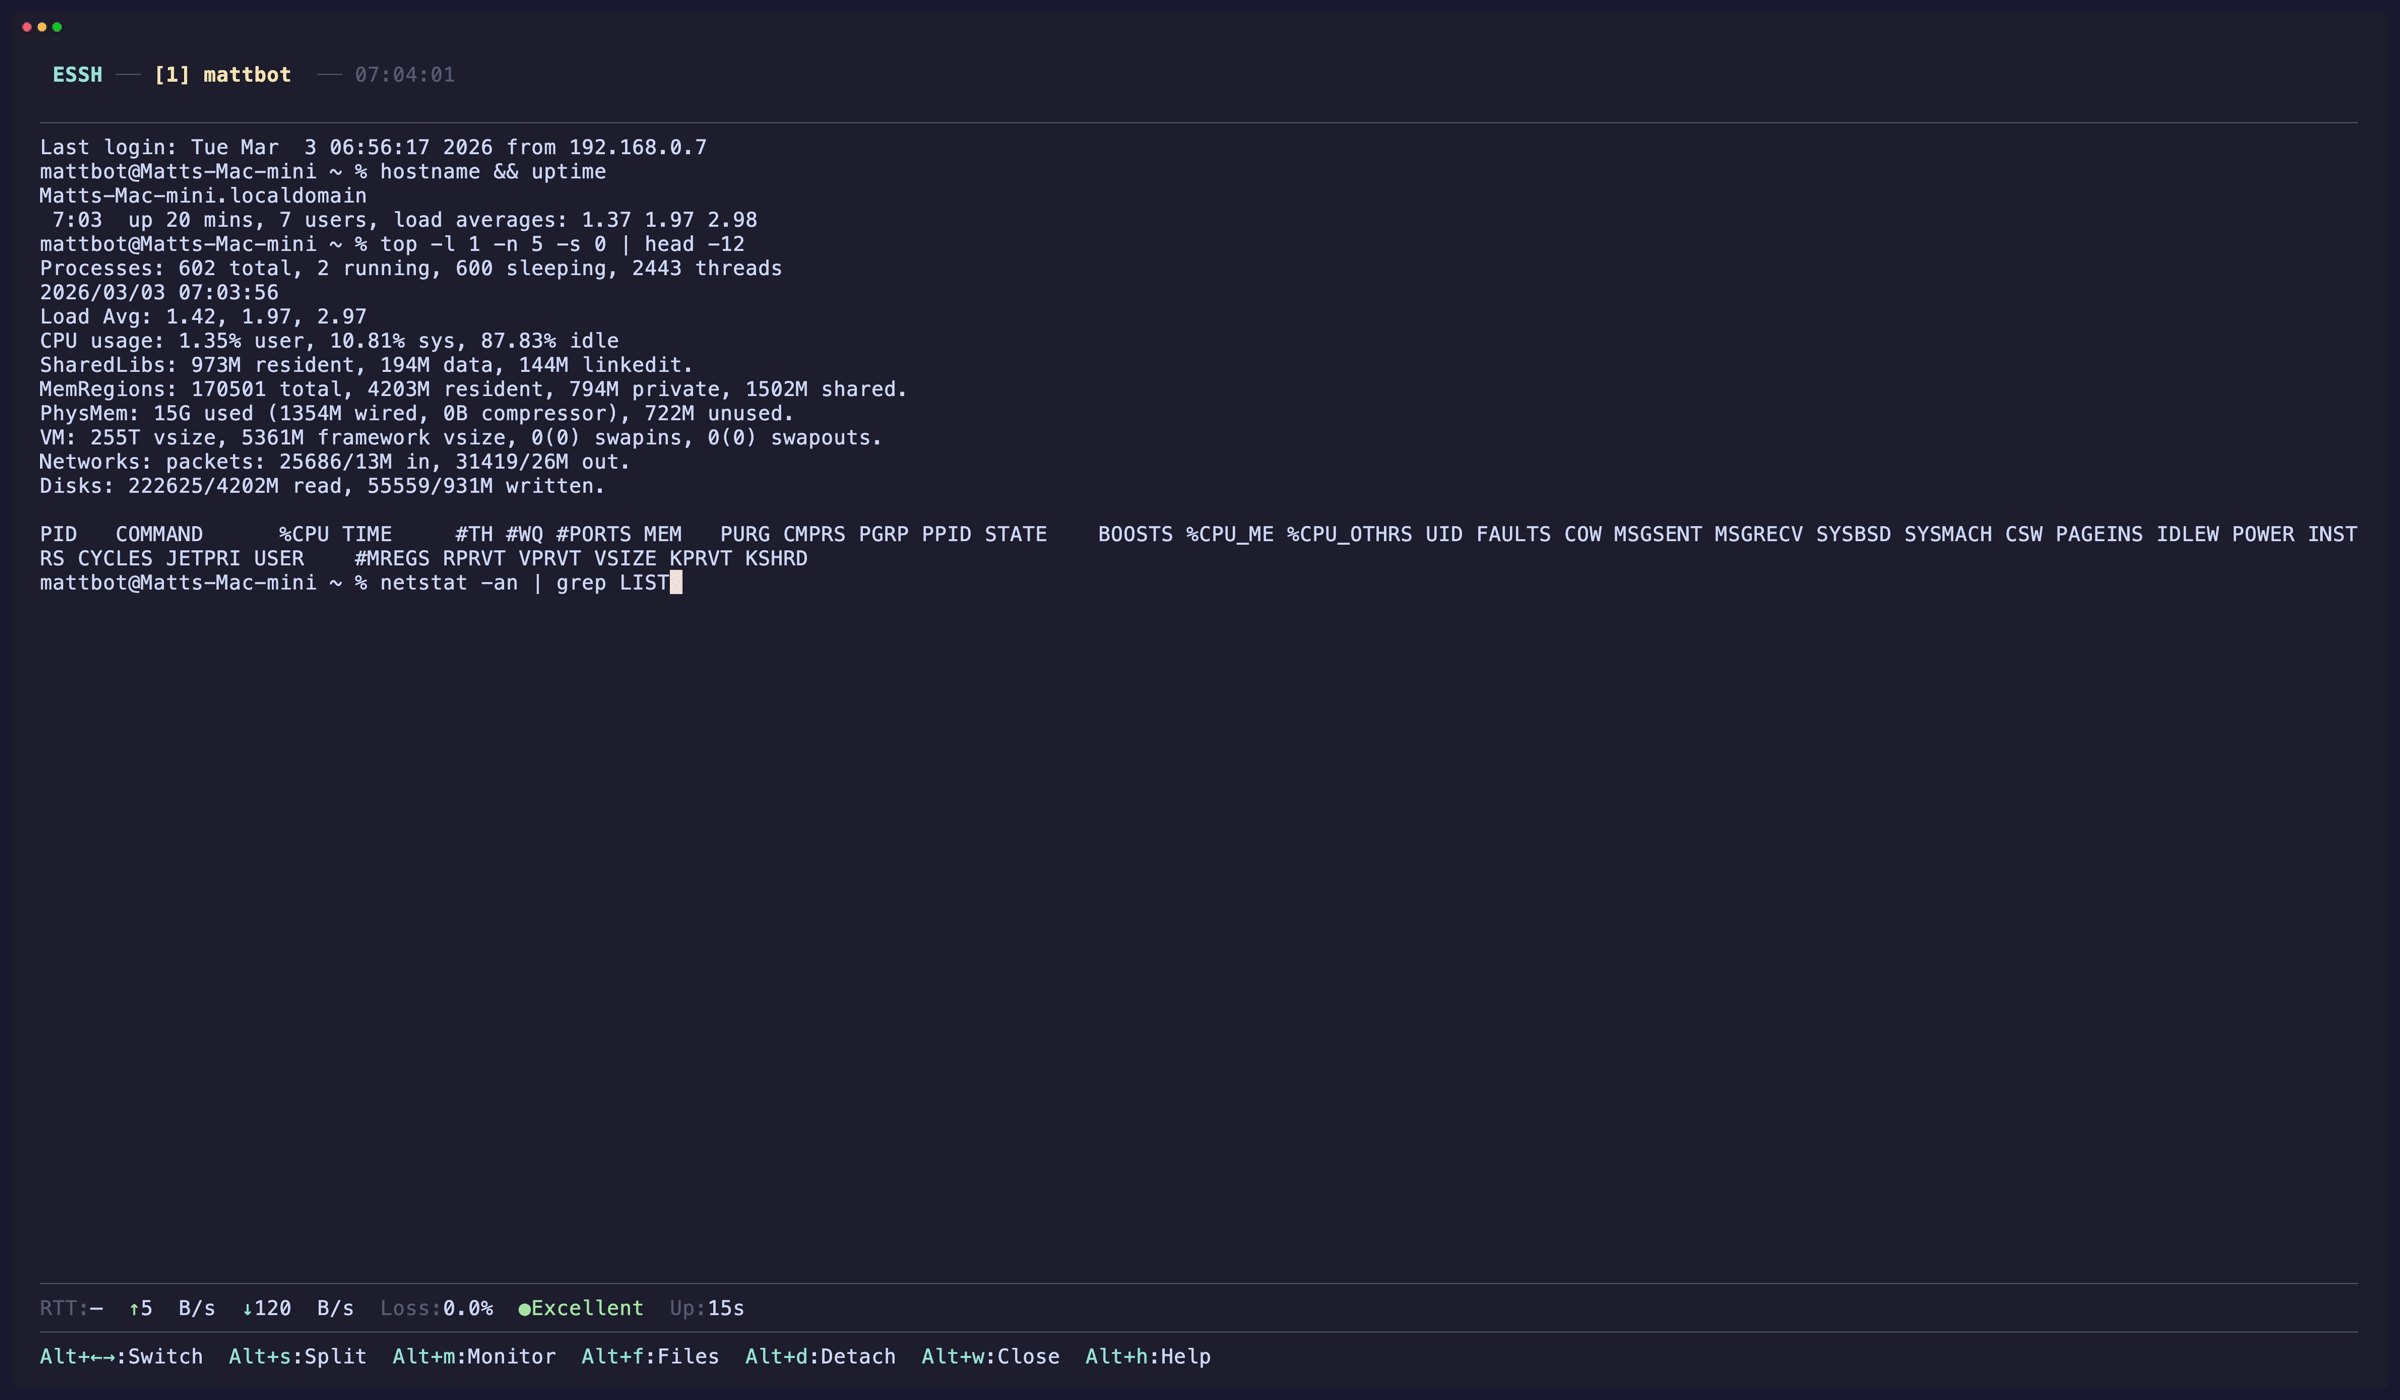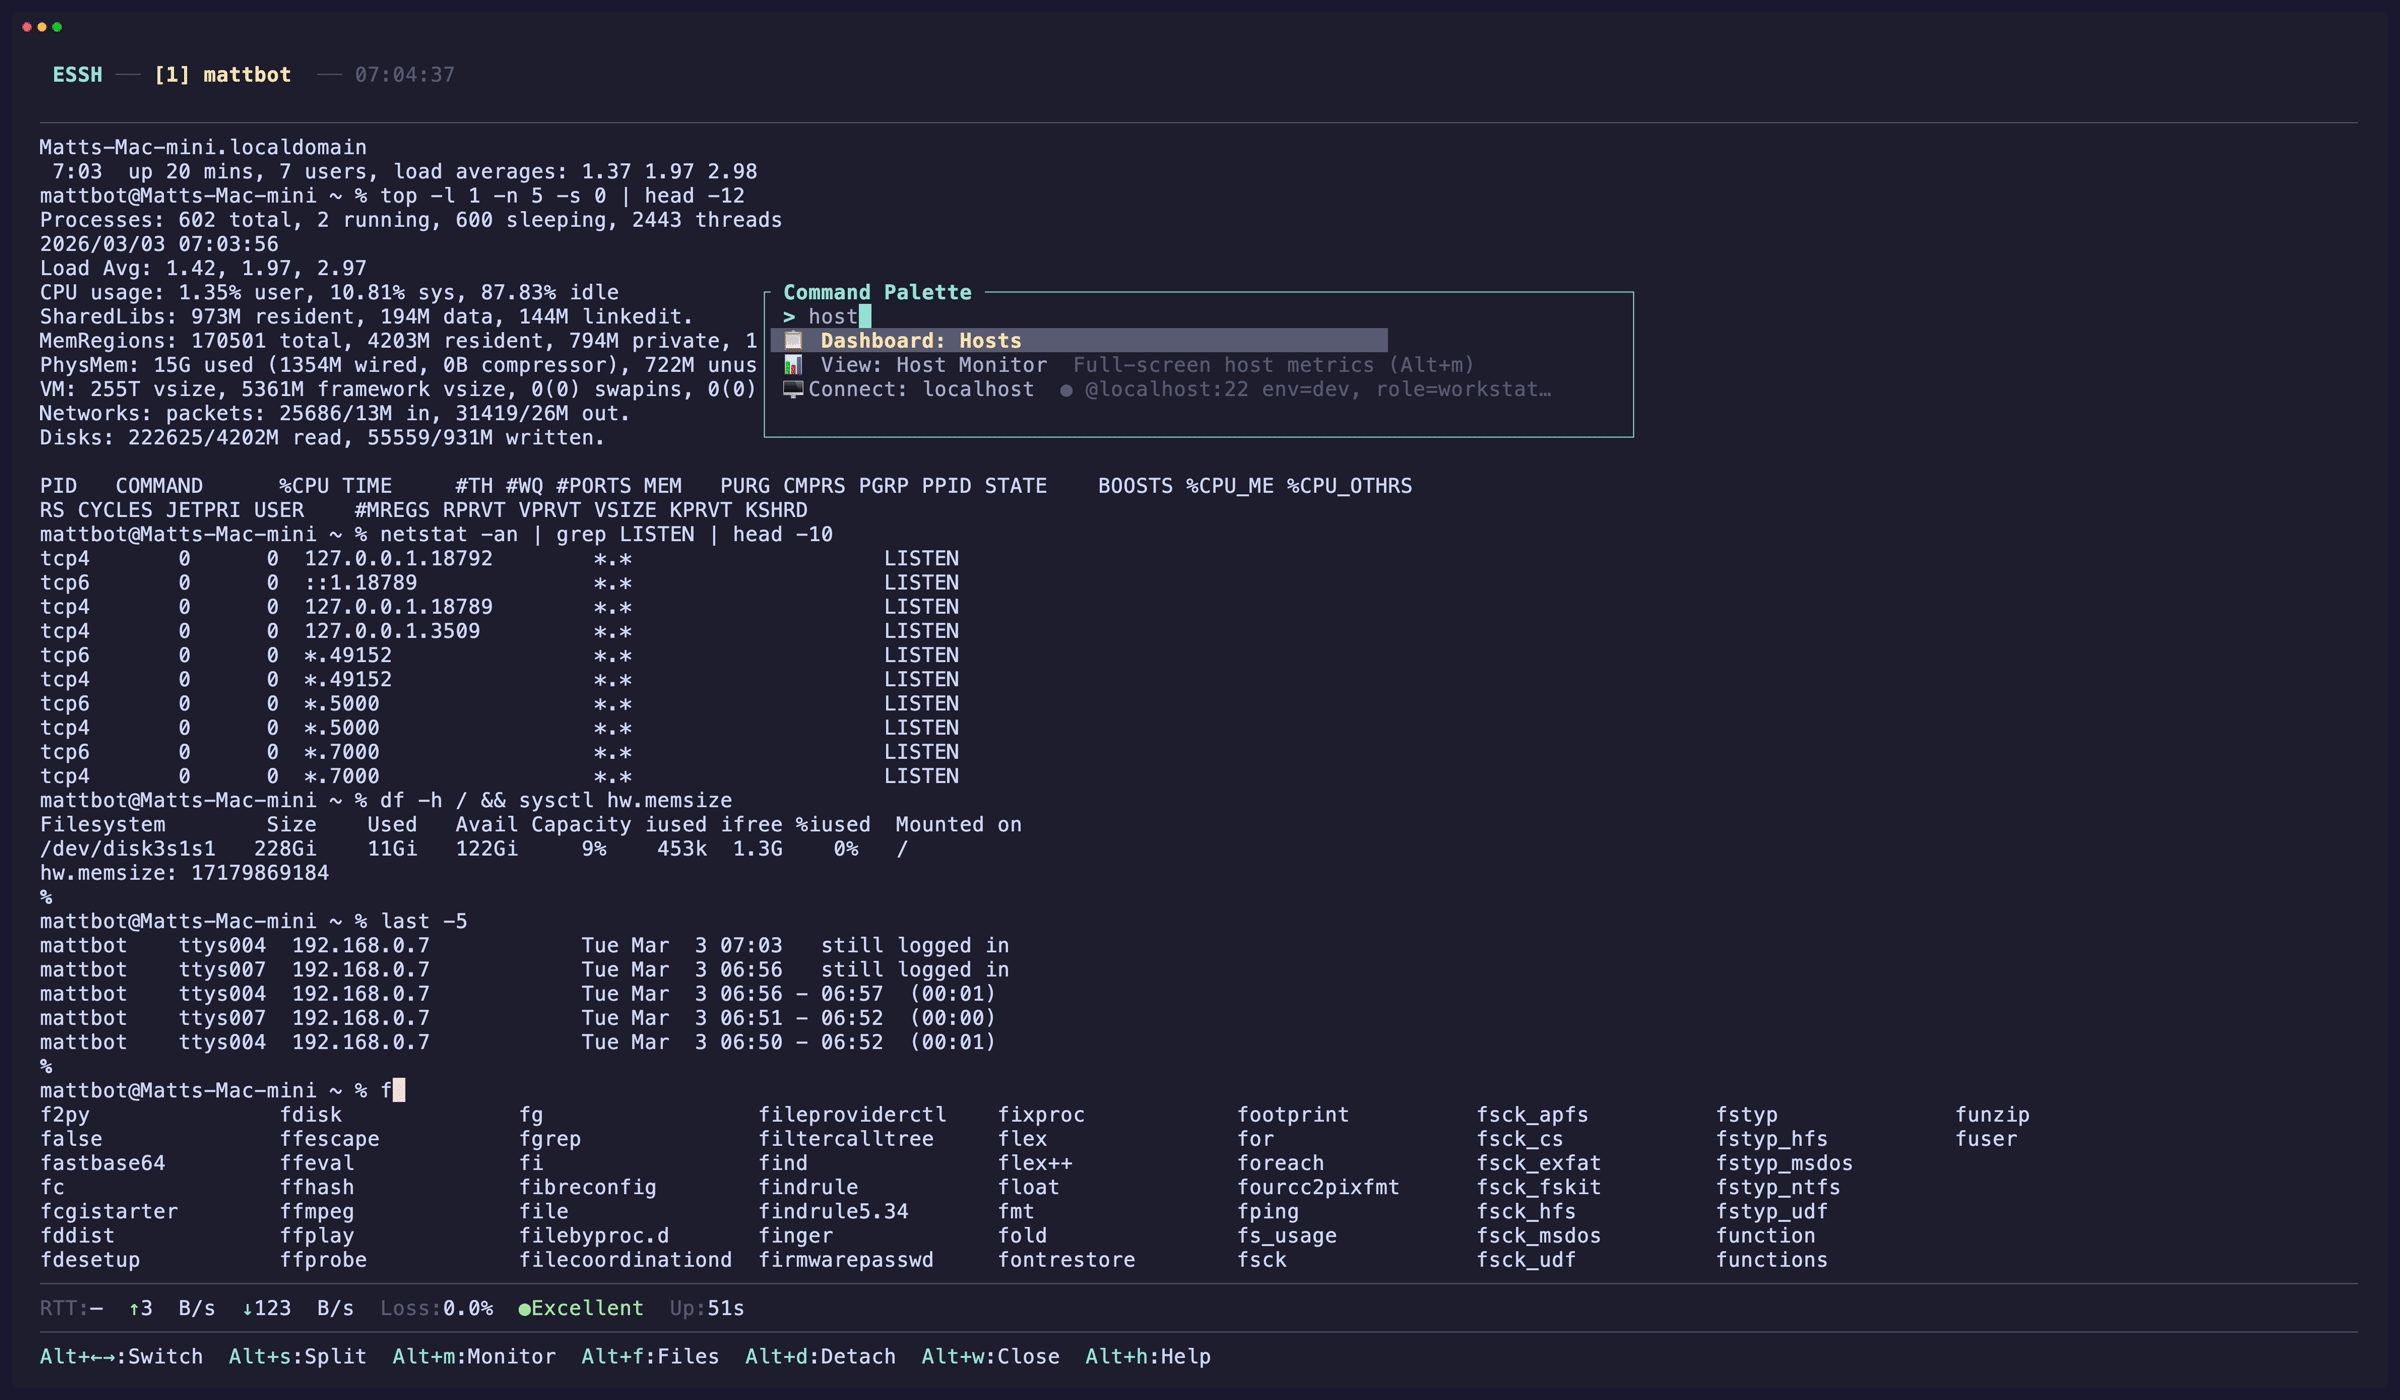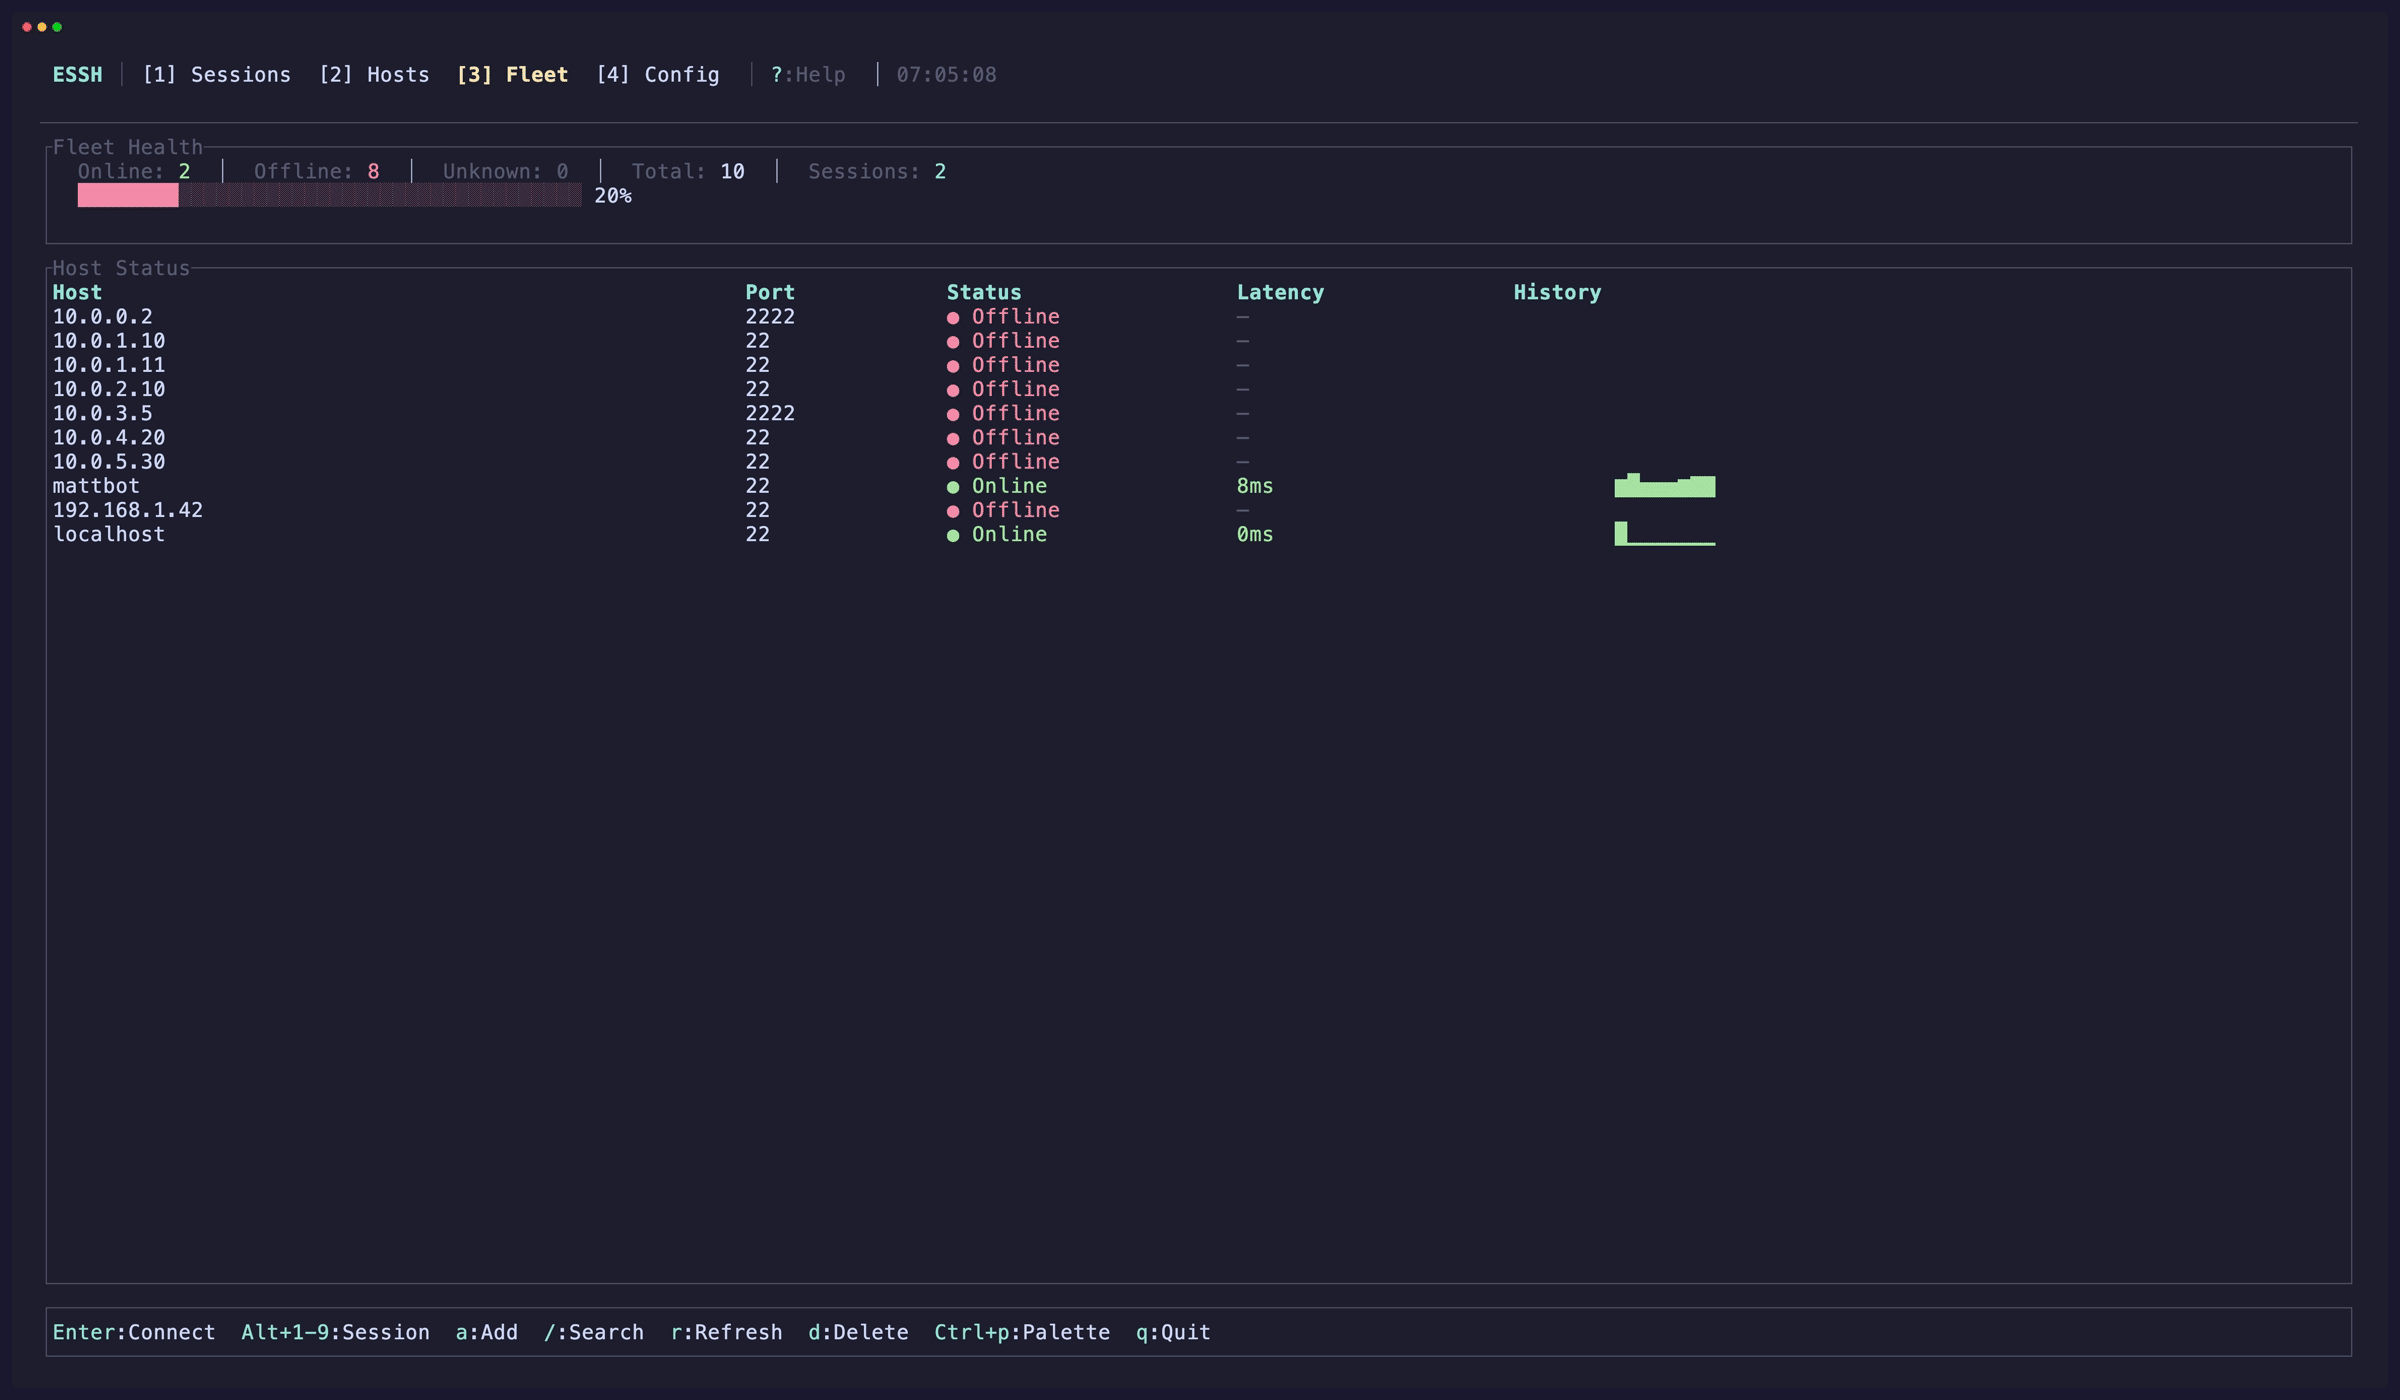 matthart1983/essh
Enhanced SSH client with TUI — manage connections, keys, and sessions
 teamtopkarl/cve-2025-32433
Erlang/OTP SSH 远程代码执行漏洞
 shoucheng3/apache__mina-sshd_cve-2023-35887_2-9-2
Pure Java SSH client/server library implementing SSH-2 protocol with support for multiple ciphers, key exchanges, authentication methods, SFTP, SCP,…
 likekabin/cve-2018-10933_ssh
Python exploit for CVE-2018-10933 that bypasses libssh server authentication and spawns an unauthenticated shell on vulnerable SSH servers.
 openssh/openssh-portable
Portable OpenSSH
 apenwarr/sshuttle
Wrong project! You should head over to http://github.com/sshuttle/sshuttle
 wardgate/wardgate
Security gateway for AI agents - credential-isolated API proxying and policy-gated remote execution (conclaves). Reduce the blast radius!
 kurlee/libssh-exploit
Takes advantage of CVE-2018-10933