
CVE-2026-65400
 horkimhab/cve-2026-65400
Proof-of-concept exploit for CVE-2026-65400 enabling authenticated file read/write, reverse shells, and persistence on macOS via Apple ScreenSharing.
authenticationeducationexploitation+4
3
horkimhab/cve-2026-65400Proof-of-concept exploit for CVE-2026-65400 enabling authenticated file read/write, reverse shells, and persistence on macOS via Apple ScreenSharing.
 r4v3nbl4ck/apache-struts-2-cve-2017-5638-exploit-
Exploit created by: R4v3nBl4ck end Pacman
 dmonst3r/cve-2015-8562
Joomla 1.5 - 3.4.5 Object Injection RCE X-Forwarded-For header
 sbouabid-sec/cve-2023-34468-poc
PoC exploit for CVE-2023-34468 — RCE via H2 RUNSCRIPT in Apache NiFi <= 1.21.0
 kaal18/cve-2022-22909
Python-based exploit for Hotel Druid 3.0.3 Remote Code Execution (CVE-2022-22909). Injects PHP payloads via room names to achieve command execution…
 th3gokul/cve-2024-6387
CVE-2024-6387 : Vulnerability Detection tool for regreSSHion Remote Unauthenticated Code Execution in OpenSSH Server
 gscamelo/cve-2018-20580
A proof of concept for ReadyAPI 2.5.0/2.6.0 Remote Code Execution Vulnerability.
 jackhars/cve-2020-14008
Python exploit for CVE-2020-14008 in ManageEngine Applications Manager delivering a SYSTEM-level reverse shell via authenticated remote code…
 archi73ct/cve-2020-0609
Proof-of-concept exploit for CVE-2020-0609 that crashes a Remote Desktop Gateway server by sending a crafted UDP packet to port 3391.
 razureink/cve-2025-32433-erlang_ssh_rce_reproduction
Reproduction of cve-2025-32433-erlang_ssh_rce_reproduction
 jozliner/cve-2019-5392-for-python3
Legacy HPE iMC vuln
 hd-exe/cve-2009-2265-fix
fix for not working exploit script on exploitdb (50057.py)
 squid22/webmin_cve-2019-15107
CVE-2019–15107 - Unauthenticated RCE Webmin <=1.920
 xfox64x/cve-2016-5640
Crestron AirMedia AM-100 RCE (CVE-2016-5640) Metasploit Module
 principalanthony/cve-2024-6387-updated-x64bit
Private x64 RCE exploit for CVE-2024-6387 [02.07.2024] from exploit.in
 divinepwner/terramaster-tos-cve-2020-15568
Repository for CVE-2020-15568 Metasploit module
 yym8538/cve-2026-21858
Docker-based PoC environment and exploit script for CVE-2026-21858, an n8n 1.120.4 arbitrary file read and RCE flaw, providing secret extraction and…
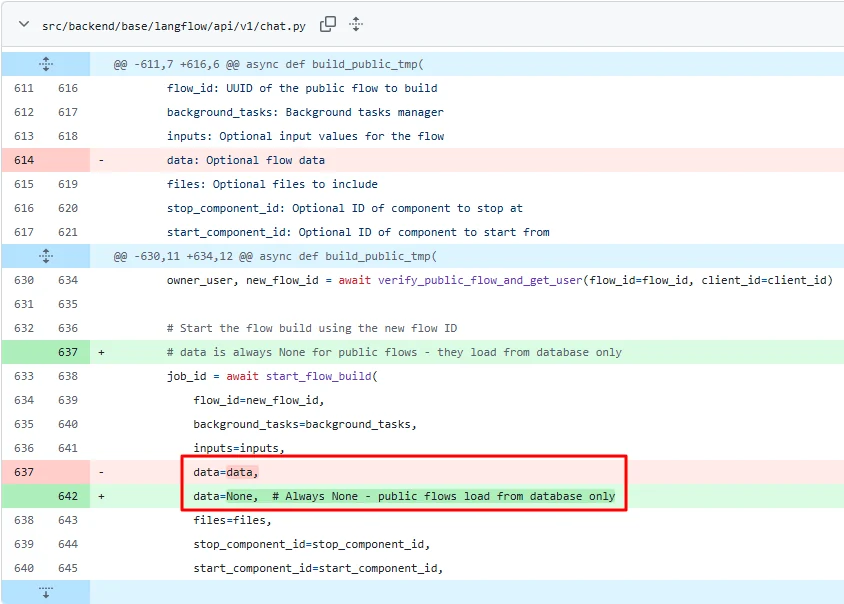 yym8538/cve-2026-33017
Proof-of-concept exploit for CVE-2026-33017, an unauthenticated RCE in Langflow's build_public_tmp endpoint, injecting a malicious custom component…