

CVE-2025-58434-59528
 azureadtrent/cve-2025-58434-59528
CVE-2025-58434 and CVE-2025-59528 chain POC
authenticationexploitationpenetration-testing+3
5
azureadtrent/cve-2025-58434-59528CVE-2025-58434 and CVE-2025-59528 chain POC
 btamburi/strutszeiro
Telegram Bot to manage botnets created with struts vulnerability(CVE-2017-5638)
 jumpserver/jumpserver
JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH,…
 freerdp/freerdp
FreeRDP is a free remote desktop protocol library and clients
 paramiko/paramiko
The leading native Python SSHv2 protocol library.
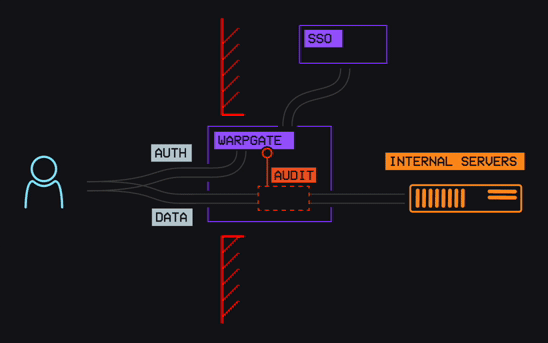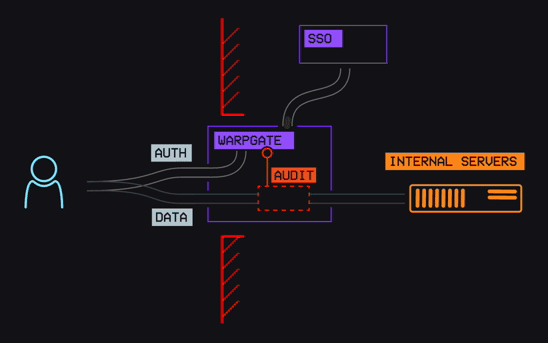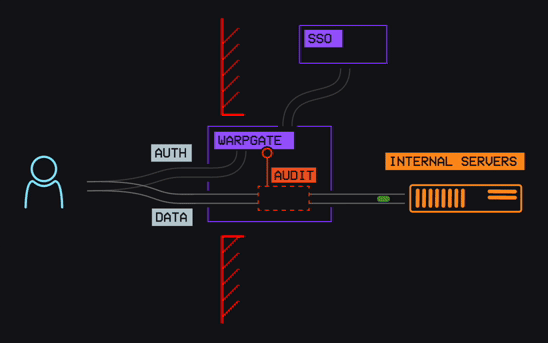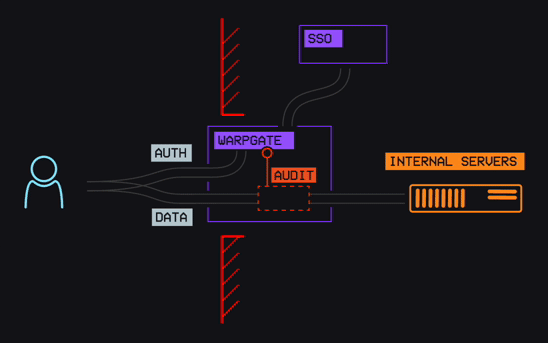 warp-tech/warpgate
Fully transparent SSH, HTTPS, Kubernetes, database and RDP/VNC bastion/PAM that doesn't need additional client-side software
 bastillion-io/bastillion
Bastillion gives you a clean, browser-based way to manage SSH access across all your systems—like a bastion host with a friendly dashboard.
 mwiede/jsch
fork of the popular jsch library
 nccgroup/sshession
The SSH Multiplex Backdoor Tool
 virgula0/poc-cve-2018-10933
LibSSH Authentication Bypass Exploit using RCE
 9aylas/backdooring-zmm100-fingerprint-devices
AuthBypass & Auto Backdooring Devices
 dollarboysushil/cve-2024-47533-cobbler-xmlrpc-authentication-bypass-rce-exploit-poc
CVE-2024-47533 is a critical authentication bypass vulnerability in Cobbler (versions 3.0.0 to before 3.2.3 and 3.3.7) allowing unauthenticated…
 34zy/cve-2025-52970
CVE-2025-52970 - FortiWeb Authentication Bypass to Remote Code Execution Exploit
 gotr00t0day/cve-2022-1388
A remote code execution vulnerability exists in the iControl REST API feature of F5's BIG-IP product. An unauthenticated, remote attacker can exploit…
 baph00met/cve-2024-47533
CVE-2024-47533: Cobbler Authentication Bypass & Code Execution
 gmh5225/gatekeeper
Self-hosted SSH access gateway in Go with OIDC/LDAP auth, RBAC, MFA, session recording, audit export, encryption at rest, IP rules, and policy…