
CVE-2022-46080
 yerodin/cve-2022-46080
Nexxt Router 15.03.06.60 Authentication Bypass and Remote Command Execution
authenticationexploitationpenetration-testing+3
yerodin/cve-2022-46080Nexxt Router 15.03.06.60 Authentication Bypass and Remote Command Execution
 exploitwritter/cve-2022-25060
This script exploits a remote command execution vulnerability under the oal_startPing component in the TPLink WR840N router.
 apenwarr/sshuttle
Wrong project! You should head over to http://github.com/sshuttle/sshuttle
 wangxso/cve-2025-66478-poc
CVE-2025-66478 Proof of Concept

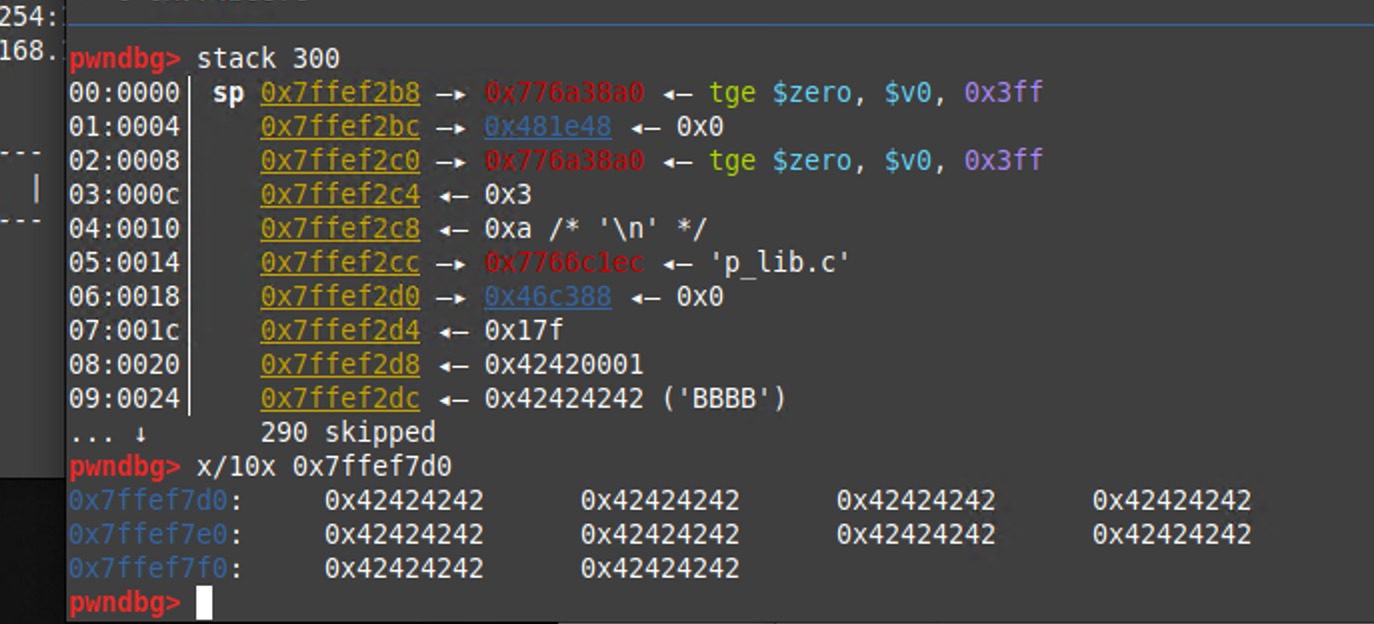 laskdjlaskdj12/cve-2024-29671-poc
This is POC of CVE-2024-29671