
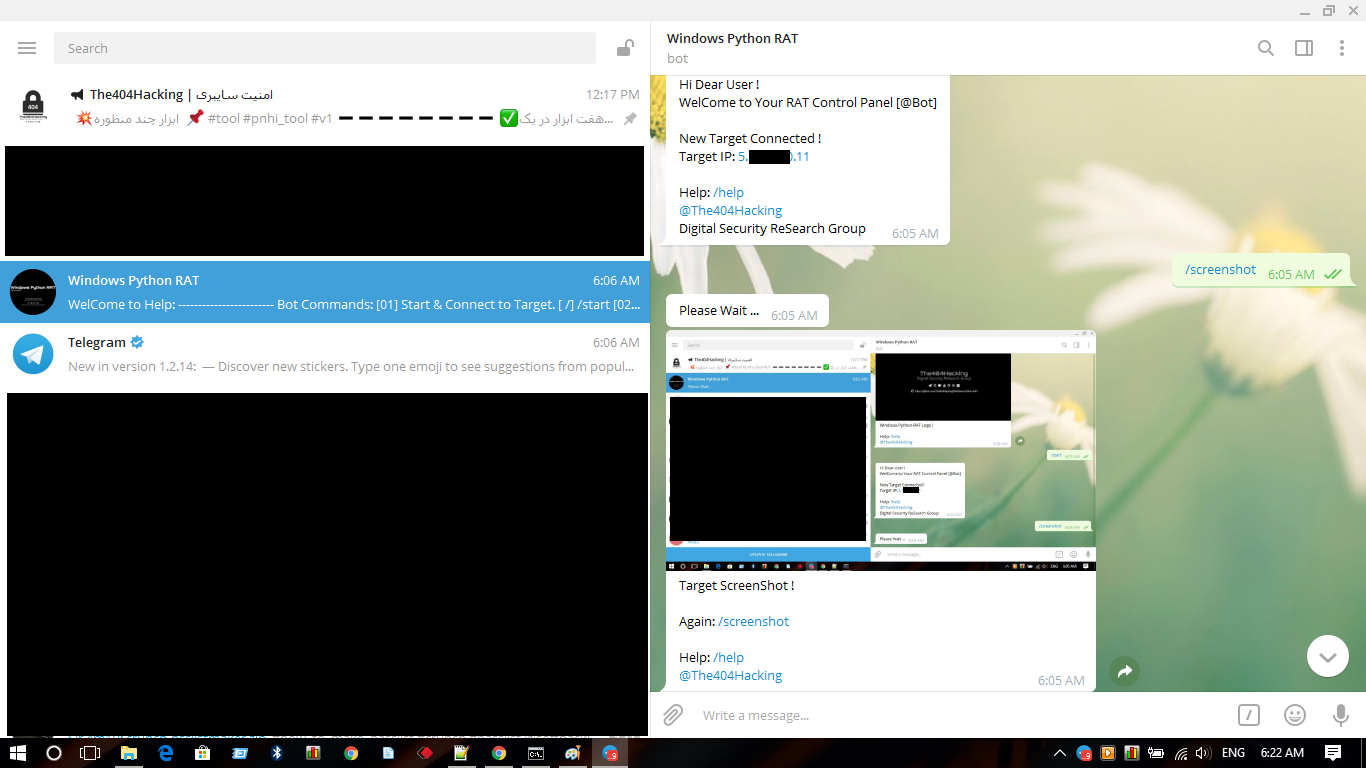
Windows-Python-RAT
 the404hacking/windows-python-rat
A New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.
api-securitycommand-and-controlpayload-development+3
118
the404hacking/windows-python-ratA New Microsoft Windows Remote Administrator Tool [RAT] with Python by Sir.4m1R.
 bkup/slackshell
PowerShell to Slack C2
 payatu/quickheal
CVE-2017-5005 for Quick Heal Antivirus
 mr-wolf-gb/d-rat_vb.net_mysql_php
D-RAT [VB.NET]+[MySQL]+[PHP]
 rbowes-r7/refreshing-soap-exploit
A PoC exploit for CVE-2022-41622 - a CSRF in F5 BIG-IP control plane that leads to remote root
 ivanitlearning/cve-2017-17562
Standalone Python 3 exploit for CVE-2017-17562 targeting GoAhead web server 2.5–3.6.5 with automated CGI endpoint discovery and reverse shell payload…
 synacktiv/ccmmessagingbackdoor
Proof-of-concept backdoor for SCCM Management Point using rogue COM service for persistent remote command execution as SYSTEM.
 c411e/cve-2024-53691
CVE-2024-53691
 geffner/cve-2020-8289
Proof-of-concept exploit for CVE-2020-8289 demonstrating remote code execution as SYSTEM/root via Backblaze backup client's SSL verification bypass…
 richard-tang/sscms-pluginshell
CVE-2022-28118
 mbadanoiu/cve-2023-34468
CVE-2023-34468: Remote Code Execution via DB Components in Apache NiFi
 keklick1337/cve-2025-55182-golang-poc
Go-based proof-of-concept for CVE-2025-55182, a critical RCE in React Server Components. Features vulnerability checking, command execution, memory…
 0-d3y/langflow-rce-exploit
Remote Code Execution Exploit for Langflow (CVE-2025-3248) - [ By S4Tech ]
 e4zyy/project-cve-2026-33017
CVE-2026-33017 - Langflow Unauthenticated RCE Exploit
 evergreencartoons/senselessviolence
CVE-2022-31814 Exploitation Toolkit.
 homjxi0e/cve-2017-0108
Proof-of-concept exploit for CVE-2017-0108, a remote code execution vulnerability in Microsoft Windows Graphics Component, triggered via crafted…
 joshuavanderpoll/cve-2026-44262
Unauthenticated RCE in dedoc/scramble — PoC, Nmap NSE & Nuclei template.
 mroplus/cve-2026-41940
Exploit for CVE-2026-41940 providing direct shell access via websocket and persistence through root API key injection.