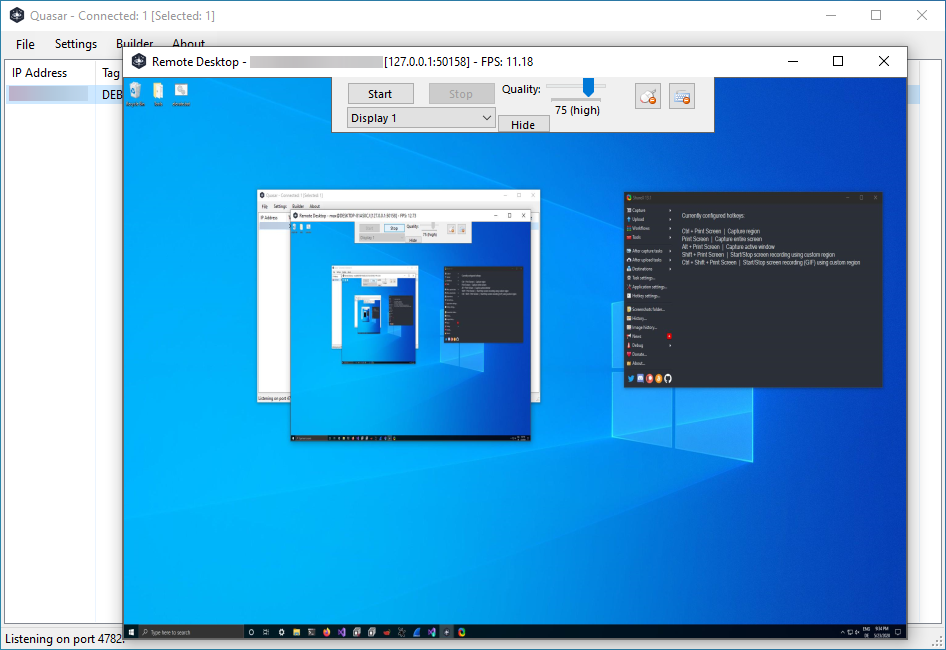
XeytanWxCpp-RAT
 melardev/xeytanwxcpp-rat
Work in Progress. RAT written in C++ using wxWidgets
command-and-controlinformation-gatheringpayload-development+3
11
melardev/xeytanwxcpp-ratWork in Progress. RAT written in C++ using wxWidgets
 qurtidev/wsus-cve-2025-59287-rce
Exploit script written in C# to aid gaining a reverse shell on targets with Windows Server Update Service(WSUS) CVE-2025-59287.
 stickxx00/cups-rce-exploit
C++ exploit for unauthenticated remote code execution on CUPS via CVE-2024-47176 chain.
 carlosalbertotuma/cve-2025-32433
Python exploit for CVE-2025-32433 targeting Erlang SSH remote code execution with reverse shell and command execution capabilities.
 gps1949/cve-2021-25646
Python exploit for Apache Druid remote code execution (CVE-2021-25646) with reverse shell and command execution capabilities.
 coldzer0/reversesock5proxy
A tiny Reverse Sock5 Proxy written in C :V
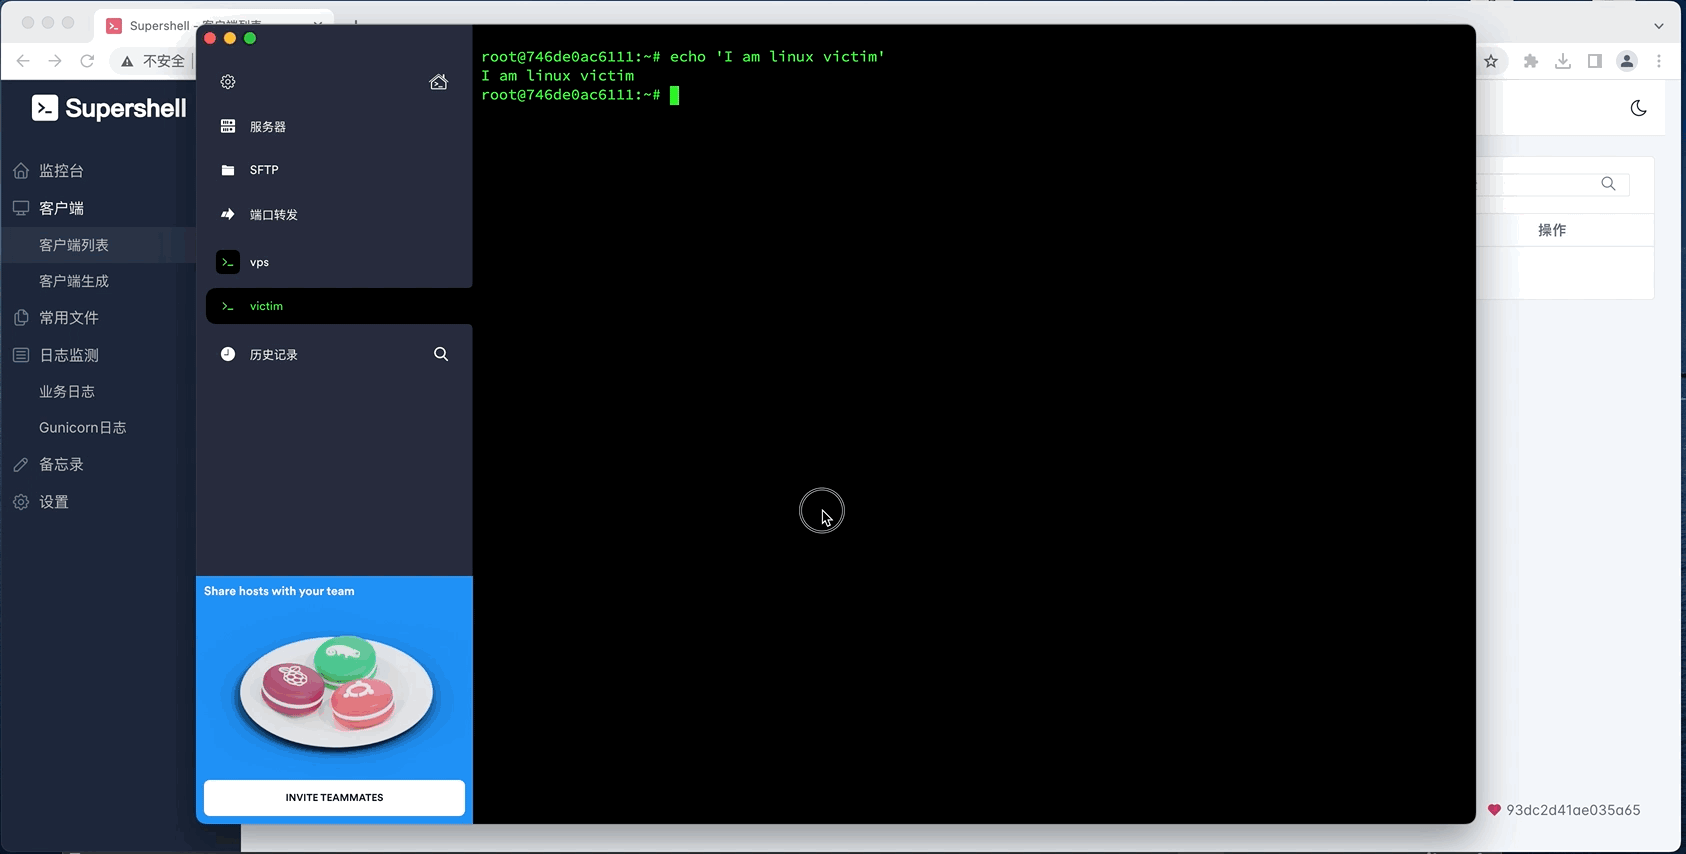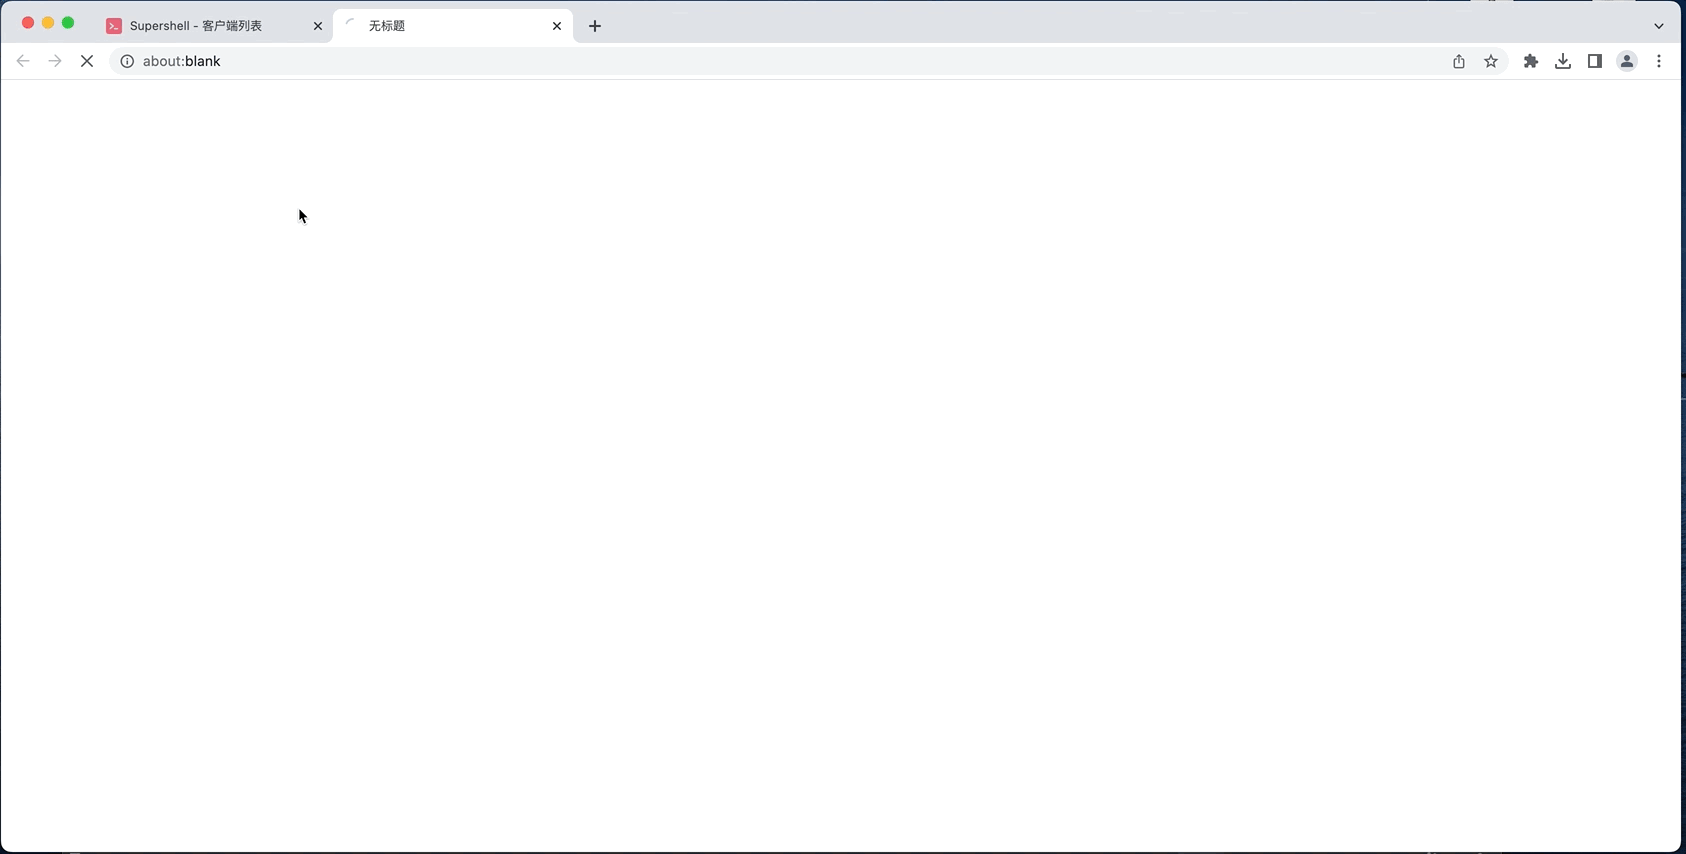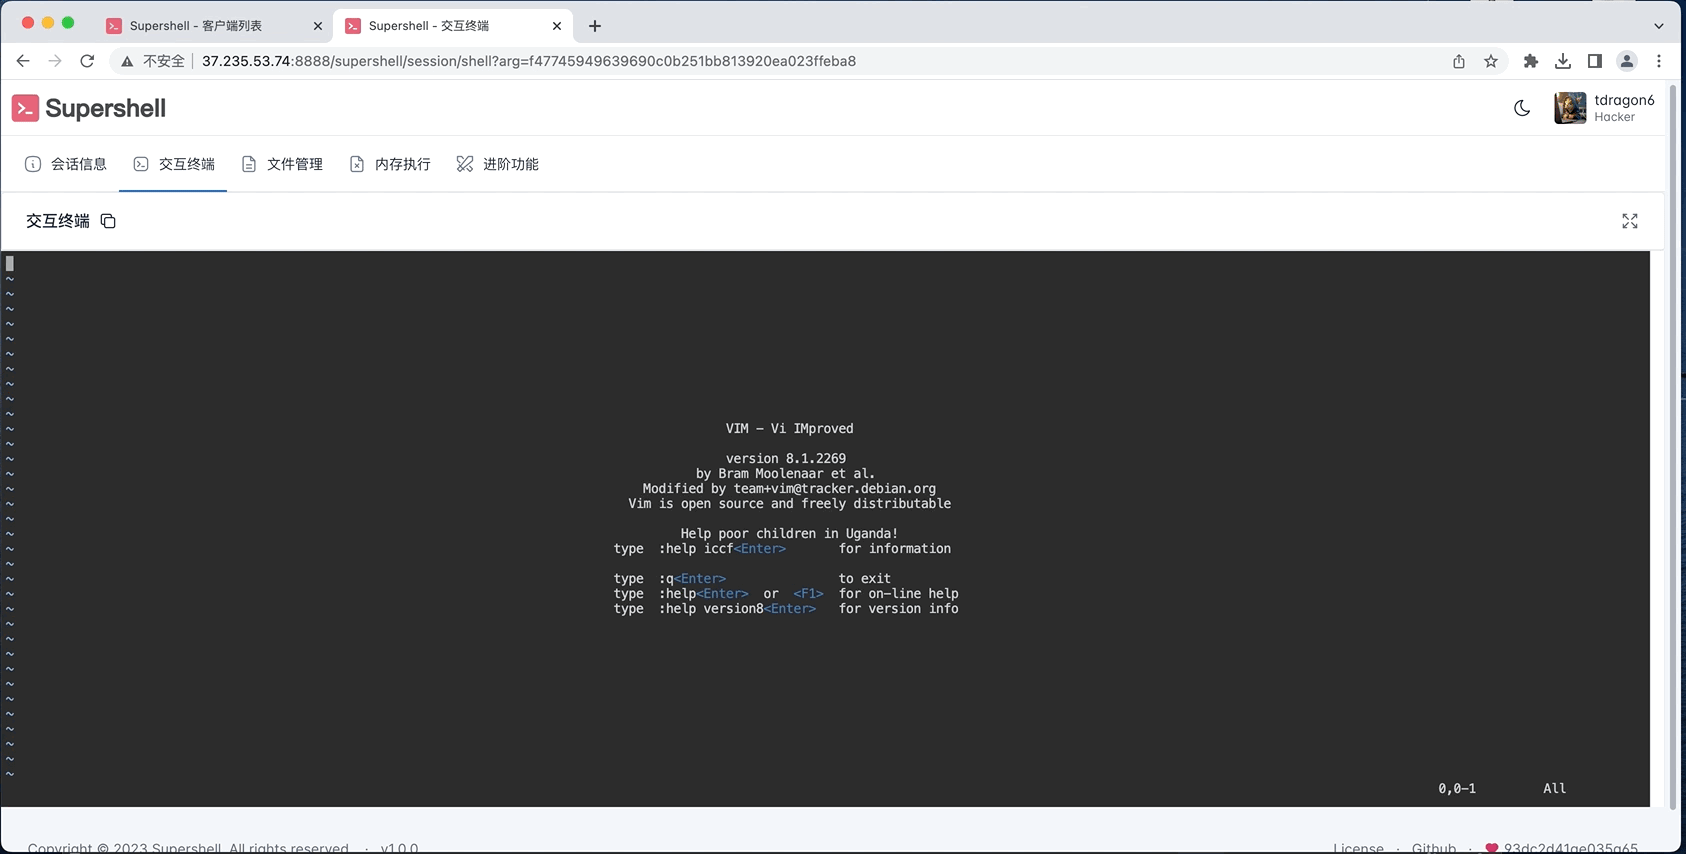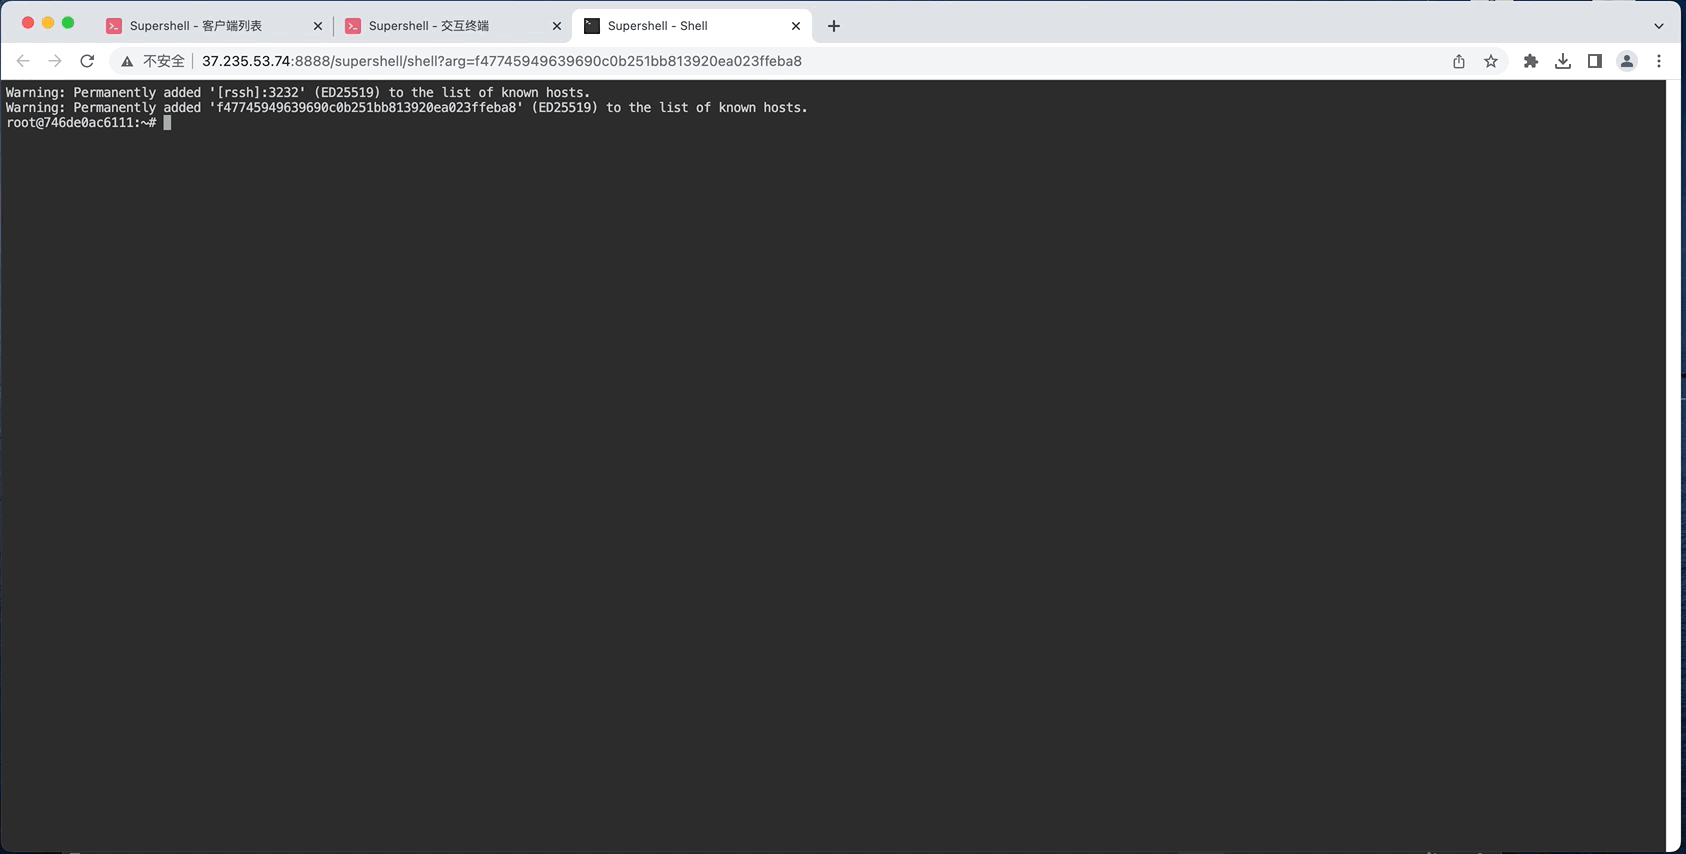 tdragon6/supershell
Supershell C2 远控平台,基于反向SSH隧道获取完全交互式Shell
 skyblueeternal/cnvd-c-2019-48814-cnnvd-201904-961
CVE-2019-2725poc汇总 更新绕过CVE-2017-10271补丁POC
 libraggbond/cve-2018-3191
CVE-2018-3191 反弹shell
 jun-5heng/cve-2021-26084
confluence远程代码执行RCE / Code By:Jun_sheng
 bambooqj/cve-2025-3248
Langflow 在对用户提交的“验证代码”做 AST 解析和编译时,在未做鉴权与沙箱限制的情况下调用了 Python 的 compile()/exec()(以及在编译阶段会评估函数默认参数与装饰器),攻击者可把恶意载荷放在参数默认值或装饰器里,借此在服务器上下文中执行任意语句(反弹…
 sashka3076/f5-big-ip-exploit
CVE-2022-1388
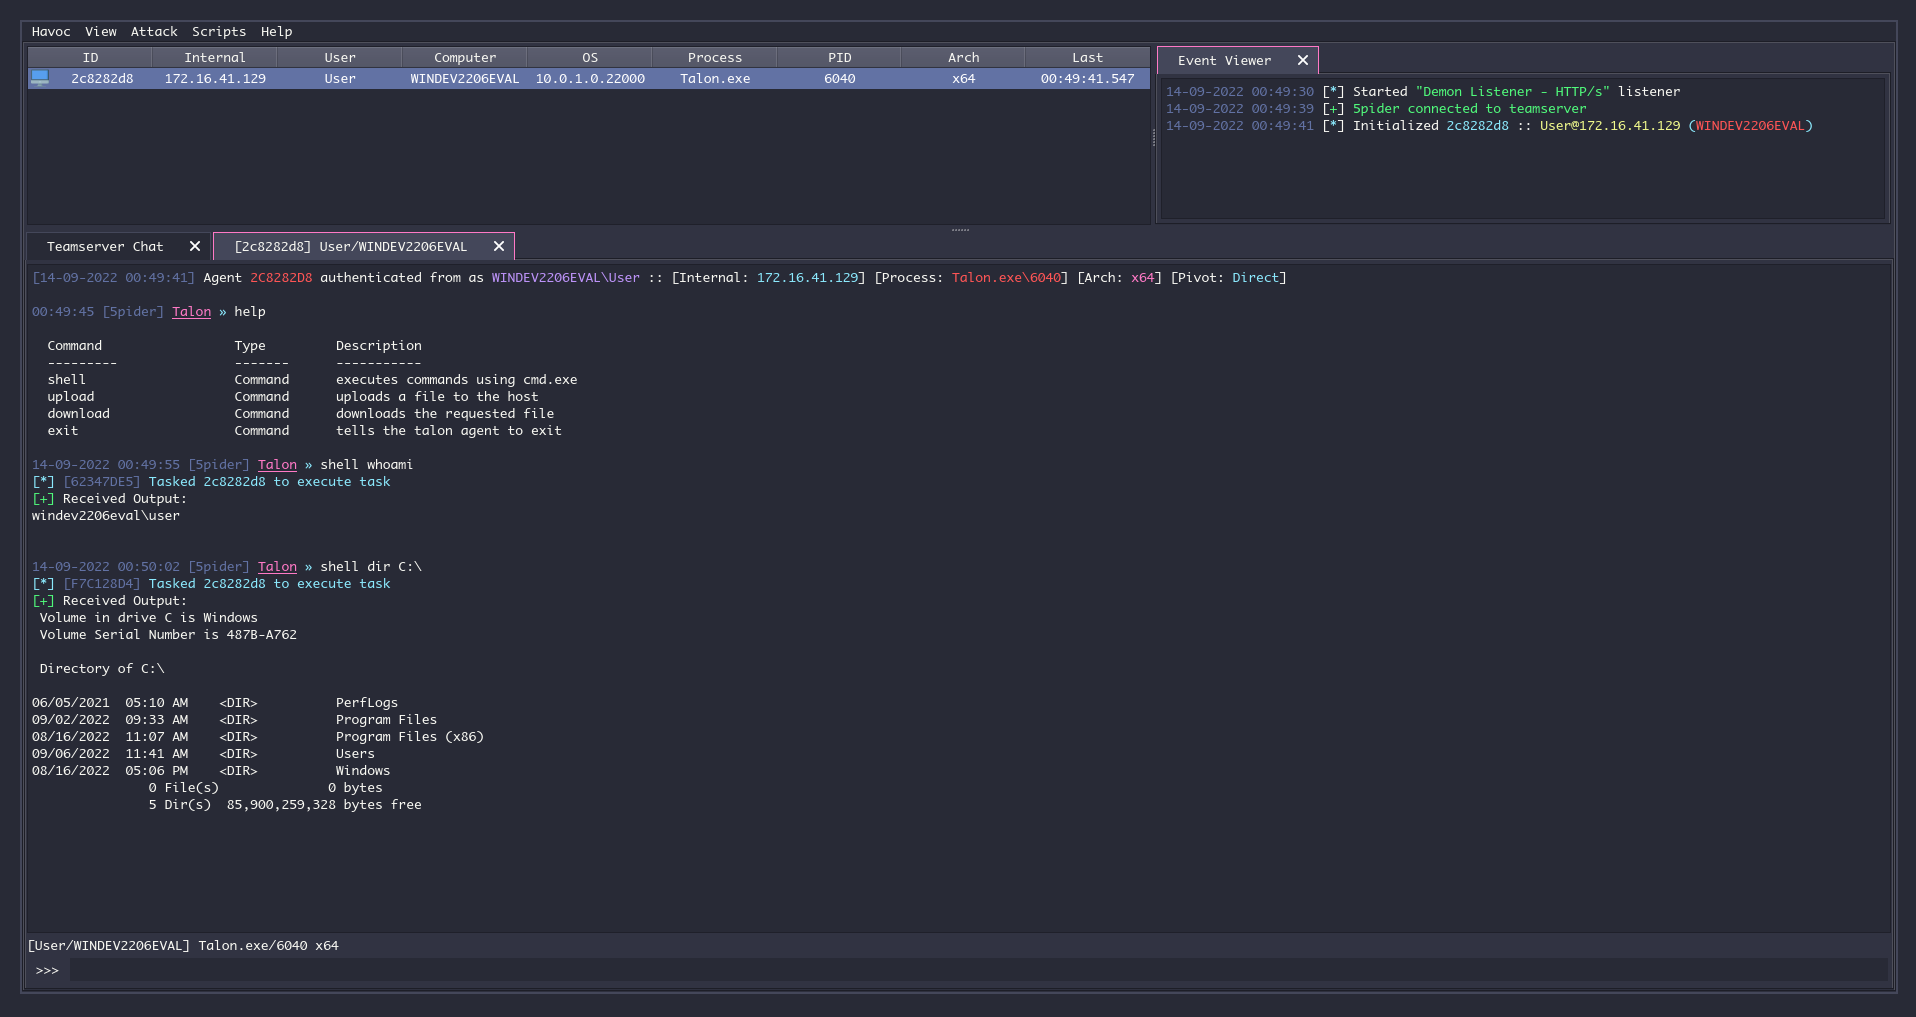
 0xtriboulet/revenant
Revenant - A 3rd party agent for Havoc that demonstrates evasion techniques in the context of a C2 framework