

CVE-2021-22941
 hoav18/cve-2021-22941
Python exploit for CVE-2021-22941 targeting Citrix ShareFile RCE with shell and ping options for remote command execution and network probing.
exploitationpenetration-testingred-teaming+3
13
hoav18/cve-2021-22941Python exploit for CVE-2021-22941 targeting Citrix ShareFile RCE with shell and ping options for remote command execution and network probing.
 0xcan1337/cve-2025-47812-poc
Simple exploit for Wing FTP Server RCE (CVE-2025-47812) to run commands and get a reverse shell. For educational use only.
 estebanzarate/cve-2025-47812-wing-ftp-server-7.4.3-unauthenticated-rce-poc
Proof-of-concept exploit for CVE-2025-47812: unauthenticated remote code execution in Wing FTP Server <= 7.4.3 via NULL byte injection in the…
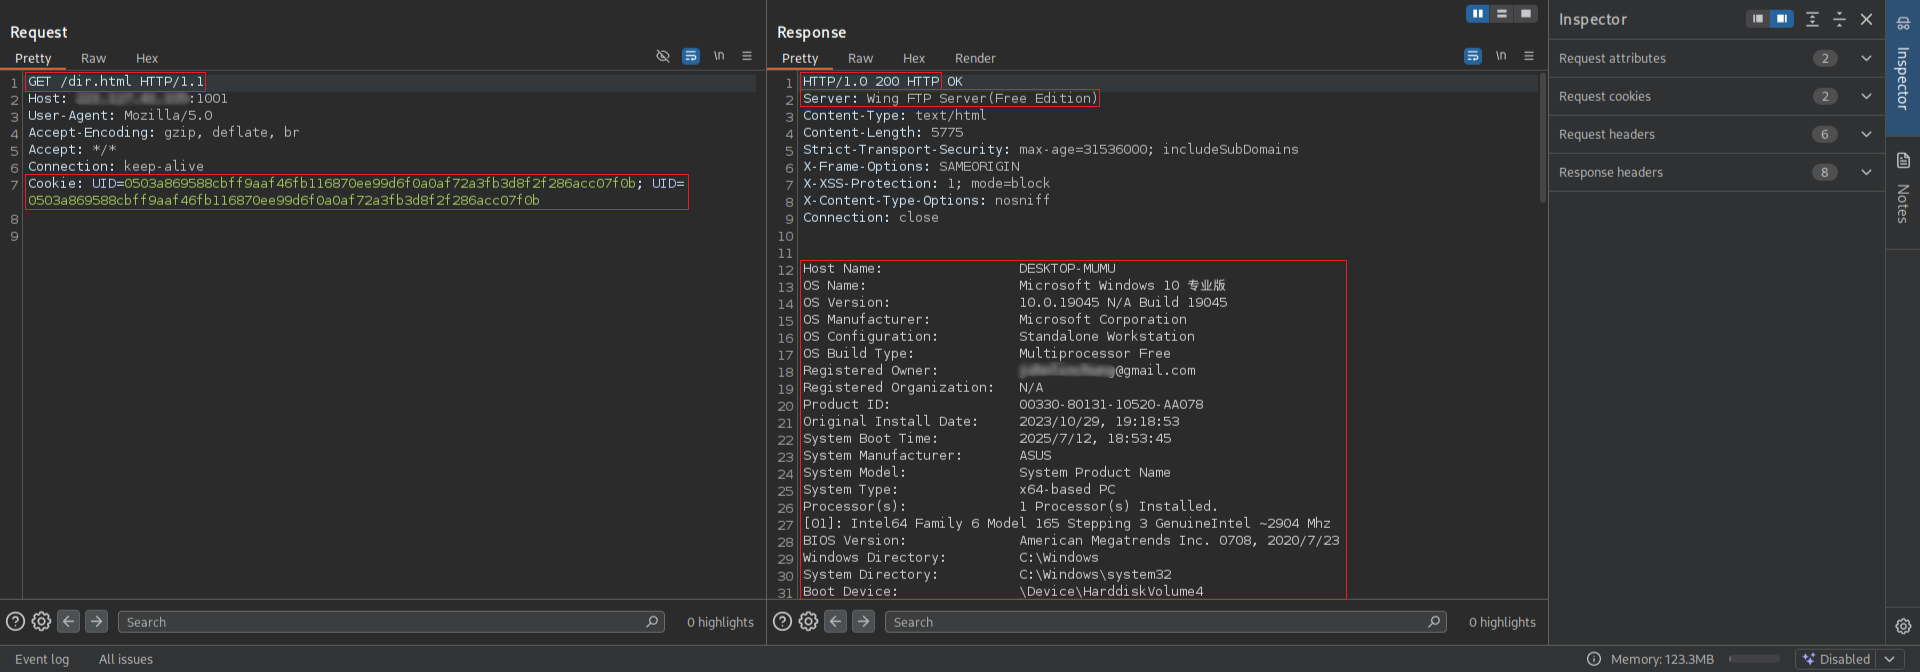 r0otk3r/cve-2025-47812
Python exploit for CVE-2025-47812, achieving remote code execution on Wing FTP Server via Lua injection in the login username parameter. Supports…
 blindma1den/cve-2025-47812
Unauthenticated remote code execution exploit for Wing FTP Server < 7.4.4, enabling command execution and reverse shells via Lua injection in session…
 0xjuarez/cve-2025-47812
Exploit and scanner for CVE-2025-47812 targeting Wing FTP Server unauthenticated remote code execution, supporting single-target, mass scanning,…
 havbay/cve-2025-47812-poc
Unauthenticated remote code execution exploit for Wing FTP Server (CVE-2025-47812) with multiple reverse shell payloads, interactive and CLI modes,…
 matesz44/cve-2025-47812
CVE-2025-47812: Wing FTP Server 7.4.3 UnauthN RCE in sh
 ill-deed/wingftp-cve-2025-47812-illdeed
Remote Command Execution exploit for Wing FTP Server (CVE-2025-47812)
 cotherm/cve-2025-25705
Proof-of-concept exploit for authenticated remote code execution via command injection in ProApps Enterprise Appliance ping functionality, with…
 j2ekim/cve-2021-25646
Python exploit for Apache Druid remote code execution vulnerability CVE-2021-25646, enabling command injection via crafted HTTP requests.
 shadowgit30/cve-2025-47812
CVE-2025-47812 POC
 zemarkhos/cve-2026-44403-wingftp-v8.1.2-poc-exploit
CVE-2026-44403-WingFTP-v8.1.2-POC-Exploit
 agilevatester/flaskcache_cve-2021-33026_poc
PoC exploit for CVE-2021-33026 that poisons Redis cache in Flask-Cache to achieve remote code execution via malicious pickle deserialization.
 kali-dass/cve-2021-44228-log4shell
Java-based proof-of-concept exploit for CVE-2021-44228 (Log4Shell) enabling remote command execution, OS information gathering, and arbitrary…
 popyue/cve-2025-47812
RCE for WingFTP v4.7.3
 dkstar11q/blackash-cve-2025-47812
CVE-2025-47812