

CVE-2025-59287
 garvitv14/cve-2025-59287
Automated exploit for CVE-2025-59287, an unauthenticated RCE in WSUS, featuring payload generation, reverse shell listener, and AES encryption with…
command-and-controlexploitationpayload-generation+4
16
garvitv14/cve-2025-59287Automated exploit for CVE-2025-59287, an unauthenticated RCE in WSUS, featuring payload generation, reverse shell listener, and AES encryption with…
 tc4dy/cve-2026-67279-86060-toolkit
Python toolkit for the MikroTrick MikroTik RouterOS SSH pre-auth takeover chain: exploit.py performs rekey bypass and fd-2 policy swap for admin…
 hev0x/cve-2021-26828_scadabr_rce
Proof-of-concept exploit for CVE-2021-26828 enabling authenticated remote code execution on ScadaBR SCADA systems via JSP file upload. Supports…
 otsmane-ahmed/cve-2025-2620-poc
Proof-of-concept exploit for CVE-2025-2620, a critical stack-based buffer overflow in D-Link DAP-1620 routers enabling unauthenticated remote code…
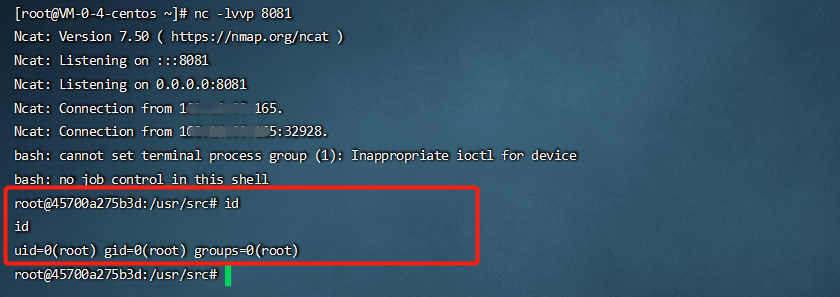 secnn/struts2_s2-062_cve-2021-31805
Python exploit for Apache Struts2 S2-062 (CVE-2021-31805) remote code execution, with Docker-based reproduction environment and reverse shell payload…
 0xcan1337/cve-2025-47812-poc
Simple exploit for Wing FTP Server RCE (CVE-2025-47812) to run commands and get a reverse shell. For educational use only.
 tc4dy/cve-2026-61511-poc-exploit
CVE-2026-61511 – vBulletin Pre-Auth RCE (CVSS 9.8). Vuln 5.x/6.x (unpatched). Multi-exploit via Endpoint Pool, AJAX, PHPFuck WAF bypass. Full…
 kartik2005221/cve-2025-58434-and-59528-poc
Modular PoC for CVE-2025-58434 (account takeover) and CVE-2025-59528 (RCE) in Flowise. Automates the full attack chain from unauthenticated token…
 p3ta00/react2shell-poc
CVE-2025-55182 React2Shell PoC - Critical RCE in React Server Components / Next.js. CVSS 10.0. Error-based exfil, reverse shell, interactive mode.
 thelastvvv/cve-2021-42013_reverse-shell
PoC CVE-2021-42013 reverse shell Apache 2.4.50 with CGI
 darrenmartyn/cve-2020-8515
Proof-of-concept exploit for CVE-2020-8515 command injection in Draytek routers. Includes automated exploitation, reverse shell delivery, and…
 geniuszly/cve-2024-7029
PoC exploit for CVE-2024-7029 in AvTech devices. Scans for vulnerable targets and provides an interactive remote shell for command execution with…
 jonaschen0103/cve-2026-33439-poc
Python PoC exploiting CVE-2026-33439, a pre-auth RCE in OpenAM via Java deserialization of the jato.clientSession parameter, with interactive and…
 blue0x1/nimrm
Native Nim WinRM shell with NTLM, Kerberos, file transfer, in-memory helpers, and AD/OPSEC reporting
 hackzuoji/freeswitch-cve-2026-116779-poc
Detection and exploitation toolkit for the FreeSWITCH SIP MESSAGE command injection (CVE-2026-116779), with API execution, DNS OAST shell output,…
 r3vpwnx/cve-2025-55182
Standalone exploit for CVE-2025-55182 achieving unauthenticated RCE in Next.js App Router via React Server Components Flight deserialization, with…
 maxprog-svg/cve-2026-76504-cisco
Python exploit for CVE-2026-76504, a Cisco Catalyst SD-WAN Manager authentication bypass via percent-encoded j_security_check, with token theft, API…
 tc4dy/cve-2026-6875-poc-exploit
CVE-2026-6875 ServiceNow Pre-Auth RCE Framework 🔥 JS Injection → Sandbox Escape → RCE → Root. Features: --detect, --exec, reverse/interactive shell,…