
CVE-2026-78159
 abraxas/cve-2026-78159
Proof-of-concept exploit for CVE-2026-78159, an unauthenticated RCE in The Events Calendar WordPress plugin via the parse_array widget classes sink.
exploitationpenetration-testingremote-access-tool+3
1
abraxas/cve-2026-78159Proof-of-concept exploit for CVE-2026-78159, an unauthenticated RCE in The Events Calendar WordPress plugin via the parse_array widget classes sink.
 abraxas/cve-2026-18937
Proof-of-concept exploit and lab reproduction pack for CVE-2026-18937, an unauthenticated RCE in the Broken Link Checker WordPress plugin before…
 crowsec-edtech/cve-2026-87902
Python PoC exploiting CVE-2026-87902, an unauthenticated path traversal in WordPress locate_template() leading to LFI and PEAR-based RCE, with safe…
 zyphorixofficialmain-lab/cve-2026-87902
Python exploit for CVE-2026-87902, a WordPress Core LFI-to-RCE chain. Fingerprints versions, writes a PHP shell via pearcmd, and provides command…
 fl0ydsec/cve-2026-63030
Python mass exploit and detector for the WordPress Core pre-auth RCE chain CVE-2026-63030 and CVE-2026-60137, chaining SQL injection into remote code…
 vulpecuna/cve-2026-87902
Python PoC for CVE-2026-87902, an unauthenticated WordPress path traversal RCE via get_page_template(), with version fingerprinting, theme checks,…
 bhideki/cve-2026-87902
Python PoC and scanner for CVE-2026-87902, a WordPress core path traversal leading to LFI and PEAR-based RCE, with WAF bypass and automated…
 pwnvader/cve-2026-87902-poc-pwnvader
Shell PoC for CVE-2026-87902, an unauthenticated WordPress core LFI via page-template resolution that chains to RCE through pearcmd.php.
 nxploited/cve-2026-14894
Multi-threaded mass exploiter chaining unauthenticated WordPress file-upload flaws in Super Forms and Elementor Pro to deploy and verify a PHP web…
 g0d150ne/xss2shell
Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…
 g0d150ne/wp2shell
Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…
 joelgmsec/pyshell
Multi-platform Python webshell providing remote shell access on web servers with command history, file upload/download, and directory traversal…
 c0gnit00/wp2shell
Exploit POC for Wp2Shell, CVE-2026-63030 + CVE-2026-63137
 joshuavanderpoll/cve-2026-54806
Proof-of-concept exploit for CVE-2026-54806: unauthenticated PHP object injection in WP Activity Log plugin enabling blind RCE via User-Agent header.…
 nxploited/cve-2026-1555
WebStack <= 1.2024 - Unauthenticated Arbitrary File Upload
 bootstrapbool/cve-2026-4257
Exploit for CVE-2026-4257: Server-Side Template Injection in Contact Form by Supsystic WordPress plugin (≤1.7.36) enabling unauthenticated remote…
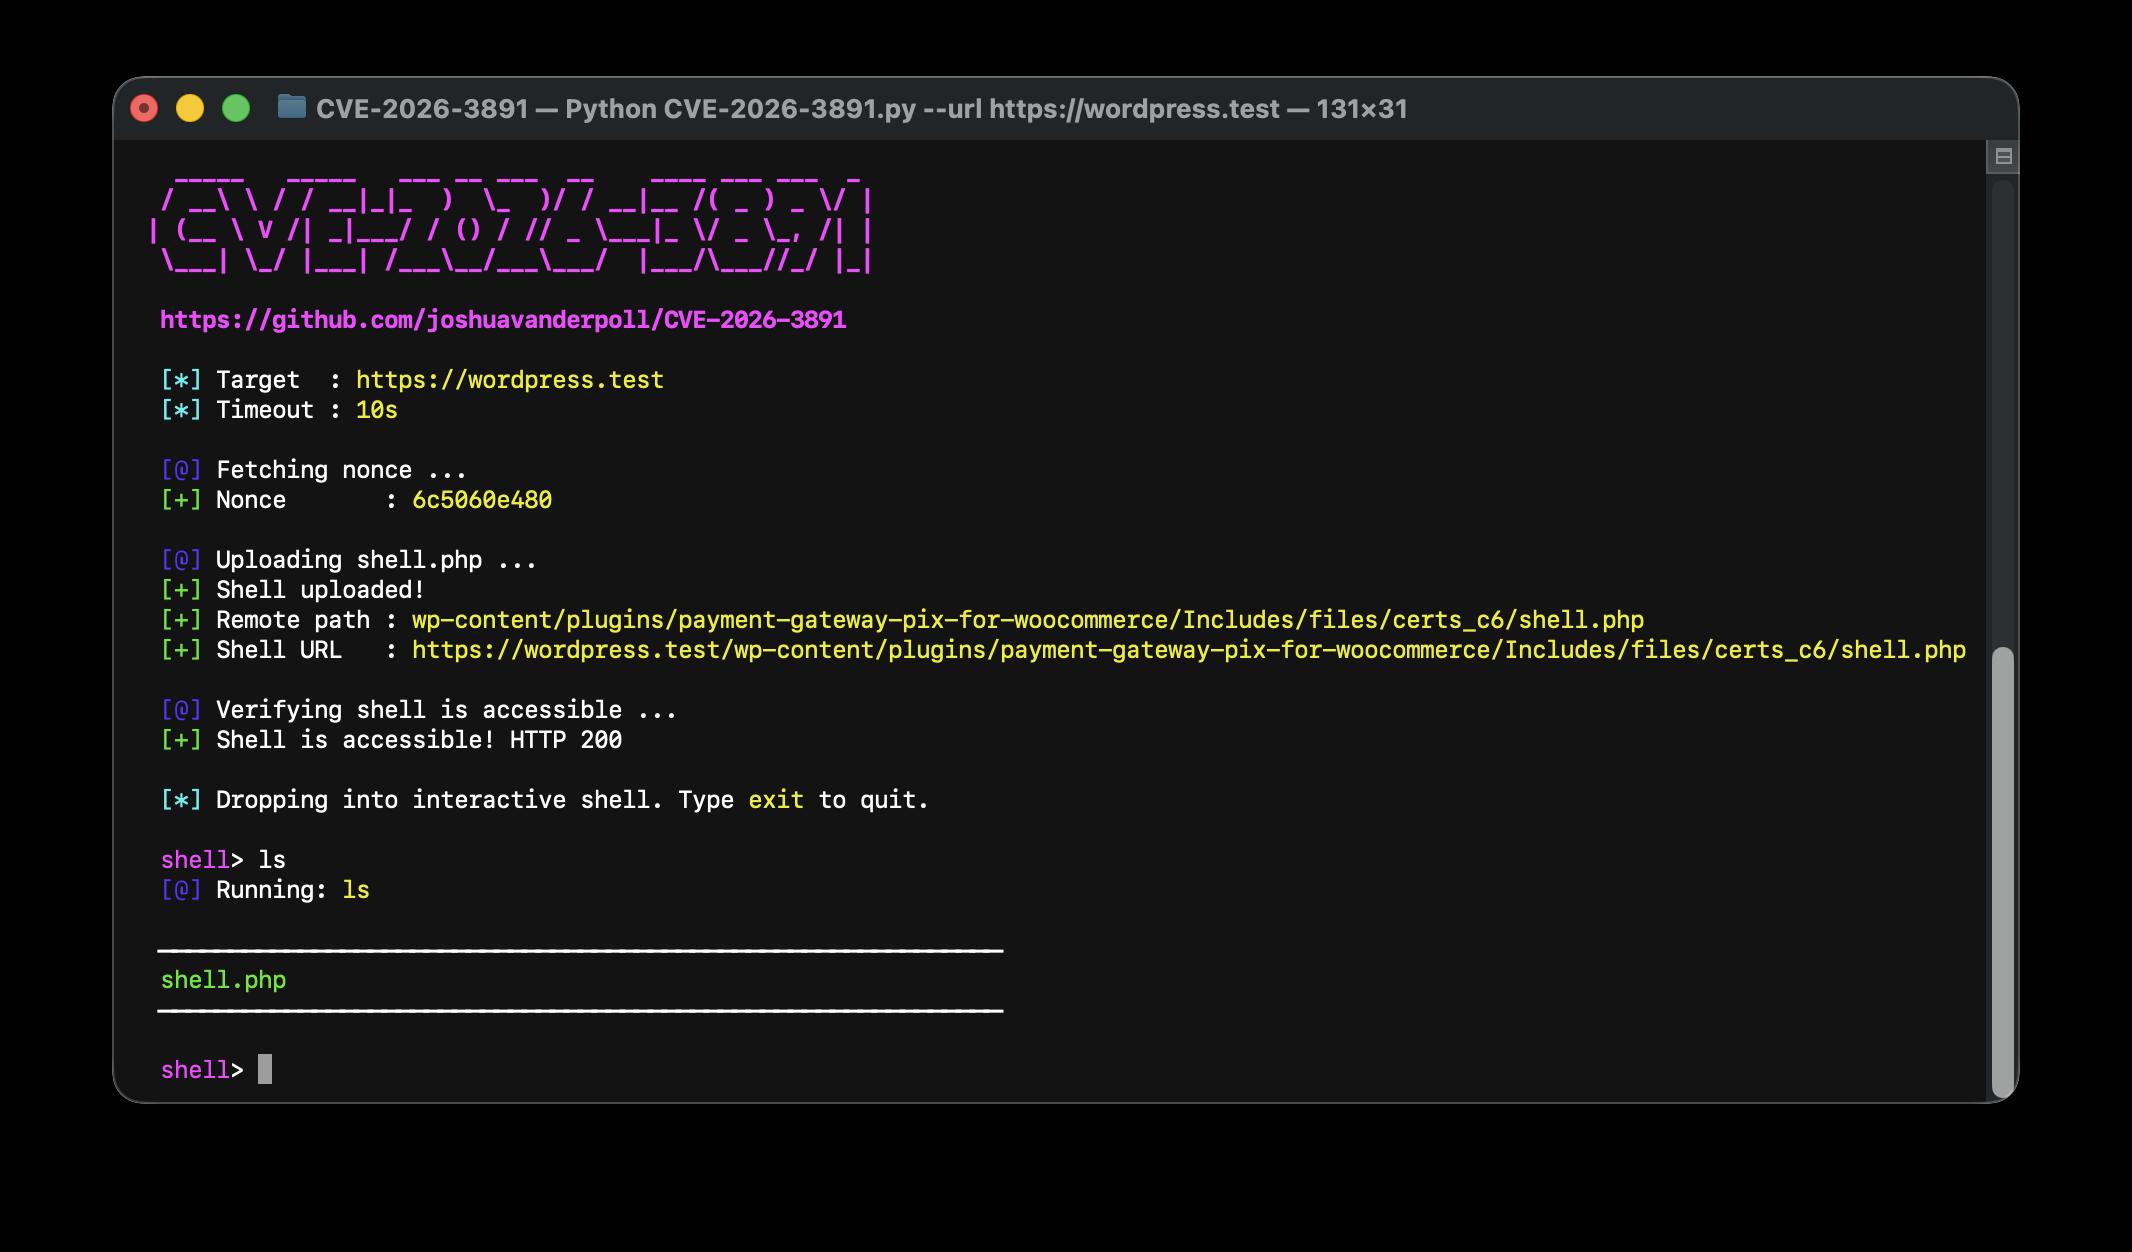 joshuavanderpoll/cve-2026-3891
Pix for WooCommerce <= 1.5.0 - Unauthenticated Arbitrary File Upload (CVE-2026-3891) PoC
 alpastx/cve-2023-3452---wordpress-canto-plugin-rce
CVE-2023-3452 exploit for WordPress Canto plugin RCE, HTTPS support included