
cve-2025-66398
Demonstrate exploitation of Signal K Server CVE-2025-66398 allowing unauthenticated attackers to inject backdoor and enable remote code execution.

Demonstrate exploitation of Signal K Server CVE-2025-66398 allowing unauthenticated attackers to inject backdoor and enable remote code execution.

Automates exploitation of CVE-2020-13160, a critical remote code execution vulnerability in AnyDesk 5.5.2, enabling penetration testers to validate…

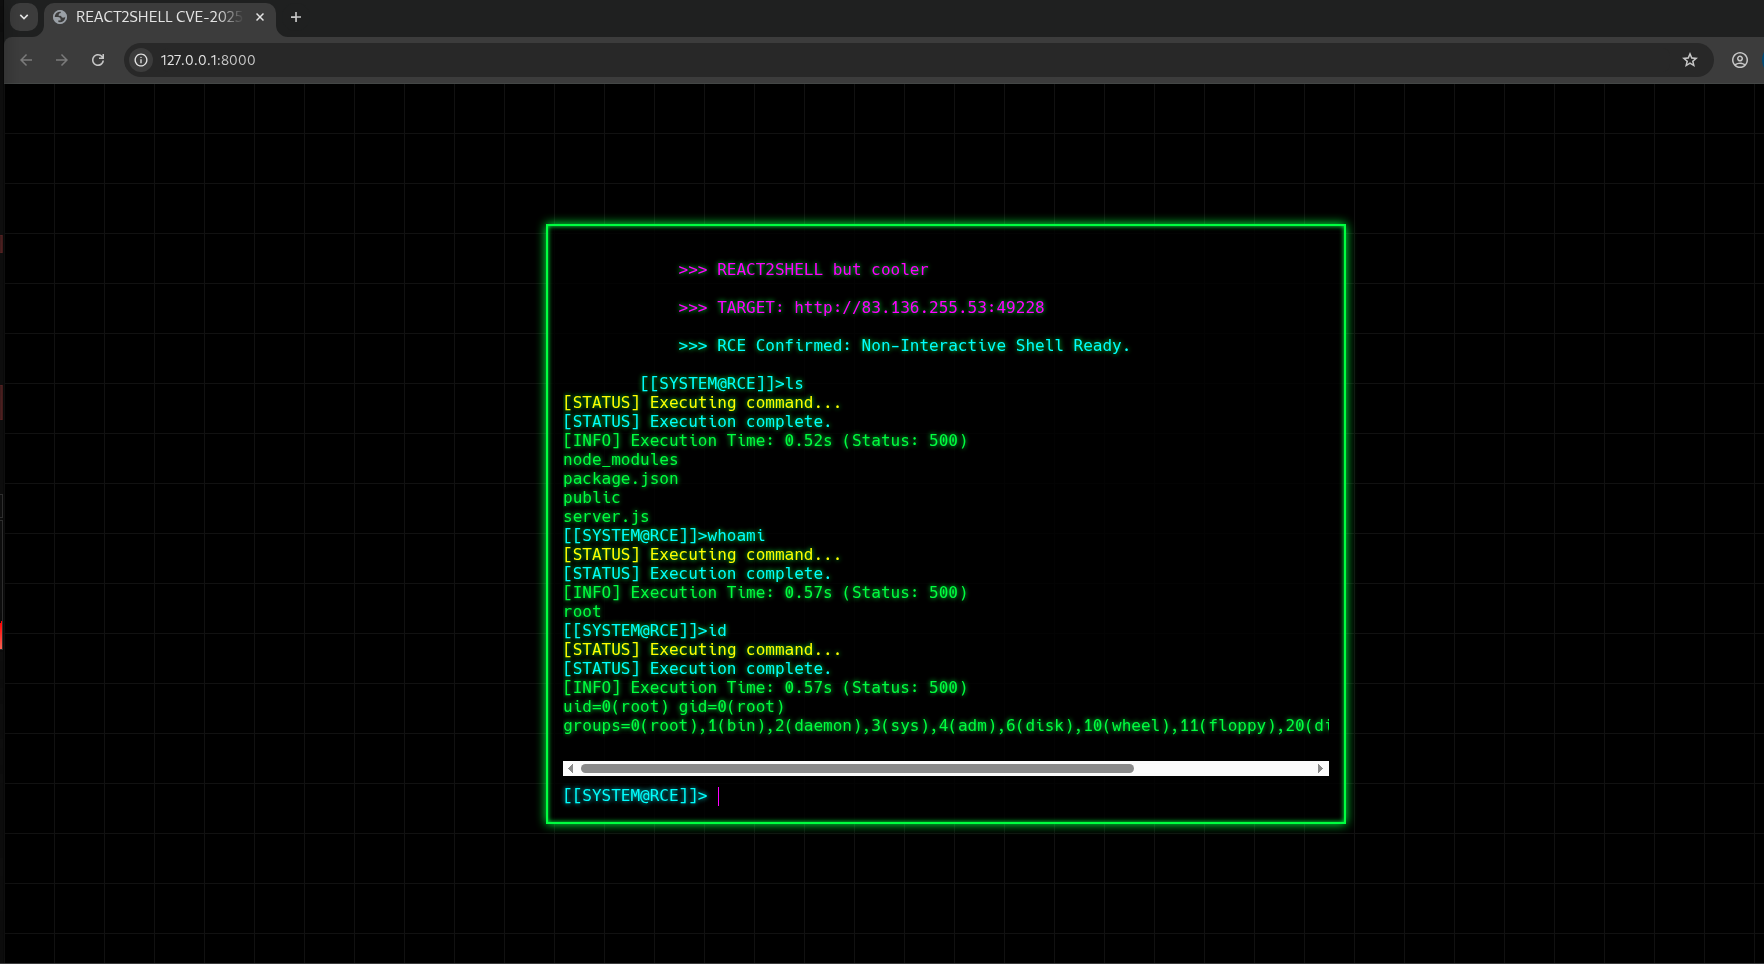
WEB-CLI_RCE_React2Shell is an educational PoC exploit tool for CVE-2025-55182, a critical Prototype Pollution flaw in Next.js applications using…

This is a POC for testing your projects that are vulnerable to CVE-2025-55182 with a terminal and ability to scan a list

# CVE-2025-0282: Remote Code Execution Vulnerability in [StorkS]

CVE-2019-11076 - Cribl UI 1.5.0 allows remote attackers to run arbitrary commands via an unauthenticated web request