
cve-2025-66398
Demonstrate exploitation of Signal K Server CVE-2025-66398 allowing unauthenticated attackers to inject backdoor and enable remote code execution.

Demonstrate exploitation of Signal K Server CVE-2025-66398 allowing unauthenticated attackers to inject backdoor and enable remote code execution.

All-in-One Hacking Tools For Hackers! And more hacking tools! For termux.

Socks5/Socks5h server and client. Full TCP/Bind/UDP and IPv4/IPv6 support

Display and control your Android device

Proof-of-concept exploit for CVE-2026-65400 enabling authenticated file read/write, reverse shells, and persistence on macOS via Apple ScreenSharing.

Asynchronous RDP client for Python (headless)

Remote Desktop Protocol .NET Console Application for Authenticated Command Execution

Voron messenger crypto/protocol library (X3DH-lite + Double Ratchet, group sender-keys, onion transport) — external review requested

A simple C2 Framework written in modern C++

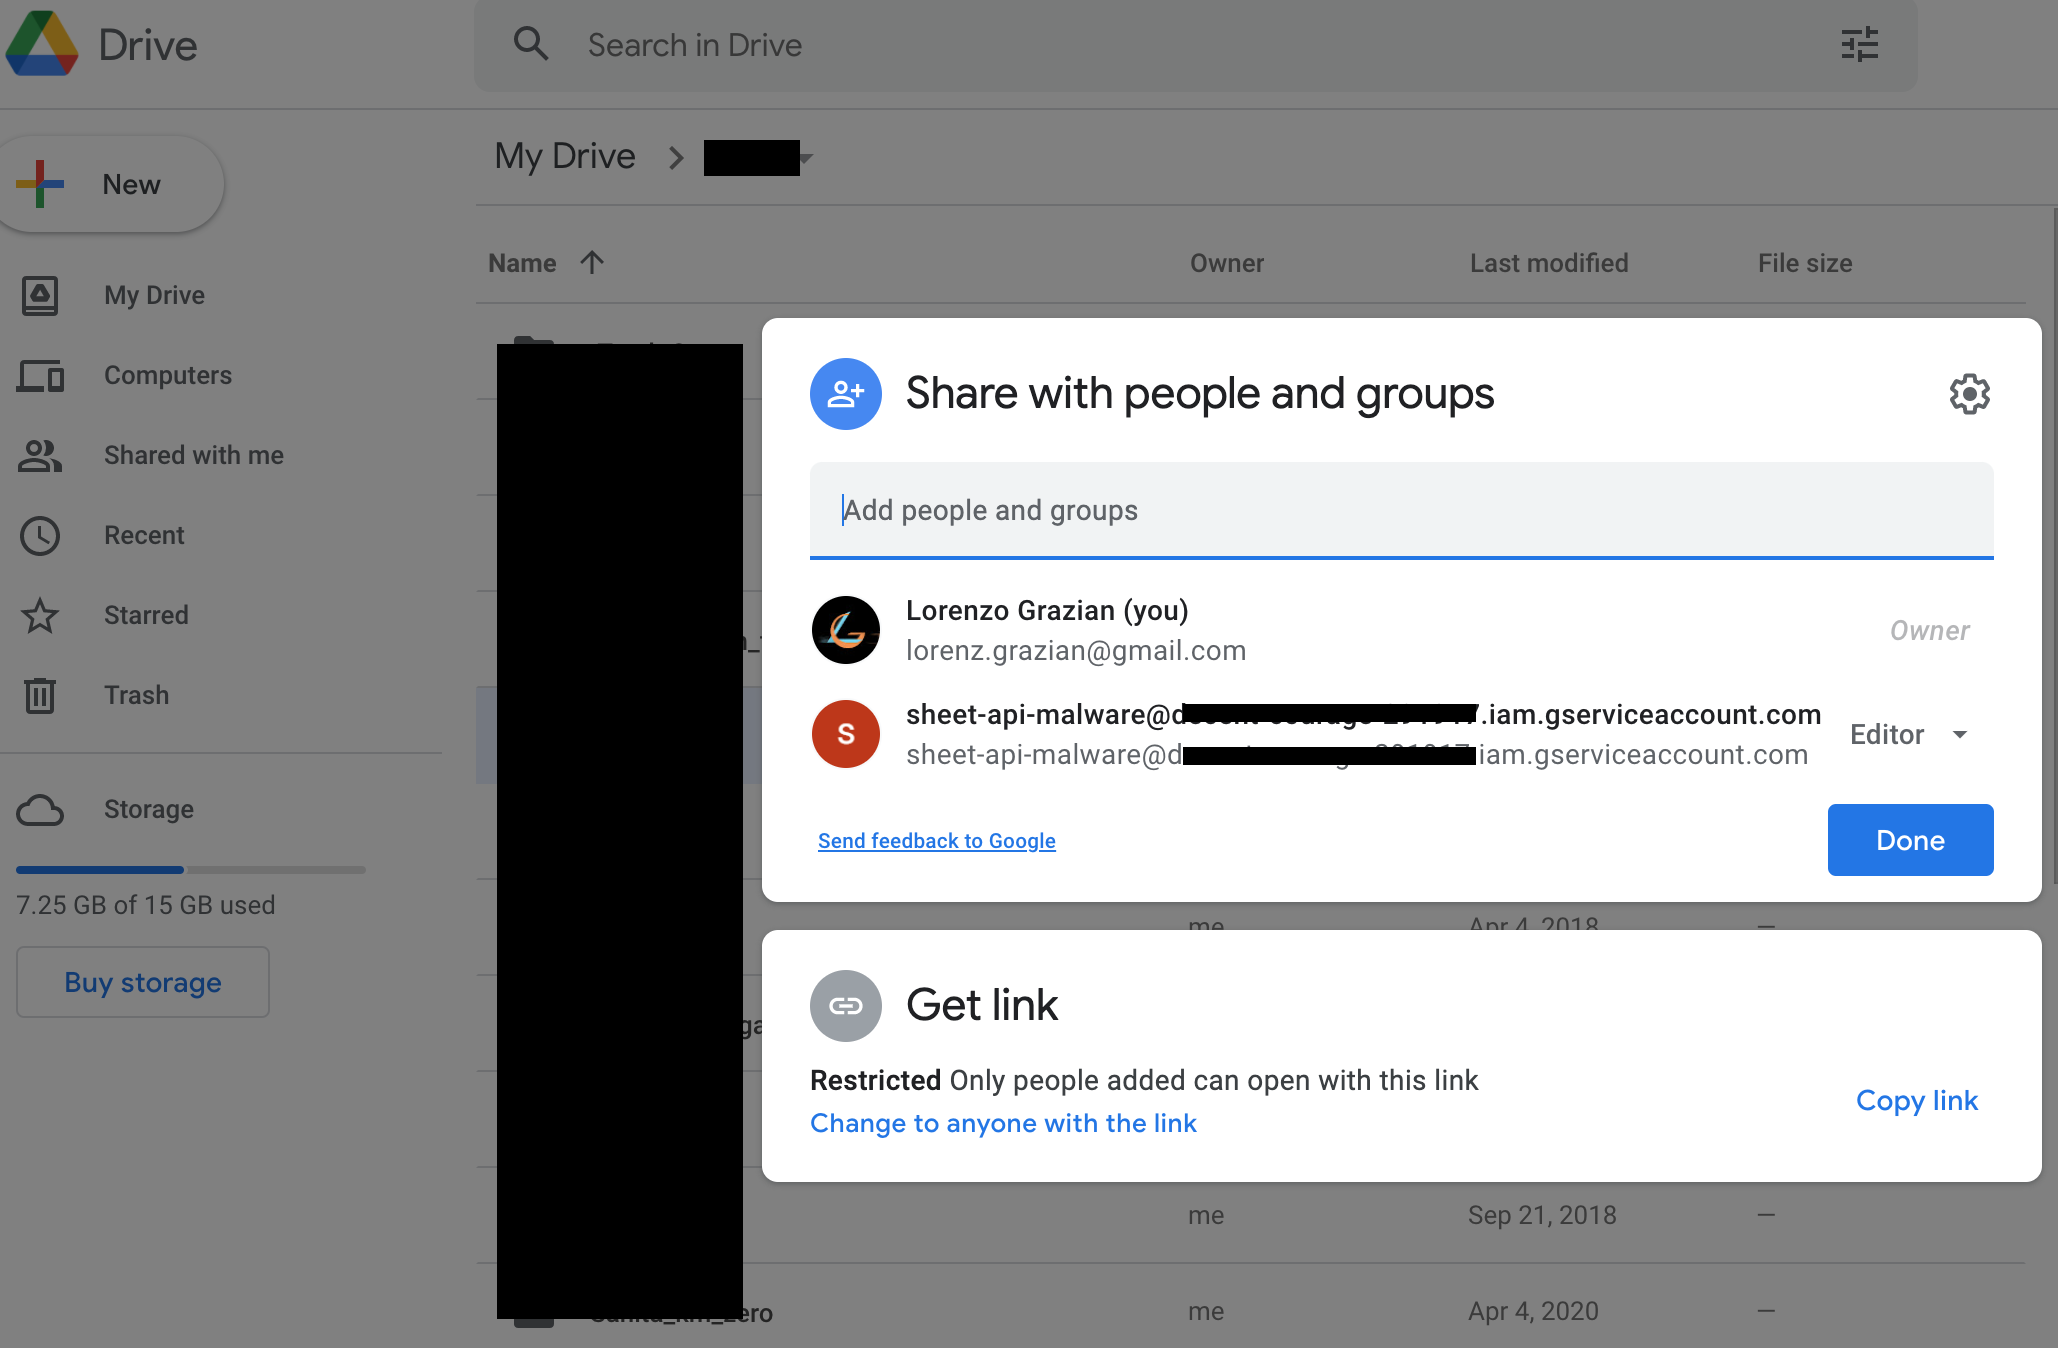
GC2 is a Command and Control application that allows an attacker to execute commands on the target machine using Google Sheet or Microsoft SharePoint…

PoC of CVE-2018-7600

CVE-2026-20253 - Splunk Enterprise

Exploitation of CVE-2023-44604. Using a Kali Linux VM (attacker) and a Debian 11 server VM (victim)

Open-source RDP client for connecting to Windows Terminal Services from Unix-like systems, supporting RDP versions 4 and 5 with smart-card…

A Proof-of-concept repository showing how an untrusted MCP server can steal literally everything...

Python exploit for vsFTPd 2.3.4 backdoor (CVE-2011-2523) that triggers a hidden shell on port 6200 via a crafted username, enabling remote command…

AI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.

Exploit CVE-2025-49132 Pterodactyl Panel RCE