
cve-2025-66398
Demonstrate exploitation of Signal K Server CVE-2025-66398 allowing unauthenticated attackers to inject backdoor and enable remote code execution.

Demonstrate exploitation of Signal K Server CVE-2025-66398 allowing unauthenticated attackers to inject backdoor and enable remote code execution.

Exploitation of CVE-2023-44604. Using a Kali Linux VM (attacker) and a Debian 11 server VM (victim)

Python exploit for vsFTPd 2.3.4 backdoor (CVE-2011-2523) that triggers a hidden shell on port 6200 via a crafted username, enabling remote command…

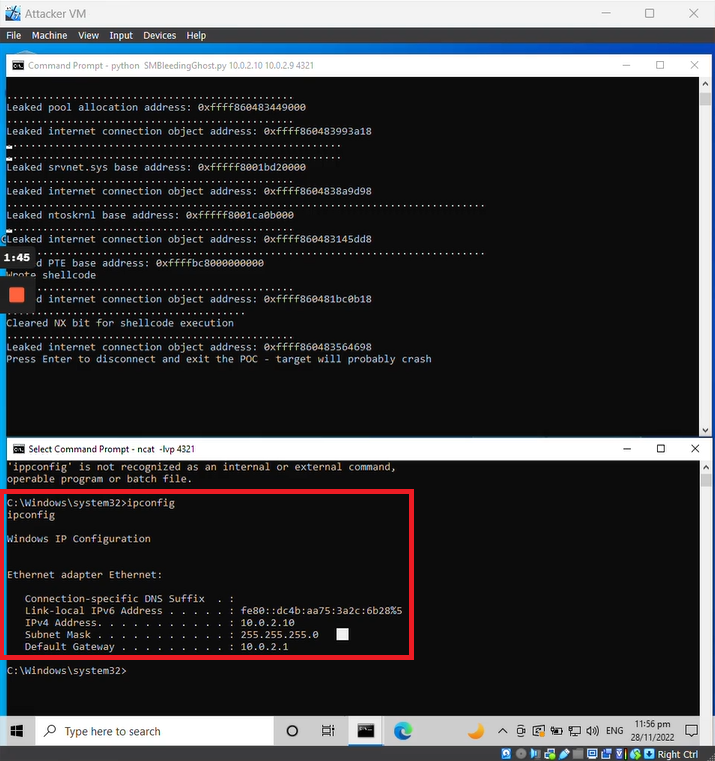
Educational proof-of-concept exploit for CVE-2020-0796 (SMBGhost) demonstrating pre-auth RCE on Windows SMBv3. Includes step-by-step lab setup,…

Automated Reverse Shell Exploit via WebSocket | Havoc-C2-SSRF with RCE

The goal of this project was to conduct a security audit of a blog recently launched by Ackme Support Incorporated, identifying any critical…

This project is a Python script that exploits the CVE-2023-24489 vulnerability in ShareFile. It allows remote command execution on the target server.…

WebLogic T3/IIOP RCE ExternalizableHelper.class of coherence.jar

WORK IN PROGRESS. RAT written in C++ using Win32 API

Generate Payloads and Control Remote Machines. [Discontinued]