
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
40 results
CVE-2025-68937 preview

CVE-2025-68937

GitHubscratchappy/cve-2025-68937

Automated PoC exploit for CVE-2025-68937 — Gitea/Forgejo Template Symlink RCE. Any authenticated user can get a shell as the git service user.
exploitationpenetration-testingprivilege-escalation+3
1 month ago
CVE-2025-8110 preview

CVE-2025-8110

GitHubixzodiak/cve-2025-8110

Gogs service Exploit and get the root user

ctfeducationexploitation+4
2 months ago
tugtainer-1.30.2-CVE-2026-55494-and-CVE-2026-62308-to-RCE preview

tugtainer-1.30.2-CVE-2026-55494-and-CVE-2026-62308-to-RCE

GitHub4qu4r1um/tugtainer-1.30.2-cve-2026-55494-and-cve-2026-62308-to-rce

A combination of CVE-2026-55494 and CVE-2026-62308 to get root privilege RCE in tugtainer
container-escapecontainer-securityeducation+5
2 months ago
oxasploits preview

oxasploits

GitHuboxasploits/oxasploits

A number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast
binary-exploitationbluetooth-securityexploitation+6
3 months ago
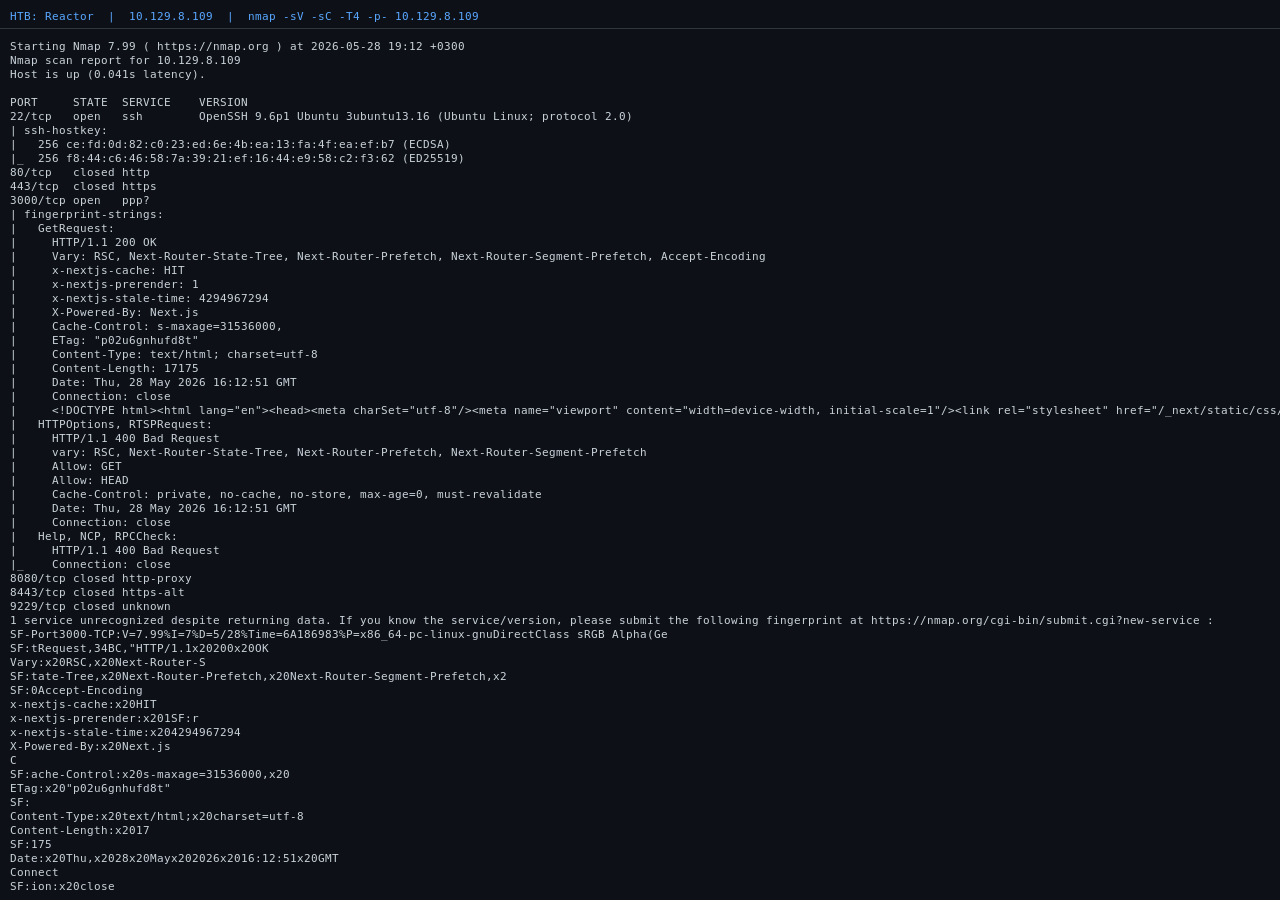
HTB-Reactor-Linux-Machine-Walkthrough preview

HTB-Reactor-Linux-Machine-Walkthrough

GitHubsonnycroco/htb-reactor-linux-machine-walkthrough

Full walkthrough of HTB's Reactor machine — exploit CVE-2025-55182 to gain a shell, then get root via an exposed Node.js debugger. Step-by-step with…

ctfeducationexploitation+8
13 months ago
cve-2025-50946 preview

cve-2025-50946

GitHubrunt1me/cve-2025-50946

Exploit script for CVE-2025-50946
exploitationpenetration-testingred-teaming+3
4 months ago
frida-c2-mcp preview

frida-c2-mcp

GitHubs4dp4nd4/frida-c2-mcp

Agentic C2-style MCP server for Frida instrumentation on rooted Android and jailbroken iOS.
android-securitycommand-and-controldynamic-analysis-sandboxing+8
656 months ago
CVE-2025-32433-available-for-windows preview

CVE-2025-32433-available-for-windows

GitHubblackcat4347/cve-2025-32433-available-for-windows

CVE-2025-32433-available-for-windows-victims

command-and-controleducationexploitation+3
7 months ago
FlaskCache_CVE-2021-33026_POC preview

FlaskCache_CVE-2021-33026_POC

GitHubagilevatester/flaskcache_cve-2021-33026_poc

PoC exploit for CVE-2021-33026 that poisons Redis cache in Flask-Cache to achieve remote code execution via malicious pickle deserialization.

exploitationpayload-generationpenetration-testing+4
18 months ago
selenium-node-takeover-kit preview

selenium-node-takeover-kit

GitHubjonstratton/selenium-node-takeover-kit

A collection of selenium tests that might aid it takeover of a selenium node

command-and-controldata-exfiltrationexploit-frameworks+6
39 months ago
CVE-2025-47812-poC preview

CVE-2025-47812-poC

GitHub0xcan1337/cve-2025-47812-poc

Simple exploit for Wing FTP Server RCE (CVE-2025-47812) to run commands and get a reverse shell. For educational use only.

educationexploitationpayload-generation+3
131 year ago
cve-2020-14008 preview

cve-2020-14008

GitHubjackhars/cve-2020-14008

Python exploit for CVE-2020-14008 in ManageEngine Applications Manager delivering a SYSTEM-level reverse shell via authenticated remote code…
exploitationpayload-generationpenetration-testing+4
51 year ago
CVE-2025-24813-PoC preview

CVE-2025-24813-PoC

GitHubtonyarris/cve-2025-24813-poc

A PoC for CVE-2025-24813
command-and-controlexploitationpayload-generation+4
11 year ago
CVE-2024-12856 preview

CVE-2024-12856

GitHubnu113d/cve-2024-12856

An exploit for Four-Faith routers to get a reverse shell
exploitationpenetration-testingremote-access-tool+2
31 year ago
EvilWinRM-NG preview

EvilWinRM-NG

GitLabceald1/evilwinrm-ng

Go-based WinRM client for remote command execution and lateral movement on Windows systems during penetration tests.
exploitationpenetration-testingremote-access-tool
22 years ago
Keylogger preview

Keylogger

GitHubaydinnyunus/keylogger

Get Keyboard,Mouse,ScreenShot,Microphone Inputs from Target Computer and Send to your Mail.
data-exfiltrationinformation-gatheringmalware-analysis+5
2.8k2 years ago
revshell preview

revshell

GitHubprodigiousmind/revshell

Pentestmonkeys' PHP reverse shell with dynamic host and port passing through GET request parameters

exploitationpayload-generationpenetration-testing+3
43 years ago
strapi_cms_3.0.0-beta.17.7 preview

strapi_cms_3.0.0-beta.17.7

GitHubhadrian3689/strapi_cms_3.0.0-beta.17.7

CVE-2019-18818/19606 Strapi RCE

educationexploitationpenetration-testing+3
3 years ago
Previous123Next
